
Arpspoof, often referred to as ARP spoofing or ARP cache poisoning, represents a significant and persistent threat within the realm of network security. It’s a method by which an attacker can intercept, modify, or even stop traffic on a local area network (LAN). Far from being a niche or obscure attack vector, ARP spoofing leverages a fundamental protocol inherent to how local networks function, making it a critical area of focus for anyone concerned with network integrity and data privacy in an increasingly interconnected technological landscape. Understanding arpspoof is not merely about identifying a vulnerability; it’s about grasping the intricate mechanisms of network communication and the innovative (albeit malicious) ways these mechanisms can be subverted.
Understanding the Core Mechanism
At its heart, ARP spoofing exploits the Address Resolution Protocol (ARP), a foundational component of IPv4 networks. To fully comprehend the attack, one must first grasp the role and function of ARP itself.
The Role of ARP
When a device on a local network wants to send data to another device, it knows the destination device’s IP address. However, to physically transmit the data over the local network medium (like Ethernet or Wi-Fi), it needs the destination device’s Media Access Control (MAC) address. The MAC address is a unique hardware identifier assigned to network interfaces. This is where ARP comes in.
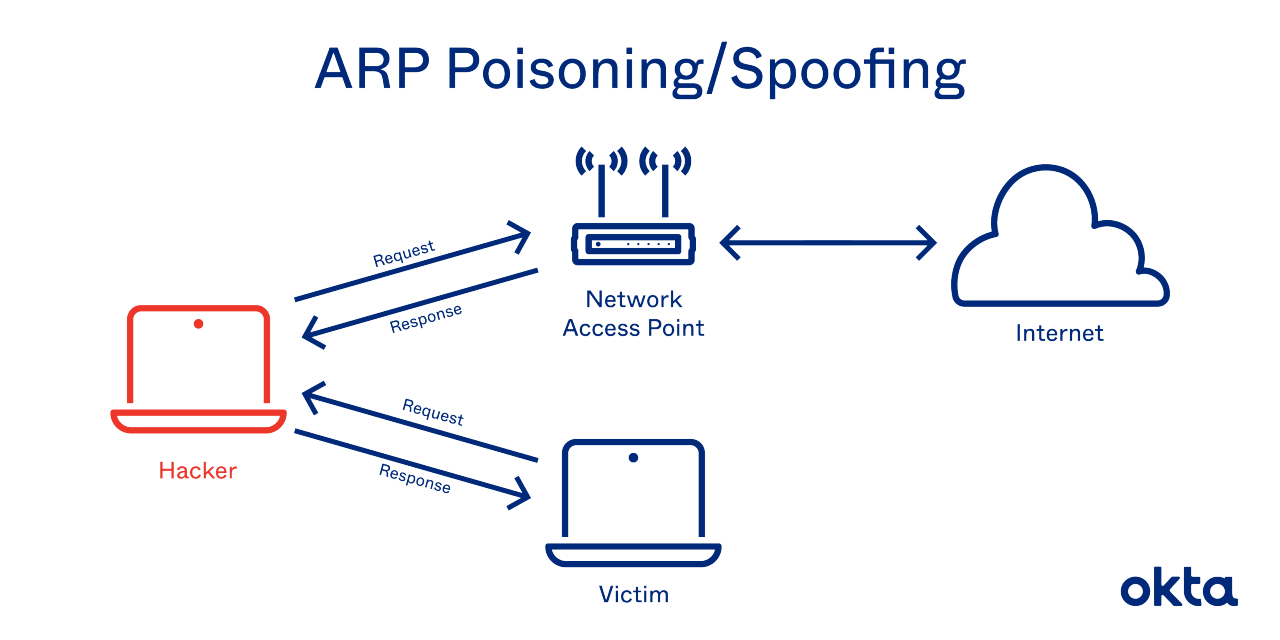
ARP acts as a translator, mapping IP addresses to MAC addresses. When a device needs to send data to an IP address for which it doesn’t have a corresponding MAC address, it broadcasts an ARP request across the local network. This request essentially asks, “Who has IP address X? Tell me your MAC address.” The device owning that IP address responds with an ARP reply, stating, “I have IP address X, and my MAC address is Y.” All devices maintain an ARP cache, a temporary table storing these IP-to-MAC address mappings to avoid repeatedly broadcasting requests.
How ARP Spoofing Works
ARP spoofing exploits the stateless nature of ARP. The protocol was designed for efficiency and simplicity, not security. When a device receives an ARP reply, it typically updates its ARP cache with the new mapping, assuming it’s legitimate, without verifying the sender’s authenticity. This trust mechanism is the Achilles’ heel that arpspoof leverages.
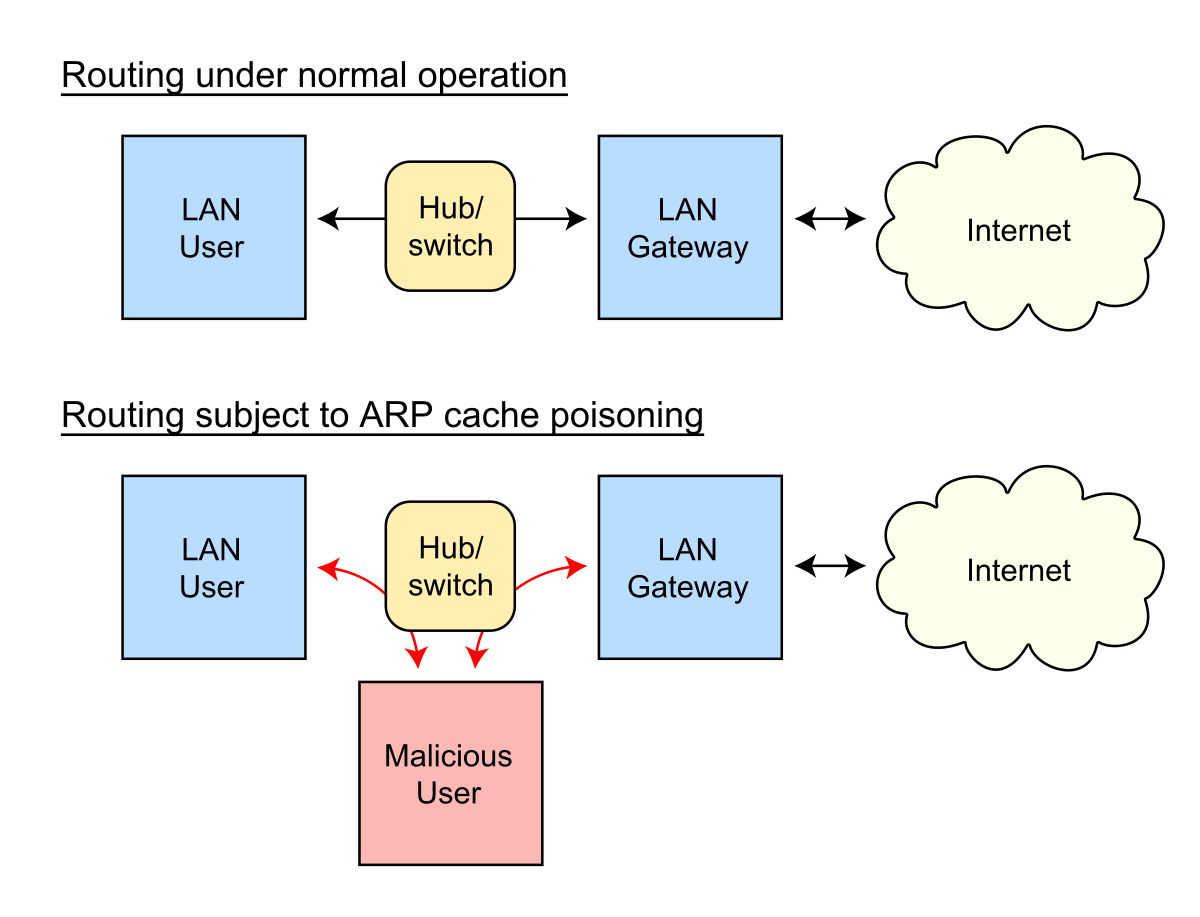
An attacker, using tools like arpspoof itself (a command-line utility for Linux), sends unsolicited or gratuitous ARP replies to other devices on the network. These crafted ARP replies falsely associate the attacker’s MAC address with the IP address of a legitimate device on the network, such as the default gateway (router) or another target host.
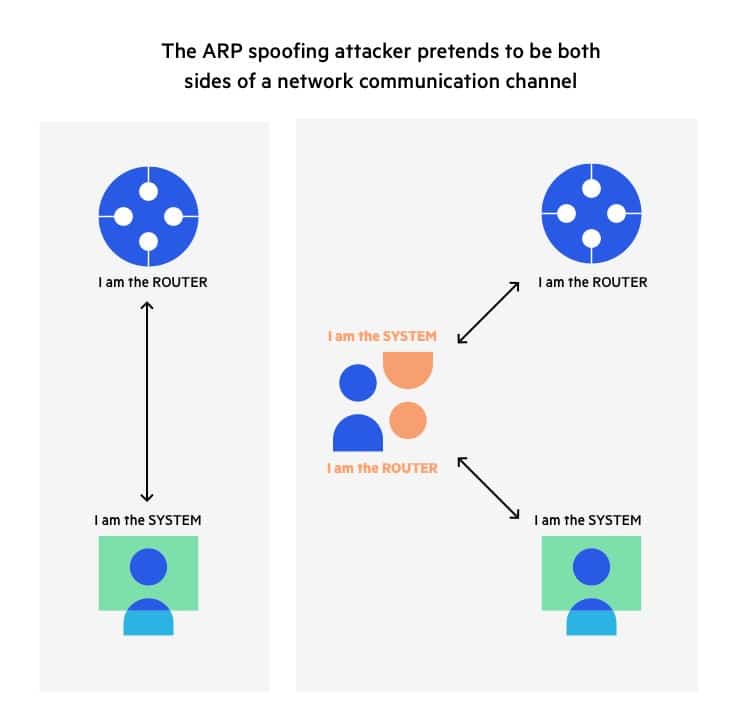
For example, an attacker might send an ARP reply to a target victim, claiming, “I am the router (IP address Z), and my MAC address is ATTACKERMAC.” Simultaneously, the attacker might send another ARP reply to the actual router, claiming, “I am the victim (IP address X), and my MAC address is ATTACKERMAC.”
Once these false entries are cached by the victim and the router, all traffic intended for the router from the victim (and vice versa) will be rerouted through the attacker’s machine. The attacker essentially positions themselves as a man-in-the-middle, transparently intercepting all communications between the two compromised hosts. This insidious manipulation of foundational network protocols underscores a significant challenge in safeguarding modern digital infrastructures.
The Ramifications of an ARP Spoof Attack
The consequences of a successful ARP spoof attack are far-reaching and can compromise the integrity, confidentiality, and availability of network resources. The attacker, once positioned as a man-in-the-middle, gains immense power over the intercepted traffic.
Man-in-the-Middle Attacks
The most common and immediate outcome of ARP spoofing is the facilitation of a Man-in-the-Middle (MitM) attack. In this scenario, the attacker can:
- Eavesdrop on Communications: All data flowing between the victim and the router (or between two victims) passes through the attacker’s machine. If the traffic is unencrypted (e.g., HTTP), the attacker can read it directly. This includes sensitive information like login credentials, personal data, and confidential communications.
- Modify Data: Beyond passive eavesdropping, the attacker can actively modify the data packets in transit before forwarding them to the legitimate destination. This could involve altering messages, injecting malicious code, or corrupting files, leading to severe operational disruptions or security breaches.
- Redirect Traffic: The attacker can redirect traffic to malicious websites or servers, tricking users into revealing further information or downloading malware.
Session Hijacking and Data Theft
With the ability to intercept and read network traffic, an ARP spoofing attacker can steal session cookies or authentication tokens. These tokens are used by web applications to maintain a user’s logged-in state. By capturing these, the attacker can hijack active user sessions, gaining unauthorized access to accounts without needing to know the victim’s username and password. This poses a significant threat to online banking, e-commerce, social media, and any web-based service that relies on session management. The theft of data, ranging from personal files to corporate secrets, becomes a straightforward task for an attacker employing an ARP spoof.
Denial of Service
ARP spoofing can also be leveraged to launch a Denial of Service (DoS) attack. By continuously sending false ARP replies that associate a non-existent MAC address with a critical network resource (like the default gateway or a server), the attacker can prevent legitimate traffic from reaching its destination. This floods the network with incorrect ARP information, causing legitimate traffic to be dropped or misrouted, effectively bringing down network connectivity for affected users or systems. This type of attack demonstrates how a seemingly simple protocol manipulation can lead to profound service disruptions.
Detecting and Mitigating ARP Spoofing
Given the potent threats posed by ARP spoofing, robust detection and mitigation strategies are essential for maintaining network security. These strategies typically involve a combination of proactive preventative measures and reactive detection techniques.
Proactive Security Measures
Preventative strategies focus on hardening the network against ARP spoofing before an attack can even begin.
- Static ARP Entries: For critical systems (e.g., servers, routers), administrators can manually configure static ARP entries in their ARP caches. This hard-codes the IP-to-MAC address mapping, preventing dynamic updates from unsolicited ARP replies. While effective for a small number of critical devices, it is impractical for large networks due to the overhead of manual configuration and maintenance.
- ARP Inspection (Dynamic ARP Inspection – DAI): Many modern managed switches offer Dynamic ARP Inspection (DAI) as a security feature. DAI works by intercepting ARP packets and validating them against legitimate IP-to-MAC address bindings stored in a trusted database (often derived from DHCP snooping). If an ARP packet contains an invalid binding, the switch drops it, preventing the false information from propagating. This is a highly effective hardware-level defense.
- Port Security: On switches, port security can be configured to allow only specific MAC addresses to communicate through certain ports. This prevents unauthorized devices from connecting and potentially launching ARP spoofing attacks, though it requires careful management in environments with frequently changing devices.
- Network Segmentation: Segmenting a network into smaller VLANs (Virtual Local Area Networks) limits the broadcast domain of ARP traffic. If an ARP spoofing attack occurs, its impact is confined to the specific VLAN, preventing it from affecting the entire network.
- Encryption (HTTPS, VPNs): While not directly preventing the ARP spoof, using end-to-end encryption for communications (like HTTPS for web traffic or VPNs for all traffic) ensures that even if an attacker intercepts data, they cannot read or meaningfully modify its contents. This turns an active MitM into a passive wiretap, but only if decryption keys are not compromised.
Reactive Detection Techniques
Even with preventative measures, robust detection mechanisms are crucial for identifying attacks in progress.
- ARP Monitoring Tools: Specialized software tools can continuously monitor ARP traffic on a network. They look for suspicious activities such as multiple devices claiming the same IP or MAC address, sudden changes in ARP cache entries for critical devices, or ARP replies being sent without a preceding request. Examples include
arpwatchandXArp. - Intrusion Detection Systems (IDS) / Intrusion Prevention Systems (IPS): Network-based IDS/IPS solutions can be configured to detect ARP spoofing patterns. They analyze network traffic for anomalies indicative of ARP cache poisoning and can alert administrators or even automatically block malicious traffic.
- Logging and Auditing: Regularly reviewing network logs for unusual ARP activity, unauthorized MAC addresses, or IP address conflicts can help identify and respond to ARP spoofing attempts.
The Evolving Landscape of Network Security
ARP spoofing serves as a stark reminder that even fundamental network protocols, designed decades ago for simpler network environments, remain potent targets in today’s complex digital ecosystems. The continuous evolution of attack techniques necessitates an equally dynamic approach to network security.
The Importance of Robust Protocols
The vulnerability of ARP highlights the need for security to be baked into protocol design from the outset, rather than being an afterthought. While modern protocols often incorporate cryptographic measures and authentication, the legacy components upon which much of our current infrastructure relies continue to present challenges. Efforts to migrate to IPv6, which incorporates IPsec for authentication and encryption, offer a more secure alternative, though widespread adoption is a gradual process. The reliance on established standards means that innovative solutions are constantly required to bridge the gap between legacy vulnerabilities and modern security demands.
Future-Proofing Network Infrastructure
In an era defined by ubiquitous connectivity and the rapid proliferation of IoT devices, securing local networks against attacks like ARP spoofing is more critical than ever. Every connected device, from smart sensors to advanced aerial platforms, relies on the underlying network infrastructure. A compromised network can lead to data breaches, operational disruptions, and a loss of trust. Therefore, future-proofing network infrastructure involves not only deploying advanced security hardware and software but also fostering a deep understanding of network fundamentals among administrators and engineers. This includes continuous education, regular security audits, and the adoption of a layered security approach that addresses vulnerabilities at every level of the network stack. As technology evolves, so too must our defenses against sophisticated, and sometimes deceptively simple, attack vectors like ARP spoofing.