
ARP cache poisoning, also known as ARP spoofing or ARP man-in-the-middle (MITM) attack, represents a significant threat within local area networks (LANs). It leverages a fundamental aspect of network communication, the Address Resolution Protocol (ARP), to redirect or intercept network traffic. Understanding this vulnerability is crucial for securing modern technological infrastructure, particularly in an era dominated by interconnected devices, autonomous systems, and pervasive data exchange.
Understanding ARP: The Foundation of Local Network Communication
At its core, ARP is a stateless protocol used to resolve IP addresses to physical MAC (Media Access Control) addresses within a local network segment. When a device needs to send data to another device on the same LAN, it knows the destination’s IP address but requires its MAC address to properly encapsulate the data into Ethernet frames. This is where ARP comes into play.
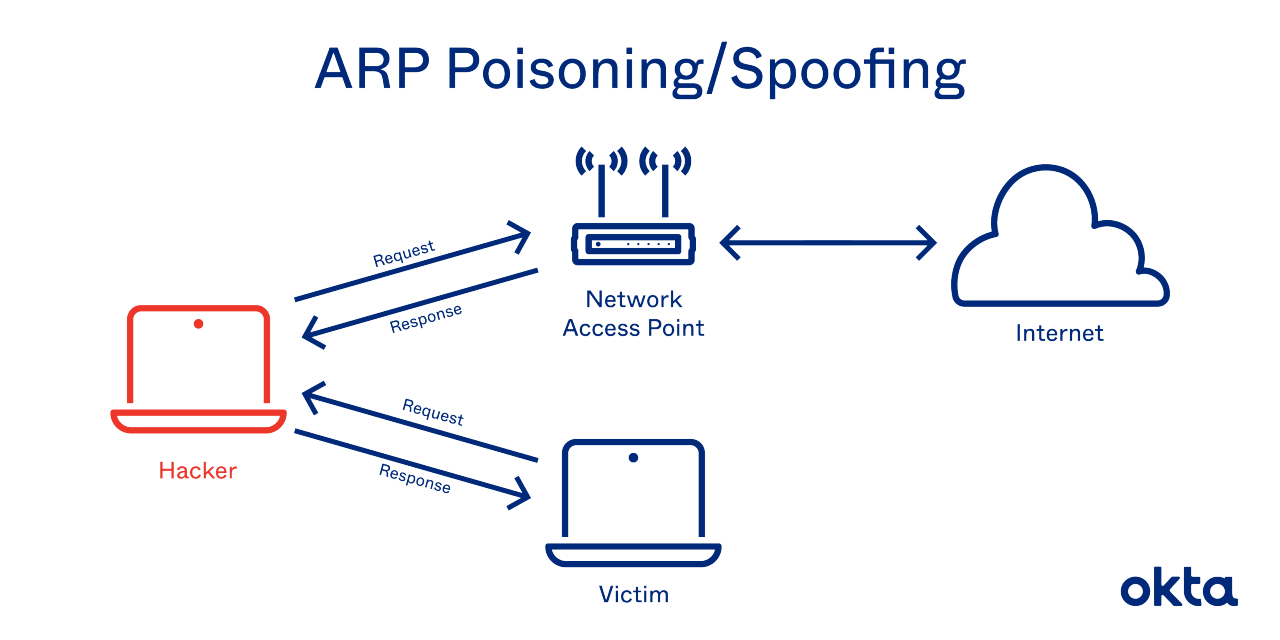
A device needing a MAC address for a known IP address broadcasts an “ARP request” to all other devices on the local network. This request typically asks, “Who has IP address X.X.X.X? Tell Y.Y.Y.Y (my IP address).” The device with the matching IP address then responds with an “ARP reply,” stating, “I have IP address X.X.X.X, and my MAC address is AA:BB:CC:DD:EE:FF.” Upon receiving this reply, the requesting device stores the IP-to-MAC mapping in its local ARP cache for a certain period, preventing the need to send an ARP request for every packet. This caching mechanism is designed for efficiency, reducing network overhead. However, it is also the very mechanism that makes ARP vulnerable to poisoning. The protocol itself does not incorporate authentication or verification for ARP replies, meaning any device can claim to possess any IP address, and other devices will, by default, trust this assertion and update their caches accordingly.
How ARP Cache Poisoning Works: The Attack Vector
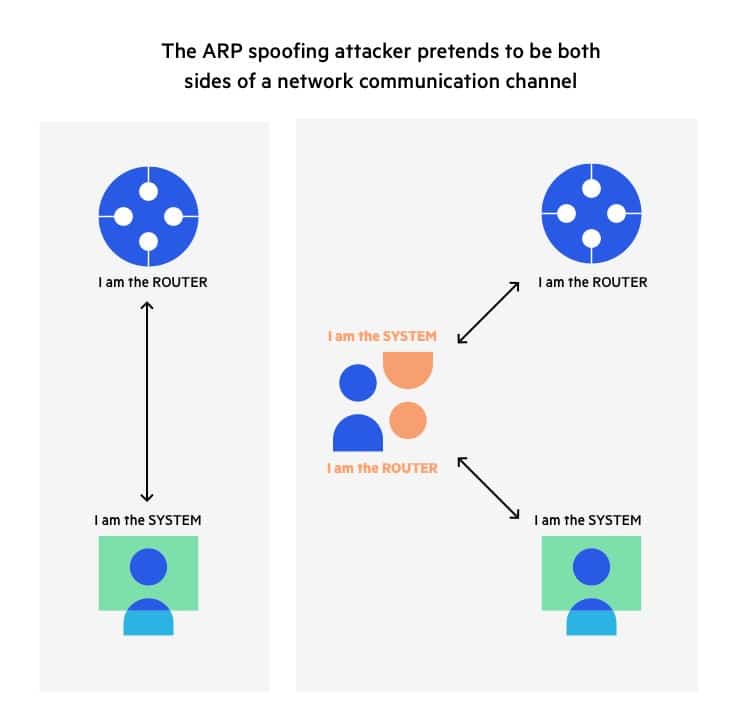
An ARP cache poisoning attack exploits this trust relationship and the stateless nature of ARP. The attacker’s objective is to associate their own MAC address with the IP address of another legitimate device on the network, typically the default gateway (router) or another host the target wishes to communicate with.
The attack unfolds in several steps:
Identifying Targets
The attacker first identifies the IP and MAC addresses of the target victim(s) and the default gateway within the local network. This can be done through network scanning tools or by simply listening to ARP traffic.
Sending Malicious ARP Replies
Once targets are identified, the attacker begins sending unsolicited, fraudulent ARP reply packets to both the victim device and the gateway.
- To the victim, the attacker sends an ARP reply claiming that the gateway’s IP address (e.g., 192.168.1.1) is associated with the attacker’s MAC address.
- To the gateway, the attacker sends an ARP reply claiming that the victim’s IP address (e.g., 192.168.1.100) is associated with the attacker’s MAC address.
Poisoning the Cache
Upon receiving these malicious ARP replies, both the victim’s and the gateway’s ARP caches are updated with the incorrect mappings. The victim now believes the attacker’s MAC address is the gateway’s, and the gateway believes the attacker’s MAC address is the victim’s.
Intercepting Traffic
With the caches poisoned, any traffic from the victim intended for the internet (via the gateway) will first be sent to the attacker’s machine. Similarly, any traffic from the internet (via the gateway) intended for the victim will also be sent to the attacker. The attacker then typically forwards the traffic to the legitimate destination after intercepting, inspecting, or modifying it, thus operating as a “man-in-the-middle.” If the attacker fails to forward the traffic, a denial-of-service condition can occur.
The Real-World Impact: Data Interception and Man-in-the-Middle Attacks
The success of an ARP cache poisoning attack leads directly to a man-in-the-middle scenario, opening the door to a wide range of malicious activities, profoundly impacting data integrity and privacy across various technological domains.
Data Eavesdropping and Credential Theft
One of the most common consequences is the interception of unencrypted traffic. An attacker can capture sensitive information such as usernames, passwords, financial details, and proprietary data that are transmitted over HTTP, FTP, or other non-secured protocols. This is particularly relevant in environments where some legacy systems or misconfigured applications might still transmit sensitive data without robust encryption, posing risks to critical infrastructure and enterprise networks.

Session Hijacking
By intercepting network traffic, an attacker can also capture session cookies or authentication tokens. These can then be used to hijack a user’s active session, gaining unauthorized access to web applications, cloud services, or internal systems without needing the actual credentials. This can impact remote management interfaces for various tech devices, including those used in remote sensing or autonomous operations.
Data Modification and Injection
Beyond mere interception, an attacker can actively modify data packets as they pass through their machine. This could involve altering financial transactions, changing commands sent to critical systems, or injecting malicious content (e.g., malware, fake updates) into legitimate data streams. For sophisticated tech operations relying on precise data, such as real-time mapping or command signals for UAVs, data modification could have catastrophic operational and safety implications.
Denial of Service (DoS)
If the attacker simply intercepts traffic without forwarding it, or if they flood the network with continuous false ARP replies, they can effectively prevent legitimate communication between devices, leading to a denial-of-service condition. This can cripple network-dependent systems, disrupting services, communications, and data flow. In tech sectors where continuous operation is vital, like autonomous navigation or critical data relay, a DoS can be highly damaging.
Malware Distribution
An attacker can redirect victims to malicious websites or servers, facilitating the distribution of malware, ransomware, or spyware. By altering DNS queries or HTTP requests, they can ensure victims land on phishing pages or download compromised software, impacting the security of endpoints and entire networks.
Detecting and Mitigating ARP Cache Poisoning
Given its potential for disruption and data compromise, effective detection and mitigation of ARP cache poisoning are paramount for any modern networked environment.
Static ARP Entries
One of the most direct mitigation techniques is to configure static ARP entries on critical devices, such as servers, gateways, and workstations. By manually mapping an IP address to a specific MAC address and marking it as static, the device will ignore any unsolicited ARP replies attempting to update that entry. While effective for a small number of critical devices, this method is impractical for large, dynamic networks.
Network Segmentation
Segmenting the network into smaller VLANs (Virtual Local Area Networks) can limit the blast radius of an ARP poisoning attack. If an attacker successfully poisons a segment, the impact is confined to that segment, preventing lateral movement to other critical parts of the network. This is a common practice in enterprise environments to isolate different departments or types of devices (e.g., IoT devices, guest networks).
ARP Monitoring Tools
Specialized network monitoring tools and Intrusion Detection/Prevention Systems (IDS/IPS) can be deployed to detect suspicious ARP activity. These tools can identify patterns indicative of an ARP poisoning attack, such as multiple ARP replies from a single MAC address for different IP addresses, or sudden, rapid changes in ARP cache entries. Upon detection, they can alert administrators or automatically block the offending MAC address.
Using VPNs and Encryption
While ARP poisoning targets the local network layer, end-to-end encryption (e.g., HTTPS, SSL/TLS, SSH, VPNs) significantly reduces the impact of data interception. Even if an attacker manages to capture encrypted traffic, they will generally be unable to decipher its contents without the decryption keys. VPNs, in particular, establish secure, encrypted tunnels, making data passing through an ARP-poisoned segment unintelligible to the attacker.
Secure Network Protocols
Implementing secure alternatives to protocols like Telnet or FTP, such as SSH and SFTP, which inherently encrypt data, can prevent credential theft and data eavesdropping even if an ARP poisoning attack occurs.
The Broader Implications for Modern Tech Systems
The vulnerability posed by ARP cache poisoning extends across a wide spectrum of modern technological systems, emphasizing the critical need for robust network security. In an era where “Tech & Innovation” drives autonomous flight, sophisticated mapping, remote sensing, and AI-powered operations, the integrity of network communication is non-negotiable.
Autonomous systems, whether ground-based robots or Unmanned Aerial Vehicles (UAVs) used for surveillance or delivery, rely heavily on precise and secure communication channels for command and control, telemetry, and data transmission. An ARP cache poisoning attack on the ground control station’s network or even within a drone’s internal network (if applicable for multi-component communication) could lead to intercepted control signals, altered mission parameters, or compromised sensor data. This could result in loss of control, diversion of assets, or the delivery of false intelligence.
Similarly, remote sensing platforms that collect vast amounts of environmental or geospatial data often transmit this information over local networks before it reaches central processing units or cloud infrastructure. A MITM attack could allow an adversary to tamper with this critical data, injecting false readings or corrupting datasets, which could undermine subsequent AI-driven analysis, machine learning model training, or decision-making processes based on compromised input.
The reliance on IoT devices in smart cities, industrial automation, and critical infrastructure further magnifies the risk. Many IoT devices have limited security features, making them easy targets for ARP poisoning, turning them into points of entry or platforms for launching further attacks within the network. Securing the underlying network layer against such fundamental attacks is not just a matter of cybersecurity hygiene; it is a foundational requirement for the trustworthy operation and advancement of innovative technologies that depend on seamless, secure connectivity.