
In the rapidly evolving landscape of unmanned aerial systems (UAS), where drones transition from standalone devices to integral components of complex, networked ecosystems, the concept of a Network Address Translation (NAT) Gateway emerges as a cornerstone of efficient and secure communication. Far from being a mere IT networking term, understanding the principles and applications of a NAT Gateway is crucial for comprehending how advanced drone fleets connect to cloud services, interact with remote operators, and maintain operational security in an era of pervasive connectivity.
At its core, a NAT Gateway acts as an intermediary, facilitating communication between devices in a private network and resources on a public network, such as the internet. For drones, this means enabling individual aircraft, often operating within a local, private network (like a swarm or a fleet managed by a ground control station), to seamlessly send data to and receive commands from external, public-facing systems like cloud-based AI platforms, remote command centers, or global navigation satellite systems. It’s a mechanism that allows multiple “private” drone entities to share a single “public” identity when interacting with the wider world, conserving public IP addresses and adding a vital layer of security.
The Foundation of Network Connectivity for Advanced Drone Systems
The burgeoning complexity of drone operations necessitates sophisticated networking solutions. Modern drone deployments often involve not just one drone, but fleets of them, each equipped with an array of sensors, onboard processing units, and communication modules. These individual drones must interact with a variety of external systems: cloud-based analytics platforms for mapping or data processing, remote operators thousands of miles away, centralized command and control systems, and potentially other IoT devices.
The challenge arises because assigning a unique, publicly routable IP address to every single drone or onboard component within a large fleet is impractical, expensive, and often unnecessary. Public IP addresses are a finite resource, and directly exposing every drone to the public internet creates a massive attack surface. This is precisely where the NAT Gateway principle becomes indispensable in drone technology.
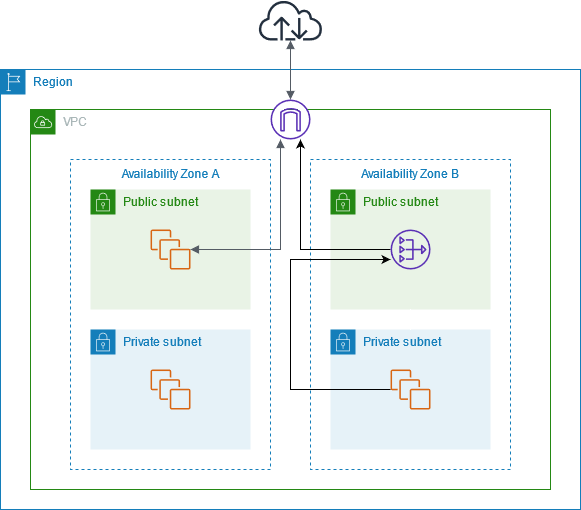
Imagine a large drone fleet engaged in an agricultural survey, with each drone gathering hyperspectral imagery and sending telemetry data. Each drone might be assigned a private IP address (e.g., 192.168.1.101, 192.168.1.102, etc.) by a local ground control station acting as a router. When these drones need to upload their aggregated data to a cloud storage service or stream live video to a remote expert, they don’t directly use their private IPs. Instead, all their outbound traffic is routed through a central point—the NAT Gateway. This gateway, which possesses a single public IP address, translates the private source IP address of the drone into its own public IP address before forwarding the data to the internet. When the cloud service responds, the NAT Gateway receives the response on its public IP and then intelligently translates it back to the correct private IP address of the originating drone, ensuring the data reaches its intended recipient. This transparent translation layer is fundamental to enabling the robust and scalable connectivity required for modern drone operations.
Enabling Scalable Drone Fleet Management and Cloud Integration
The core utility of a NAT Gateway in drone technology shines brightest in its ability to facilitate scalable fleet management and seamless integration with cloud-based services. As drone operations expand from single-aircraft missions to coordinated endeavors involving dozens or even hundreds of drones, efficient network address management becomes paramount.
Private Addresses for Individual Drones in a Fleet
In large-scale drone deployments, such as for precision agriculture, infrastructure inspection, or disaster response, each drone within a fleet typically operates on a private, internal network. This internal network is often managed by a central ground control station (GCS), a mobile command vehicle, or a powerful edge computing device. Within this private network, each drone is assigned a private IP address, which is unique only within that specific local network. This approach significantly conserves public IP addresses and simplifies internal network configuration, as the private address space is vast and easily manageable. For instance, a swarm of 50 drones mapping a forest fire might all have private IPs like 10.0.0.1 through 10.0.0.50.
The Gateway to External Services and Remote Operations
When these drones, operating on their private network, need to communicate with the outside world—be it uploading collected sensor data to a cloud-based analytics platform, receiving updated flight plans from a remote operator via satellite link, or synchronizing their positions with a global GPS service—the NAT Gateway comes into play. The NAT Gateway, typically integrated into the GCS or a dedicated communication hub, holds a single public IP address.
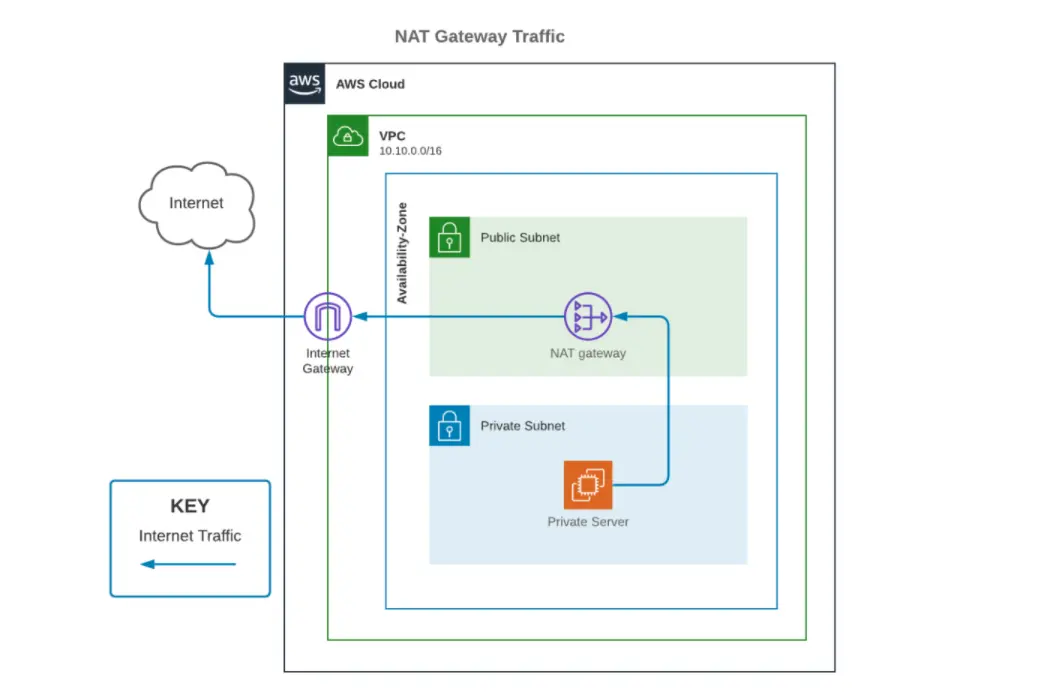
When a drone with a private IP (e.g., 10.0.0.15) sends data destined for a public cloud server, its request first reaches the NAT Gateway. The gateway then modifies the packet, replacing the drone’s private source IP address with its own public IP address. This “translated” packet is then forwarded to the internet. From the perspective of the public cloud server, the request originates from the NAT Gateway’s public IP, not from an individual drone.
Conversely, when the cloud server sends a response, it addresses the response to the NAT Gateway’s public IP. Upon receiving this response, the NAT Gateway consults its internal translation table, which maps active private-to-public connections. It then translates the destination IP address back to the correct private IP of the requesting drone (10.0.0.15) and forwards the response internally. This bidirectional translation ensures that all communication is seamless, despite the drones having only private network identities.
Benefits for Large-Scale Deployments
This architecture offers profound benefits for large-scale drone deployments. Firstly, it provides immense scalability. New drones can be easily added to or removed from the private network without the need to acquire new public IP addresses or reconfigure complex public routing tables. Secondly, it ensures resource efficiency by conserving the finite pool of public IPv4 addresses, which is particularly relevant in scenarios involving hundreds or thousands of networked devices. Lastly, it creates a simplified network architecture, centralizing external communication management through a single point, which streamlines troubleshooting and policy enforcement.
Enhancing Security and Control in Autonomous Drone Operations
Beyond merely enabling connectivity, a NAT Gateway plays a pivotal role in bolstering the security and control frameworks essential for autonomous drone operations. Given the sensitive nature of many drone missions—from surveillance and critical infrastructure inspection to package delivery—protecting the drone fleet from cyber threats is paramount.
A Shield for Internal Drone Networks
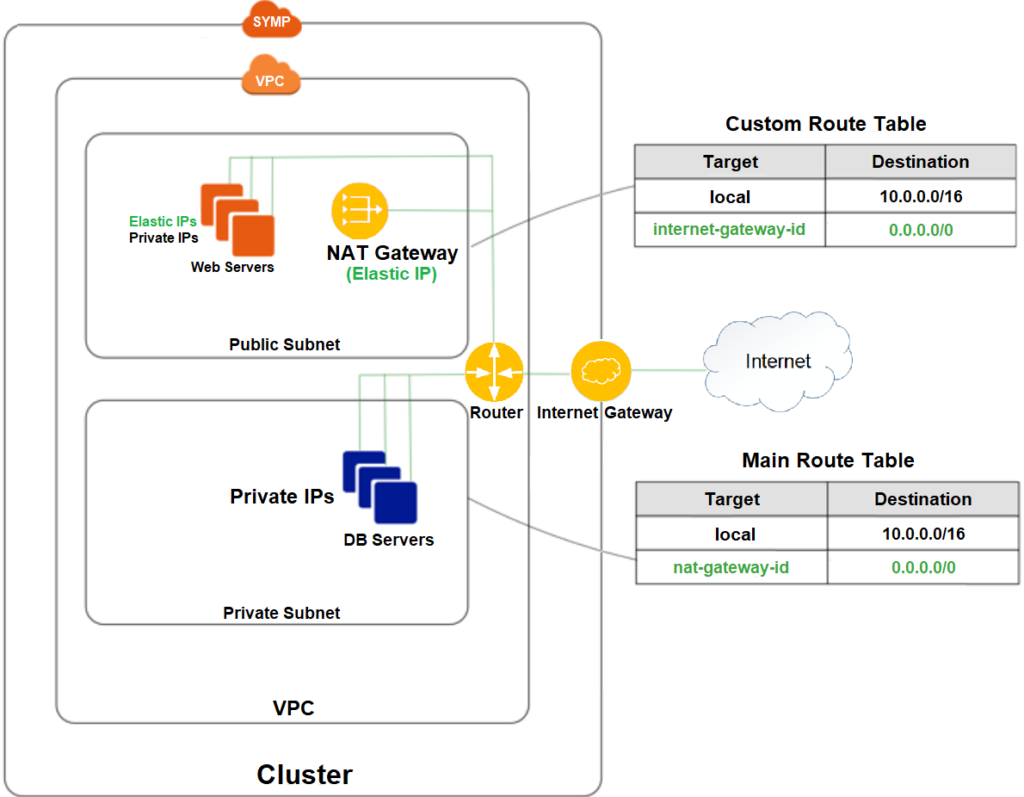
One of the most significant security advantages of a NAT Gateway is the layer of isolation it provides for internal drone networks. Since individual drones within a private network do not have publicly routable IP addresses, they are effectively “hidden” from the public internet. External entities, including potential malicious actors, cannot directly initiate connections to a specific private-addressed drone. Their visibility is limited to the public IP address of the NAT Gateway.
This architecture acts like a one-way mirror: drones can initiate outbound connections to the internet, but external systems cannot initiate unsolicited inbound connections directly to individual drones. This significantly reduces the attack surface for the drone fleet, making it much harder for cybercriminals to identify and exploit vulnerabilities in individual aircraft. Instead of hundreds of potential targets, attackers can only see one public-facing entry point—the robustly secured NAT Gateway.
Controlled Ingress and Egress
The NAT Gateway serves as a critical choke point for all communication between the private drone network and the public internet. This central position allows for the implementation of stringent security policies and controls. Network administrators can configure the NAT Gateway with detailed firewall rules, access control lists (ACLs), and even deep packet inspection capabilities.
This means that only authorized types of outbound data—such as encrypted telemetry streams, aggregated sensor readings, or authenticated status reports—are permitted to leave the drone network. Conversely, only legitimate and authenticated inbound commands, flight plan updates, or software patches are allowed to pass through the gateway and reach the appropriate drone. Any unauthorized data, suspicious command signals, or attempts at data exfiltration can be detected and blocked at this central point, preventing compromise of the drone’s operational integrity or the confidentiality of its collected data. This level of controlled ingress and egress is vital for sensitive applications where data integrity and command authenticity are non-negotiable.
NAT Principles in Swarm Intelligence and Edge Computing for Drones
The utility of NAT principles extends deeply into advanced drone paradigms like swarm intelligence and edge computing, illustrating its versatility beyond conventional networking setups. As drones become more autonomous and form collaborative units, managing their internal and external communication efficiently and securely is key.
Distributed NAT in Swarm Architectures
In sophisticated drone swarm operations, individual drones often communicate intensely among themselves to coordinate actions, share sensor data, and maintain formation. This intra-swarm communication typically occurs over a highly localized, private network. To reduce external network traffic, enhance responsiveness, and simplify external communication, a “leader” drone or a designated communication relay drone within the swarm can act as a miniature, distributed NAT Gateway.
This leader drone would manage the private IP addresses for its peer drones within the immediate swarm. When any drone in the swarm needs to send data to the ground control station or receive commands from a cloud-based AI system, it routes its traffic through the leader drone. The leader, equipped with a more robust communication link and a public IP (or acting as a proxy to a GCS with a public IP), performs the NAT function for the entire sub-swarm. This arrangement facilitates rapid and secure internal communication within the swarm, while streamlining and securing its interaction with external networks. It reduces the computational load on individual drones for external connectivity and simplifies network management for dynamic, autonomous swarms.
Edge Device as a NAT Proxy for Remote Sensing
Remote sensing missions, such as extensive environmental monitoring, large-scale geological surveys, or long-duration pipeline inspections, involve drones collecting vast amounts of raw data. Transmitting all this raw data directly to the cloud can be bandwidth-intensive and costly, especially in remote areas with limited connectivity. Here, an edge computing device, either onboard a larger drone acting as a data hub or deployed at a remote ground station, can implement NAT-like proxy functions.
This edge device not only processes and filters raw data locally, reducing the volume of data that needs to be transmitted, but also acts as a NAT Gateway for the data sources (individual sensors or sub-systems on multiple drones). The various data streams, originating from private addresses within the drone’s internal network or the local fleet, are consolidated and translated by the edge device. When transmitting processed or summarized data to a cloud storage or analytics platform, the edge device uses its single public IP, effectively representing multiple internal data sources. This optimizes bandwidth usage, reduces latency for critical data, and enhances the privacy of the internal data acquisition network by preventing direct exposure of individual sensor streams to the public internet.
The Future Landscape: 5G, IoT, and Ubiquitous Drone Connectivity
As drones become inextricably linked with 5G networks and the broader Internet of Things (IoT) ecosystem, the principles embodied by NAT Gateways will become even more critical. The sheer volume of interconnected devices, including swarms of drones, ground sensors, and smart city infrastructure, will necessitate intelligent and efficient network address management.
NAT-like functions will play a crucial role in navigating the transition from IPv4 to IPv6, ensuring backward compatibility and managing the vast address space requirements of future drone fleets. They will be fundamental in facilitating secure and scalable machine-to-machine (M2M) communication, enabling drones to seamlessly interact with other IoT devices in smart cities, industrial automation, and logistics networks. We can anticipate the development of advanced, software-defined NAT solutions, dynamically embedded directly into drone operating systems or integrated within 5G network slices specifically designed for UAS. These innovations will support increasingly dynamic, autonomous flight operations, real-time data exchange, and robust security postures, ultimately unlocking the full potential of ubiquitous drone connectivity in an ever more connected world.