
Cloud computing has revolutionized the landscape of technology and innovation, offering unprecedented scalability, flexibility, and cost-efficiency. It underpins much of the advancements seen in areas like artificial intelligence, autonomous systems, large-scale data processing for mapping, and remote sensing. However, this transformative power comes with a unique set of security challenges that organizations must meticulously address to protect their digital assets, maintain operational integrity, and foster continued innovation. Understanding these risks is paramount for any entity leveraging cloud infrastructure to drive technological progress.
The Evolving Landscape of Cloud Adoption and Shared Responsibilities
The rapid adoption of cloud services has shifted traditional IT security paradigms. No longer are all assets housed within a physical perimeter controlled solely by the organization. Instead, resources are distributed across powerful, often shared, infrastructures managed by third-party cloud providers. This distributed model necessitates a clear understanding of where security responsibilities lie, a concept formalized in the “Shared Responsibility Model.”
The Shared Responsibility Model Explained
In essence, cloud security is a partnership. The cloud service provider (CSP) is responsible for the security of the cloud – that is, the underlying infrastructure, hardware, networking, and virtualization that supports cloud services. This includes physical security of data centers, securing network infrastructure, and patching underlying hypervisors. Conversely, the customer is responsible for the security in the cloud – encompassing everything they put into or build within the cloud environment. This typically includes data, applications, operating systems (if managed by the customer), network configurations, access management, and client-side encryption. The exact demarcation points vary depending on the service model (IaaS, PaaS, SaaS). For IaaS, customers bear more responsibility, whereas for SaaS, the CSP shoulders a larger share. Misunderstanding this model is a foundational security risk, as it often leads to neglected security controls by the customer, assuming the provider handles everything.
Implications for Emerging Technologies
For fields heavily reliant on cloud resources, such as AI development, autonomous flight planning, or advanced remote sensing data analysis, the implications of this shared responsibility are profound. The vast datasets collected for mapping or training AI models, the proprietary algorithms developed, and the sensitive operational parameters for autonomous systems all reside “in the cloud.” If these are not adequately secured by the customer’s configuration, access controls, and data management practices, even the most robust security of the cloud by the CSP will not prevent a breach. Innovation thrives on data and connectivity, making secure cloud environments indispensable for safeguarding intellectual property and ensuring the reliability of cutting-edge applications.
Key Vulnerabilities and Threats in Cloud Environments
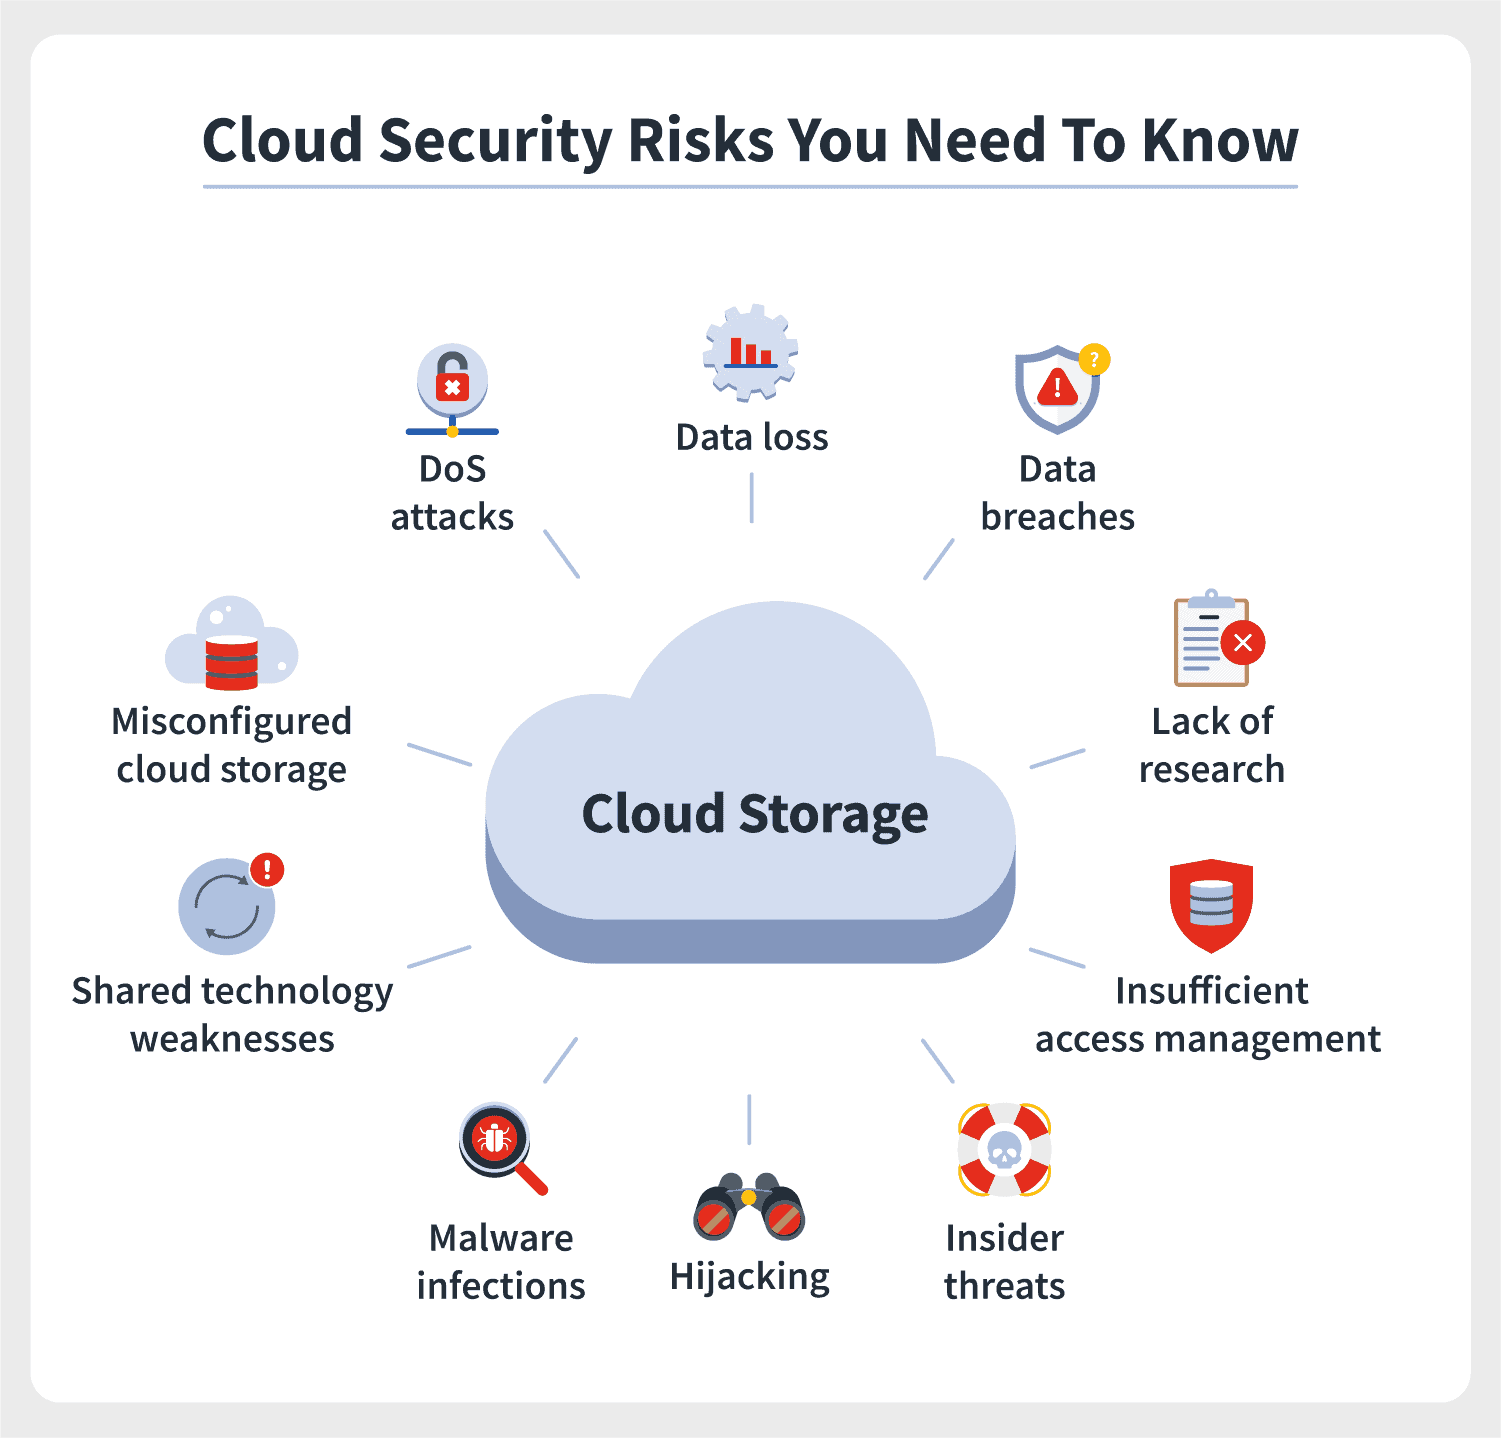
Despite the robust security measures implemented by major CSPs, specific vulnerabilities and threats persistently challenge cloud users. These risks often stem from human error, misconfiguration, or sophisticated attack vectors targeting the unique architecture of cloud platforms.
Data Breaches and Leakage
This remains one of the most significant and feared risks. Data breaches in the cloud can occur due to weak access controls, misconfigured storage buckets (e.g., S3 buckets left publicly accessible), insecure APIs, or compromised credentials. The vast quantities of sensitive data often stored in cloud environments – from personal identifiable information (PII) to proprietary business intelligence and sensor data – make them prime targets. A single breach can lead to massive financial losses, reputational damage, and legal penalties, particularly for data-intensive innovations like those in mapping and remote sensing that often handle vast geospatial datasets or critical infrastructure information.
Identity and Access Management (IAM) Weaknesses
Poorly managed IAM is a primary vector for cloud attacks. This includes weak passwords, lack of multi-factor authentication (MFA), over-provisioned permissions, and failure to regularly review access rights. Attackers exploiting IAM weaknesses can gain unauthorized access to cloud resources, escalate privileges, and move laterally across an organization’s cloud infrastructure, leading to data exfiltration or service disruption. In the context of autonomous systems, compromised IAM could theoretically enable unauthorized modification of operational parameters or access to critical command-and-control functions, posing severe safety and security risks.
Misconfiguration and Inadequate Change Control
Cloud environments are complex and highly configurable. This flexibility, while powerful, also presents a significant risk if not managed correctly. Misconfigurations of security groups, network access control lists (ACLs), firewall rules, storage settings, and even serverless function permissions are common. Developers and operations teams, under pressure to deploy rapidly, may inadvertently leave security gaps. Lack of robust change control processes can exacerbate this, making it difficult to track and correct insecure configurations, leaving systems exposed to known vulnerabilities.
Insecure APIs and Interfaces
Cloud services are fundamentally API-driven. APIs are how users and applications interact with cloud resources, and if these interfaces are not properly secured, they can become entry points for attackers. This includes weak authentication for APIs, lack of encryption, improper input validation, and insufficient logging. As AI and autonomous systems increasingly rely on microservices architectures communicating via APIs in the cloud, securing these interfaces is crucial to prevent unauthorized access, data manipulation, or denial-of-service attacks against critical components.
Advanced Persistent Threats and Supply Chain Risks
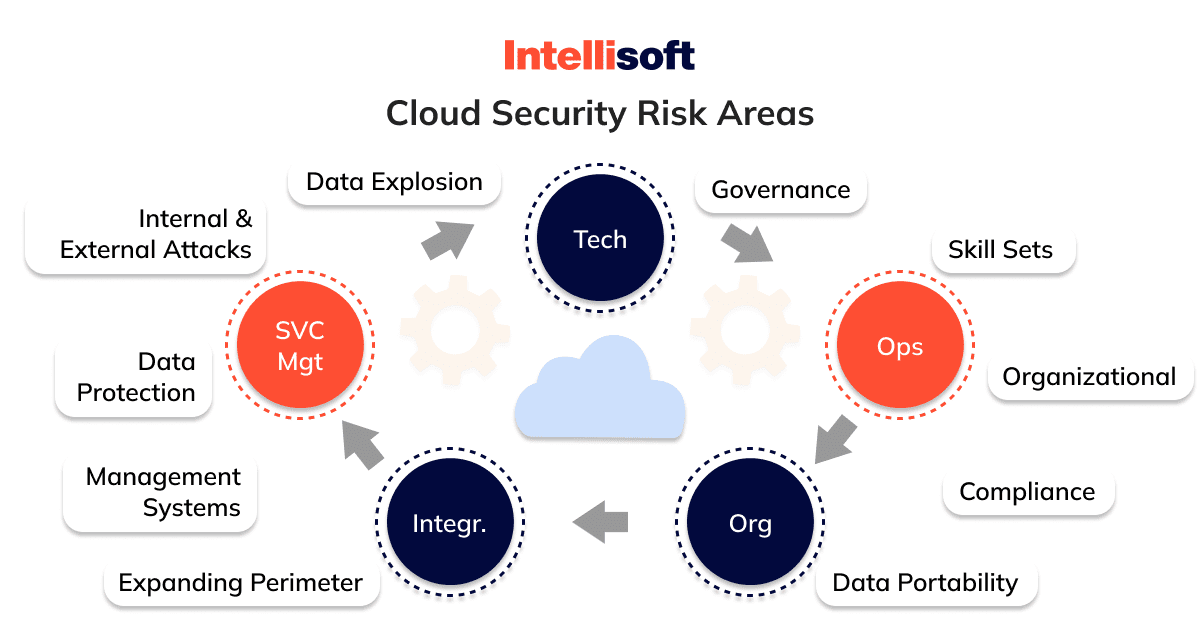
Cloud environments are not immune to sophisticated, long-term attacks. Advanced Persistent Threats (APTs) can leverage compromised credentials, zero-day vulnerabilities, or social engineering to establish a foothold and remain undetected for extended periods, continuously exfiltrating data or disrupting operations. Furthermore, the cloud supply chain introduces its own set of risks. If third-party services, libraries, or tools integrated into cloud applications have vulnerabilities, these can be inherited by the user, creating cascading security issues. This is particularly relevant for innovative solutions that often integrate various open-source components and third-party APIs.
Data Sovereignty, Privacy, and Regulatory Compliance
Beyond technical vulnerabilities, cloud computing introduces complex legal and regulatory challenges, particularly concerning data residency, privacy, and compliance. These are critical considerations for organizations pushing the boundaries of technology, often handling sensitive or regulated data.
Navigating Global Data Protection Laws
Data stored in the cloud can reside in data centers located in different geographical regions or even across international borders. This raises significant concerns regarding data sovereignty and privacy regulations, such as the General Data Protection Regulation (GDPR) in Europe, the California Consumer Privacy Act (CCPA), and numerous industry-specific compliance mandates (e.g., HIPAA for healthcare, PCI DSS for payment processing). Organizations must understand where their data is stored, how it is processed, and ensure their cloud architecture and data handling practices comply with all relevant laws, both in their operating jurisdiction and where their data physically resides. Failure to do so can result in hefty fines and legal repercussions, hindering market adoption for new innovations.
Ensuring Data Integrity and Availability
The integrity and availability of data are paramount for any technological endeavor. In the cloud, risks to integrity can stem from unauthorized modifications, corruption during transfer, or inadequate backup and recovery strategies. Availability can be impacted by denial-of-service attacks, regional outages, or provider-side issues. While CSPs offer high availability and redundancy, customers must still implement their own robust data lifecycle management, backup policies, and disaster recovery plans tailored to their specific applications and recovery time objectives (RTOs) and recovery point objectives (RPOs). For autonomous systems relying on real-time data or remote sensing applications requiring uninterrupted data streams, maintaining integrity and availability is non-negotiable for operational safety and reliability.
The Challenge of Cloud Forensics and Incident Response
When a security incident occurs in a cloud environment, conducting thorough forensics and implementing an effective incident response can be more challenging than in on-premise setups. Access to underlying infrastructure logs may be limited by the CSP’s shared responsibility model. Collecting comprehensive forensic data often requires specific cloud-native tools and expertise, and the ephemeral nature of some cloud resources can complicate post-incident analysis. Organizations need well-defined cloud-specific incident response plans, including clear communication protocols with their CSP, to minimize damage and restore operations swiftly.
Strategic Mitigation: Securing Innovation in the Cloud Era
Addressing cloud security risks effectively requires a multi-faceted and proactive approach. It involves a combination of robust technological controls, stringent policy enforcement, and a strong security-aware culture. By strategically mitigating these risks, organizations can fully harness the innovative power of cloud computing while safeguarding their assets and reputation.
Adopting a Zero Trust Approach
A Zero Trust security model, where no user, device, or application is inherently trusted, regardless of its location, is increasingly vital in cloud environments. This approach mandates strict identity verification for every access request, least-privilege access, continuous authentication, and micro-segmentation of networks. Implementing Zero Trust principles helps prevent lateral movement of attackers within the cloud infrastructure, significantly reducing the impact of compromised credentials or misconfigurations. For dynamic and interconnected innovative systems, Zero Trust provides a critical layer of defense.
Continuous Security Monitoring and Automation
Given the dynamic nature of cloud environments, continuous security monitoring is essential. This includes real-time logging, threat detection, and vulnerability scanning. Leveraging Security Information and Event Management (SIEM) systems and Cloud Security Posture Management (CSPM) tools can help identify misconfigurations, suspicious activities, and compliance deviations automatically. Automation plays a critical role in responding to threats rapidly, patching vulnerabilities, and ensuring consistent security policies across ephemeral resources, which is especially important for agile development and deployment cycles inherent in tech innovation.
Leveraging Cloud-Native Security Tools and Expertise
Major CSPs offer a rich suite of integrated security services, including firewalls, IAM solutions, encryption services, and threat detection tools. Organizations should leverage these cloud-native capabilities, as they are often optimized for the underlying infrastructure and can provide seamless integration. Furthermore, investing in or partnering with cloud security specialists is crucial. These experts understand the nuances of cloud architecture, the shared responsibility model, and the specific security challenges posed by advanced cloud deployments, providing invaluable guidance for securing complex innovative applications.
Building a Culture of Security
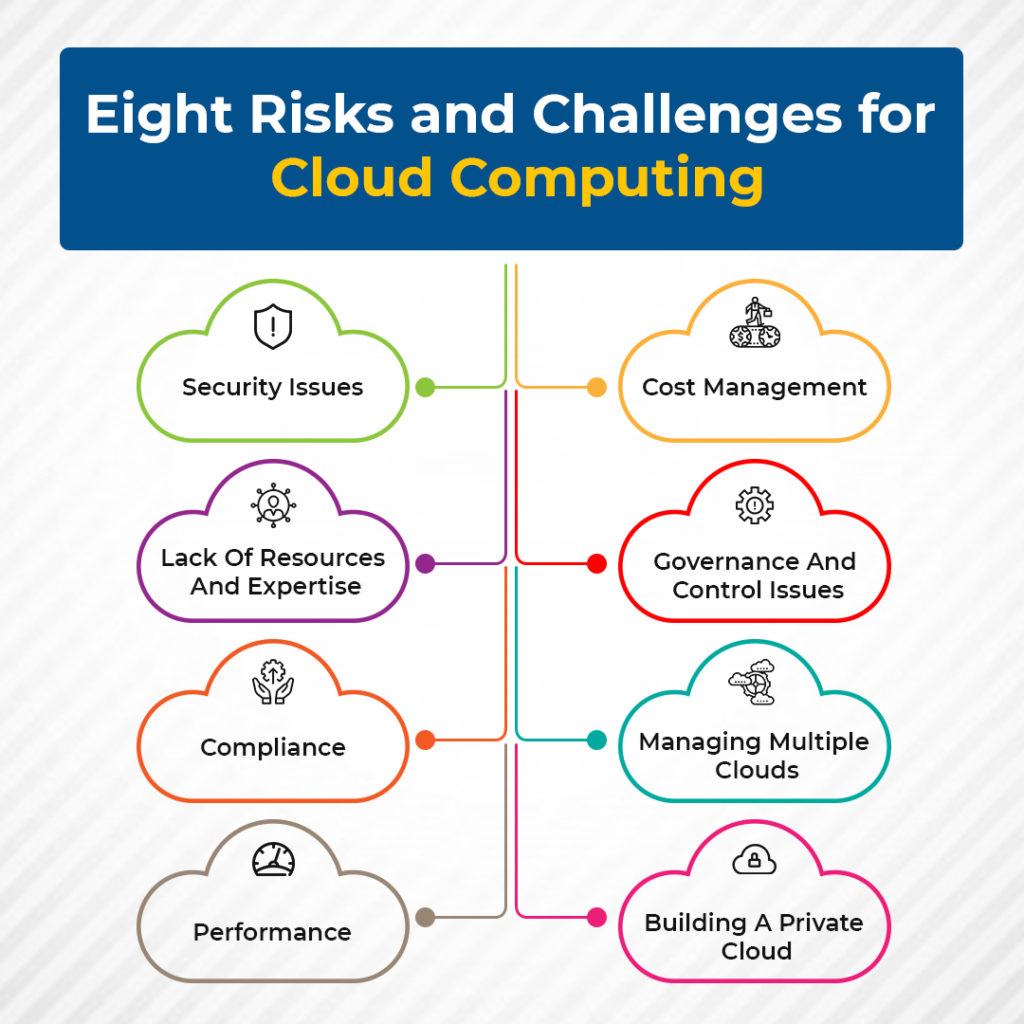
Ultimately, technology alone cannot ensure cloud security. Human factors, such as developer awareness, operational discipline, and user behavior, play a significant role. Fostering a strong culture of security through continuous training, regular security awareness programs, and embedding security practices into the entire software development lifecycle (DevSecOps) is critical. Educating teams on the shared responsibility model, secure coding practices, and the importance of adhering to security policies empowers them to become proactive participants in maintaining a secure cloud environment, thereby enabling responsible innovation. By prioritizing security from the ground up, organizations can confidently explore new technological frontiers enabled by the cloud.