
The landscape of drone technology has evolved dramatically, transforming unmanned aerial vehicles (UAVs) from mere remote-controlled gadgets into sophisticated, networked devices. Today, drones are integral to advanced applications like precision mapping, remote sensing, autonomous surveillance, and AI-driven inspections. This evolution means that the digital infrastructure supporting these operations – from ground control stations (GCS) to cloud-based data processing platforms – is more critical than ever. Understanding and managing network ports is a foundational element of ensuring secure, reliable, and high-performing drone operations within the realm of tech and innovation.
The Critical Role of Network Ports in Advanced Drone Systems
Network ports are logical endpoints that identify distinct services or processes on a networked device. In essence, they are like numbered doors on a digital building, allowing specific types of information to enter or exit. For advanced drone systems, these ports are the conduits for a vast array of critical communications.
Modern drones are no longer standalone entities. They are often deeply integrated into complex technological ecosystems. Consider a drone deployed for a large-scale agricultural mapping project. It might transmit high-resolution imagery and telemetry data in real-time to a ground control station. From there, this data could be relayed to a cloud server for AI-driven analysis, such as identifying crop health anomalies or predicting yields. Each step in this process relies on specific network ports being open and correctly configured, facilitating everything from MAVLink communication for flight control to RTP/RTSP for video streaming, or HTTPS for secure data uploads to a mapping platform.
Autonomous flight systems, for example, depend on constant, low-latency communication between the drone’s onboard flight controller, its mission planning software, and potentially external AI modules providing real-time trajectory adjustments or obstacle avoidance data. These sophisticated interactions frequently leverage established network protocols over specific ports. Similarly, remote sensing applications demand robust data pipelines to transmit vast amounts of LiDAR, hyperspectral, or thermal imaging data. Any disruption or misconfiguration of these ports can lead to mission failure, data loss, or even compromise the safety of operations. Therefore, recognizing which ports are active and what services they facilitate is paramount for developers, operators, and security professionals in the drone technology space.
Why Understanding Open Ports is Essential for Drone Tech & Innovation
In the dynamic world of drone tech and innovation, the ability to identify and manage open network ports extends beyond mere technical curiosity; it’s a strategic imperative. From safeguarding sensitive data to ensuring seamless integration with cutting-edge AI and mapping solutions, the security and efficiency of port configurations directly impact operational success.
Enhancing Security for Drone Deployments
One of the most pressing concerns in any networked system is security, and drone systems are no exception. An open port that is not actively secured or monitored represents a potential vulnerability. For enterprise drone fleets, which might be collecting proprietary data, conducting critical infrastructure inspections, or operating in sensitive environments, an exposed port could be an invitation for unauthorized access, data interception, or even malicious control. For instance, a ground control station connected to a corporate network, if left with unnecessary ports open, could become an entry point for cyber attackers to pivot into the drone system or even deeper into the company’s infrastructure. Regularly checking what ports are open allows teams to identify and close unnecessary ports, fortify those that must remain open with strong authentication and encryption, and proactively mitigate risks before they can be exploited. This is especially crucial for drones designed for autonomous flight or AI follow modes, where the integrity of control signals and data streams is paramount.
Streamlining Troubleshooting and Connectivity Diagnostics
Connectivity is the lifeblood of advanced drone operations. When a drone fails to connect to its ground station, a video feed lags, or data uploads stall, the first point of investigation often involves network communication. Open ports play a direct role here. If a particular service, like a telemetry link or a live video feed, isn’t functioning, checking whether the designated port for that service is indeed open and accessible on both ends (e.g., the drone’s companion computer and the GCS) can quickly pinpoint the problem. Blocked ports, misconfigured firewalls, or incorrect port forwarding can all lead to connectivity issues that halt missions. For complex integrations involving multiple drone platforms, cloud services, and custom applications, understanding the port landscape is critical for rapid fault isolation and resolution, ensuring minimal downtime and maximum operational efficiency.
Facilitating Seamless System Integration
The future of drone technology lies in its ability to integrate with broader technological ecosystems. This includes connecting with remote sensing platforms, integrating with geographic information systems (GIS) for mapping, feeding data into AI/ML pipelines for predictive analytics, or linking with IoT systems for environmental monitoring. Each of these integrations typically requires specific network services to communicate over predefined ports. For example, a custom mapping application might listen on a particular port for incoming processed data from a drone’s cloud service. Knowing which ports are open and available, and how to configure them for specific services, is fundamental to designing and implementing these complex, multi-component drone solutions. Without this understanding, achieving interoperability and creating truly innovative drone applications becomes significantly more challenging.
Practical Methods for Identifying Open Ports in a Drone Ecosystem
To effectively manage the network footprint of advanced drone systems, practical tools and techniques are indispensable. These methods allow operators and developers to systematically examine which ports are active, aiding both security posture and troubleshooting efforts within the drone tech and innovation context.
Network Scanning Tools for Drone-Related Discovery
Dedicated network scanning tools are the cornerstone of port identification. These applications probe a target host or network range to determine which ports are open and often which services are running on those ports.
Using Nmap for Drone-Related Network Discovery
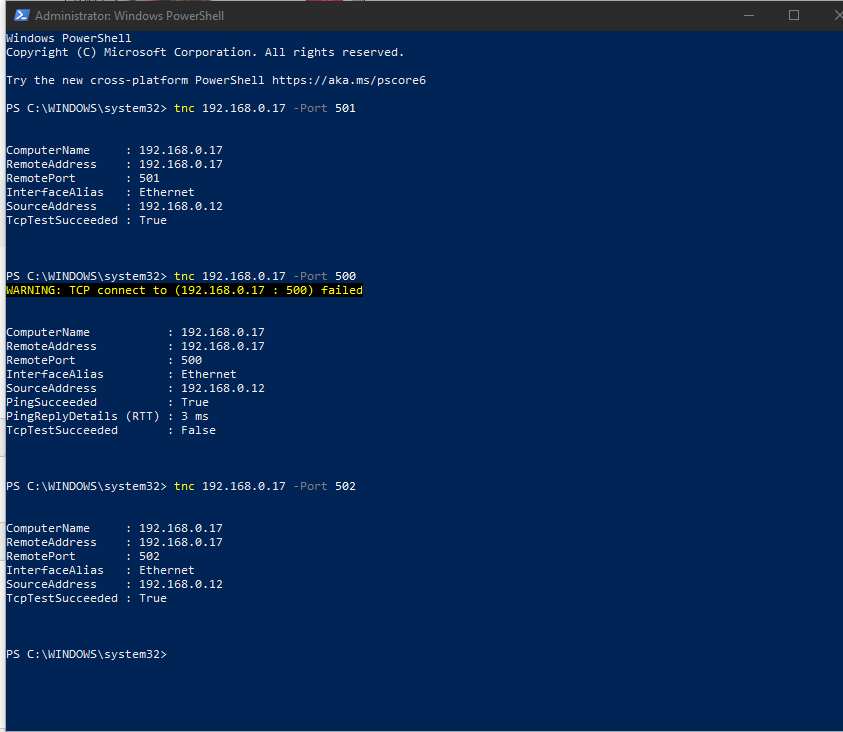
Nmap (Network Mapper) is an open-source utility that is incredibly versatile for network discovery and security auditing. When applied to drone ecosystems, Nmap can be used to scan the IP addresses of ground control stations, companion computers on drones (if they have an accessible IP on a network), or servers hosting drone-related services (like mapping platforms or data repositories).
- Basic Scan: To identify open ports on a specific host, you can use
nmap [target IP address]. For instance,nmap 192.168.1.100would scan the GCS with that IP. This will often reveal commonly open ports. - Service Version Detection: For a more insightful scan,
nmap -sV [target IP address]attempts to determine the service name and version running on each open port. This is crucial for identifying potential vulnerabilities associated with outdated software. - Scanning Specific Ports: If you’re looking for a particular drone communication port (e.g., a custom telemetry port or a video streaming port), you can specify it:
nmap -p 8080,9000-9010 [target IP address]. - Scanning a Subnet: To discover all active hosts and their open ports within a drone deployment network,
nmap 192.168.1.0/24would scan an entire subnet.
For cloud-hosted drone services, ensure you have proper authorization before scanning, as unauthorized scanning can be flagged as malicious activity. Nmap also has a graphical front-end called Zenmap, which provides an easier-to-use interface for those less comfortable with the command line.
Operating System Utilities for Local Port Checks
Beyond network-wide scans, the operating systems of ground control stations or drone companion computers often have built-in utilities to inspect locally open ports and connections.
Local Port Checks on GCS and Companion Computers
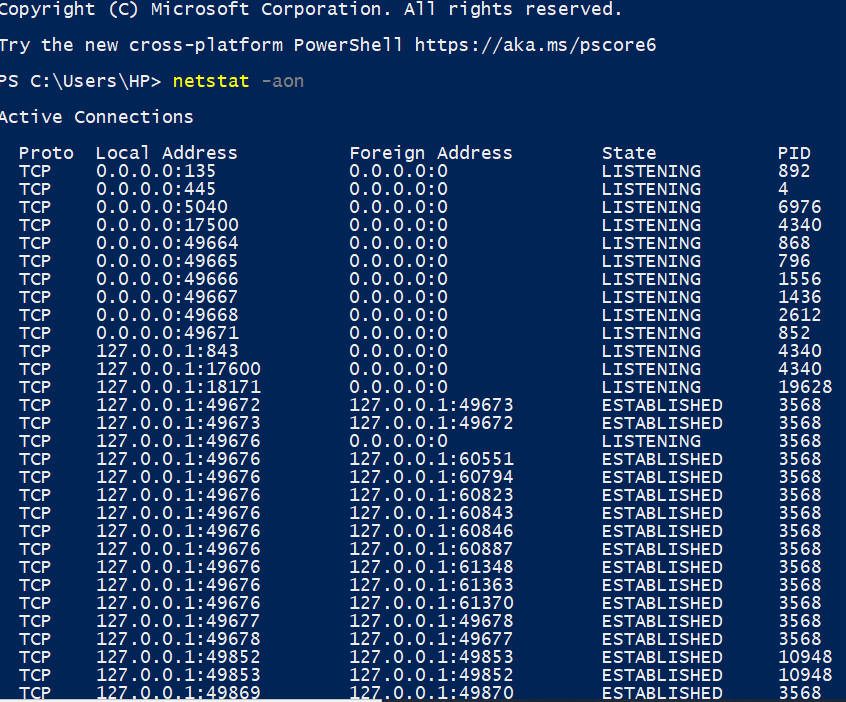
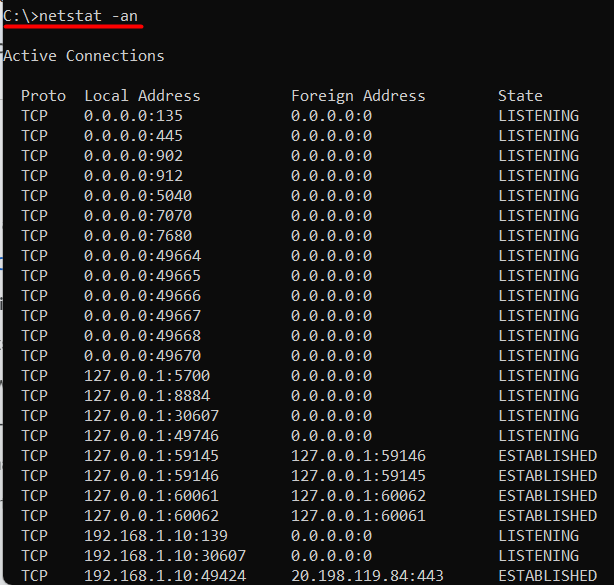
netstat(Windows, Linux, macOS): This command displays active network connections, routing tables, and a variety of network interface statistics.netstat -tulnp(Linux): Shows TCP and UDP listening ports (-t,-u), numeric addresses (-n), and the process ID/name (-p). This is highly useful for seeing which drone software or GCS application is listening on which port.netstat -ano(Windows): Shows all connections and listening ports, along with the process ID (PID) that opened the port. You can then use Task Manager to identify the application associated with the PID.
ss(Linux): A more modern and faster alternative tonetstatfor Linux systems.ss -tulnp: Provides similar output tonetstat, showing listening TCP and UDP sockets with associated processes.
lsof -i(Linux, macOS): “List open files” can also list network connections.lsof -i :<port_number>: Will show processes using a specific port.lsof -i -P -n: Lists all open network files/sockets.
These utilities are invaluable for diagnosing connectivity issues directly on the machine running drone control software or data processing applications, ensuring that the expected services are indeed listening on their designated ports.
Firewall Configuration Review
Firewalls, whether software-based on a GCS or hardware-based at a network gateway, are designed to control network traffic by blocking or allowing specific ports. Reviewing firewall rules is crucial because a port might appear “closed” from a network scan, but it’s simply being blocked by a firewall, not necessarily because no service is listening. For cloud-based drone services, checking security group rules and network access control lists (NACLs) is equally important. Ensure that necessary inbound and outbound rules are configured for drone telemetry, video feeds, and data uploads, while strictly limiting access on other ports.
Router/Gateway Port Forwarding Settings
For drone operations that require remote access to a ground station or a drone-connected server situated behind a router (e.g., in a local office network), port forwarding becomes relevant. This involves configuring the router to direct incoming traffic on a specific external port to an internal IP address and port. Incorrect port forwarding can lead to connectivity failures, while overly permissive rules can expose internal systems to the internet. Always review these settings to ensure they align with the minimum necessary access.
Securing Your Drone’s Network Footprint
Identifying open ports is merely the first step; the true value lies in using this knowledge to enhance the security and integrity of your drone operations. In the domain of Tech & Innovation, proactive security measures are paramount for protecting advanced systems and data.
Principle of Least Privilege: A fundamental security tenet is to operate with the least necessary privileges. For network ports, this translates to closing any port that isn’t absolutely required for drone system functionality. Every unnecessary open port is an attack surface. Conduct regular audits using the methods outlined above to identify and disable superfluous services or close unused ports.
Strong Authentication and Encryption: For ports that must remain open (e.g., for ground control communication, data streaming, or cloud integration), implement robust security measures. This includes using strong, unique passwords for any accessible services, implementing multi-factor authentication (MFA) where possible, and employing encryption protocols (like TLS/SSL for web traffic, SSH for remote access, or VPNs) to protect data in transit. Ensure that drone telemetry and control channels are encrypted to prevent signal hijacking or data eavesdropping.
Robust Firewall Rules: Beyond merely reviewing existing firewall configurations, actively define and enforce strict firewall rules. On ground control stations, configure software firewalls (like Windows Defender Firewall or Linux’s UFW/iptables) to allow only specific, trusted IP addresses or networks to access necessary ports. For network gateways or cloud environments, configure security groups and network access control lists to be as restrictive as possible, permitting traffic only on essential ports from authorized sources.
Regular Security Audits: The network landscape of a drone ecosystem can change. New software might be installed, configurations might be altered, or vulnerabilities might emerge. Schedule periodic security audits to re-evaluate open ports, review firewall rules, and check for any unauthorized changes. Automated scanning tools can be integrated into a continuous monitoring strategy to alert administrators to unexpected port openings.
Utilize Virtual Private Networks (VPNs): When remote access to a ground control station or drone server is required, a VPN provides a secure, encrypted tunnel over public networks. This creates an additional layer of security, effectively making remote connections appear as if they are originating from within the secure internal network, protecting against interception and unauthorized access to open ports.
By diligently applying these security best practices in conjunction with regular port monitoring, organizations can significantly strengthen the resilience and trustworthiness of their advanced drone technology deployments, safeguarding valuable data and ensuring the uninterrupted execution of critical missions.