
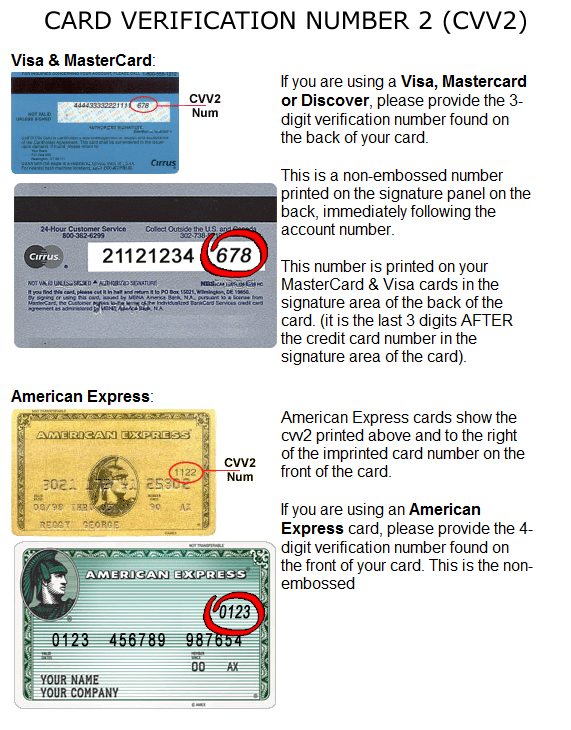
The Card Security Code (CSC), often labeled as CVV2 (Card Verification Value 2) for Visa, CVC2 (Card Verification Code 2) for Mastercard, or CID (Card Identification Number) for American Express, represents a critical element in the architecture of modern payment security. At its core, the CSC is a unique, three or four-digit number typically found on the back of credit and debit cards, separate from the primary account number. Its fundamental purpose is to provide an additional layer of security for “card-not-present” transactions, such as online purchases or telephone orders, where the physical card cannot be swiped or inserted.
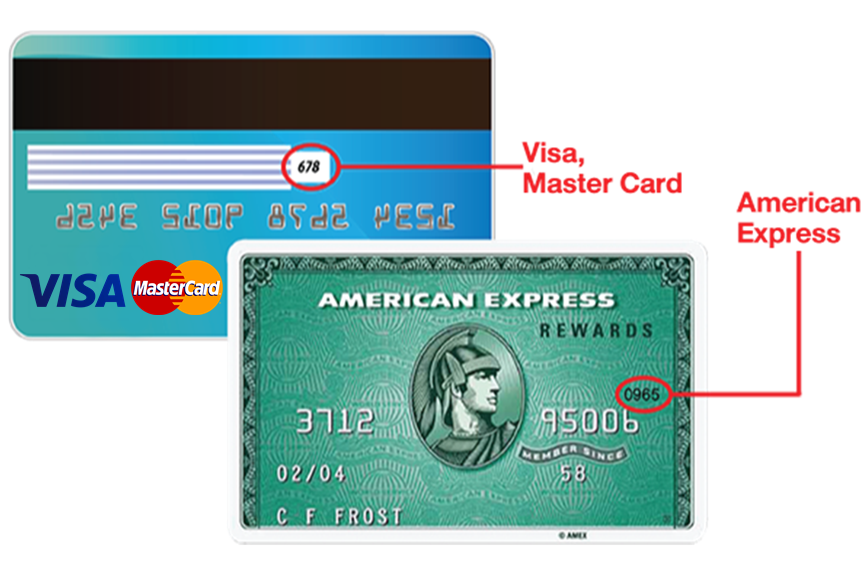
Unlike the card number and expiration date, the CSC is not encoded in the magnetic stripe of the card, nor is it embossed on the front. This design choice is deliberate, ensuring that if a card’s magnetic stripe data is compromised, the CSC remains protected, thus preventing fraudsters from easily making unauthorized remote purchases. When a customer provides their CSC during an online transaction, it serves as a real-time verification that they are in possession of the physical card, significantly reducing the risk of fraud and building a vital layer of trust between the consumer, merchant, and financial institution. This straightforward yet highly effective mechanism underpins countless digital transactions daily, safeguarding both consumer assets and the integrity of global financial networks.
The Fundamental Principle of Verification
The concept embodied by the Credit Card CSC—a unique, sensitive, and context-specific verification datum—extends far beyond financial transactions, serving as a foundational principle across various domains of advanced technology and innovation. At its heart, the CSC represents a simple yet powerful idea: an independent factor used to confirm the legitimacy of an action or identity when direct, physical presence or authentication is impractical or impossible. This principle is not confined to commerce but is a cornerstone for securing the integrity and reliability of autonomous systems, safeguarding sensitive data, and ensuring trustworthy operations in a world increasingly reliant on remote interaction and automated processes.
In the realm of advanced technology, the need for such verification is paramount. Imagine autonomous drones operating over sensitive areas, collecting critical mapping data or performing remote sensing tasks. How does one ensure that the commands sent to these drones are legitimate, originating from an authorized operator, and that the data they transmit back has not been tampered with? This is where the underlying philosophy of the CSC finds profound relevance. It’s about establishing a “root of trust” for every interaction, every data point, and every command within complex systems, mimicking the financial world’s need to verify the cardholder’s legitimate possession of their card.
Translating Security Principles to Advanced Technologies
The core idea of a CSC—a sensitive, non-persistent, and unique verification datum—finds compelling parallels across various domains of tech and innovation, especially in the context of drones, flight technology, and remote operations. Just as a credit card CSC authenticates the cardholder for a transaction, analogous security codes and protocols are vital for authenticating devices, commands, and data streams in sophisticated technological ecosystems. This involves ensuring that only authorized entities can initiate actions, access sensitive information, or control critical systems.
Securing Autonomous Flight and Data Integrity
In drone operations, the principle of a “CSC-like” identifier is crucial for maintaining command and control integrity. Imagine a scenario where malicious actors intercept or spoof drone control signals. Without robust authentication, they could hijack a drone, alter its flight path, or even commandeer it for nefarious purposes. Here, cryptographic keys and secure tokens function as the drone world’s “CSC,” ensuring that flight commands originate from authenticated ground control stations. These digital signatures verify the sender’s identity and confirm that the instructions have not been tampered with in transit.
Beyond command, data integrity is paramount, particularly for drones engaged in mapping, remote sensing, and aerial inspections. The raw data—be it high-resolution imagery, thermal scans, or LiDAR point clouds—often holds significant commercial or strategic value. A “CSC-like” verification system ensures that this data, once collected, remains unaltered from the point of capture through processing and storage. This might involve embedding cryptographic hashes at the point of origin, creating an unchangeable digital fingerprint that can be verified at any stage. Such measures are vital for applications like AI Follow Mode, where real-time data integrity ensures the drone accurately tracks its subject without interference, or in precision navigation, where the smallest data corruption could lead to significant deviations.

Blockchain and Immutable Records
The emergence of distributed ledger technologies, such as blockchain, offers a revolutionary, “CSC-like” system for verifying the authenticity and history of operations in drone technology. Each flight, data capture event, or maintenance log can be recorded as a transaction on a blockchain. This record is timestamped, cryptographically secured, and linked to previous transactions, forming an immutable chain. This parallels the non-alterable nature of a CSC, but on a systemic level.
For drones, this means creating an auditable, transparent, and tamper-proof ledger of all activities. For instance, in aerial inspections of critical infrastructure, every image taken, every anomaly detected, and every flight parameter recorded can be immutably stored. This enhances trust and accountability, providing verifiable proof of compliance, mission execution, and data provenance. Should questions arise about a drone’s flight path, its sensor readings, or the chain of custody for collected data, the blockchain provides an indisputable “CSC-like” record, solidifying the integrity of operations and the trustworthiness of autonomous systems.
The Imperative of Multi-Layered Security
Modern technological landscapes, especially those involving sophisticated machinery like drones and critical data streams, demand far more than a single “CSC” for robust security. They necessitate a multi-layered approach, integrating hardware, software, and procedural safeguards to create a resilient defense against an evolving array of threats. Just as a credit card’s CSC is but one component in a broader financial security framework, analogous security measures for drones must be holistic.
Hardware-Based Security Modules
A cornerstone of this multi-layered approach involves hardware-based security modules. Technologies such as Trusted Platform Modules (TPMs) or Secure Elements (SEs) are increasingly being integrated into drones and their associated ground control systems. These modules act as highly secure “CSCs” for the device itself, storing cryptographic keys, digital certificates, and boot measurements in a tamper-resistant environment. They establish a “root of trust” by verifying the integrity of the drone’s firmware and software before execution. If any unauthorized modification is detected during the boot process, the drone can refuse to operate or enter a secure recovery mode, effectively preventing malicious code from taking control. This is analogous to a credit card terminal verifying the physical security features of a card before processing a transaction, ensuring the device itself is legitimate and untampered with.
Protecting Intellectual Property and Sensitive Information
Drones are powerful tools for data acquisition, often capturing highly sensitive information, whether it pertains to industrial espionage prevention, safeguarding governmental surveillance data, or protecting personal privacy. The principle of the CSC extends here to protecting access to this invaluable data. Encryption of data both in transit and at rest, coupled with strong authentication protocols, ensures that only authorized entities can decrypt, view, or process the captured information. This involves not only secure storage but also secure processing environments and stringent access controls based on roles and permissions. Furthermore, secure communication channels, utilizing end-to-end encryption, prevent eavesdropping or interception of critical command signals or data feeds, establishing a robust digital perimeter around sensitive operations.
Evolving Threats and Future-Proofing Security
The landscape of technology is a constant arms race between innovation and exploitation. As drones become more autonomous and their applications more critical, the methods employed by malicious actors grow increasingly sophisticated. Consequently, the concept of a “CSC” within this domain must also continuously evolve. It’s not a static three-digit number but a dynamic set of principles and technologies designed to adapt to emerging threats.
Future-proofing security involves a commitment to continuous updates, algorithm evolution, and the adoption of cutting-edge cryptographic techniques, including a move towards post-quantum cryptography to withstand the theoretical threats posed by future quantum computers. The underlying principle of a CSC—a unique, difficult-to-replicate, and crucial verification factor—remains relevant. However, its implementation will rely on advanced biometrics for operator authentication, AI-driven anomaly detection to identify unusual flight patterns or communication disruptions, and self-healing security architectures that can automatically detect and neutralize threats. Emphasizing adaptation, resilience, and proactive threat intelligence will be key to ensuring that the integrity and security of drone operations and the sensitive data they handle remain uncompromised in an ever-changing digital frontier.