
In an increasingly interconnected digital landscape, the quest for robust security measures remains paramount. As technologies evolve, from autonomous flight systems to advanced remote sensing platforms, the need to protect sensitive data and access points intensifies. At the forefront of this battle against cyber threats stands the hardware token, a dedicated physical device designed to enhance digital authentication beyond the traditional username and password. Representing a significant innovation in cybersecurity, these tokens serve as a critical second, or even third, factor in verifying a user’s identity, making unauthorized access substantially more difficult.
The Foundation of Enhanced Authentication: Moving Beyond Passwords
Traditional authentication, reliant solely on something a user knows (like a password), has proven to be increasingly vulnerable. The digital age has brought with it an escalating sophistication in cyber-attacks, ranging from brute-force attempts and phishing schemes to sophisticated malware designed to steal credentials. Passwords, no matter how complex, can be compromised through various vectors, leaving accounts and the sensitive data they protect exposed. This inherent weakness necessitated a paradigm shift in how we verify digital identities, paving the way for multi-factor authentication (MFA) and the pivotal role of hardware tokens.
The Vulnerability of Single-Factor Authentication
The fundamental flaw of single-factor authentication lies in its singular point of failure. A stolen password, whether through a data breach, a phishing email, or a simple guess, grants an attacker immediate entry. This vulnerability is exacerbated by common user behaviors, such as reusing passwords across multiple services or choosing easily decipherable combinations. For critical systems, especially those managing high-value assets or sensitive operational data pertinent to modern technological applications like drone fleet management, sophisticated mapping projects, or confidential remote sensing data, relying solely on passwords is an unacceptable risk. The potential for catastrophic data loss, operational disruption, or even physical security breaches stemming from compromised accounts underscores the urgent need for stronger defenses.
Introducing the Second Factor: Something You Have
Multi-factor authentication addresses the shortcomings of single-factor methods by requiring users to provide two or more distinct pieces of evidence to verify their identity. These “factors” typically fall into three categories: something you know (like a password or PIN), something you have (like a hardware token or smartphone), and something you are (like a fingerprint or facial scan). Hardware tokens exemplify the “something you have” factor. By integrating a physical device into the authentication process, they introduce a tangible barrier that an attacker, even with a stolen password, cannot easily circumvent. This physical possession requirement transforms the security landscape, making it exponentially harder for remote adversaries to gain unauthorized access. The token acts as a cryptographic key, often generating unique, time-sensitive codes or responding to cryptographic challenges, thereby proving the legitimate user’s presence.
Diverse Manifestations: Exploring Types of Hardware Tokens
The realm of hardware tokens is diverse, with various forms tailored to different use cases, security requirements, and user experiences. Each type, while serving the overarching goal of enhanced authentication, employs distinct mechanisms and physical designs. Understanding these variations is crucial for appreciating their broad applicability across a spectrum of technological environments.
USB Security Keys
Perhaps the most recognizable form of modern hardware tokens, USB security keys are compact devices that plug directly into a computer’s USB port. These keys often support industry standards such as FIDO (Fast Identity Online) U2F (Universal 2nd Factor) and FIDO2, which enable strong, phishing-resistant authentication without the need for complex drivers or software installations. When a user attempts to log in to a supported service, the security key cryptographically verifies their presence by interacting with the website or application. This interaction typically involves the key signing a challenge issued by the service, proving possession without ever exposing sensitive cryptographic material. Their ease of use, portability, and strong cryptographic backing make them a popular choice for securing online accounts, enterprise systems, and developer environments.
One-Time Password (OTP) Tokens
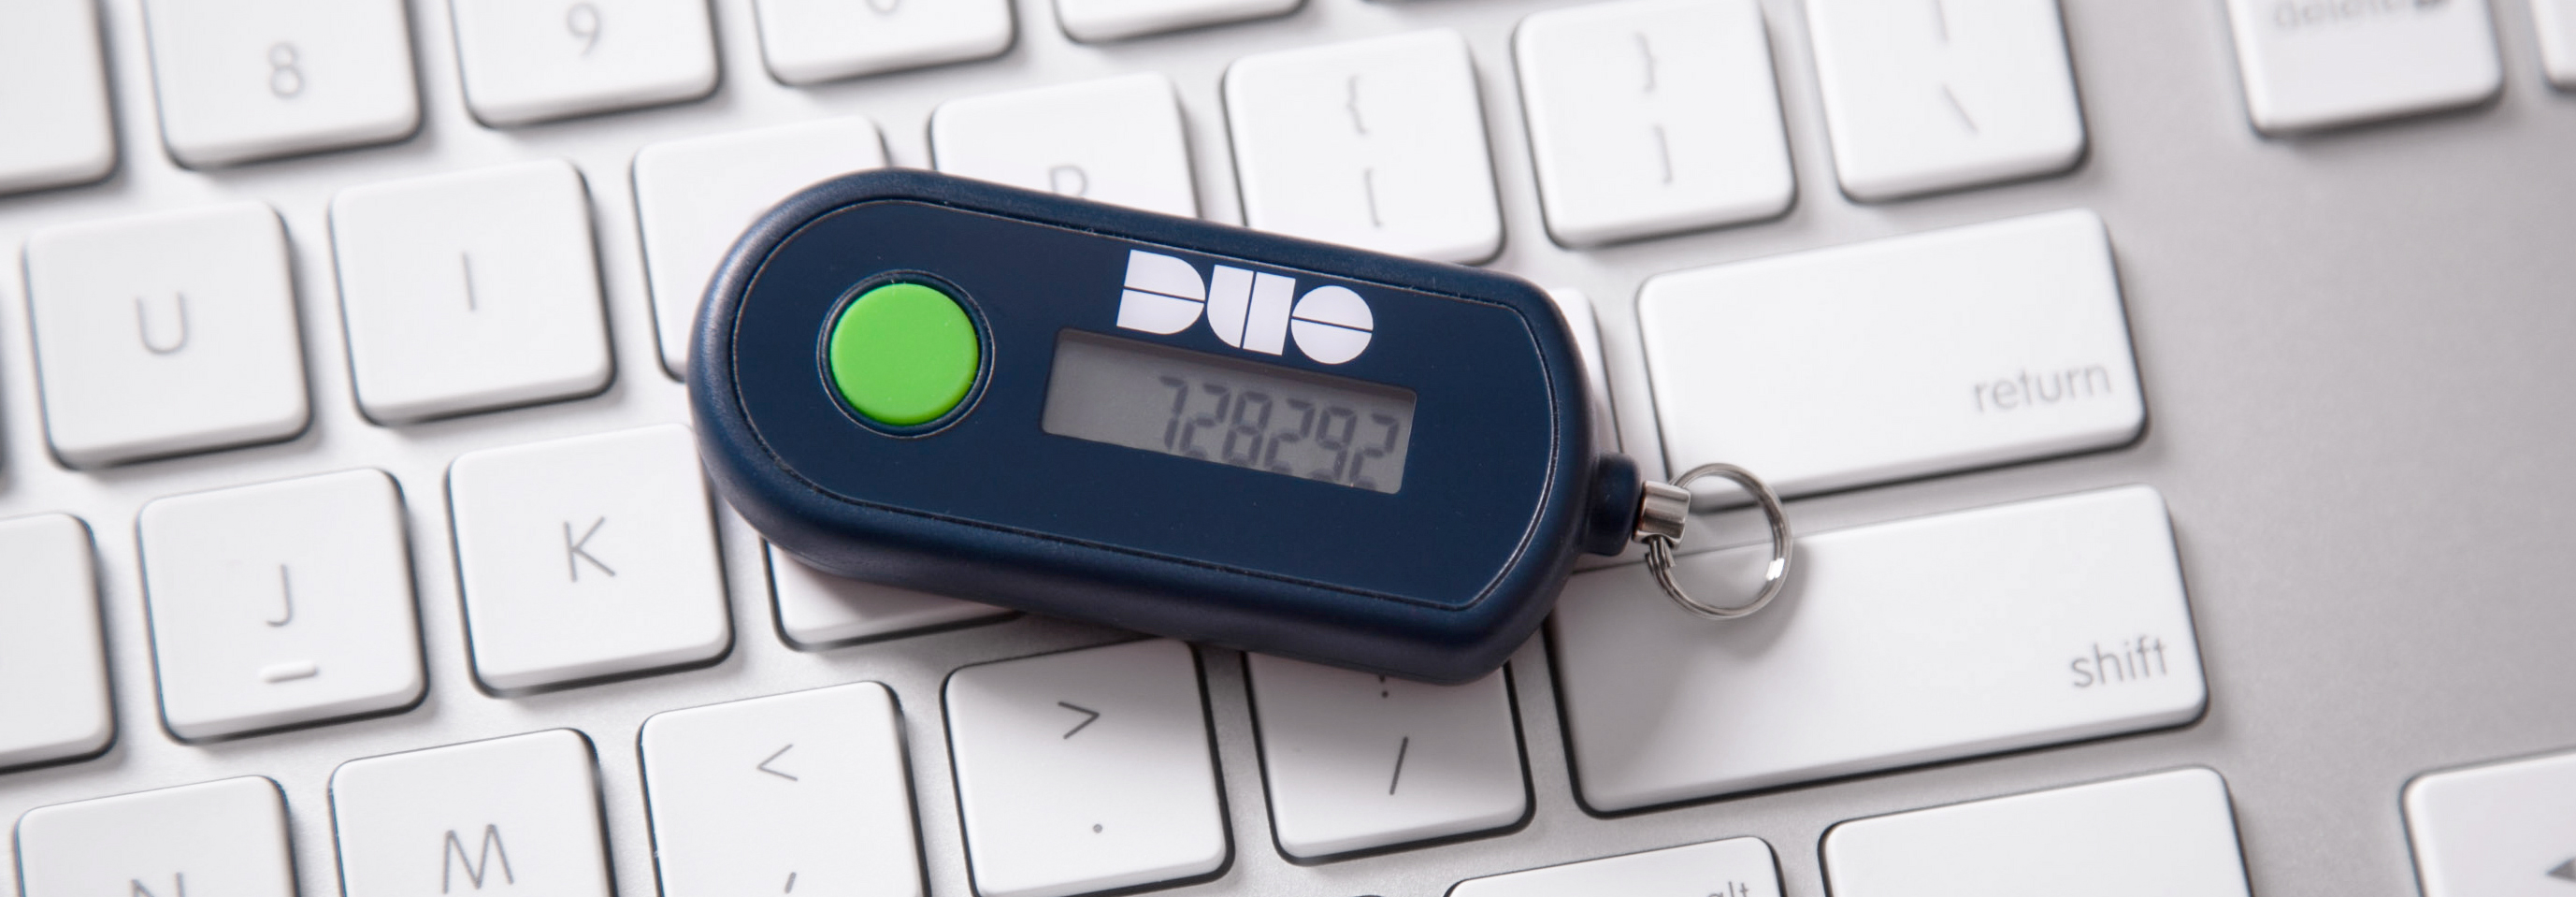
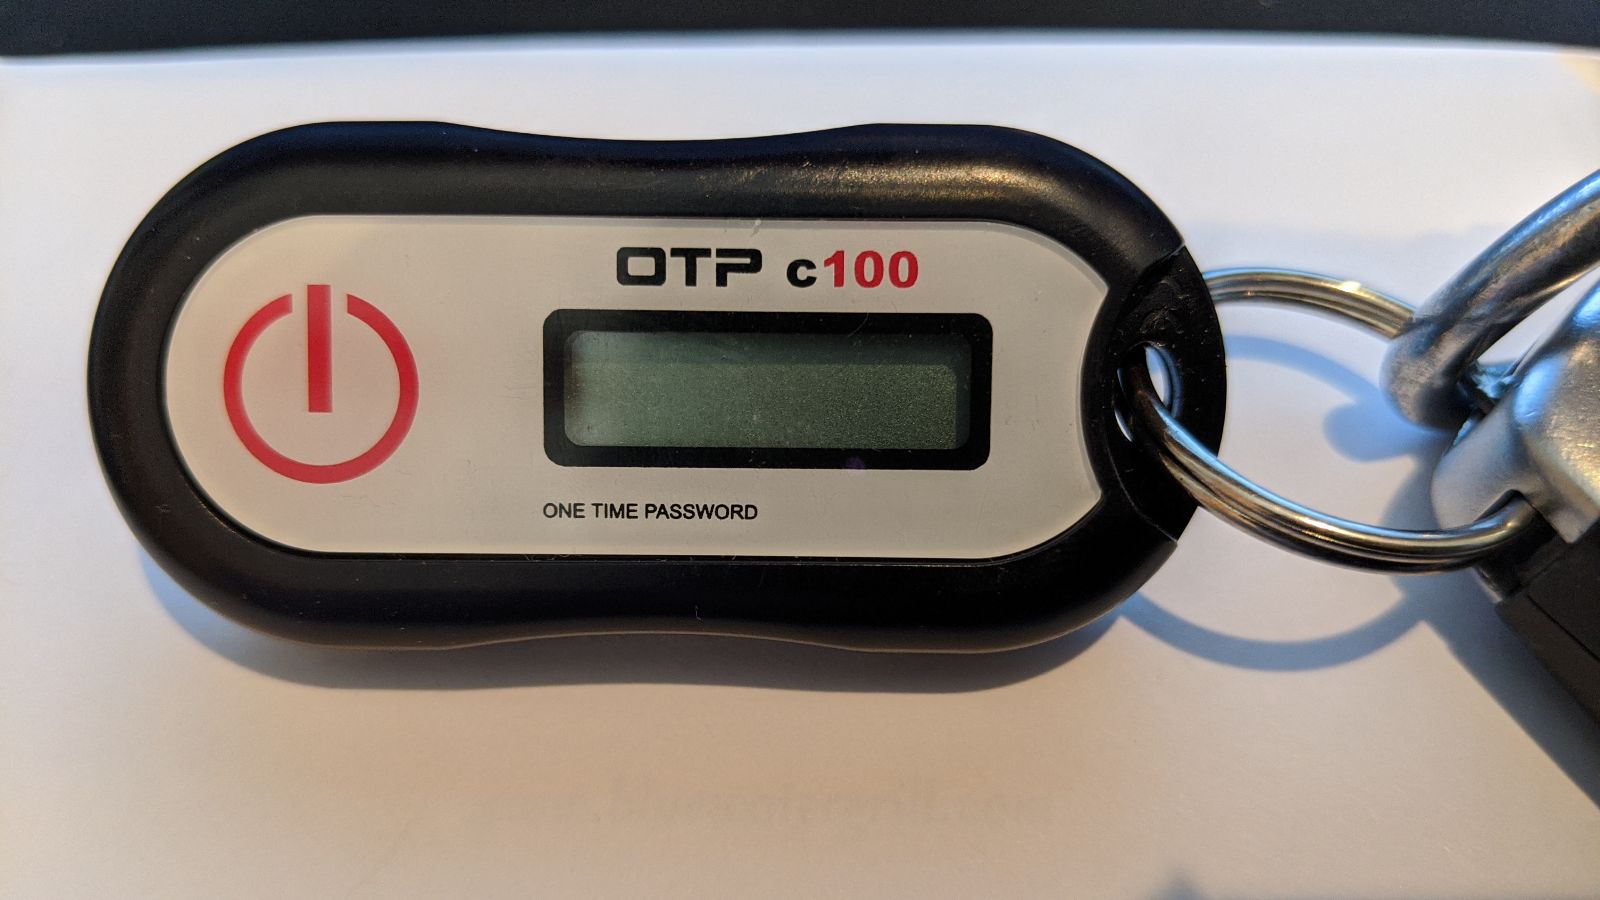
OTP tokens represent an earlier but still widely used class of hardware tokens. These devices feature a small display that continuously generates and updates a unique, time-sensitive code, typically every 30 or 60 seconds. When prompted for a second factor during login, the user simply reads the current code from the token and enters it into the authentication field. There are two primary types of OTP tokens:
- Time-based One-Time Passwords (TOTP): These tokens synchronize with a server’s clock and generate codes based on the current time, ensuring that the code is valid only for a short window.
- HMAC-based One-Time Passwords (HOTP): These tokens generate codes based on a shared secret key and a moving counter. Each successful authentication increments the counter, ensuring a new code is generated.
OTP tokens are robust against replay attacks since each code is valid for only one use or a very limited time. They are commonly found in enterprise environments for secure remote access, banking applications, and government systems.
Smart Cards
Smart cards, resembling credit cards in form factor, contain an embedded microchip capable of storing cryptographic keys and performing cryptographic operations. While not exclusively authentication tokens, smart cards are frequently used as such, often requiring a PIN to activate the chip’s functions. When used for authentication, the smart card is inserted into a smart card reader, and the user enters their PIN. The card then uses its internal processor to verify the PIN and cryptographically authenticate the user to the system. Smart cards are prevalent in corporate environments for network login, physical access control, and digital signing, providing a high level of security by requiring both physical possession of the card and knowledge of the PIN.
Embedded Tokens and Mobile Integration
The concept of a hardware token has also evolved to integrate directly into other devices, particularly smartphones. While a smartphone itself isn’t a dedicated hardware token in the traditional sense, its secure elements (specialized tamper-resistant chips) can function similarly. Applications on a smartphone can leverage these secure elements or act as software-based tokens that utilize cryptographic functions, sometimes requiring biometric verification (fingerprint, facial scan) as an additional “something you are” factor. This convergence creates a highly convenient and secure authentication method, blurring the lines between dedicated hardware and integrated solutions. Examples include using a phone’s biometric scanner to approve a login or generating OTPs directly within a secure authenticator app that is itself protected by the device’s hardware-backed security features.
How Hardware Tokens Fortify Digital Defenses
The intrinsic value of hardware tokens lies in their ability to significantly elevate the difficulty and complexity for malicious actors attempting unauthorized access. By introducing a physical, cryptographic element, they create a formidable barrier that software-based attacks often cannot overcome. This fortification is critical for any organization handling sensitive data or operating complex technological infrastructures, ensuring data integrity and operational continuity.
Resistance to Phishing and Man-in-the-Middle Attacks
One of the most insidious threats in the digital realm is phishing, where attackers trick users into divulging credentials on fake websites. Man-in-the-middle (MitM) attacks similarly intercept communications to steal information. Hardware tokens, especially those supporting standards like FIDO, offer strong resistance to these attacks. Unlike passwords that can be entered into any text field, a FIDO-compliant security key verifies the origin of the login request. It cryptographically binds the authentication process to the specific website or application it’s designed to secure. If a user attempts to use their key on a fraudulent phishing site, the key will detect the mismatch in origin and refuse to authenticate, effectively thwarting the attack. This contextual awareness makes it incredibly difficult for attackers to harvest valid credentials or intercept authentication sessions.
Protection Against Keyloggers and Malware
Keyloggers, malicious software designed to record keystrokes, and other forms of malware can capture passwords entered on a compromised computer. Since hardware tokens introduce an out-of-band authentication mechanism, they largely circumvent the threats posed by such malware. When using a USB security key, no password is typed directly, and the cryptographic interaction occurs securely between the key and the legitimate service. For OTP tokens, even if a keylogger captures the one-time code, its time-sensitive nature or single-use validity means it will likely expire or become invalid before an attacker can utilize it. This physical separation and cryptographic processing make hardware tokens resilient against many common software-based credential theft techniques.
Non-Repudiation and Enhanced Identity Verification
Beyond simply preventing unauthorized access, hardware tokens can also provide a stronger sense of non-repudiation. In certain contexts, especially where digital signatures are involved (e.g., signing documents or approving transactions), the use of a hardware token provides a higher assurance that a specific action was performed by the legitimate owner of the token. The cryptographic operations performed by the token can serve as irrefutable proof of intent and identity. This is particularly valuable in high-stakes environments where accountability and verifiable actions are paramount, such as in financial transactions, legal agreements, or the secure deployment of software updates for critical infrastructure, including drone flight controllers or mapping payloads.
Applications Across Modern Tech Ecosystems
The security advantages offered by hardware tokens make them indispensable across a wide array of modern technological applications. From safeguarding personal data to protecting global enterprise systems and national infrastructure, their role in maintaining digital integrity is expanding.
In the context of “Tech & Innovation,” hardware tokens are vital for securing the ecosystems built around advanced technologies. For instance, in the operation of large-scale drone fleets, ensuring that only authorized personnel can access flight planning software, drone control interfaces, or sensitive data collected from remote sensing missions is paramount. A hardware token can be used to authenticate pilots or operators to their ground control stations, to access secure cloud platforms storing high-resolution imagery or mapping data, or even to unlock specific features on the drones themselves (though this is more niche).
Beyond drones, consider autonomous vehicles, IoT deployments, or critical infrastructure management systems. The data generated and processed by these systems is often highly sensitive, requiring robust protection against tampering and unauthorized access. Hardware tokens provide an effective means to secure access to development environments, administrative portals, and data repositories for these complex systems, ensuring that innovations remain secure from conception to deployment. They are foundational to maintaining the integrity of supply chains for high-tech components, securing remote work access for engineers, and protecting intellectual property in competitive industries.
The Future of Hardware Token Integration
As technology progresses, the integration of hardware tokens is set to become even more seamless and pervasive. The trend is towards greater user convenience without compromising security, often through the convergence with other authentication factors and the adoption of open standards.
Biometrics and Multi-factor Authentication Convergence
The future of hardware tokens is deeply intertwined with the advancements in biometrics. Increasingly, hardware keys are incorporating fingerprint sensors, allowing for a “something you have” (the key) and “something you are” (the fingerprint) authentication experience in a single device. This multi-modal approach offers an even higher level of security, as an attacker would need to not only possess the physical token but also replicate the legitimate user’s unique biological identifier. This convergence is driven by the desire for frictionless security, where complex authentication is simplified for the user while remaining incredibly robust against sophisticated attacks.
Seamless User Experience and Ubiquity
Efforts are continuously underway to make hardware tokens easier to deploy, manage, and use. The evolution from complex, driver-dependent devices to plug-and-play standards like FIDO represents this shift. Future innovations will likely focus on even greater ubiquity, with hardware-backed security becoming an inherent feature of more devices, including wearable technology and IoT endpoints. The goal is a world where strong, hardware-protected authentication is not an optional add-on but an invisible, integrated layer of defense across all digital interactions, ensuring the integrity and security of the ever-expanding landscape of advanced technological innovations.