
Understanding SQL Injection: The Fundamental Threat to Data-Driven Innovation
SQL Injection (SQLi) stands as one of the oldest, most prevalent, and critically dangerous web application vulnerabilities. It allows an attacker to interfere with the queries an application makes to its database. In an era where innovation is increasingly data-driven, from AI-powered autonomous systems to sophisticated remote sensing platforms, the integrity and security of underlying databases are paramount. A successful SQLi attack can lead to unauthorized access to sensitive data, data manipulation, authentication bypass, and even full control over the database server, posing a direct threat to the reliability and trustworthiness of cutting-edge technological advancements.
The SQL Language and Database Interaction
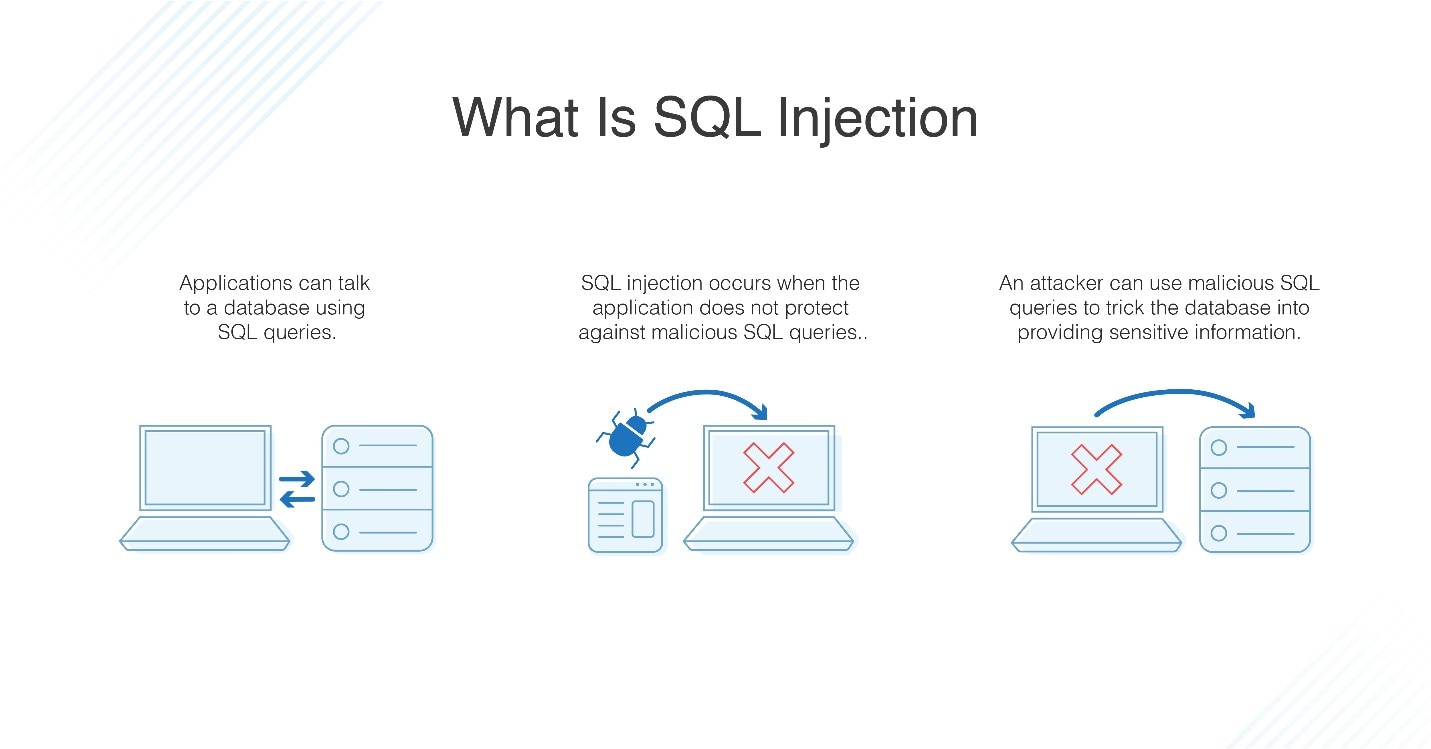
Structured Query Language (SQL) is the standard language used to communicate with and manage relational databases. Almost every modern application, whether it’s a social media platform, an e-commerce site, or the backend system managing data for drone mapping services, relies on a database to store, retrieve, and process information. When a user interacts with a web application (e.g., logging in, searching for a product, submitting a form), the application typically constructs SQL queries based on user input and sends them to the database. For instance, a login form might generate a query like SELECT * FROM Users WHERE Username = 'user_input' AND Password = 'password_input';. If user_input contains malicious SQL code, and the application does not properly sanitize or validate this input, the database server will execute the attacker’s unintended commands alongside the legitimate query.
How an Injection Works: Malicious Code Insertion
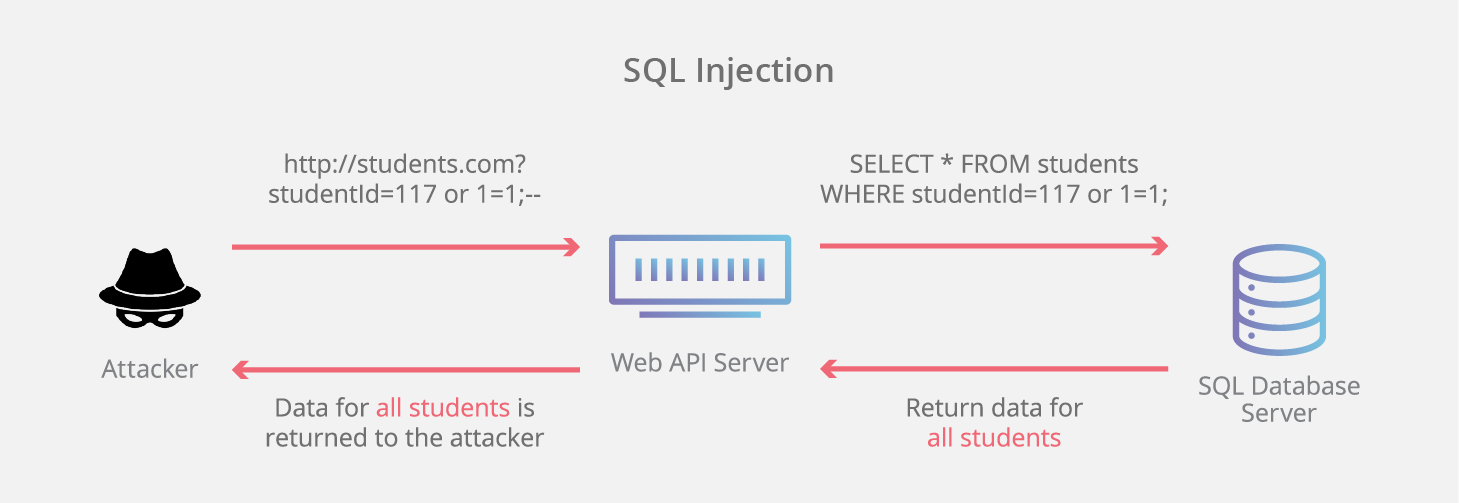
The core mechanism of a SQL injection attack involves injecting malicious SQL code into input fields. This code is then executed by the database. Consider an application that takes a user ID as input to display user details. A typical query might look like:
SELECT name, email FROM users WHERE id = 'user_id_input';
If an attacker enters 1 OR 1=1 instead of a legitimate user ID, the query becomes:
SELECT name, email FROM users WHERE id = '1 OR 1=1';
Since 1=1 is always true, the database might return details for all users, not just user ID 1. This simple example illustrates how an attacker can manipulate the query’s logic. More sophisticated attacks can lead to:
- Retrieving data from other tables (e.g.,
UNION SELECT password, credit_card_number FROM financial_data;). - Modifying database contents (e.g.,
UPDATE users SET password = 'new_password' WHERE username = 'admin';). - Executing operating system commands if the database management system (DBMS) allows it.
Such vulnerabilities, if present in systems underpinning innovative technologies, could severely compromise data models, operational parameters, or user credentials critical for next-gen functionalities like AI-driven analytics or secure remote operations.
Varieties of SQL Injection: Exploiting the Gates of Innovation
SQL injection attacks are not monolithic; they manifest in several forms, each exploiting different aspects of how an application interacts with its database. Understanding these variations is crucial for developers and cybersecurity professionals tasked with securing the complex systems that drive modern innovation. A robust defense strategy requires anticipating these diverse attack vectors, especially given the sensitive nature of data processed by technologies like autonomous systems or advanced mapping solutions.
In-band SQLi (Error-based, Union-based)
In-band SQLi attacks are the most common and straightforward. The attacker uses the same communication channel to inject the malicious SQL code and to retrieve the results.
- Error-based SQLi: This technique relies on error messages generated by the database server to gather information. Attackers deliberately cause the database to produce error messages that contain sensitive data, such as database structure, column names, or even specific records. For example, injecting a string that causes a division-by-zero error might reveal table names in the error output, allowing the attacker to progressively map out the database schema. In the context of innovative tech, such leaks could expose proprietary algorithms stored in lookup tables or the architecture of a complex data processing pipeline.
- Union-based SQLi: This method leverages the
UNIONSQL operator to combine the results of two or moreSELECTstatements into a single result set. Attackers use this to retrieve data from tables other than the one originally intended by the query. By manipulating the number of columns and data types in their injectedSELECTstatement, they can extract data from any table in the database, including user credentials, configuration settings, or critical operational data that might underpin autonomous decision-making processes. Imagine an attacker extracting configuration parameters vital for an AI’s operational boundaries; the consequences could be catastrophic for system integrity.
Inferential SQLi (Blind SQLi: Boolean-based, Time-based)
Inferential SQLi, often referred to as “Blind SQLi,” is employed when the application does not return the results of an SQL query directly to the attacker. Instead, the attacker deduces information by observing the application’s response (e.g., time delays, boolean responses). This method is slower but equally potent, making it a persistent threat to applications where direct data leakage is prevented.
- Boolean-based Blind SQLi: In this technique, the attacker sends SQL queries that force the application to return a different response depending on whether a single condition within the query is true or false. For example, an attacker might inject a query like
' AND SUBSTRING(VERSION(), 1, 1) = '5'--. If the application behaves differently (e.g., shows a different page, or loads faster/slower) when this condition is true, the attacker can deduce information character by character. This painstaking process can eventually reconstruct entire database contents, from sensitive user profiles to proprietary mapping data or sensor calibration settings essential for precise autonomous operation. - Time-based Blind SQLi: This is a more advanced blind technique used when the attacker cannot rely on distinct boolean responses. Instead, the attacker sends SQL queries that, depending on whether a condition is true or false, will cause the database to delay its response for a specified amount of time. For example,
'; IF(1=1) WAITFOR DELAY '0:0:5'--would cause a 5-second delay if the condition is true. By observing these time delays, attackers can infer the truthfulness of their injected statements, character by character. This method is particularly insidious because it leaves minimal traces, making detection challenging. For systems requiring real-time data integrity, like those managing advanced navigation or remote sensing data, such subtle compromise could lead to significant operational inaccuracies or security breaches over time.
Out-of-band SQLi
Out-of-band SQLi is the least common type of SQL injection. It occurs when the attacker cannot use the same channel to inject and retrieve results. Instead, the attacker causes the database server to make an out-of-band communication with a system controlled by the attacker. This might involve DNS lookups, HTTP requests, or other network protocols. This method typically relies on specific database server features that allow external network interactions. While rarer, its impact can be severe, enabling data exfiltration even from highly isolated systems or facilitating the execution of remote commands, which could compromise the entire server infrastructure supporting advanced innovations.
The Perilous Impact: Compromising the Fabric of Modern Tech
The consequences of a successful SQL injection attack can be devastating, extending far beyond simple data theft. For organizations pushing the boundaries of technology and innovation, these attacks can erode trust, compromise proprietary assets, disrupt critical operations, and ultimately jeopardize the viability of new products and services. The interconnectedness of modern tech means that a single SQLi vulnerability can cascade through multiple systems, impacting data integrity, security, and the very foundation upon which innovation is built.
Data Breach and Confidentiality Loss
The most immediate and common impact of SQLi is a data breach. Attackers can access, copy, or exfiltrate confidential information stored in the database. This includes sensitive user data (e.g., personal details, authentication credentials), financial records, intellectual property, and proprietary algorithms. In the context of innovative fields, this could mean the theft of design schematics for cutting-edge hardware, source code for AI algorithms, or highly sensitive mapping data collected by remote sensing platforms. Such breaches not only lead to regulatory fines and reputational damage but also grant competitors an unfair advantage, stifling future innovation.
Data Manipulation and Integrity Erosion
Beyond mere theft, SQLi allows attackers to modify or delete data within the database. This capability is particularly dangerous for systems that rely on accurate and untampered data for their operations. Imagine an attacker altering critical parameters in a database used by an autonomous flight system, subtly changing its navigation waypoints or sensor calibration settings. Or consider the impact on sophisticated mapping applications where geographical data is foundational: malicious alterations could lead to inaccurate models, faulty navigation, or incorrect environmental assessments. The integrity of data is paramount for the reliable functioning of AI models, machine learning algorithms, and real-time operational systems. Compromised data integrity undermines the very trust placed in technological advancements.
Authentication Bypass and System Control
A common objective of SQLi is to bypass authentication mechanisms. By injecting malicious SQL, an attacker can trick the application into granting them administrative access without valid credentials. Once an attacker gains administrative privileges, they can effectively take full control of the application and potentially the underlying server. For innovative tech platforms, this could mean unauthorized access to administrative panels of a drone fleet management system, control over data ingestion pipelines for remote sensing, or the ability to manipulate the backend of an AI training environment. Such control grants an attacker the power to disrupt services, deploy malware, or leverage the compromised system as a launchpad for further attacks within a network, severely impacting operational security.
Denial of Service and Operational Disruption
SQL injection can also be used to launch denial-of-service (DoS) attacks. An attacker might inject queries that are deliberately complex, resource-intensive, or designed to delete critical database tables. This can overload the database server, making the application unresponsive or completely inoperable. For systems delivering innovative services, such as real-time analytics for flight operations or continuous data streams for autonomous vehicles, a DoS attack caused by SQLi can lead to significant service outages, financial losses, and a complete halt to essential operations. This directly impacts the reliability and availability expected from modern technological solutions.
Defending Against SQL Injection: Securing the Future of Tech Innovation
Protecting against SQL injection is not merely about patching vulnerabilities; it’s about embedding security into the very architecture and development lifecycle of innovative applications. As technological advancements continue to rely heavily on database interactions, implementing robust defense mechanisms becomes critical for safeguarding data, maintaining operational integrity, and preserving user trust. Securing these foundations ensures that the fabric of modern tech innovation remains resilient against persistent threats.
Parameterized Queries and Prepared Statements
The most effective defense against SQL injection is the use of parameterized queries or prepared statements. Instead of directly concatenating user input into the SQL query string, these methods separate the SQL code from the user-supplied data. The database then understands that the user input is merely a value to be used in the query, not part of the SQL command itself. For example, using placeholders like ? or named parameters (e.g., :username) ensures that special characters in user input are treated as literal strings rather than executable SQL code. This completely neutralizes the injection vector, making it the gold standard for secure database interaction in all new and evolving applications, especially those handling sensitive data for AI, autonomous control, and mapping.
Input Validation and Escaping User Input
While parameterized queries are paramount, comprehensive input validation adds another layer of defense. All user input should be strictly validated to ensure it conforms to expected formats, types, and lengths. For instance, if an input field is expected to be an integer, reject any input that contains non-numeric characters. Whitelisting (allowing only known good input) is more secure than blacklisting (trying to filter out known bad input), as attackers continuously find ways to bypass blacklists. For legacy systems where parameterized queries might be difficult to implement immediately, escaping user input can provide some protection. This involves modifying characters that have special meaning in SQL (e.g., single quotes, backslashes) so that they are treated as literal characters by the database. However, escaping is less reliable than parameterized queries as it’s prone to implementation errors and bypasses.
Least Privilege and Database Security Best Practices
Adopting the principle of least privilege is fundamental to minimizing the impact of any potential breach, including SQLi. Database users and application connections should only have the minimum necessary permissions to perform their required tasks. For example, an application user should not have administrative rights to the database, nor should it have permissions to drop tables or execute system commands. Furthermore, regularly patching database management systems, encrypting sensitive data at rest and in transit, and robust password policies are essential best practices. These measures help limit the damage if an attacker successfully exploits a vulnerability, ensuring that critical data supporting innovations like AI models and autonomous systems remains protected.
Web Application Firewalls (WAFs) and Continuous Monitoring
Web Application Firewalls (WAFs) act as a protective shield between the web application and the internet, filtering and monitoring HTTP traffic. A WAF can detect and block malicious SQLi attempts by analyzing incoming requests for known attack patterns or anomalies. While WAFs provide an important external layer of defense, they are not a substitute for secure coding practices but rather a complementary tool. Alongside WAFs, continuous security monitoring, including regular vulnerability scanning, penetration testing, and log analysis, is crucial. Detecting unusual database activity, failed login attempts, or anomalous error messages quickly can indicate an ongoing SQLi attack, enabling rapid response and mitigation to protect the integrity of innovative platforms. This proactive approach is vital for maintaining the security posture of dynamic, evolving technologies.