
Phishing fraud represents a pervasive and evolving cyberthreat, deeply entrenched within the digital landscape and continually challenging the boundaries of technological security. At its core, phishing is a deceptive practice where malicious actors attempt to trick individuals into divulging sensitive information—such as usernames, passwords, credit card details, or financial data—by masquerading as a trustworthy entity in an electronic communication. This form of social engineering is intricately linked with technological exploitation, leveraging communication platforms and human psychology to bypass sophisticated security measures. Understanding its mechanics, impact, and the innovative countermeasures being developed is crucial for safeguarding the integrity of digital ecosystems and fostering continued technological advancement.
The Digital Deception: Understanding Phishing Mechanics
The fundamental principle of phishing relies on deception, but the methods and vectors employed are diverse and continually refined, often leveraging new communication technologies. These attacks are not merely simple tricks but often involve sophisticated technical setups to mimic legitimate services and evade detection.
Email Phishing: The Classic Approach
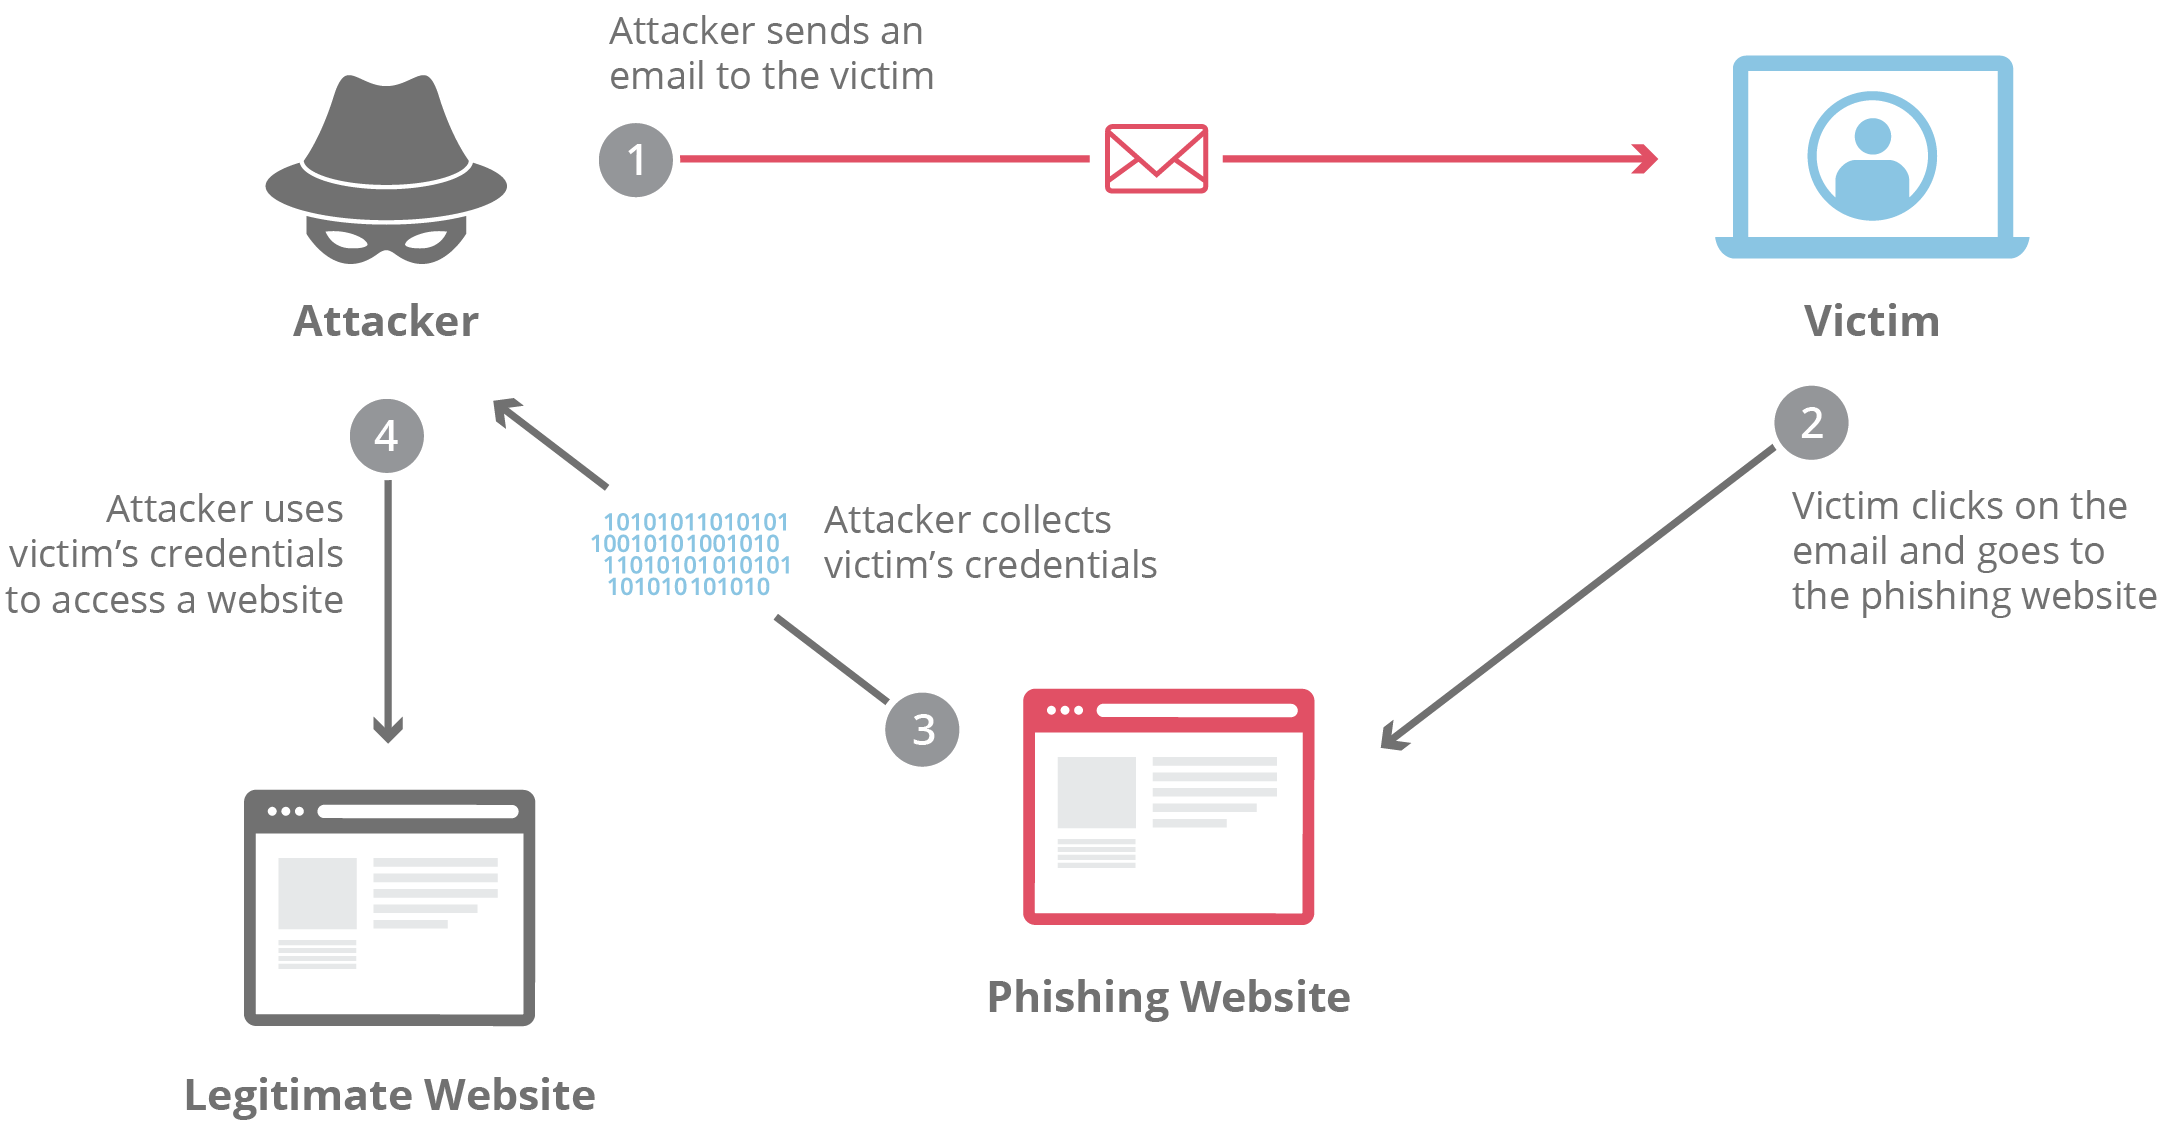
Email phishing remains the most common vector. Attackers craft emails that appear to originate from reputable organizations—banks, tech companies, government agencies, or even internal IT departments. These emails typically contain urgent language, threats of account suspension, or tempting offers to prompt immediate action. The embedded links often direct victims to meticulously crafted fake websites that mirror the legitimate ones, designed to capture login credentials or personal data. The technical execution often involves domain spoofing, where the sender’s email address is falsified, or the use of look-alike domains that are subtly different from the genuine ones (e.g., “micros0ft.com” instead of “microsoft.com”).
Spear Phishing and Whaling: Targeted Attacks
Moving beyond broad-brush campaigns, spear phishing involves highly targeted attacks aimed at specific individuals or organizations. Attackers conduct extensive reconnaissance, gathering personal information about their targets to craft highly personalized and convincing messages. This can include details about their job role, colleagues, recent projects, or even personal interests, making the deception incredibly difficult to detect. Whaling is an even more specialized form of spear phishing, exclusively targeting high-value individuals within an organization, such as CEOs, CFOs, or other senior executives, often with the goal of initiating fraudulent wire transfers or obtaining highly sensitive corporate data. The technical complexity here lies in the data aggregation and analysis used to build detailed profiles of targets.
Smishing and Vishing: Mobile and Voice Vectors
As communication technologies evolve, so do phishing tactics. Smishing (SMS phishing) leverages text messages to deliver malicious links or induce victims to call fraudulent phone numbers. These messages often appear to be from package delivery services, banks, or emergency alerts. Vishing (voice phishing) involves phone calls where fraudsters impersonate legitimate entities, using social engineering to extract information directly or convince victims to perform actions that compromise their security, such as installing remote access software. Both smishing and vishing exploit the inherent trust many users place in direct communication channels and the immediacy of mobile alerts.
Pharming and Watering Hole Attacks: Infrastructure Compromise
Some phishing techniques go beyond direct communication with the victim. Pharming involves redirecting users from legitimate websites to malicious ones without their knowledge, often by poisoning DNS (Domain Name System) records on a server or a user’s local machine. This is a more technically sophisticated attack, compromising foundational internet infrastructure. Watering hole attacks involve compromising a website frequently visited by a specific target group (e.g., employees of a particular company or members of an industry association) and infecting it with malware. When a target visits the compromised site, their system is automatically infected, allowing attackers to steal data or gain further access. These methods demonstrate a deep understanding of network architecture and exploit vulnerabilities within the broader digital ecosystem.
The Technological Underpinnings of Phishing Attacks
Phishing, while rooted in social engineering, is heavily dependent on and facilitated by various technological elements. Attackers continuously innovate, leveraging new tools and techniques to enhance their effectiveness and evade detection.
Social Engineering Meets Advanced Tech
The art of social engineering is amplified by technology. Phishing kits, readily available on dark web markets, provide pre-built templates for fake login pages, email content, and even server-side scripts for data collection. These kits allow attackers with limited technical expertise to launch sophisticated campaigns. Furthermore, automated tools are used for sending vast quantities of phishing emails, harvesting publicly available information for targeted attacks, and even registering look-alike domains programmatically. The integration of advanced analytics allows attackers to refine their campaigns based on click-through rates and successful compromises.
Exploit Kits and Malicious Payloads
Beyond just collecting credentials, phishing attacks often serve as an initial vector for delivering more potent threats. Clicking a malicious link in a phishing email can lead to a drive-by download, where malware is installed automatically without user interaction, often via an exploit kit. These kits are bundles of exploits that target known vulnerabilities in web browsers, operating systems, or common applications. Once a vulnerability is successfully exploited, the kit can download and execute various malicious payloads, including ransomware, spyware, or remote access Trojans (RATs), giving attackers deep control over the victim’s system.
Obfuscation and Evasion Techniques
Phishing attacks employ various technical methods to bypass security filters and detection systems. URL encoding, domain masking, and the use of legitimate but compromised websites (URL redirection) are common tactics to hide malicious links. Attackers also use image-based emails or manipulate character sets to make text unreadable by automated scanners, yet perfectly legible to human eyes. Advanced phishing campaigns might even incorporate CAPTCHAs on their fake login pages to trick automated bots, demonstrating an understanding of security defense mechanisms and an effort to mimic legitimate security practices. The use of encrypted connections (HTTPS) on phishing sites, obtained via free certificate authorities, adds a false sense of legitimacy, making it harder for users to distinguish real from fake.
Impact on Digital Ecosystems and Innovation
The consequences of phishing fraud extend far beyond individual financial loss, posing significant threats to the stability and trustworthiness of global digital ecosystems and hindering technological innovation.
Data Breaches and Intellectual Property Theft

Phishing is a primary gateway for major data breaches. When employees or individuals within an organization fall victim, their credentials can provide attackers with access to corporate networks, sensitive customer data, proprietary technologies, or critical intellectual property. The theft of trade secrets, research data, or product designs can cripple businesses, erode competitive advantages, and cost billions in remediation and lost future earnings. This directly undermines the investment in R&D and the processes of innovation.
Financial Losses and Reputational Damage
Direct financial losses from phishing are staggering, impacting individuals, businesses, and even national economies. Business Email Compromise (BEC) scams, a form of whaling, have led to billions of dollars in fraudulent wire transfers. Beyond immediate monetary costs, successful phishing attacks inflict severe reputational damage. Customers lose trust in organizations that suffer breaches, leading to lost business, regulatory fines, and protracted legal battles. This erosion of trust in digital transactions and platforms can slow the adoption of new technologies and digital services.
Undermining Trust in Digital Platforms
Every successful phishing attack, particularly those that mimic major tech platforms or financial institutions, chips away at user trust in the digital sphere. If users constantly fear that every email, text, or website could be a deception, it impedes the seamless flow of information and commerce that drives the digital economy. This lack of trust can stifle user engagement with innovative digital services, from online banking to cloud computing, out of fear of compromise. It forces tech companies to divert significant resources from product development to security, impacting the pace of innovation.
Innovative Countermeasures and Future Trends
The fight against phishing is a continuous arms race, driving significant innovation in cybersecurity. As attackers refine their methods, security experts and technologists are developing increasingly sophisticated defenses.
AI and Machine Learning for Threat Detection
Artificial Intelligence (AI) and Machine Learning (ML) are at the forefront of anti-phishing innovation. ML algorithms can analyze vast datasets of emails, URLs, and network traffic in real-time to identify patterns indicative of phishing attempts that might elude traditional rule-based filters. They can detect anomalies in sender behavior, analyze subtle linguistic cues in email content, and identify malicious redirects with high accuracy. AI-driven systems are becoming adept at predicting emerging phishing trends, providing proactive defense capabilities by learning from new attack vectors.
Multi-Factor Authentication (MFA) and Biometrics
Multi-Factor Authentication (MFA) has become a cornerstone defense. By requiring two or more verification methods (e.g., something you know like a password, something you have like a phone or hardware token, something you are like a fingerprint), MFA drastically reduces the effectiveness of stolen credentials. Even if a phishing attack compromises a password, access is denied without the second factor. Biometric authentication (fingerprints, facial recognition, iris scans) further enhances security by linking identity to unique biological traits, making it virtually impossible for phishers to spoof. Innovation in passwordless authentication methods, leveraging FIDO2 standards and cryptographic keys, is also gaining traction.
Advanced Email Security Gateways and URL Scanners
Next-generation email security gateways employ a combination of AI, sandboxing technologies, and reputation analysis to detect and block phishing attempts before they reach inboxes. Sandboxing allows suspicious attachments and links to be opened in an isolated virtual environment to observe their behavior without risk to the network. Advanced URL scanners analyze links in real-time, checking against blacklists, performing domain reputation checks, and even executing JavaScript on target pages to detect malicious code. Many also incorporate DMARC, SPF, and DKIM protocols for email authentication, making it harder for attackers to spoof legitimate sender domains.
Blockchain and Decentralized Identity
Emerging technologies like blockchain hold promise for future anti-phishing strategies. Decentralized identity systems, built on blockchain, could offer a more secure way to verify identities and manage credentials, reducing reliance on centralized systems that are single points of failure. By cryptographically linking identity to an immutable ledger, it could become significantly harder for attackers to impersonate individuals or organizations, or to create fake digital assets.
Continuous Security Awareness Training through Gamification
While technology provides robust defenses, human vigilance remains critical. Innovation in security awareness training now incorporates gamification, interactive simulations, and personalized learning paths to make employees more resilient to social engineering tactics. Regular, simulated phishing campaigns help employees recognize sophisticated threats in a safe environment, turning them into a strong line of defense rather than a vulnerability.
Safeguarding Digital Assets and Fostering Innovation
Combating phishing fraud is an ongoing endeavor that requires a multi-layered approach, blending cutting-edge technology with vigilant human practices. For the tech and innovation sector, successfully mitigating this threat is paramount.
Proactive Defense Strategies
Organizations must adopt proactive security postures, integrating threat intelligence feeds, continuous vulnerability assessments, and robust incident response plans. Investing in AI-powered security analytics and automated remediation tools can significantly reduce the window of opportunity for attackers. Furthermore, promoting a culture of cybersecurity awareness from the top down ensures that every individual acts as a sensor and defender within the digital ecosystem.
Collaborative Security Ecosystems
The fight against phishing cannot be waged in isolation. Collaboration across industries, with government agencies, and among cybersecurity researchers is crucial. Sharing threat intelligence, best practices, and innovative defense strategies enables a collective response that outpaces the evolving tactics of cybercriminals. By viewing cybersecurity as a shared responsibility, the tech and innovation sector can ensure that digital advancements continue to flourish without being undermined by pervasive digital deception.