
The Payment Card Industry (PCI) represents the global ecosystem involved in the processing, storage, and transmission of credit and debit card information. It encompasses a vast network of stakeholders, including merchants, payment processors, banks, financial institutions, and technology vendors, all of whom play critical roles in facilitating secure electronic transactions. At its core, the PCI exists to establish and enforce a consistent set of security standards designed to protect sensitive cardholder data from compromise. This robust framework is essential in an era where digital payments are ubiquitous, and the threats from cyberattacks are constantly evolving. Understanding the PCI means delving into its operational mandates, technological underpinnings, and the continuous innovation required to maintain trust in digital financial systems.
The Foundation of Digital Payment Security
The proliferation of electronic payments transformed commerce, but with convenience came an increased vulnerability to data theft. Before a unified standard, businesses often had disparate security practices, creating weak links that criminals exploited. The need for a standardized approach became acutely clear as data breaches escalated, leading to significant financial losses and erosion of consumer confidence.
Evolution of Payment Security
Initially, payment security was largely reactive, with measures often implemented only after a breach occurred. As internet commerce grew, so did the sophistication of cyber threats. Early efforts by individual card brands (Visa, Mastercard, American Express, Discover, JCB) to establish their own security programs were a step forward, but they often led to overlapping and sometimes conflicting requirements for merchants. This fragmented landscape prompted a collaborative effort among these major card brands. In December 2004, they unified their individual security initiatives to create the Payment Card Industry Data Security Standard (PCI DSS), managed by the PCI Security Standards Council (PCI SSC). This landmark development provided a single, comprehensive framework for all entities involved in processing card payments.
The Role of PCI DSS
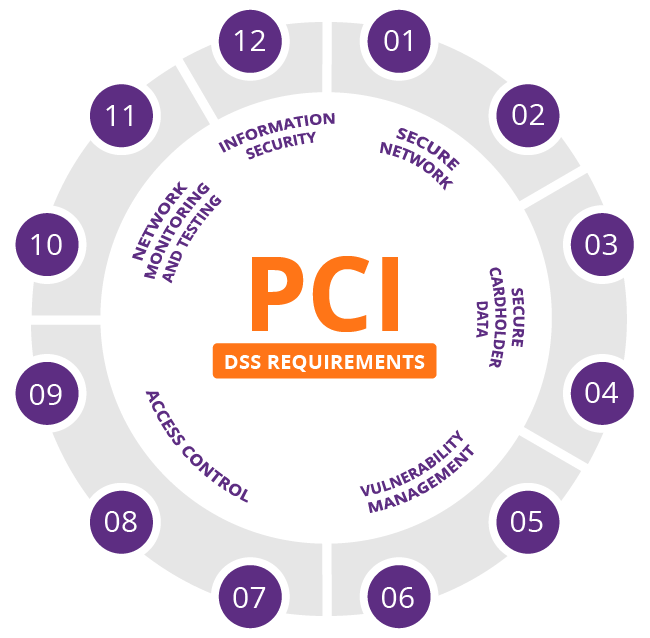
PCI DSS is not a law, but a set of mandatory operational and technical requirements designed to ensure that all companies that process, store, or transmit credit card information maintain a secure environment. Compliance with PCI DSS is enforced by the individual card brands and acquirers, who can impose substantial fines and penalties on non-compliant entities in the event of a data breach. The standard outlines twelve core requirements, categorized into six logical groups, each addressing a specific area of security crucial for protecting cardholder data. These requirements are periodically updated to address new threats and technological advancements, ensuring that the standard remains relevant and effective in a dynamic cybersecurity landscape. The overarching goal of PCI DSS is to reduce credit card fraud through the proactive protection of cardholder data across the entire payment ecosystem.
Core Principles of PCI DSS Compliance
Achieving and maintaining PCI DSS compliance is a continuous process that demands significant investment in technology, processes, and personnel. The twelve requirements are interconnected, forming a comprehensive security posture.
Building and Maintaining Secure Networks
The first two requirements focus on foundational network security. This includes installing and maintaining a firewall configuration to protect cardholder data, which acts as a barrier between a trusted internal network and untrusted external networks. Additionally, entities must not use vendor-supplied defaults for system passwords and other security parameters. Default settings often include easily guessable passwords or known vulnerabilities that can be exploited, necessitating customization for robust security.
Protecting Cardholder Data
Requirements three and four directly address the most sensitive asset: cardholder data. This involves protecting stored cardholder data, meaning encryption or tokenization of primary account numbers (PAN) when stored. Furthermore, entities must encrypt transmission of cardholder data across open, public networks. This ensures that even if data is intercepted during transmission, it remains unintelligible and unusable to unauthorized parties. The use of strong cryptographic protocols like TLS (Transport Layer Security) is paramount here.
Implementing Strong Access Control Measures
A significant portion of PCI DSS focuses on limiting and controlling access to cardholder data. Requirements seven, eight, and nine mandate restricting access to cardholder data on a need-to-know basis, ensuring that only individuals with a legitimate business reason can access sensitive information. This is complemented by assigning a unique ID to each person with computer access and managing all user accounts effectively. Physical access to cardholder data is also critical; this includes implementing strong physical access controls to prevent unauthorized entry into facilities where cardholder data is stored or processed.
Regularly Monitoring and Testing Networks
Vigilance is key to cybersecurity. Requirements ten and eleven emphasize regular monitoring and testing. This involves tracking and monitoring all access to network resources and cardholder data, maintaining audit logs to detect and investigate suspicious activities. Furthermore, entities must regularly test security systems and processes, including penetration testing and vulnerability scanning, to identify and remediate potential weaknesses before they can be exploited by malicious actors.
Maintaining an Information Security Policy

Finally, requirements six and twelve address the organizational and policy aspects. Developing and maintaining secure systems and applications is crucial, which includes applying security patches promptly and developing secure applications. Requirement twelve, often considered the most encompassing, mandates maintaining an information security policy that addresses all personnel and outlines clear responsibilities for information security. This policy should be regularly reviewed and updated to reflect changes in technology, threats, and organizational structure.
Technological Innovations Driving PCI Compliance
The landscape of payment processing and cybersecurity is constantly evolving. As such, PCI DSS compliance is not static; it requires continuous adoption of innovative technologies and strategies to stay ahead of threats.
Tokenization and Encryption Advancements
Traditional encryption has been a cornerstone of data protection. However, innovations like tokenization have revolutionized how sensitive data is handled. Tokenization replaces sensitive cardholder data (like a PAN) with a unique, non-sensitive equivalent called a “token.” This token can be used in internal systems and payment processes without exposing the original card data, significantly reducing the scope and risk of a data breach. If a system holding tokens is compromised, no actual card numbers are exposed. Advanced encryption techniques, including stronger algorithms and key management systems, also continue to evolve, offering enhanced protection for data at rest and in transit.
Cloud Security and Virtualization
The move to cloud computing presents both opportunities and challenges for PCI compliance. Cloud providers offer robust security features and scalability, but they also introduce complexities regarding data residency, shared responsibility models, and virtualized environments. Innovative cloud security solutions, including specialized firewalls, intrusion detection systems, and data loss prevention (DLP) tools tailored for cloud infrastructures, are critical for maintaining compliance. Virtualization technologies demand specific security controls to ensure isolation between virtual machines and prevent unauthorized access to cardholder data across shared resources.
AI and Machine Learning in Fraud Detection
Artificial intelligence (AI) and machine learning (ML) are transforming fraud detection and prevention. These technologies can analyze vast datasets of transaction patterns, behavioral anomalies, and historical fraud indicators in real-time. By identifying subtle deviations from normal behavior, AI/ML algorithms can flag potentially fraudulent transactions with greater accuracy and speed than traditional rule-based systems. This proactive approach helps reduce false positives, improve the customer experience, and significantly mitigate financial losses due to fraud, making them indispensable tools for PCI compliance efforts focused on secure transaction processing.
Continuous Monitoring and Automated Compliance Tools
Manual compliance checks are time-consuming and prone to human error. The rise of continuous monitoring platforms and automated compliance tools is a major innovation. These solutions provide real-time visibility into an organization’s security posture, automatically detecting misconfigurations, vulnerabilities, and policy violations. They can integrate with existing security systems, perform automated vulnerability scans, and generate reports, streamlining the compliance process and ensuring that security controls remain effective around the clock. This shift from periodic assessments to continuous vigilance is vital for maintaining an agile and robust security framework.
Impact and Future of PCI in the Digital Economy
The Payment Card Industry, guided by PCI DSS, plays an indispensable role in safeguarding the integrity of digital payments globally. Its impact extends beyond mere compliance, shaping consumer behavior, fostering innovation, and laying the groundwork for future payment technologies.
Mitigating Cyber Risks
PCI DSS has significantly raised the baseline of security for cardholder data across millions of entities worldwide. By enforcing a common set of best practices, it has made it considerably harder for cybercriminals to compromise payment systems. While breaches still occur, compliance helps mitigate the severity and frequency, providing a crucial layer of defense against sophisticated attacks like ransomware, phishing, and malware designed to steal financial information. The continuous updates to the standard reflect a proactive stance against emerging threats, ensuring that protective measures evolve with the threat landscape.
Fostering Consumer Trust
For consumers, the PCI framework provides an invisible but essential guarantee of security. Knowing that their payment card information is protected by industry-wide standards instills confidence in using credit and debit cards for online and in-store purchases. This trust is fundamental to the continued growth of the digital economy. A secure payment environment encourages increased transaction volumes, reduces hesitation from consumers, and ultimately drives economic activity, benefiting businesses and individuals alike.
Adapting to Emerging Technologies
The future of PCI will be defined by its adaptability to rapid technological advancements. As new payment methods emerge—such as contactless payments, mobile wallets, cryptocurrencies, and IoT-enabled transactions—PCI DSS must evolve to address their unique security challenges. The PCI SSC is actively involved in developing guidance and extensions to the core standard to cover these innovations, ensuring that security best practices extend to every new frontier of commerce. This includes addressing risks associated with biometric authentication, quantum computing threats, and the complexities of securing vast networks of interconnected devices. The Payment Card Industry, through its ongoing commitment to security and innovation, will remain a critical pillar in building a secure and trusted global digital economy.