Understanding the Threat to Connected Drone Ecosystems
In the rapidly evolving landscape of unmanned aerial systems (UAS), innovation often outpaces security considerations. As drones become more sophisticated, integrating deeply with cloud platforms, web applications, and ground control systems, they become increasingly susceptible to cyber threats. One such pervasive vulnerability is Cross-Site Scripting (XSS), a client-side code injection attack that can have profound implications for drone operations, data integrity, and even flight safety. While commonly associated with general web applications, the interconnected nature of modern drone technology makes understanding and mitigating XSS critical for safeguarding this cutting-edge sector.
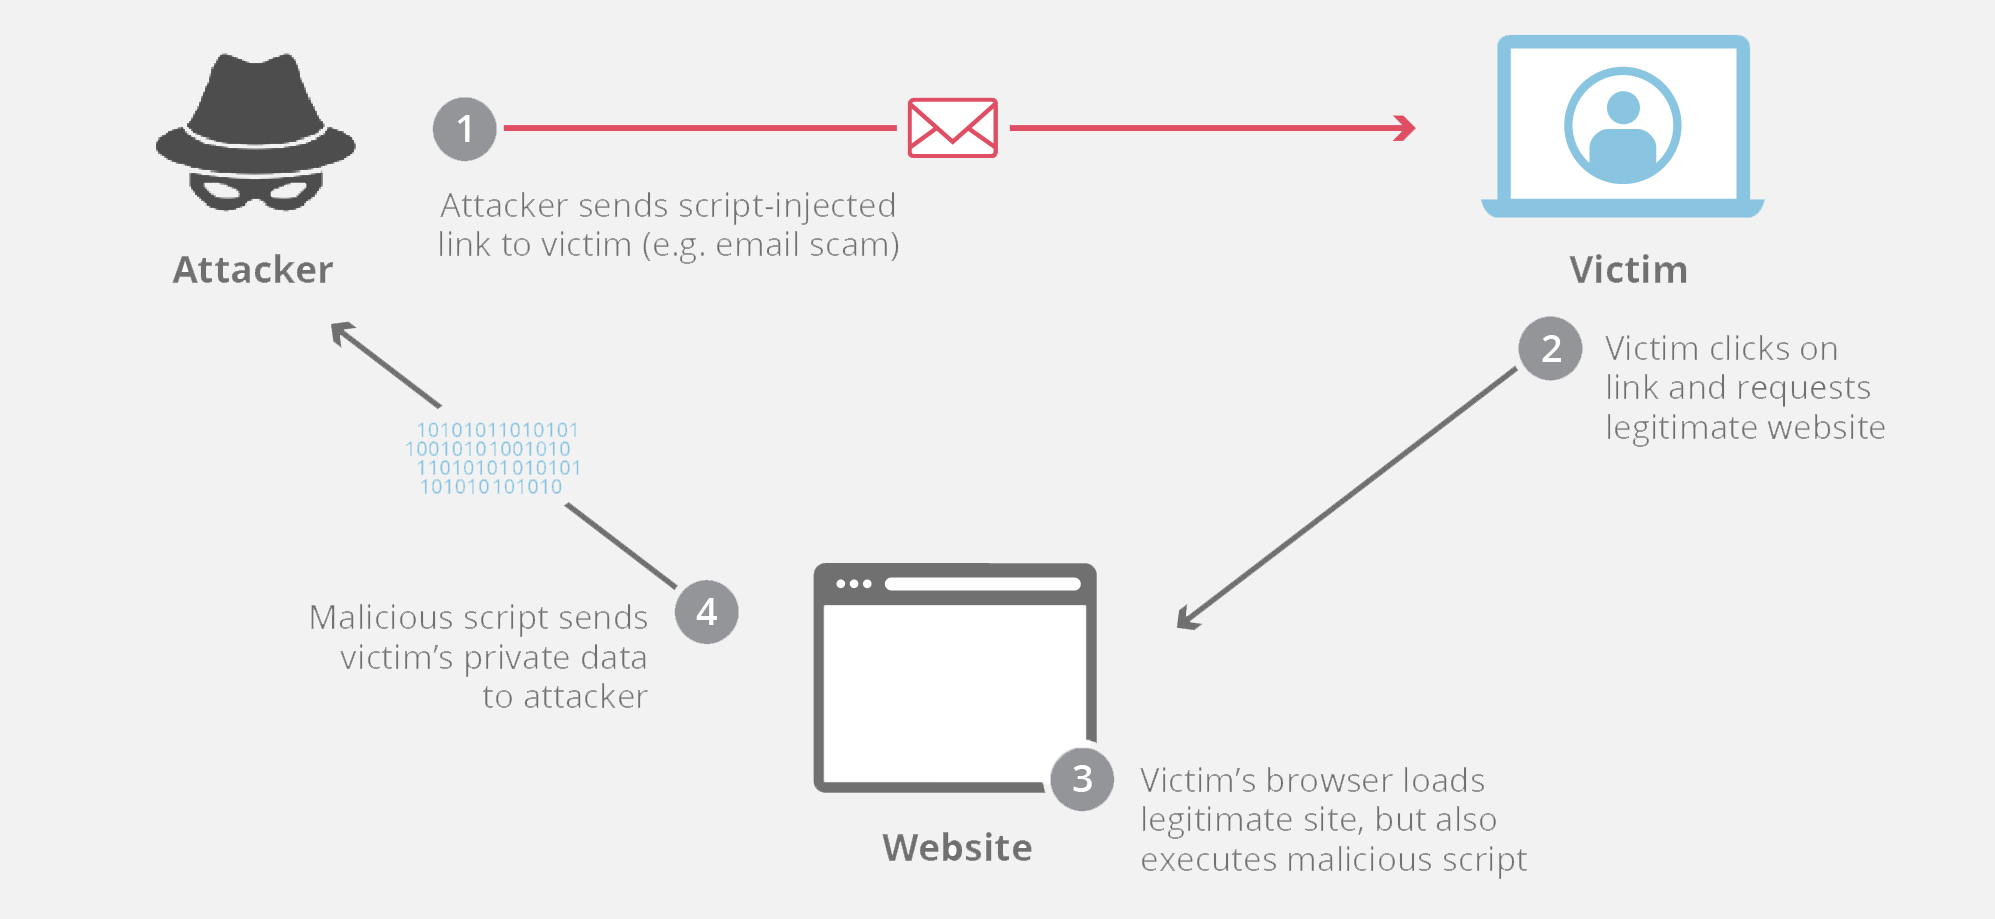
At its core, XSS exploits trust. It occurs when an attacker successfully injects malicious scripts, typically JavaScript, into a legitimate and trusted website or web application. When a user’s browser loads the vulnerable page, these malicious scripts are executed as if they were part of the trusted application, allowing the attacker to bypass access controls, steal sensitive information, or even manipulate the user’s interaction with the site. For drone operators, manufacturers, and service providers, this can mean compromised telemetry data, unauthorized access to flight plans, or even control over connected drone services.
The Core Mechanism of XSS
XSS attacks fundamentally leverage the browser’s trust in content delivered by a web server. When a web application fails to properly validate, filter, or encode user-supplied input before rendering it back to the user’s browser, an attacker can inject arbitrary client-side scripts. These scripts then run within the context of the user’s browser, essentially inheriting the permissions and access rights of the legitimate web application.
Consider a drone fleet management portal where operators log in to schedule flights, review mission data, or update drone firmware. If a comment section or a user profile field on this portal is vulnerable to XSS, an attacker could inject a script. When another legitimate operator views that page, their browser executes the attacker’s script. This script could then perform actions such as:
- Session hijacking: Stealing the victim’s session cookies, allowing the attacker to impersonate the victim and gain unauthorized access to their drone management account.
- Defacement: Modifying the content of the vulnerable page, potentially displaying false information or disrupting operational interfaces.
- Malicious redirects: Forcing the victim’s browser to an attacker-controlled site, potentially for phishing purposes.
- Keylogging: Capturing keystrokes entered by the victim on the page, leading to credential theft.
- Data exfiltration: Sending sensitive data, such as flight logs, user IDs, or internal communications, from the drone management portal to an attacker-controlled server.
Reflective, Stored, and DOM-based XSS Explained
XSS vulnerabilities are generally categorized into three primary types, each with distinct attack vectors and implications for drone technology:
Reflective XSS (Non-Persistent)
This is the most common type. The malicious script is “reflected” off the web server to the user’s browser. The attacker crafts a malicious URL containing the script and tricks a victim into clicking it. When the victim’s browser sends a request to the server, the server includes the script in its response, which the browser then executes. For drone applications, this could involve a crafted link sent via email to a drone operator that, when clicked, executes a script in their browser to steal their session cookie for a flight planning application.
Stored XSS (Persistent)
This is arguably the most dangerous type. The malicious script is permanently stored on the target server, typically in a database, forum, comment field, or a user profile. When victims browse the affected page, their browsers retrieve the malicious script from the server, and it executes. In the drone context, an attacker might inject a script into a shared flight log, a drone maintenance report, or a collaborative mission planning interface. Any user viewing that content later would unwittingly execute the script, potentially leading to widespread compromise across an entire drone team or organization.
DOM-based XSS
This type of XSS occurs entirely on the client-side, within the user’s browser, without the malicious script ever touching the web server. It exploits vulnerabilities in client-side code that manipulates the Document Object Model (DOM) of a web page using data sourced from the URL (e.g., URL fragments, query parameters). An attacker might craft a URL that, when loaded by a victim, causes the client-side script in a drone dashboard application to improperly process a part of the URL, leading to script execution within the victim’s browser. This bypasses server-side security measures, making it particularly insidious.
XSS Vulnerabilities in Drone Management Platforms
The modern drone ecosystem relies heavily on web-based interfaces and cloud services for everything from mission planning and fleet management to data analysis and compliance reporting. These platforms, if not developed with robust security practices, become prime targets for XSS attacks, with potentially severe consequences for operational integrity and safety.
Impact on Flight Planning and Telemetry Data
Imagine a cloud-based flight planning application where drone operators define waypoints, altitudes, and mission parameters. An XSS vulnerability in such an application could allow an attacker to inject scripts that:
- Manipulate flight plans: While direct manipulation of a drone’s in-flight commands via XSS is complex, an attacker could alter submitted flight plans before they are sent to the drone, potentially leading to unauthorized deviations, entry into restricted airspace, or even collisions.
- Exfiltrate sensitive telemetry: Real-time telemetry data, including drone location, speed, altitude, and sensor readings, is often displayed or stored in web interfaces. An XSS attack could steal this data, revealing sensitive operational details to adversaries.
- Corrupt mission logs: An attacker could inject scripts to alter or delete historical flight logs, obscuring evidence of unauthorized activity or hindering post-mission analysis and compliance audits.
Compromising User Accounts and Operational Control
The most immediate danger of XSS in a drone context is the compromise of user accounts. If an attacker gains access to a drone operator’s credentials or session tokens through XSS, they could log in as that operator. This could grant them:
- Unauthorized access to drone fleets: Scheduling unauthorized flights, deploying drones for malicious purposes, or disrupting legitimate operations.
- Manipulation of ground control software: If ground control systems are web-enabled or interact with vulnerable web services, an XSS attack could potentially lead to remote manipulation of drone parameters or flight instructions.
- Access to confidential data: Including sensitive company information, client data, or proprietary drone designs stored within interconnected web applications.

Supply Chain Risks through Web Interfaces
Drone manufacturing and maintenance increasingly rely on complex supply chains, often managed through vendor portals and collaborative web platforms. An XSS vulnerability in a supplier’s portal, or even in a drone manufacturer’s internal asset management system, could pose significant risks:
- Firmware injection risks: If a web interface is used for managing firmware updates or software distribution to drones, an XSS attack could theoretically be part of a broader exploit chain to inject malicious firmware updates.
- Intellectual property theft: Access to internal documentation, schematics, or bill of materials, which might be stored and accessed via web applications vulnerable to XSS.
- Disruption of manufacturing or logistics: Interfering with web-based ordering systems, inventory management, or shipping manifests.
Safeguarding Drone Operations from XSS Attacks
Mitigating XSS vulnerabilities requires a multi-layered approach, emphasizing secure coding practices, rigorous testing, and continuous monitoring throughout the entire development and operational lifecycle of drone-related web applications. For “Tech & Innovation” in the drone space to thrive securely, these measures are non-negotiable.
Input Validation and Output Encoding
The cornerstone of XSS prevention lies in treating all user-supplied data as untrusted.
- Input Validation: At the point where data is received by the server, it must be strictly validated against expected formats and content. This means rejecting unexpected characters, enforcing length limits, and ensuring data types are correct. For example, a flight ID field should only accept alphanumeric characters, not
<script>tags. - Output Encoding/Escaping: Before any user-supplied data is displayed back to a user’s browser, it must be properly encoded or escaped. This converts potentially malicious characters (like
<,>,&,",') into their harmless HTML entities (e.g.,<becomes<). This way, the browser interprets them as data to be displayed, not as executable code. Modern web frameworks often provide built-in functions for safe output encoding.
Content Security Policy (CSP) Implementation
Content Security Policy (CSP) is an HTTP response header that allows web application developers to control which resources (e.g., JavaScript, CSS, images) the user agent is allowed to load. By specifying a strong CSP, drone-related web applications can significantly reduce the risk and impact of XSS attacks:
- Whitelisting trusted sources: CSP can restrict script execution to only those originating from trusted domains or directly inline within the page. This prevents an attacker’s injected script, even if present on the page, from loading external malicious resources or executing its code.
- Preventing inline scripts: Strict CSP policies can block all inline
<script>tags, forcing developers to externalize all JavaScript. This makes it harder for an attacker to execute injected code directly. - Reporting violations: CSP can be configured to report violations to a specified URI, providing valuable intelligence for incident response and further hardening.
Secure Development Lifecycles and Regular Audits
Integrating security into the entire Software Development Life Cycle (SDLC) is paramount for drone technology innovation.
- Security by Design: Threat modeling and security requirements should be addressed from the initial design phase of any drone management platform or web service.
- Developer Training: Educating developers on common web vulnerabilities, including XSS, and secure coding best practices is crucial.
- Automated Security Testing: Regularly employing static application security testing (SAST) and dynamic application security testing (DAST) tools to identify XSS vulnerabilities during development and testing phases.
- Penetration Testing: Engaging ethical hackers to conduct comprehensive penetration tests on production or pre-production drone web applications to uncover exploitable XSS flaws.
- Vulnerability Management: Establishing a robust process for reporting, tracking, and remediating identified vulnerabilities promptly.
The Broader Implications for Drone Innovation
Securing against XSS is not merely a technical exercise; it underpins the very trust and reliability required for the continued advancement and widespread adoption of drone technology. As drones move beyond niche applications into critical infrastructure, logistics, and even urban air mobility, their security posture directly impacts public safety and economic viability.
Trust, Compliance, and Data Integrity
An XSS incident within a drone ecosystem can erode user trust, lead to costly data breaches, and incur significant regulatory fines. Ensuring the integrity of flight data, operator credentials, and sensitive operational parameters is fundamental for compliance with aviation regulations (e.g., FAA, EASA) and industry standards. A compromised web interface due to XSS could undermine data authenticity, making it difficult to prove regulatory compliance or investigate incidents accurately.

Protecting Autonomous Systems and AI Implementations
The future of drones lies heavily in autonomous flight and AI-powered decision-making. These advanced systems often rely on cloud-based data feeds, machine learning models accessed via APIs, and web-based interfaces for monitoring and control. While XSS directly targets client-side web interactions, a successful attack could be an entry point to compromise adjacent systems, manipulate input data for AI models, or gain unauthorized access to the control mechanisms of autonomous drone fleets. Ensuring the web interfaces that manage these sophisticated technologies are XSS-hardened is a foundational step in securing the next generation of drone innovation.
In conclusion, XSS is a potent threat that demands serious attention within the drone technology sector. By understanding its mechanisms, identifying potential vulnerabilities in connected drone platforms, and implementing robust security measures, we can ensure that the innovation in aerial technology continues to soar, securely and reliably.