
In the rapidly evolving landscape of tech and innovation, where cloud computing forms the bedrock of countless advancements from AI-driven solutions to autonomous systems and sophisticated remote sensing applications, robust security is not merely an afterthought—it is a fundamental prerequisite. At the heart of securing these cutting-edge deployments within the Amazon Web Services (AWS) ecosystem lies AWS Identity and Access Management, or IAM. AWS IAM is a core service that empowers organizations to securely control access to AWS services and resources. It’s the mechanism through which you define who can access what, under what conditions, ensuring that your innovative projects, from mapping vast terrains with remote sensing to powering intelligent autonomous flight, operate with the highest level of security and integrity.
The Core of Cloud Security: Understanding AWS IAM
AWS IAM serves as the central pillar for managing access and permissions across your entire AWS environment. In an age where digital threats are constant and data breaches can cripple innovation, IAM provides the granular control necessary to protect sensitive data and operational critical resources. Without a robust IAM strategy, the immense power of cloud computing platforms like AWS becomes a double-edged sword, offering incredible capabilities but also potential vulnerabilities. For any organization pushing the boundaries of technology, whether developing AI follow modes for drones or building complex mapping infrastructures, understanding and effectively utilizing IAM is non-negotiable.
Identity Management
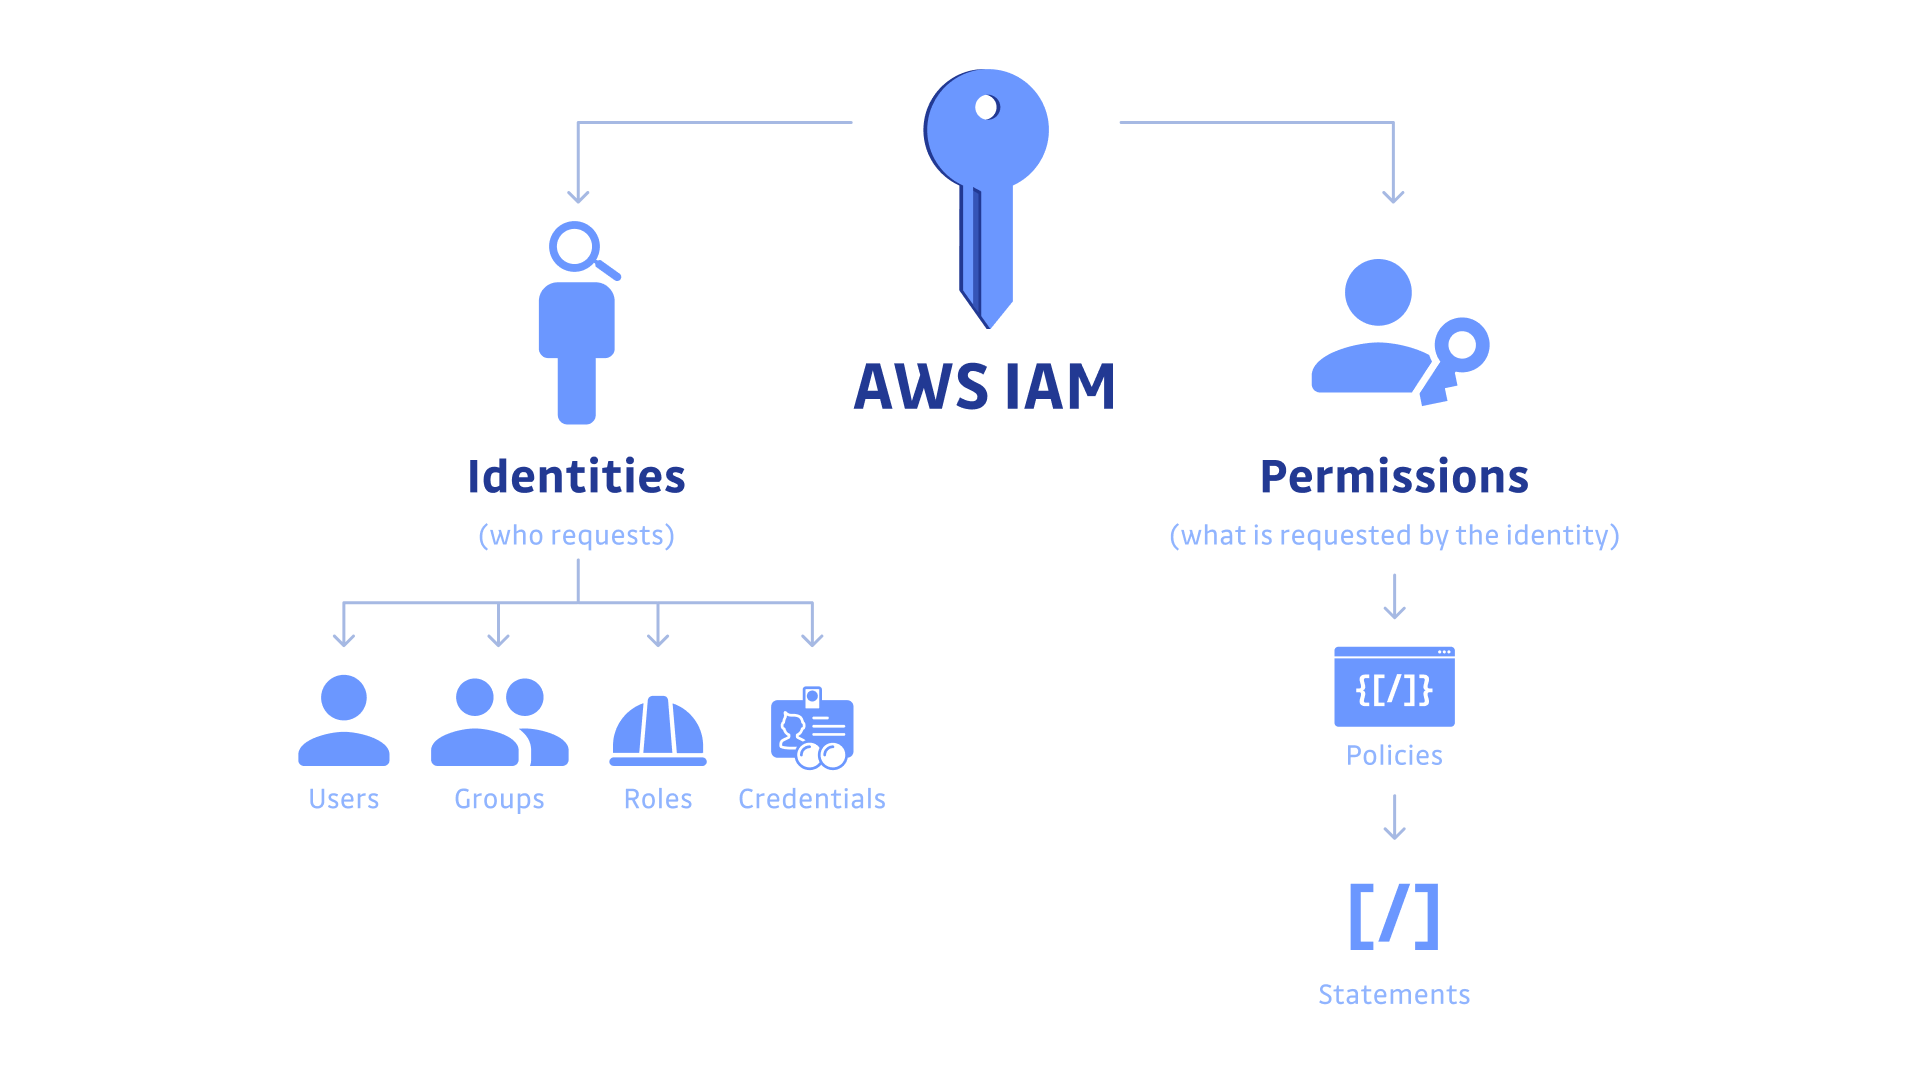
At its essence, IAM is about identity management. It allows you to create and manage AWS users and groups, providing a clear definition of who (or what) is interacting with your AWS resources. This includes human users—like your data scientists developing AI models or engineers deploying autonomous flight algorithms—as well as programmatic identities such as applications, services, and even IoT devices. Each identity in AWS IAM represents a unique entity that might need to perform actions within your cloud environment. Properly identifying and categorizing these entities is the first crucial step in establishing a secure and controllable environment for all your tech innovations.
Access Control
Beyond merely identifying users, IAM’s primary function is access control. It dictates what actions an identified entity can perform on specific AWS resources. This means specifying whether a particular AI model is allowed to read data from a specific S3 bucket, or if an autonomous flight system has permission to publish telemetry data to an IoT topic. This level of control is paramount for maintaining the security and integrity of your innovative applications. Without it, an unauthorized entity could potentially access sensitive research data, disrupt critical autonomous operations, or compromise the integrity of mapping data. IAM ensures that every interaction with your cloud resources is intentional, authorized, and aligned with your security policies.
Resource Authorization
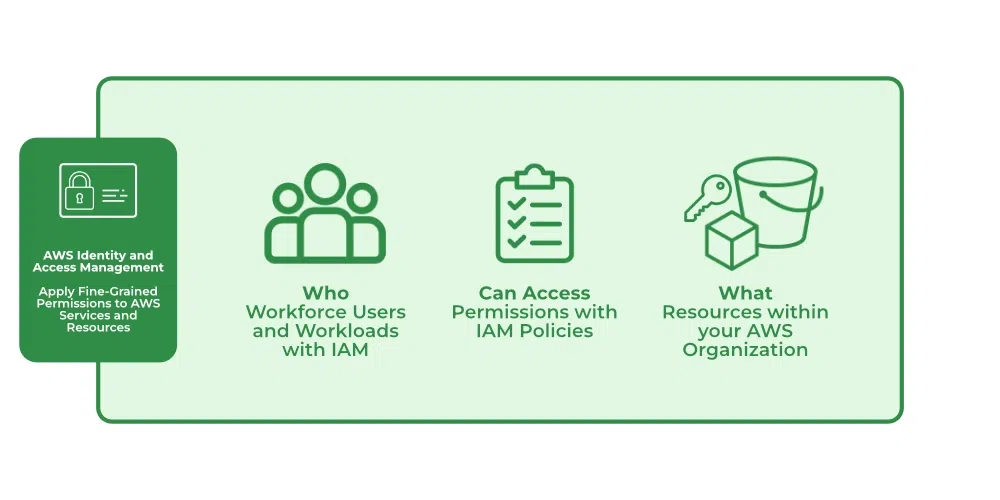
Resource authorization is the tangible outcome of IAM’s identity management and access control features. It’s the process by which AWS determines whether a particular request to access a resource (e.g., an S3 bucket, an EC2 instance, a Lambda function) should be granted or denied. This determination is made based on the identity making the request, the resources being accessed, and the specific permissions defined through IAM policies. For complex innovative projects involving multiple services and data flows—like real-time remote sensing data processing or AI model training pipelines—IAM ensures that only authorized components can interact with the necessary data and compute resources, safeguarding the entire system against unauthorized access and potential misuse.
Key Components and How They Work
To effectively manage identities and control access, AWS IAM leverages several interconnected components, each playing a vital role in establishing a secure environment for tech innovation. Understanding these building blocks is crucial for designing a robust security architecture that supports the dynamic needs of modern technological advancements.
Users, Groups, and Roles
- Users: In IAM, a User represents a person or service that interacts with AWS. For instance, an individual engineer working on autonomous drone software, or a data scientist training a new machine learning model, would typically have an IAM User account. Each user can be assigned specific permissions.
- Groups: IAM Groups are collections of Users. Instead of assigning permissions to individual users, you can assign permissions to a group, and all users within that group inherit those permissions. This simplifies management significantly, especially in larger teams. For example, all members of your “Remote Sensing Data Processing” team could be part of a group with permissions to access specific S3 buckets storing imagery and to run analysis jobs on EC2 instances.
- Roles: IAM Roles are designed to grant temporary permissions to trusted entities. Unlike users, roles are not tied to a specific individual but are assumed by entities like AWS services (e.g., an EC2 instance assuming a role to access an S3 bucket), external identities (federated users), or even other AWS accounts. Roles are incredibly powerful for securing innovative applications where services need to interact with each other without hardcoding credentials, such as an autonomous drone’s on-board computing unit assuming a role to upload captured mapping data directly to an S3 bucket.
Policies and Permissions
At the heart of access control are IAM Policies. These are JSON documents that define permissions. They specify what actions are allowed or denied on which resources, under what conditions. Policies can be attached to Users, Groups, or Roles.
- Identity-based Policies: These are attached to IAM identities (users, groups, and roles) and grant permissions to that identity. For example, a policy might allow a specific user to launch EC2 instances of a certain type or permit a role used by an autonomous system to write data to a particular DynamoDB table.
- Resource-based Policies: These policies are attached directly to AWS resources, such as S3 buckets, SQS queues, or KMS keys. They specify who has access to that specific resource and what actions they can perform. An S3 bucket policy, for instance, might allow an external organization’s AWS account to upload data for a joint remote sensing project.
- Permissions Boundary: This advanced feature allows you to set the maximum permissions an identity-based policy can grant to an IAM entity. It’s a way to delegate administrative authority without granting full administrative privileges, ensuring that even administrators cannot accidentally or intentionally exceed predefined security limits, critical for large-scale innovative projects with multiple development teams.
Multi-Factor Authentication (MFA)

For an additional layer of security, IAM strongly supports Multi-Factor Authentication (MFA). MFA requires users to provide two or more verification factors to gain access to their AWS account. This typically involves something they know (their password) and something they have (a physical or virtual MFA device). Implementing MFA significantly reduces the risk of unauthorized access due to compromised credentials, which is paramount when dealing with sensitive intellectual property in areas like AI algorithms, proprietary autonomous flight code, or confidential remote sensing data. For any team working on cutting-edge innovation, MFA should be a mandatory part of their AWS access strategy.
IAM in the Ecosystem of Tech & Innovation
AWS IAM is not just a security tool; it’s an enabler of innovation. By providing a secure and controlled environment, it allows developers, engineers, and data scientists to focus on building groundbreaking technologies without constantly worrying about underlying security vulnerabilities. Its capabilities are intrinsically linked to the successful and secure deployment of advanced tech solutions.
Securing AI and Machine Learning Workloads
AI and Machine Learning (ML) initiatives often involve vast amounts of sensitive data, complex models, and specialized computing resources. IAM plays a critical role in securing every stage of the AI/ML lifecycle. It ensures that only authorized data scientists can access and train models with proprietary datasets stored in S3, that ML models deployed via SageMaker have the necessary permissions to access inference data without over-privileging, and that automated ML pipelines can securely interact with various AWS services like Lambda, Glue, and Redshift. By enforcing strict access policies, IAM prevents unauthorized access to valuable training data, protects intellectual property embedded in AI models, and ensures the integrity of AI-driven decisions, which can range from anomaly detection in remote sensing imagery to predictive maintenance for autonomous systems.
Enabling Autonomous Systems and IoT Deployments
The rise of autonomous systems, from self-driving vehicles to intelligent drones and robots, heavily relies on secure, real-time data exchange and command execution. IoT deployments, the backbone of many autonomous solutions, involve thousands, if not millions, of devices communicating with the cloud. IAM is indispensable here. Each IoT device or autonomous agent can be assigned a unique IAM role or credential, granting it specific, limited permissions—for example, to publish telemetry data to AWS IoT Core, retrieve mission parameters from DynamoDB, or update its firmware from S3. This fine-grained control ensures that even if an individual device is compromised, the blast radius is contained. It allows for secure communication, data collection (e.g., for mapping and remote sensing), and remote control, making robust and scalable autonomous operations a reality.
Data Integrity for Mapping and Remote Sensing
High-resolution mapping, remote sensing, and geospatial intelligence projects generate and process massive volumes of often sensitive data, from satellite imagery to lidar scans. The integrity and confidentiality of this data are paramount. IAM provides the tools to ensure that only authorized processes or users can upload, modify, or delete this invaluable information. Through IAM policies, access to S3 buckets storing raw imagery, Aurora databases containing geospatial metadata, or EC2 instances running powerful GIS analysis software can be tightly controlled. This protects the veracity of environmental data, urban planning models, and critical infrastructure assessments derived from remote sensing, thereby upholding the reliability of insights drawn from these innovative technologies.
Fostering Secure Development and DevOps Practices
Modern software development, especially in innovative fields, thrives on agility and continuous delivery (DevOps). IAM integrates seamlessly into these practices. By creating specific roles for CI/CD pipelines, automated testing frameworks, and deployment services, IAM enables secure automation without the need for static, long-lived credentials. Developers can be granted permissions through groups that align with their project roles (e.g., “AI Development Team,” “Autonomous Flight Testing”), ensuring they have the necessary access to development and staging environments but are restricted from production systems. This promotes a secure-by-design approach, where security is woven into the development lifecycle from the outset, accelerating innovation while minimizing risks.
Best Practices for Robust IAM Implementation
To fully leverage AWS IAM’s power in supporting your tech and innovation efforts, adherence to best practices is essential. These guidelines help build a resilient security posture, crucial for protecting your groundbreaking work.
Principle of Least Privilege
The most fundamental IAM best practice is the Principle of Least Privilege. This dictates that you should grant only the permissions required to perform a task, and nothing more. Instead of granting broad administrative access, create specific policies that allow only the necessary actions on the necessary resources. For an autonomous drone system, this means granting only s3:PutObject to a specific bucket for uploading data, rather than s3:* on all buckets. This minimizes the potential impact of compromised credentials or misconfigurations, which is particularly vital in highly sensitive areas like AI model development or remote sensing data processing.
Regular Auditing and Monitoring
An active security posture requires continuous vigilance. AWS IAM integrates with services like AWS CloudTrail, which logs all API calls made to your AWS account. Regularly reviewing CloudTrail logs allows you to monitor access patterns, identify unusual activity, and detect potential security breaches. This is critical for innovative projects where new services are constantly being deployed and access requirements may change frequently. Tools like IAM Access Analyzer can further help by identifying unintended access to your resources, ensuring your mapping data or AI models aren’t inadvertently exposed to external entities.
Strong Credential Management
Secure management of credentials is the bedrock of IAM security. Never embed access keys directly into application code. Instead, utilize IAM roles for AWS services and temporary credentials generated by AWS Security Token Service (STS). For human users, enforce strong password policies, enable Multi-Factor Authentication (MFA) across the board, and rotate credentials regularly. AWS Secrets Manager can be used to securely store and rotate database credentials and API keys, crucial for applications that interact with external services or sensitive data stores within your innovative tech stack. By prioritizing robust credential management, you fortify the first line of defense against unauthorized access to your valuable intellectual property and operational systems.