
In an increasingly interconnected digital world, the concept of encrypted data has moved from the esoteric realm of cryptography experts to a fundamental pillar of daily technological interaction. At its core, encrypted data is information that has been transformed using an algorithm to make it unreadable and unusable to anyone without the proper decryption key. This process is a sophisticated form of digital scrambling, designed to protect the confidentiality, integrity, and authenticity of sensitive information across myriad platforms and applications. It is the invisible shield that safeguards everything from personal messages and financial transactions to national security communications and critical infrastructure control systems. Understanding encrypted data is not merely an academic exercise; it is essential for comprehending the security landscape of modern tech and innovation.

The Core Concept of Encryption
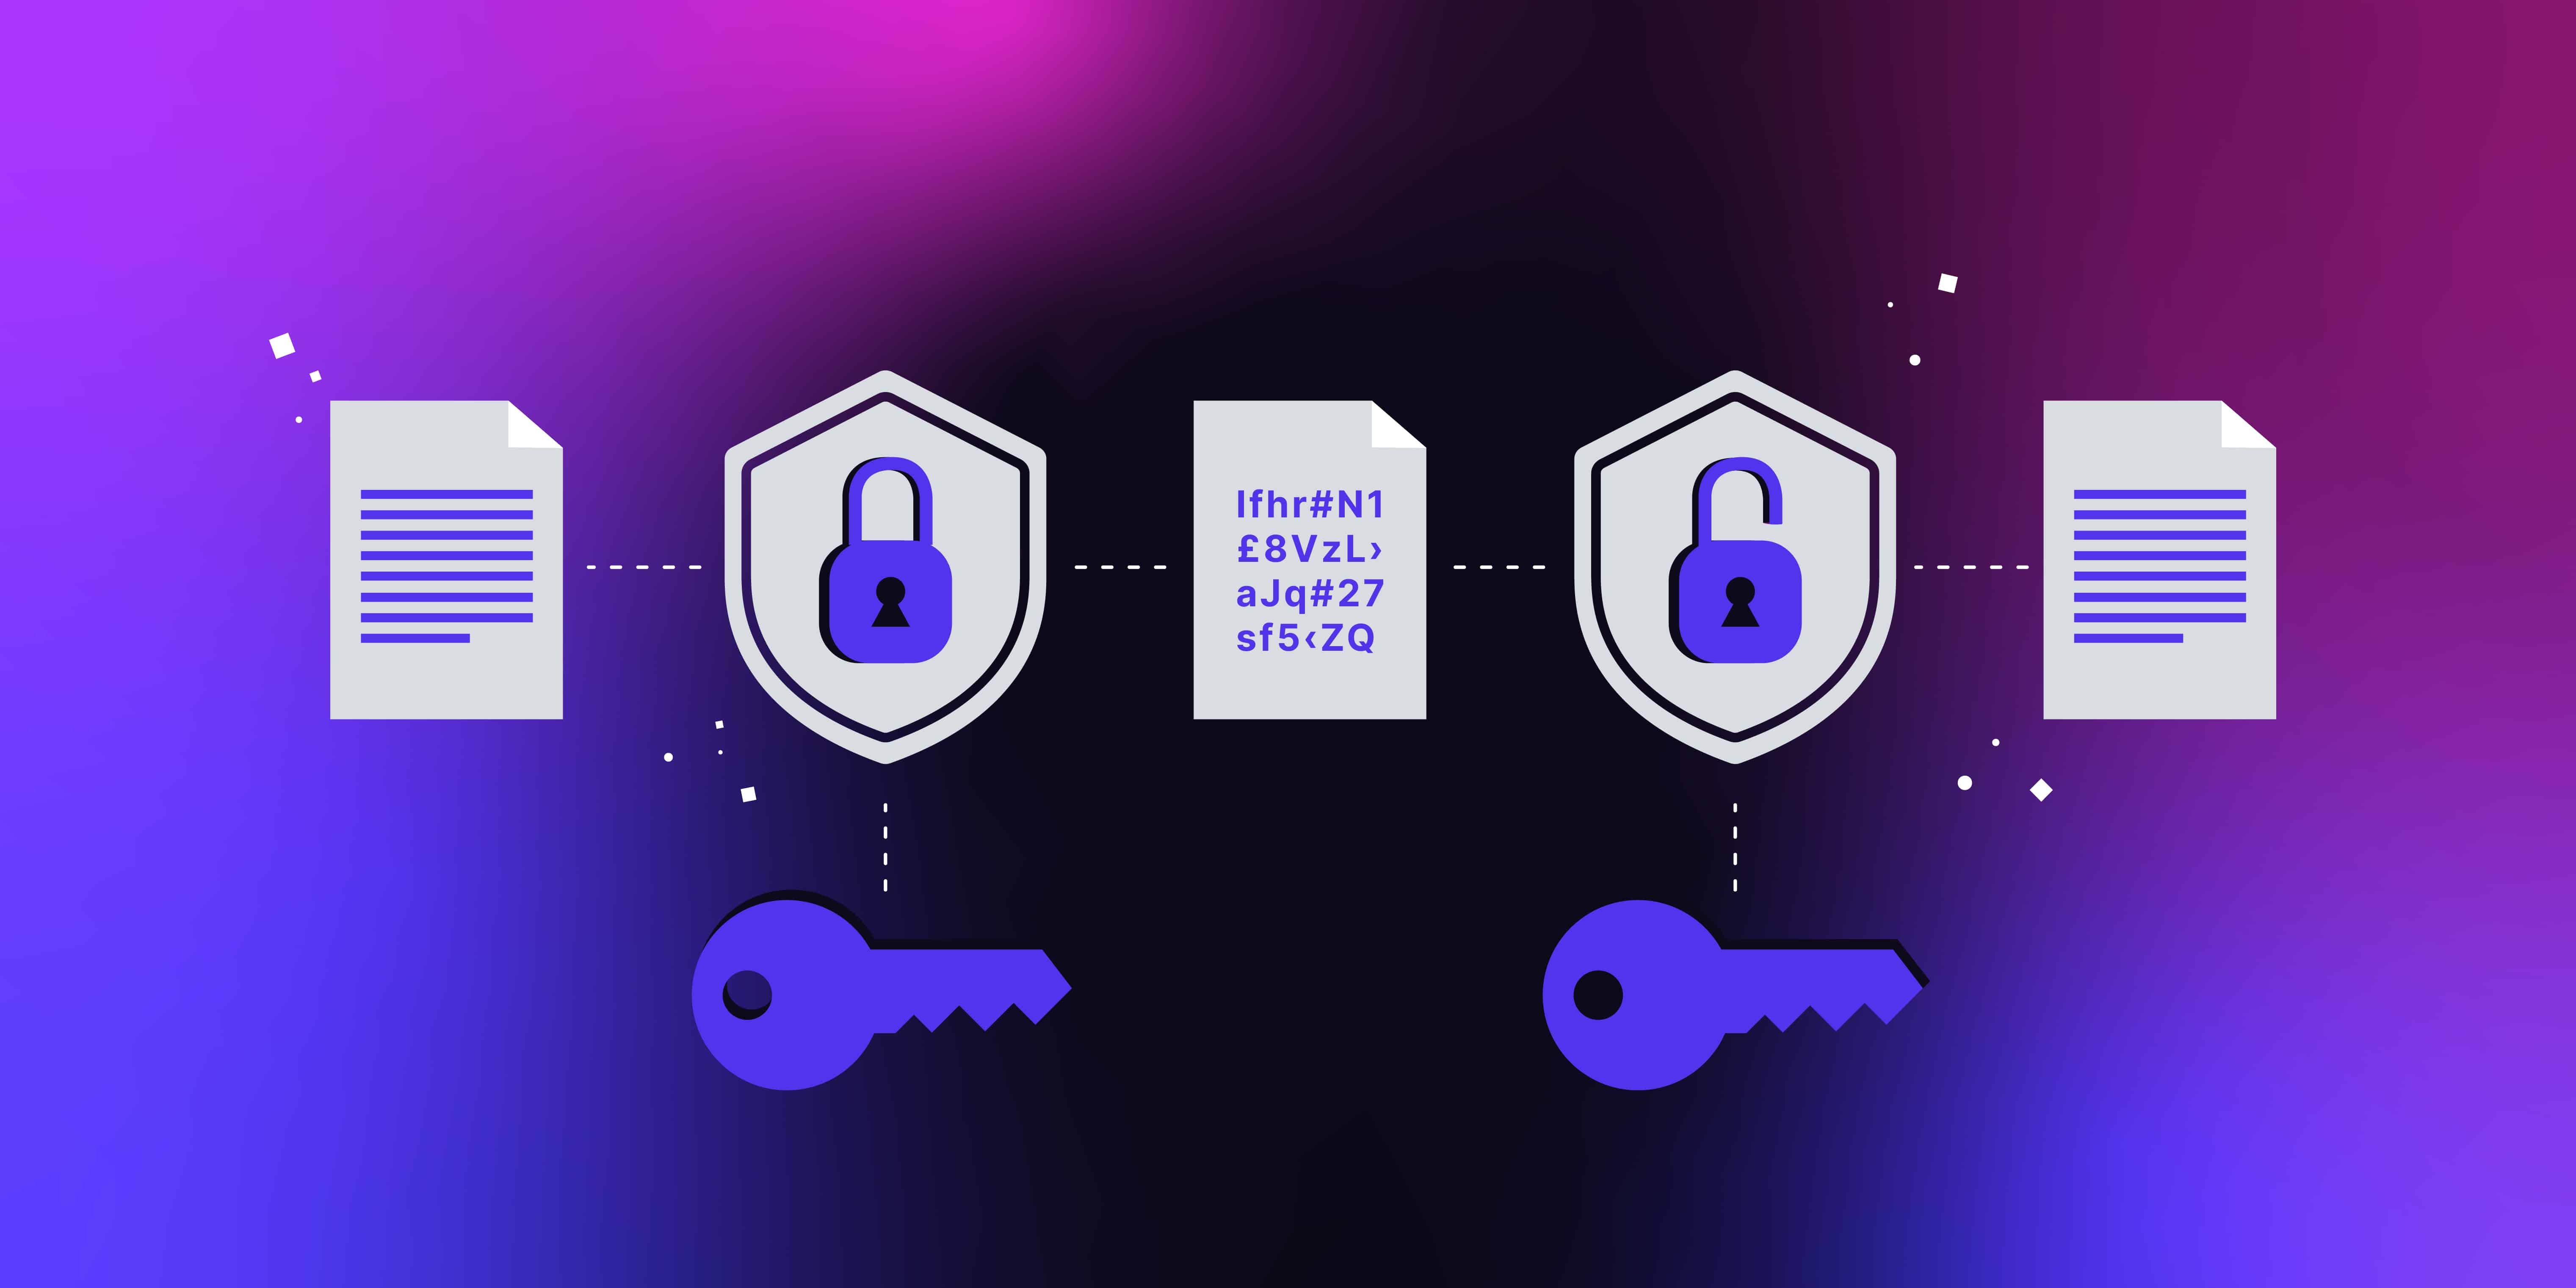
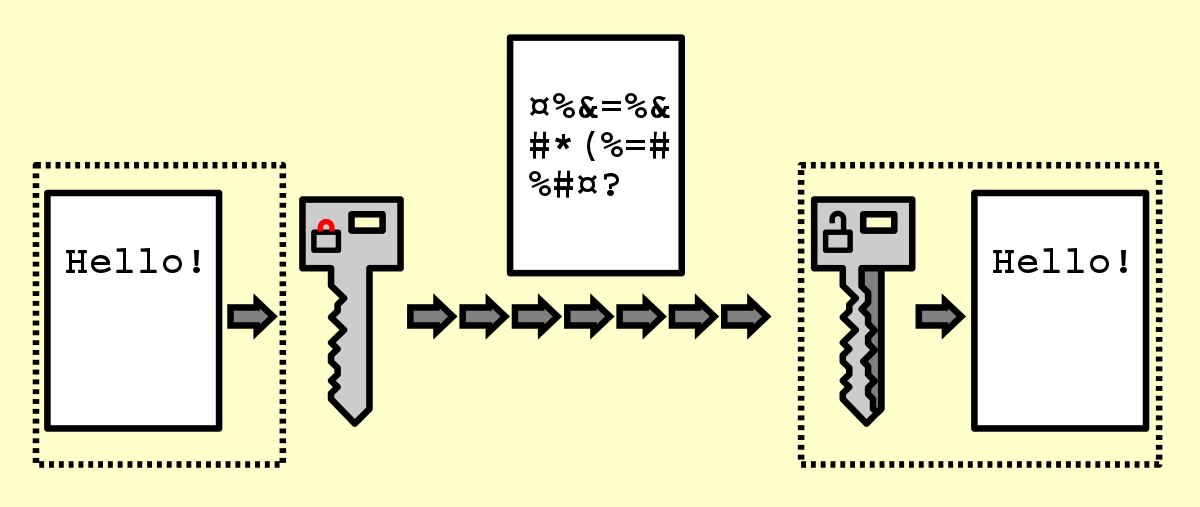
Encryption begins with plaintext – the original, readable information – and applies a mathematical function, or algorithm, to transform it into ciphertext. This ciphertext appears as a jumble of characters, utterly meaningless without the specific key that can reverse the process. The strength of this transformation lies in the complexity of the algorithm and the secrecy of the key, making it computationally infeasible for unauthorized parties to revert the ciphertext back to plaintext.
From Plaintext to Ciphertext
The journey from plaintext to ciphertext is orchestrated by an encryption algorithm, also known as a cipher. These algorithms are precise sets of rules that dictate how data should be manipulated. Early ciphers, like the Caesar cipher, were simple substitutions, easily broken. Modern algorithms, however, employ incredibly complex mathematical operations, including permutations, substitutions, and modular arithmetic, often repeated over multiple rounds, to achieve a high degree of diffusion and confusion. Diffusion ensures that changes to a single plaintext bit affect many ciphertext bits, while confusion makes the relationship between the key and the ciphertext as complex as possible. This intricate dance makes brute-force attacks – attempting every possible key – an astronomically improbable endeavor for sufficiently long and random keys.
The Role of Cryptographic Keys
Central to any encryption system is the cryptographic key. This is a piece of information, typically a string of bits, that works in conjunction with the algorithm to encrypt and decrypt data. Think of it as the secret password that unlocks the scrambled message. The security of encrypted data hinges directly on the strength and secrecy of its key. If a key is compromised, the encryption becomes worthless, as any attacker possessing it can easily decrypt the data. Keys vary in length, with longer keys offering exponentially greater security, making them more resistant to exhaustive search attacks. The management, generation, storage, and exchange of these keys, collectively known as key management, is a critical and often challenging aspect of maintaining robust cryptographic security. Poor key management can undermine even the strongest encryption algorithms.
The Imperative for Data Security in the Digital Age
The proliferation of digital technologies has created an unprecedented volume of data, much of it highly sensitive. From personal health records and financial transactions to proprietary business strategies and governmental intelligence, the need to protect this data from unauthorized access, manipulation, or disclosure is paramount. Data breaches can lead to financial losses, reputational damage, identity theft, and even threats to national security. Encryption serves as the primary defense mechanism against these threats. It ensures that even if data falls into the wrong hands, it remains indecipherable and therefore useless to the attacker. In a world where data is constantly in transit and stored in myriad locations, encryption provides the foundational layer of trust and privacy necessary for individuals, businesses, and governments to operate securely. Regulatory frameworks like GDPR, HIPAA, and CCPA further underscore the legal and ethical imperative to implement strong encryption practices for data protection.
Types of Encryption Algorithms
Encryption algorithms generally fall into two broad categories: symmetric-key and asymmetric-key encryption. Each has distinct characteristics, applications, and advantages, contributing to a comprehensive security architecture.
Symmetric-Key Encryption (Private-Key)
Symmetric-key encryption, also known as private-key encryption, uses the same key for both encryption and decryption. This means that both the sender and the receiver must possess this shared secret key. Examples include algorithms like AES (Advanced Encryption Standard), DES (Data Encryption Standard), and Twofish. Symmetric encryption is highly efficient and fast, making it suitable for encrypting large volumes of data. However, its primary challenge lies in secure key distribution: how do two parties securely exchange the shared key without risk of interception? If an attacker intercepts the key during distribution, all encrypted communications thereafter are compromised. This “key exchange problem” is a significant consideration in symmetric cryptography.
Asymmetric-Key Encryption (Public-Key)
Asymmetric-key encryption, or public-key encryption, addresses the key distribution problem by using a pair of mathematically related keys: a public key and a private key. The public key can be freely shared with anyone, while the private key must be kept secret by its owner. Data encrypted with the public key can only be decrypted with the corresponding private key, and vice-versa. RSA (Rivest–Shamir–Adleman) and ECC (Elliptic Curve Cryptography) are prominent examples. This system allows anyone to encrypt a message for a recipient using their public key, but only the recipient, who holds the private key, can decrypt it. Asymmetric encryption is computationally more intensive and slower than symmetric encryption, making it less ideal for encrypting large data sets. Its strength lies in secure key exchange and digital signatures, often used to establish secure channels for symmetric key exchange.
Hashing: A One-Way Street
While not strictly encryption, hashing is a related cryptographic process frequently used in conjunction with encryption to ensure data integrity. A hash function takes an input (or ‘message’) and returns a fixed-size string of bytes, typically a ‘hash value’ or ‘message digest’. Unlike encryption, hashing is a one-way function; it is computationally infeasible to reverse the process and reconstruct the original input from the hash value. Even a tiny change in the input data will produce a drastically different hash value, making hashes excellent for detecting data tampering. Common hashing algorithms include SHA-256 and MD5 (though MD5 is now considered insecure for many applications due to collision vulnerabilities). Hashing is used for storing passwords (storing hashes instead of actual passwords), verifying file integrity, and creating digital signatures.
How Encryption Safeguards Information
Encryption provides a multi-faceted approach to information security, extending beyond mere secrecy to encompass integrity, authenticity, and non-repudiation. These security services are vital for trustworthy digital interactions.
Confidentiality: Keeping Secrets Safe
Confidentiality is the most intuitive and direct benefit of encryption. By transforming plaintext into an unreadable format, encryption ensures that sensitive information remains private and inaccessible to unauthorized individuals. Whether it’s an email containing personal details, financial records stored on a cloud server, or strategic business plans transmitted across a network, encryption acts as a robust barrier. Even if an attacker manages to intercept or access the encrypted data, without the correct decryption key, the information remains gibberish, thus maintaining its confidentiality. This protection is crucial for safeguarding personal privacy, intellectual property, and critical operational data from espionage, theft, or unauthorized disclosure.
Integrity: Ensuring Data Authenticity
While confidentiality prevents unauthorized access, integrity ensures that data has not been altered or tampered with during storage or transmission. Encryption, especially when combined with digital signatures or Message Authentication Codes (MACs), plays a pivotal role in verifying data integrity. By digitally signing encrypted data using an asymmetric key pair, the recipient can verify that the data originated from the claimed sender and has not been modified since it was signed. A change, however minor, in the data would cause the signature verification to fail, immediately alerting the recipient to potential tampering. Hash functions are also fundamental to integrity checks, as any alteration to the original data will produce a different hash, signaling a compromise.
Authentication: Verifying Identities
Authentication is the process of verifying the identity of a user, device, or system. Encryption is instrumental in establishing secure authentication mechanisms. For instance, in public-key infrastructure (PKI), digital certificates, which rely on asymmetric encryption, bind an individual’s or entity’s identity to their public key. When a server presents its digital certificate, a client can use the certificate authority’s public key to verify the server’s identity, ensuring it’s communicating with the legitimate entity rather than an impostor. Similarly, challenge-response authentication mechanisms often use encryption to prove identity without transmitting credentials in plaintext, further bolstering security against eavesdropping and impersonation.
Non-Repudiation: Proving Actions
Non-repudiation ensures that a party cannot deny having sent a message or performed an action. This is particularly important in legal and contractual digital interactions. Digital signatures, powered by asymmetric encryption, provide strong non-repudiation. When a sender signs a document with their private key, only they could have generated that specific signature. If the signature is successfully verified using their public key, the sender cannot legitimately deny having signed the document. This mechanism creates legally binding proof of origin and intent, comparable to a handwritten signature in the physical world, but with enhanced cryptographic assurances.
Practical Applications and Emerging Trends in Encrypted Data
Encrypted data underpins nearly every aspect of modern digital life, from the mundane to the mission-critical. Its applications are vast, and the field continues to evolve to meet new challenges and leverage innovative technologies.
Securing Communications and Transactions
One of the most widespread applications of encryption is securing communications. When you browse a website with “HTTPS” in the URL, you are using encryption (specifically TLS/SSL protocols) to secure the connection between your browser and the web server. This ensures that your login credentials, payment information, and browsing activity remain confidential. Messaging apps offering end-to-end encryption (E2EE) ensure that only the sender and intended recipient can read messages, even the service provider cannot access the plaintext. Financial transactions, whether online banking or mobile payments, rely heavily on encryption to protect sensitive account details and transaction data from fraud. VPNs (Virtual Private Networks) use encryption to create secure, private tunnels over public networks, protecting user privacy and data integrity.
Data at Rest vs. Data in Transit
Encryption is applied to data in two primary states: “data at rest” and “data in transit.” Data at rest refers to information stored on hard drives, SSDs, USB drives, cloud storage, or databases. Encrypting data at rest protects it from unauthorized access if the storage medium is stolen or compromised. Full disk encryption (FDE) and database encryption are common examples. Data in transit refers to information moving across networks, such as the internet, local area networks, or wireless connections. Securing data in transit is critical because network interception is a common attack vector. Protocols like TLS/SSL for web traffic, SSH for remote access, and IPSec for VPNs are designed to encrypt data as it travels across networks, protecting it from eavesdropping and tampering. A comprehensive security strategy mandates encryption for both states, ensuring continuous protection throughout the data lifecycle.
Homomorphic Encryption and Quantum Computing’s Challenge
The landscape of encryption is constantly evolving. One exciting frontier is homomorphic encryption, which allows computations to be performed directly on encrypted data without first decrypting it. This could revolutionize cloud computing and data privacy, enabling services to process sensitive information (e.g., medical data, financial models) without ever seeing the plaintext, thus greatly enhancing security and compliance. While still computationally intensive, advancements are steadily making it more practical.
Conversely, the advent of quantum computing poses a significant challenge to existing cryptographic standards. Many current asymmetric encryption algorithms, such as RSA and ECC, rely on the mathematical difficulty of factoring large numbers or solving elliptic curve problems – problems that quantum computers could potentially solve efficiently using algorithms like Shor’s algorithm. This threat necessitates the development of post-quantum cryptography (PQC) – new cryptographic algorithms that are resistant to attacks from both classical and quantum computers. Research and standardization efforts in PQC are ongoing, aiming to future-proof our digital infrastructure against the quantum threat and ensure that encrypted data remains secure for decades to come. The continuous innovation in encryption ensures that as technology advances, so too does our ability to protect the most valuable asset of the digital age: information itself.