
Phishing scams represent one of the most pervasive and insidious cyber threats in the modern digital landscape. Far from being a simple trick, phishing is a sophisticated form of social engineering often bolstered by continuously evolving technological tactics. At its core, a phishing scam involves attackers attempting to deceive individuals into divulging sensitive information—such as usernames, passwords, credit card numbers, or other personal data—by masquerading as a trustworthy entity in an electronic communication. These entities typically include reputable organizations like banks, government agencies, e-commerce sites, or even colleagues and superiors within an organization. The innovation in phishing lies in its adaptability and the ingenious ways attackers leverage human psychology and technological vulnerabilities to achieve their illicit goals.
The Evolving Landscape of Digital Deception
The digital realm has brought forth unprecedented connectivity and efficiency, but with it, a new frontier for illicit activities. Phishing, in particular, exploits the trust embedded in digital communications, making it a critical area of focus for cybersecurity innovation. Understanding its mechanics requires a look into both the human and technological facets.
Social Engineering’s Digital Frontier
The foundation of most phishing scams is social engineering—the psychological manipulation of people into performing actions or divulging confidential information. In a digital context, this often means creating a sense of urgency, fear, curiosity, or desire to bypass critical thinking. Attackers innovate constantly, studying human behavior and current events to craft believable narratives. For instance, during tax season, phishing attempts often mimic tax authorities; during global health crises, they might impersonate health organizations; and during major sporting events, they could offer fraudulent merchandise or streaming links. The success of social engineering in phishing relies on the attacker’s ability to perfectly replicate the visual and linguistic cues of a legitimate entity, down to logos, fonts, and specific jargon, making the victim less likely to question the authenticity.
Technical Vectors of Attack
While social engineering is the art, technology provides the canvas. Phishing attacks primarily leverage email, but their reach has expanded significantly. The technical vectors include:
- Email Spoofing: Attackers manipulate email headers to make it appear as though the message originated from a legitimate source, often by mimicking sender addresses or displaying friendly names that hide the true sender.
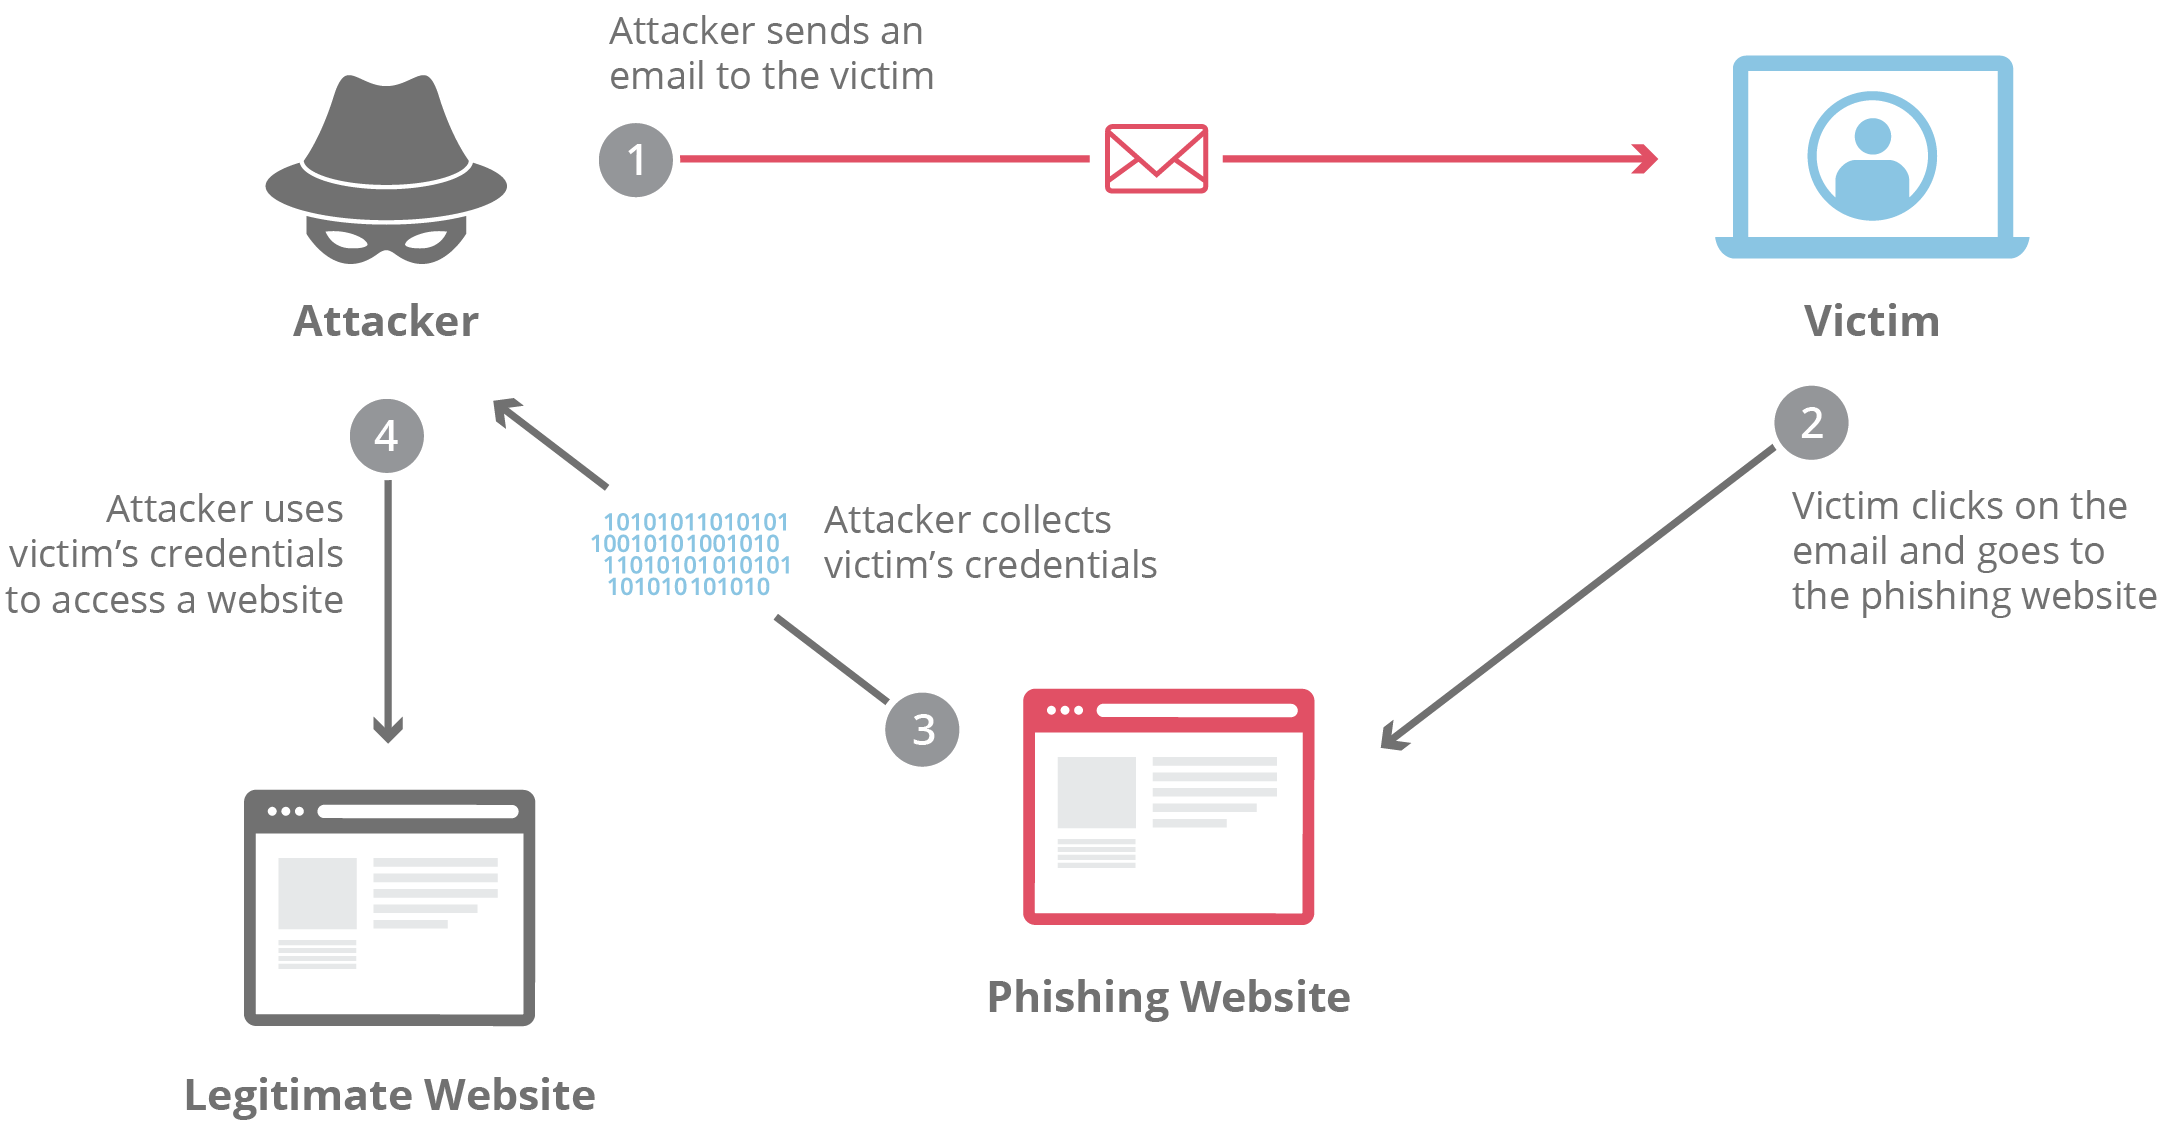
- Malicious Links (URL Redirection): The most common technique involves embedding malicious hyperlinks in emails. These links appear to point to legitimate websites but actually redirect users to fraudulent sites designed to capture credentials or install malware. Innovations here include subtle misspellings in domain names (typosquatting) or using URL shortening services to obscure the true destination.
- Malicious Attachments: Emails may contain attachments (e.g., seemingly innocent PDFs, Word documents, or spreadsheets) embedded with malware. When opened, these files execute malicious code that can compromise the user’s system, steal data, or provide remote access to the attacker.
- Web Form Manipulation: Fake login pages are meticulously crafted to resemble legitimate ones. When a user enters their credentials on such a page, the data is immediately sent to the attacker. These pages often feature identical branding and even seemingly functional elements to enhance their credibility.
Innovative Tactics in Phishing Campaigns
Phishing isn’t static; it continually evolves, adopting new technologies and refining its methodologies to bypass existing defenses. The innovation in attacker tactics means that defense strategies must also innovate continuously.
Spear Phishing and Whaling: Targeted Precision
Beyond broad, untargeted attacks, attackers employ highly sophisticated, personalized techniques:
- Spear Phishing: This is a highly targeted attack where the phisher researches their victim extensively, often using information gleaned from social media or corporate websites. The email or message is tailored to the individual, referencing their name, job title, company, and specific interests or projects. This personalization drastically increases the success rate, as the message appears highly relevant and credible.
- Whaling: An even more potent form of spear phishing, whaling targets high-value individuals within an organization, such as CEOs, CFOs, or other senior executives. These attacks are meticulously planned, often involving months of reconnaissance to understand the target’s role, their contacts, and common communication patterns. The goal is typically to authorize large financial transactions or release highly sensitive corporate data. The “innovation” here is in the extreme dedication to reconnaissance and the psychological manipulation of high-level decision-makers.

Smishing and Vishing: Expanding Beyond Email
Phishing has broadened its scope beyond traditional email:
- Smishing (SMS Phishing): Attackers send fraudulent text messages (SMS) to trick recipients. These messages often contain malicious links or phone numbers designed to elicit personal information. Common smishing scams include fake package delivery notifications, urgent bank alerts, or prize winnings that require immediate action.
- Vishing (Voice Phishing): This involves using voice communication (telephone calls) to impersonate legitimate entities. Vishing calls can be highly sophisticated, employing caller ID spoofing to display a legitimate company’s name or number. Attackers might use pre-recorded messages or even live agents who are skilled in social engineering to convince victims to reveal information or perform actions like transferring money. The rise of VoIP technology and readily available tools for voice manipulation contributes to the increasing sophistication of vishing attacks.
AI-Driven Deepfakes and Voice Mimicry
The cutting edge of phishing innovation is the integration of artificial intelligence and machine learning. Deepfake technology, which uses AI to create highly realistic synthetic media, poses a significant threat. Attackers can now generate convincing video or audio of individuals saying or doing things they never did. This could be used in vishing to mimic a CEO’s voice authorizing a wire transfer or in highly personalized spear phishing to create a “video message” from a trusted contact. While still emerging for mass phishing, the potential for AI-driven mimicry to create hyper-realistic and deceptive communications represents a profound leap in attacker capabilities, making it increasingly difficult for individuals to discern truth from sophisticated fabrication.
Technological Countermeasures and Future Innovation
Combating the ever-evolving threat of phishing requires continuous innovation in defensive technologies. Cybersecurity researchers and developers are constantly working on new methods to detect, prevent, and mitigate phishing attacks.
Advanced Email Filters and AI Detection
Traditional spam filters have evolved into highly sophisticated systems that utilize machine learning and artificial intelligence to analyze email content, headers, sender reputation, and embedded links. These systems can identify suspicious patterns, linguistic anomalies, and known phishing indicators with remarkable accuracy, quarantining or flagging malicious emails before they reach the user’s inbox. Behavioral analytics, which monitors user interaction patterns and flags unusual activity, also plays a crucial role in post-delivery detection. Future innovations will likely involve more dynamic, real-time analysis of potential threats, including the ability to rapidly identify and adapt to new phishing templates and deepfake indicators.
Multi-Factor Authentication (MFA) and Biometrics
One of the most effective technological countermeasures against credential-harvesting phishing is Multi-Factor Authentication (MFA). By requiring more than one form of verification (e.g., something you know like a password, something you have like a phone or hardware token, and something you are like a fingerprint), MFA significantly reduces the impact of a compromised password. Even if an attacker successfully phishes a password, they typically cannot log in without the second factor. Biometric authentication (fingerprints, facial recognition, iris scans) further strengthens MFA by making the “something you are” factor virtually impossible to phish or replicate. Continued innovation in user-friendly and secure MFA solutions remains a priority in cybersecurity.
Blockchain and Decentralized Identity Solutions
Emerging technologies like blockchain hold promise for future anti-phishing innovations, particularly in the realm of identity and verification. Decentralized identity systems, which leverage blockchain to give individuals more control over their digital identities, could make it much harder for attackers to spoof legitimate entities. By providing verifiable, tamper-proof credentials and digital signatures, these systems could enable users to definitively confirm the authenticity of a sender or website, fundamentally disrupting many traditional phishing vectors. While still in early stages of adoption for broad cybersecurity applications, this represents a significant area of technological innovation for future defense.
User Education: The Human Firewall in a Tech World
Despite the marvels of technological defense, the human element remains the strongest, and often the weakest, link in the security chain. No amount of technological innovation can fully protect against a determined social engineer if the end-user is uninformed. Regular, engaging, and updated cybersecurity awareness training is paramount. This training should not only educate users on how to identify phishing attempts but also instill a culture of skepticism towards unsolicited communications, encourage verification of suspicious requests through alternative, trusted channels, and promote the consistent use of security best practices, such as strong, unique passwords and MFA. In the ongoing arms race against phishing, the synergy between advanced technology and an informed user base is the ultimate defense.