
The CAN-SPAM Act stands as a critical piece of legislation governing commercial email in the United States, designed to protect consumers from unwanted and deceptive unsolicited messages while still permitting businesses to engage in legitimate electronic marketing. Enacted in 2003, this federal law sets forth requirements for commercial messages, gives recipients the right to have businesses stop emailing them, and spells out tough penalties for violations. For any entity operating in the digital sphere, from burgeoning startups to established corporations, understanding and adhering to the CAN-SPAM Act is not merely a legal obligation but a cornerstone of responsible digital communication and a commitment to consumer trust. In an era defined by rapid technological advancements and innovative marketing methodologies, navigating these regulations is paramount to sustainable growth and ethical practice within the tech and innovation landscape.
The Genesis and Purpose of CAN-SPAM
Before the CAN-SPAM Act, the burgeoning internet age was plagued by an escalating volume of unsolicited commercial email, colloquially known as spam. This torrent of unwanted messages not only clogged inboxes but also became a significant vector for fraud, scams, and deceptive practices. Consumers felt overwhelmed and powerless, while legitimate businesses struggled to differentiate their marketing efforts from the deluge of illegitimate spam. The lack of a unified federal standard meant a patchwork of state laws, creating confusion and inconsistent enforcement.
Curbing Unsolicited Commercial Email
The primary impetus behind the CAN-SPAM Act was to bring order to this chaotic digital frontier. Its full title, “Controlling the Assault of Non-Solicited Pornography And Marketing Act,” highlights its dual focus: tackling both explicit content and broader commercial solicitations. The Act doesn’t outright ban all unsolicited commercial email, a common misconception. Instead, it establishes a comprehensive set of rules for legitimate commercial email, distinguishing it from illegal, fraudulent, or abusive spam. By imposing clear requirements on sender identity, content, and opt-out mechanisms, the Act aimed to create a more transparent and trustworthy email ecosystem, fostering an environment where innovation in digital marketing could thrive without succumbing to unchecked abuse.
Empowering Consumers with Control
A cornerstone of the CAN-SPAM Act is the empowerment of consumers. Before its enactment, recipients often had no recourse to stop receiving unwanted emails. The Act fundamentally shifted this dynamic by mandating that every commercial email must provide a clear and conspicuous mechanism for recipients to opt out of future mailings. This right to say “no” is central to the Act’s purpose, giving individuals control over their inboxes and helping them manage their digital footprint. For businesses, this translates into a direct responsibility to respect consumer preferences, thereby building stronger, trust-based relationships that are vital for long-term engagement in the digital economy.
Core Requirements for Compliance
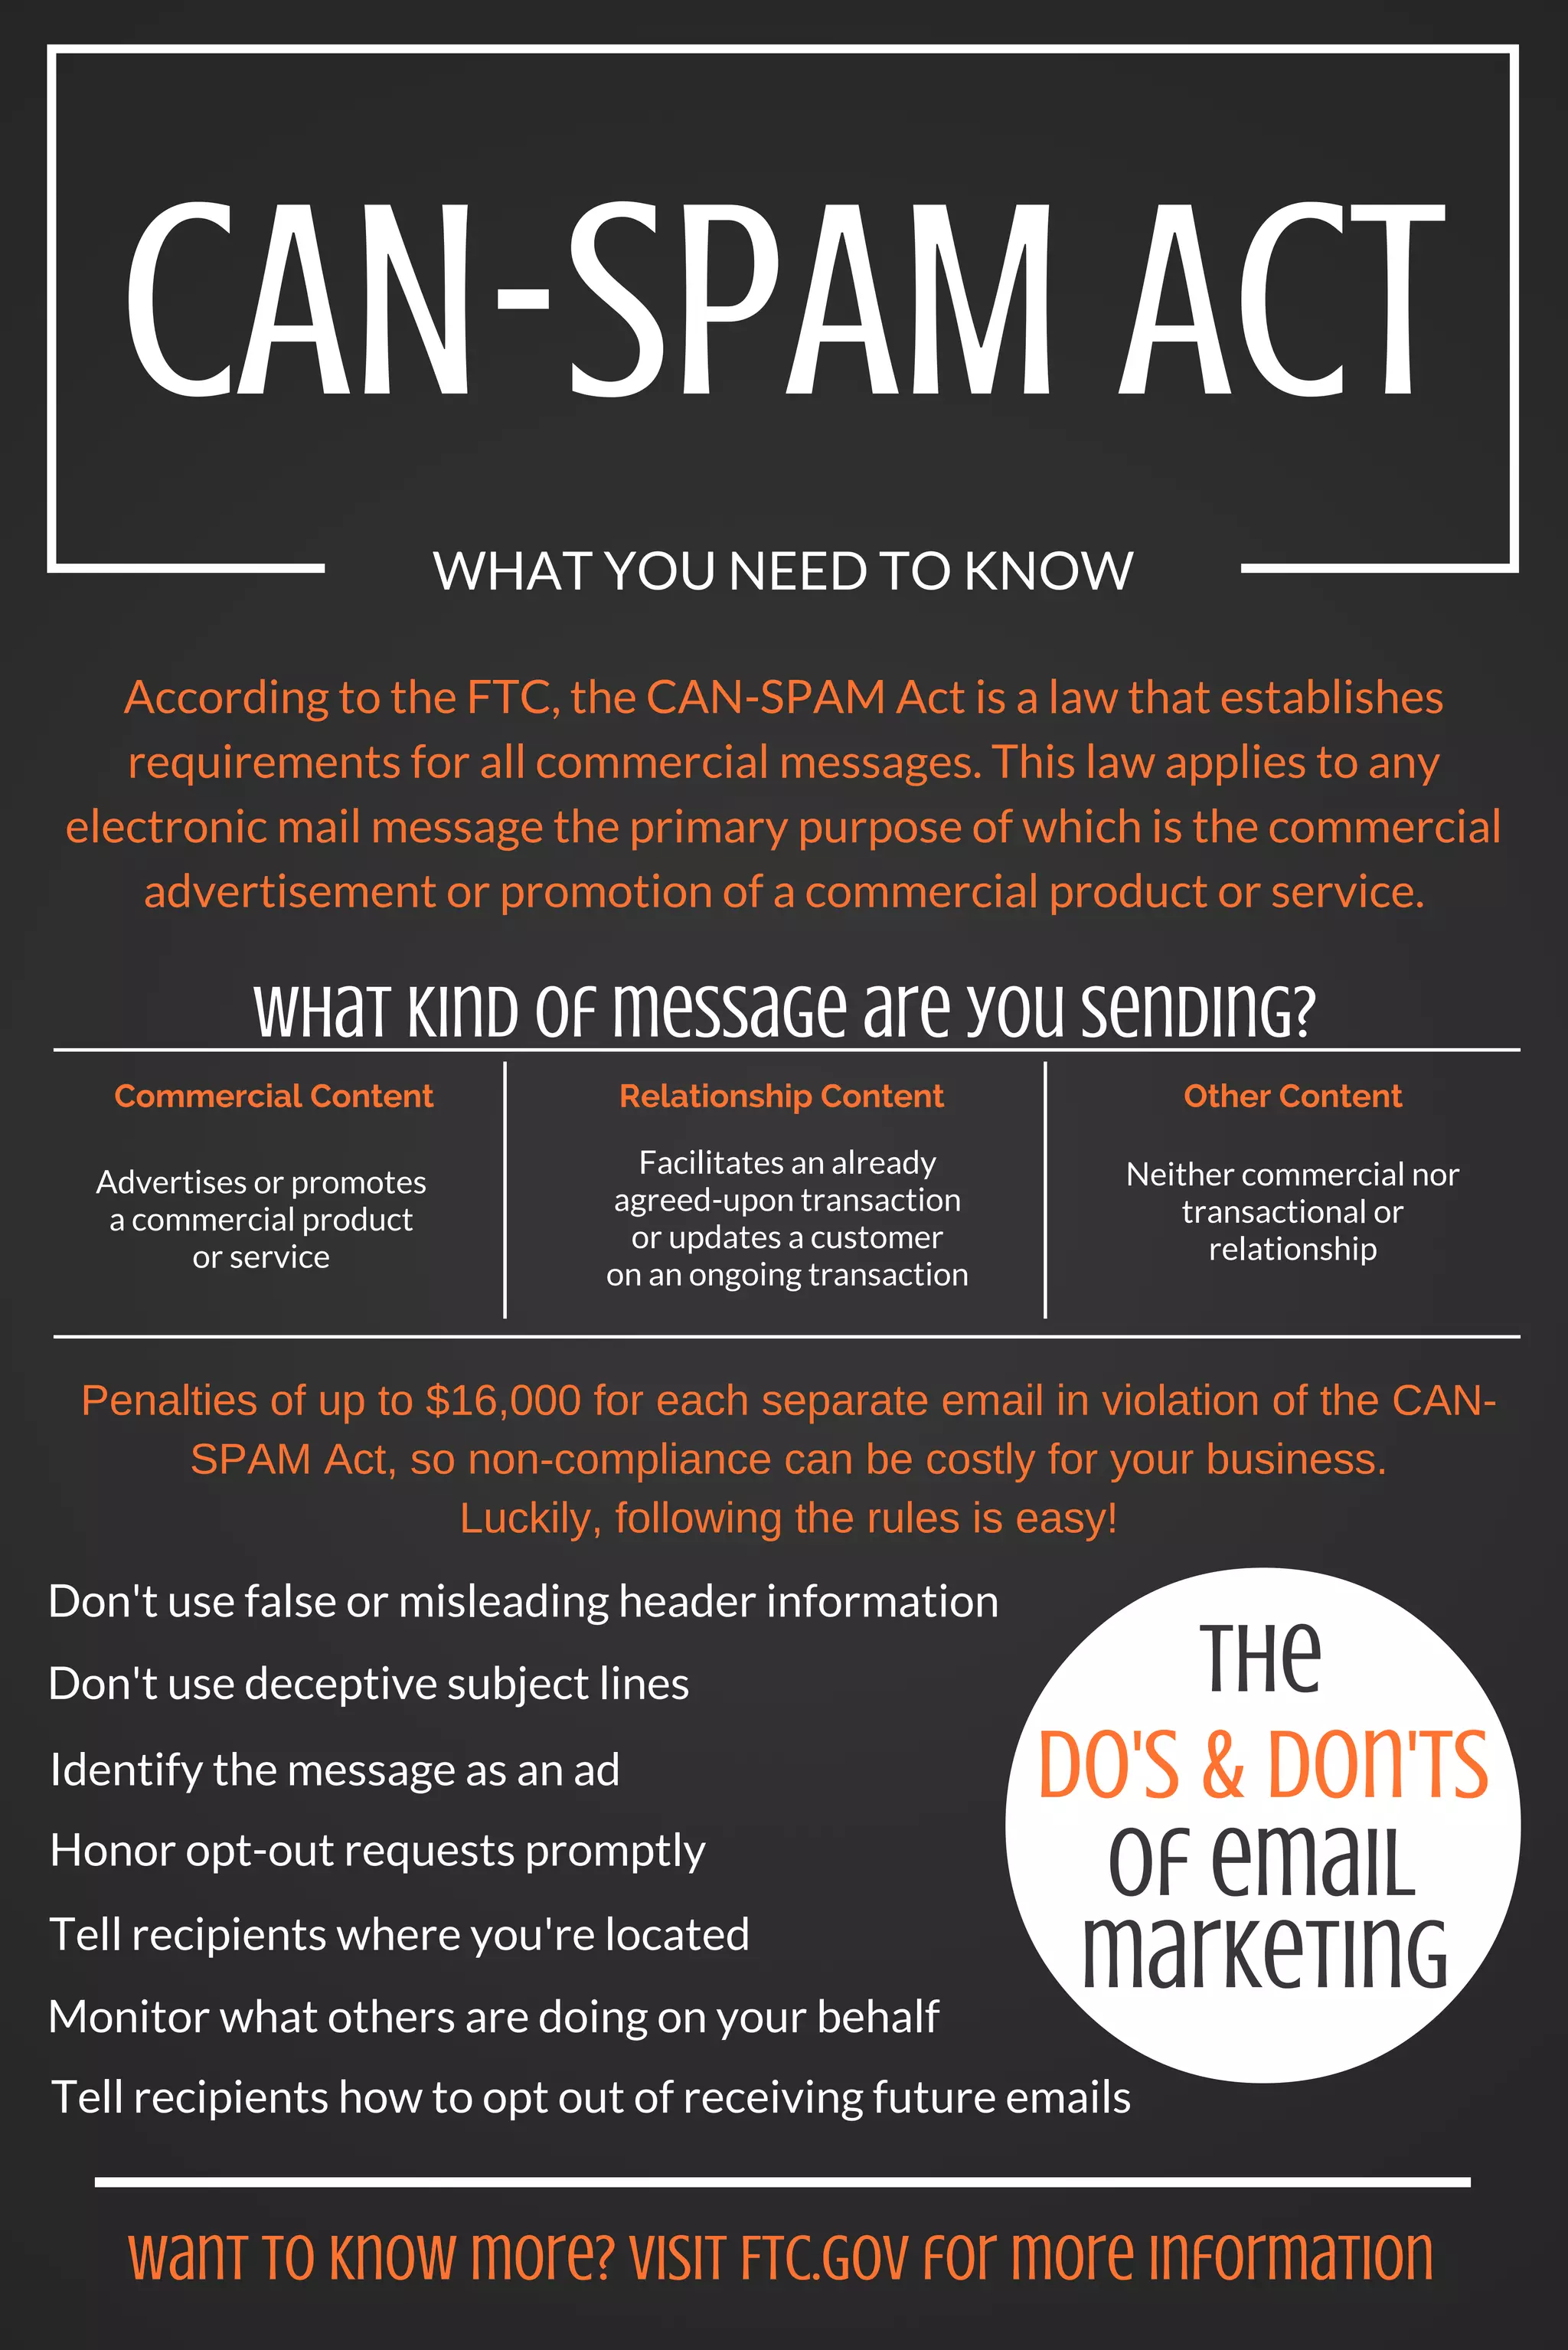
Adherence to the CAN-SPAM Act involves several key requirements that apply to nearly all commercial emails. A “commercial email message” is defined broadly as “any electronic mail message the primary purpose of which is the commercial advertisement or promotion of a commercial product or service.” This broad definition covers even transactional or relationship messages if they include promotional content. Understanding these mandates is crucial for any organization leveraging email for outreach, product promotion, or customer engagement.
Prohibition Against False or Misleading Headers
The Act strictly prohibits using false or misleading header information. This means that the “From,” “To,” “Reply-To,” and routing information—including the originating domain name and email address—must be accurate and genuinely identify the person or business initiating the message. Deceptive practices, such as spoofing email addresses or misrepresenting the sender, are direct violations and carry severe penalties. Transparency in sender identification is fundamental to building trust and enabling consumers to identify the source of communication effectively.
No Deceptive Subject Lines
Subject lines must accurately reflect the content of the message. Using misleading or deceptive subject lines to entice recipients to open emails is a clear violation. For instance, a subject line promising “Your order has shipped!” when the email is actually a product promotion would be non-compliant. The subject line should provide a truthful preview of the email’s primary purpose, ensuring that recipients are not tricked into engaging with content they might otherwise disregard.
Disclosure of Commercial Intent
Every commercial email must clearly and conspicuously disclose that it is an advertisement or solicitation. This doesn’t necessarily mean placing “ADVERTISEMENT” in the subject line of every email, but the commercial nature of the message must be readily apparent to the recipient. This requirement aims to prevent covert marketing, ensuring that consumers are aware when they are being pitched a product or service.
Valid Physical Postal Address
All commercial emails must include a valid physical postal address of the sender. This can be the sender’s current street address, a post office box registered with the U.S. Postal Service, or a private mailbox registered with a commercial mail receiving agency. This requirement provides a tangible point of contact for recipients and serves as another layer of transparency and accountability for senders.
Clear and Conspicuous Opt-Out Mechanism
Perhaps one of the most significant requirements, every commercial email must provide a clear and conspicuous way for recipients to opt out of receiving future emails from the sender. This opt-out mechanism must be easy for an ordinary person to recognize, read, and use. Typically, this takes the form of an “unsubscribe” link prominently displayed in the email’s footer. The process should be straightforward, requiring no more than a few clicks or a single email reply, without additional steps like logging in or providing personal information beyond the email address itself.
Honoring Opt-Out Requests Promptly
Once a recipient has exercised their right to opt out, senders must honor that request promptly. The Act stipulates that opt-out requests must be processed within 10 business days. Furthermore, senders cannot charge a fee, require recipients to provide any information other than an email address, or make recipients take any step other than sending a reply email or visiting a single page on an Internet website as a condition to honoring an opt-out request. After an opt-out, the sender is prohibited from sending any further commercial emails to that address, or causing them to be sent, even through another party.
Enforcement and Penalties
The CAN-SPAM Act carries significant weight, with substantial penalties for non-compliance, reflecting the government’s commitment to maintaining a fair and lawful digital communication environment.
Who Enforces the Act?
The primary enforcer of the CAN-SPAM Act is the Federal Trade Commission (FTC), with assistance from the Department of Justice. State attorneys general also have the authority to bring enforcement actions against violations that affect their residents. Additionally, Internet Service Providers (ISPs) can sue senders who violate the Act, adding another layer of oversight. This multi-pronged enforcement approach ensures broad coverage and accountability across the digital landscape.
Consequences of Non-Compliance
Violations of the CAN-SPAM Act can lead to severe financial penalties. Each separate email in violation of the Act is subject to penalties of up to $50,120 (adjusted for inflation, the current figure can be found on the FTC website). Aggravated violations, such as using email harvesting, dictionary attacks, or automated creation of multiple email accounts, can result in increased fines and even criminal charges, including imprisonment. The financial repercussions alone are a powerful deterrent, underscoring the importance of rigorous compliance for any business leveraging email for commercial purposes.
Impact on Businesses and Reputation
Beyond legal and financial penalties, non-compliance with the CAN-SPAM Act can severely damage a business’s reputation. Being flagged for spam or having a high complaint rate can lead to email service providers (ESPs) blocking or throttling a sender’s messages, drastically reducing email deliverability. This not only cripples marketing efforts but also signals to customers and partners a disregard for ethical digital practices. In a highly interconnected and trust-driven digital economy, a tarnished reputation can have long-lasting negative effects on customer acquisition, brand loyalty, and overall market standing, impacting even the most innovative tech companies.
Navigating CAN-SPAM in the Digital Age of Innovation
For tech companies and innovators, the CAN-SPAM Act isn’t a relic of the past but a foundational element of the regulatory framework that shapes modern digital communication. As new technologies emerge and marketing strategies evolve, understanding and integrating CAN-SPAM compliance remains critical.
Adapting Marketing Strategies
The Act influences how businesses design and execute their email marketing campaigns. It necessitates a focus on permission-based marketing, where consent is explicitly or implicitly obtained before sending commercial emails. This encourages businesses to build genuine relationships with their audience, providing value and respecting preferences rather than resorting to mass, unsolicited outreach. For tech and innovation companies, this means investing in robust customer relationship management (CRM) systems, developing engaging content strategies that encourage opt-ins, and maintaining clean, segment-specific email lists. This approach not only ensures compliance but also leads to higher engagement rates and better return on investment (ROI) from email marketing efforts.
The Role of AI and Automation
As artificial intelligence and marketing automation become more sophisticated, they present both opportunities and challenges for CAN-SPAM compliance. AI-driven personalization can enhance relevance, leading to more engaged recipients who are less likely to perceive messages as unwanted. However, automated email sequences and large-scale outreach powered by AI must still strictly adhere to all CAN-SPAM requirements. Developers of AI tools for marketing must ensure their algorithms incorporate compliance checks, such as verifying opt-in status, respecting opt-out preferences, and ensuring accurate header and subject line generation. The innovation in automation must be paired with an unwavering commitment to legal and ethical standards.
Future Implications for Digital Communication
The principles enshrined in the CAN-SPAM Act continue to influence the development of digital communication regulations globally. It serves as a precedent for data privacy laws like GDPR and CCPA, which often include similar consent and opt-out provisions for electronic communications. For companies pushing the boundaries of technology, such as those developing new communication platforms or innovative methods of engagement, the spirit of CAN-SPAM—transparency, consumer control, and ethical conduct—remains a vital guiding principle. Adhering to these tenets fosters a more trustworthy digital ecosystem, which is essential for innovation to flourish responsibly and sustainably. As technology continues to reshape how we interact, the core principles of the CAN-SPAM Act will likely remain relevant, adapting to new forms of digital advertising while continuing to protect consumers and uphold legitimate commerce.