
In the intricate world of Tech & Innovation, where the seamless operation of autonomous systems, the precision of remote sensing, and the intelligence of AI algorithms dictate progress, the concept of a secure and reliable communication channel is not merely a convenience—it is a foundational necessity. At the heart of this secure connectivity often lies SSH, or Secure Shell, and its associated port. Understanding “what is SSH port” is paramount for anyone involved in developing, deploying, or managing advanced technological solutions, from drone fleets performing autonomous inspections to sophisticated remote sensing platforms collecting critical environmental data.
The Foundation of Secure Remote Access in Tech & Innovation
SSH is more than just a means to log into a remote computer; it’s a cryptographic network protocol that enables secure data communication between two networked devices. It provides a secure channel over an unsecured network by using strong encryption. This capability is indispensable in domains like autonomous flight, AI-driven systems, and remote sensing, where data integrity, system uptime, and security are non-negotiable.
Demystifying SSH: Protocol and Port
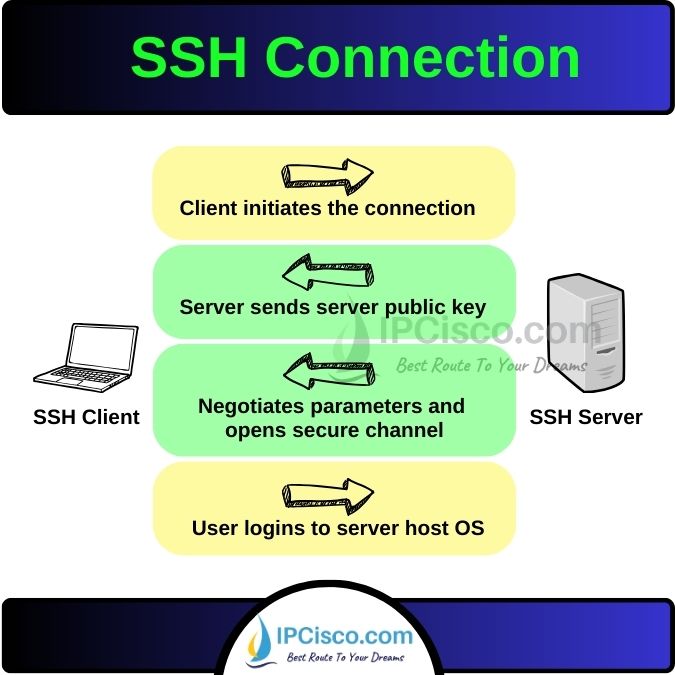
At its core, SSH operates as a client-server model. An SSH client initiates a connection to an SSH server, and once authenticated, a secure, encrypted tunnel is established. This tunnel allows for various services to be securely communicated over a network, including remote command-line execution, remote file transfer (SCP/SFTP), and even tunneling arbitrary network ports.
The “port” aspect of SSH refers to the network port number through which the SSH service listens for incoming connections. By default, the standard port for SSH is TCP port 22. This is a well-known port, universally recognized for SSH services. While this default is convenient, for enhanced security in critical innovation deployments, administrators often configure SSH servers to listen on a non-standard port. This practice, known as “port knocking” or “security by obscurity,” aims to deter automated scanning attempts by malicious actors who typically target port 22. In the context of drone ground control stations, remote AI inference servers, or data collection units in the field, this simple configuration change can significantly bolster defense against unauthorized access.
Beyond Basic Login: A Toolkit for Innovation
SSH’s utility extends far beyond just logging into a remote server. For tech innovators, it serves as a versatile toolkit:
- Secure File Transfers: Using SCP (Secure Copy Protocol) or SFTP (SSH File Transfer Protocol), developers can securely upload new firmware to drone flight controllers, download log files from autonomous vehicles for post-mission analysis, or transfer large datasets from remote sensing platforms to central processing units. This ensures that sensitive operational data or proprietary AI models remain confidential during transit.
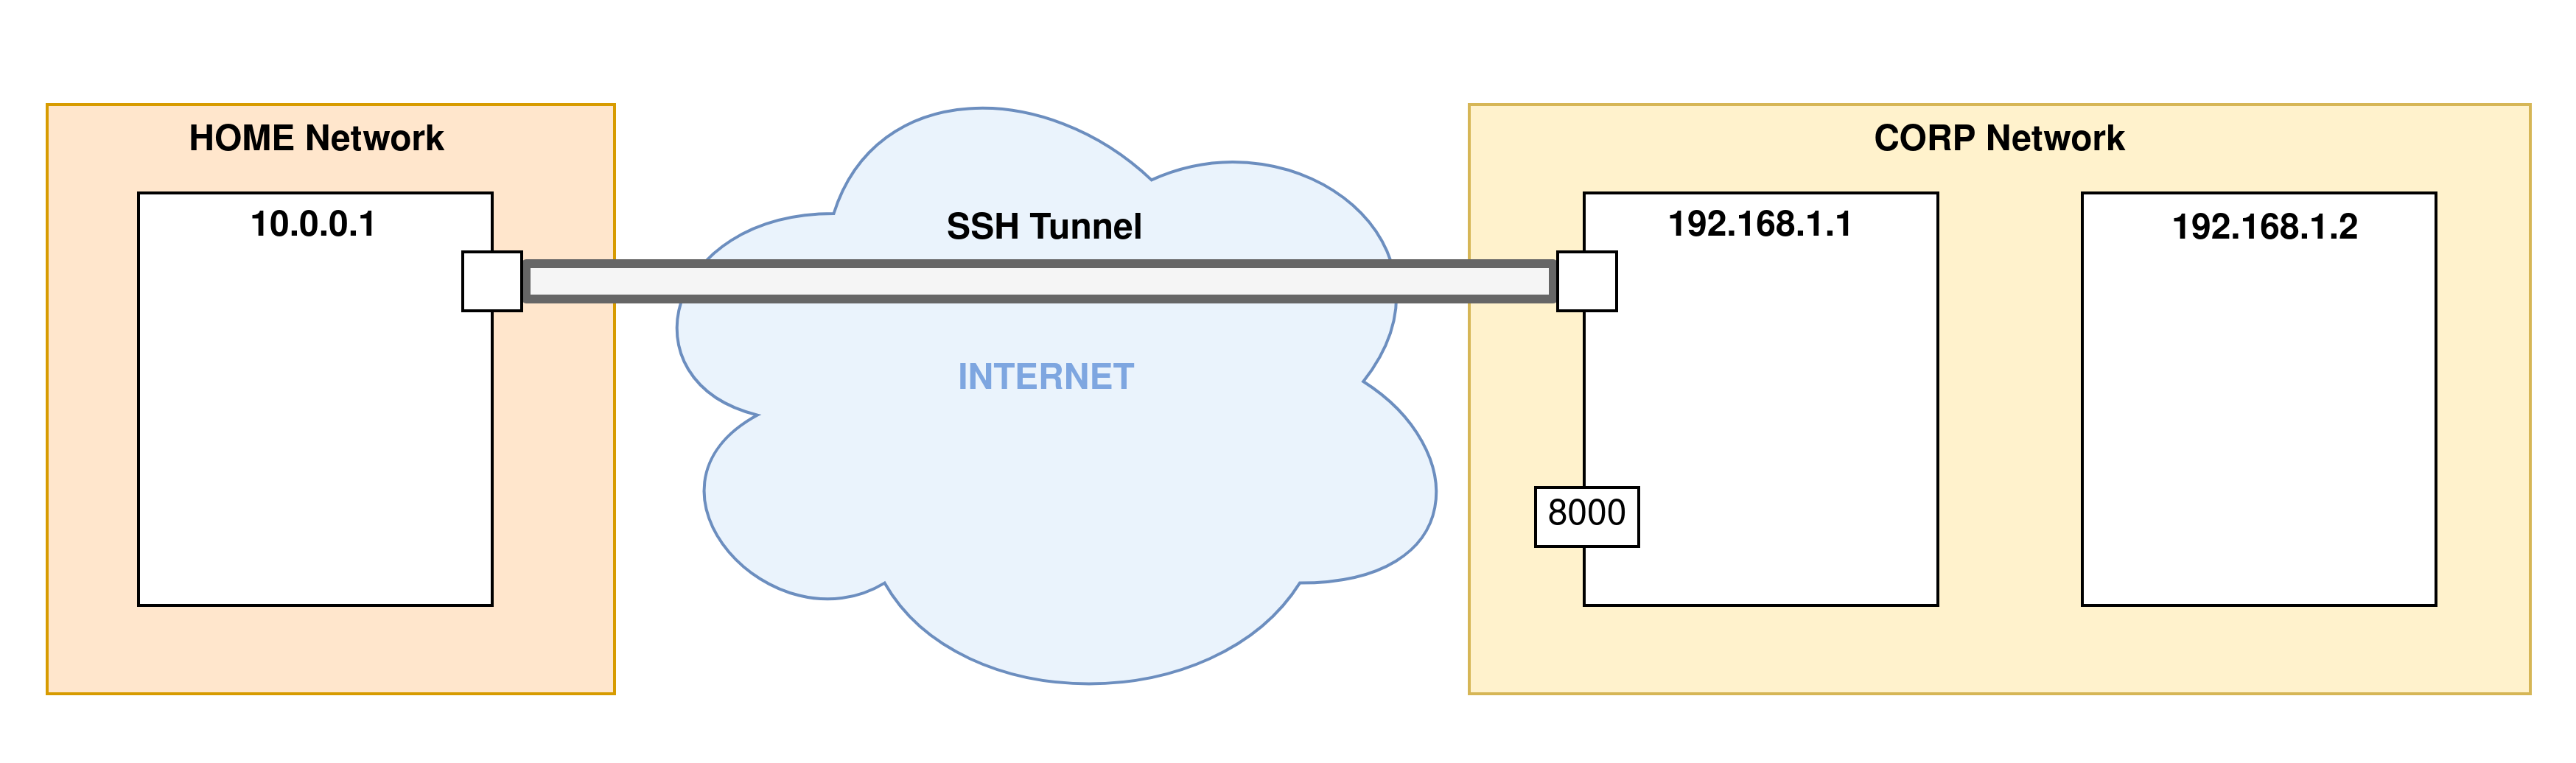
- Port Forwarding (Tunneling): SSH can create encrypted tunnels to forward network traffic. This is incredibly useful for accessing internal services (e.g., a web interface for a drone’s onboard computer or a database on a remote sensing station) that are not directly exposed to the internet. It allows secure communication with resources deep within a network from a remote location, a critical feature for managing distributed autonomous systems.
- Automated Scripting: SSH can be integrated into scripts for automating tasks. Imagine automatically deploying a new AI model update to a fleet of edge devices or scheduling regular data backups from mapping drones. SSH keys (public-private key pairs) enable passwordless authentication, making automation both secure and seamless, reducing manual intervention and potential human error in complex tech deployments.
SSH and the Autonomous Flight Revolution
The development and deployment of autonomous flight systems, from delivery drones to sophisticated surveillance UAVs, fundamentally rely on robust, secure communication. SSH plays a critical role in enabling the full lifecycle of these intelligent aerial platforms.
Remote Management of Onboard Systems
Autonomous drones are essentially flying computers, equipped with flight controllers, mission computers, and various sensors. These systems require constant monitoring, configuration, and sometimes, intervention. SSH provides the secure conduit for engineers and operators to access these onboard systems remotely. Whether it’s to adjust PID tuning parameters on a flight controller, check the status of a navigation sensor, or restart a unresponsive software module, SSH ensures that these interactions are encrypted and authenticated, preventing unauthorized access that could compromise flight safety or mission integrity.
Secure Software Deployment and Updates
The continuous improvement of autonomous flight capabilities often necessitates frequent software updates and model deployments. New navigation algorithms, enhanced obstacle avoidance logic, or updated AI models for object recognition must be securely transmitted to and installed on the drone’s computational units. SSH, through its secure file transfer capabilities (SCP/SFTP) and secure command execution, allows for the reliable and confidential deployment of these updates. This minimizes the risk of tampering or data leaks during the crucial upgrade process, which is vital for maintaining the operational security and performance of a drone fleet.
Real-time Diagnostics and Troubleshooting
When an autonomous drone encounters an anomaly or performs unexpectedly, rapid diagnostics are essential. SSH enables engineers to securely connect to the drone’s logging systems and retrieve real-time data or historical logs. This remote access facilitates quick identification of issues, from software bugs to hardware malfunctions, without physically recalling the drone. In scenarios where drones operate in remote or hazardous environments, this capability is not just convenient but absolutely critical for ensuring continuous operation and minimizing downtime.
Powering Mapping and Remote Sensing Operations
Mapping and remote sensing operations generate vast amounts of valuable data, often from geographically dispersed and sometimes challenging locations. SSH is instrumental in ensuring this data is securely collected, transferred, and processed, forming the backbone of reliable information pipelines.
Safeguarding Data Transfer from Field to Cloud

Mapping drones equipped with high-resolution cameras, LiDAR, or multispectral sensors collect gigabytes, if not terabytes, of data during a single mission. This raw data, often containing sensitive geographical information or critical environmental metrics, needs to be securely transferred from the drone or its ground station to cloud storage or centralized processing servers. Using SCP or SFTP over SSH provides an encrypted tunnel for this transfer, protecting the data from interception and ensuring its integrity. This is particularly important when dealing with proprietary mapping data or intelligence collected for critical infrastructure monitoring or environmental surveillance.
Remote Control of Data Processing Workflows
Beyond data transfer, SSH allows for the secure initiation and monitoring of data processing workflows on remote servers. For example, once raw imagery from a remote sensing mission is uploaded, an engineer can use SSH to securely log into a powerful cloud instance and trigger photogrammetry processing, LiDAR point cloud generation, or AI-driven feature extraction. This enables remote teams to manage complex computational tasks efficiently, scaling resources as needed without physical access to the computing infrastructure.
Interfacing with Specialized Sensors
Many remote sensing platforms employ specialized sensors that may have their own embedded Linux systems or require specific commands for configuration and data retrieval. SSH provides a universal, secure method to interact with these devices, regardless of their location. This allows for remote calibration, firmware updates for sensors, or direct data extraction, ensuring that the sensing equipment is always performing optimally and collecting accurate information.
SSH in the Age of AI and Edge Computing
The proliferation of AI and the move towards edge computing—where data is processed closer to its source, often on the drone itself or its immediate ground station—further elevates the importance of SSH for secure and efficient operations.
Secure Model Deployment to Edge Devices
AI models for tasks like real-time object detection, anomaly identification, or autonomous navigation are increasingly deployed directly onto edge devices, such as drone onboard computers or specialized ground units. These models are often proprietary and represent significant intellectual property. SSH offers the secure channel required to transmit these trained AI models from development servers to the edge devices. This ensures that the model files are not intercepted or tampered with during deployment, preserving the integrity and performance of the AI-powered functionalities.
Enabling Distributed AI Architectures
Modern AI applications in tech innovation often involve distributed architectures, where different parts of an AI pipeline run on various machines—some on the edge, some in a local server, and others in the cloud. SSH facilitates secure communication between these distributed components. For instance, an edge device might use SSH to securely send inference results to a central server for aggregation or further analysis, or a central server might use SSH to remotely update the training data used by a federated learning system on multiple edge nodes.
Auditing and Compliance for Autonomous Systems
The operation of autonomous systems, especially in sensitive applications, often comes with stringent auditing and compliance requirements. Every interaction, every software change, and every data transfer needs to be traceable and secure. SSH, with its robust authentication and encryption, provides a verifiable record of access and activity. By properly configuring SSH logging and integrating it with security information and event management (SIEM) systems, organizations can ensure that their autonomous and AI-driven operations meet regulatory standards and maintain a high level of accountability.
Best Practices for SSH Security in Tech Operations
Given SSH’s critical role in securing cutting-edge tech operations, implementing best practices for its usage is non-negotiable.
Strong Authentication Methods
Relying solely on passwords for SSH authentication, especially on default port 22, is a significant security risk. Implementing public-key authentication (using SSH keys) is a far superior method. SSH keys are cryptographically strong and negate the need for passwords, making brute-force attacks significantly harder. Additionally, protecting private keys with strong passphrases and ensuring proper key management is crucial. For highly sensitive systems, multi-factor authentication (MFA) should be employed alongside SSH keys to provide an extra layer of security.
Principle of Least Privilege
Granting users only the necessary permissions to perform their tasks is a fundamental security principle. This applies equally to SSH access. Instead of giving root access by default, configure SSH to allow access to specific user accounts with limited privileges. Additionally, leverage SSH configuration options to restrict certain users to specific commands or to chroot jails, confining them to a particular directory to prevent system-wide access.
Regular Audits and Patching
Like any software, SSH implementations can have vulnerabilities. It is imperative to regularly update SSH clients and servers to the latest versions to patch any known security flaws. Furthermore, conduct regular security audits of SSH configurations, review access logs for suspicious activity, and rotate SSH keys periodically. Proactive security management ensures that the secure backbone provided by SSH remains resilient against evolving cyber threats, safeguarding the continuous innovation and reliable operation of advanced technological systems.