
The Foundational Layer: Understanding lsass.exe in a Tech & Innovation Ecosystem
In the expansive and rapidly evolving landscape of Tech & Innovation, particularly in areas like autonomous flight, advanced mapping, and remote sensing, the underlying computing infrastructure forms the bedrock upon which all advanced capabilities are built. While the focus often naturally gravitates towards groundbreaking algorithms, sophisticated sensor arrays, or next-generation propulsion systems, the security and integrity of the operating systems managing these innovations are equally paramount. Within the Windows operating system, one critical process that exemplifies this foundational importance is lsass.exe.
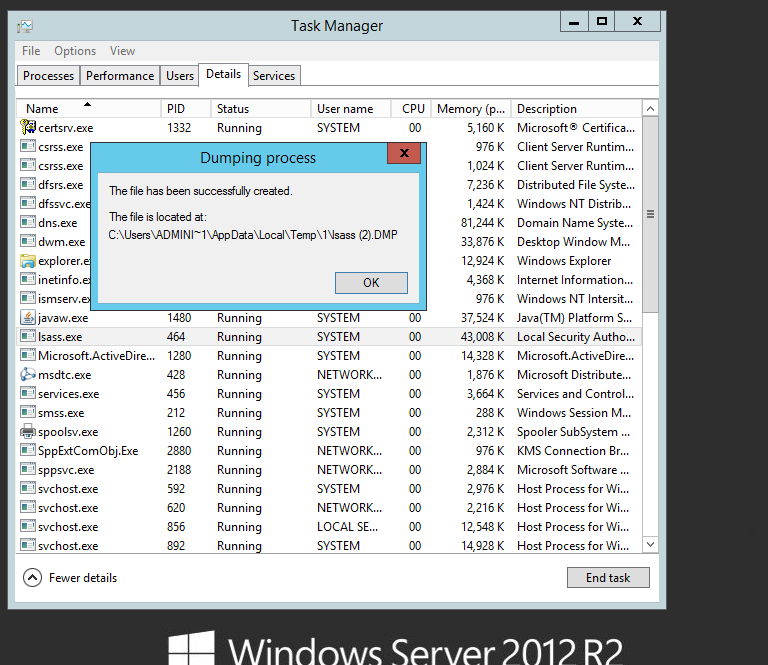
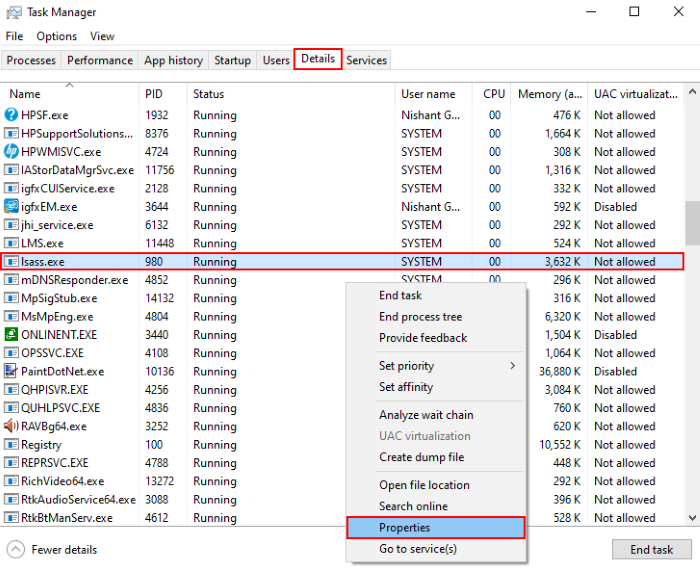
The name lsass.exe stands for Local Security Authority Subsystem Service. When you open Task Manager, this process is listed precisely as lsass.exe under the “Processes” tab (or “Details” tab in newer Windows versions). It’s not typically given a more user-friendly name, which sometimes leads to confusion or concern for those unfamiliar with its crucial role. Far from being a mere background operation, lsass.exe is a core component responsible for enforcing the security policy on the system. This includes managing user logins, password changes, and creating access tokens. Essentially, it verifies user credentials to allow access to local and remote resources, a fundamental function without which modern computing environments, and thus the innovative applications built upon them, could not operate securely.
The continuous innovation in areas like AI follow mode for drones, complex data processing for remote sensing, or sophisticated navigation algorithms for autonomous flight often relies on powerful computing platforms – whether they are ground control stations, cloud-based data analysis servers, or even the embedded systems performing specific security checks. Each of these platforms requires robust authentication and authorization mechanisms to protect sensitive data, prevent unauthorized access to control systems, and ensure the integrity of operational commands. lsass.exe is the Windows operating system’s primary actor in maintaining this crucial security posture, making its secure and stable operation intrinsically linked to the reliability and trustworthiness of any cutting-edge tech deployment.
The Role of Authentication and Authorization in Advanced Systems
The concept of authentication and authorization is not confined to human users logging into a computer. In an interconnected Tech & Innovation ecosystem, it extends to services, applications, and even hardware components verifying their identities and permissions. For example, a drone performing an autonomous mission might be uploading critical mapping data to a secure server. The server needs to authenticate that the data originates from an authorized drone and that the drone has the necessary permissions to write to a specific directory. While lsass.exe primarily handles local Windows security, its principles and the security mechanisms it enforces are representative of the rigorous security models required across the entire innovation stack. A compromised lsass.exe on a ground control station, for instance, could lead to credential theft, allowing an adversary to gain administrative access to the system, potentially disrupting operations, tampering with flight plans, or exfiltrating valuable intellectual property related to drone technology. Thus, understanding and safeguarding such critical OS processes is a non-negotiable aspect of responsible innovation.
lsass.exe and System Integrity: Enabling Reliable Autonomous Flight and Mapping
The pursuit of innovation in areas such as autonomous flight, precise mapping, and sophisticated remote sensing hinges significantly on the stability and integrity of the underlying computing systems. lsass.exe, as a protector of the local security authority, contributes directly to this system integrity. Any disruption or compromise of lsass.exe can severely impact the operating system’s ability to function securely, leading to instability, performance degradation, or even complete system failure – scenarios that are unacceptable in mission-critical drone operations.
For instance, consider a ground station running complex software for real-time drone control, telemetry analysis, or post-mission data processing for generating 3D maps. This software relies on the operating system to provide a stable, secure environment where processes can execute without interference and where data can be accessed and stored according to strict security policies. If lsass.exe were to suffer from a memory leak, consume excessive CPU, or be targeted by malware, the entire system’s performance and security could be jeopardized. This could manifest as lags in control input, errors in data processing, or, in the worst case, a system crash during a critical phase of an autonomous mission. The ripple effect could lead to financial losses, loss of valuable data, or even the physical loss of a drone.
The integrity lsass.exe upholds is therefore not just about abstract security; it directly translates into operational reliability. For developers pushing the boundaries of autonomous flight, where precision and predictability are paramount, ensuring that the control software runs on a stable and uncompromised operating system is a fundamental requirement. Similarly, in high-precision mapping and remote sensing applications, where data accuracy and confidentiality are crucial, the robust operation of lsass.exe safeguards the processing pipeline from potential integrity breaches or unauthorized access to sensitive geospatial information.
Protecting Sensitive Data and Intellectual Property
Innovations in drone technology often involve proprietary algorithms, confidential flight plans, and sensitive data captured through advanced sensors. The security policies enforced by lsass.exe are crucial for protecting this intellectual property and data. When a user or application attempts to access a file, directory, or network resource, lsass.exe is involved in verifying the access token associated with that request against the resource’s security descriptor. This ensures that only authorized entities can read, write, or modify critical data.
In the context of remote sensing, for example, high-resolution imagery or multispectral data might contain valuable commercial insights or even classified information. The integrity of the system processing and storing this data, upheld in part by processes like lsass.exe, is vital to prevent data exfiltration or tampering. Safeguarding these foundational OS processes thus becomes a direct contributor to maintaining a competitive edge and ensuring the ethical handling of sensitive information within the Tech & Innovation domain.
Identifying and Mitigating Risks Associated with lsass.exe
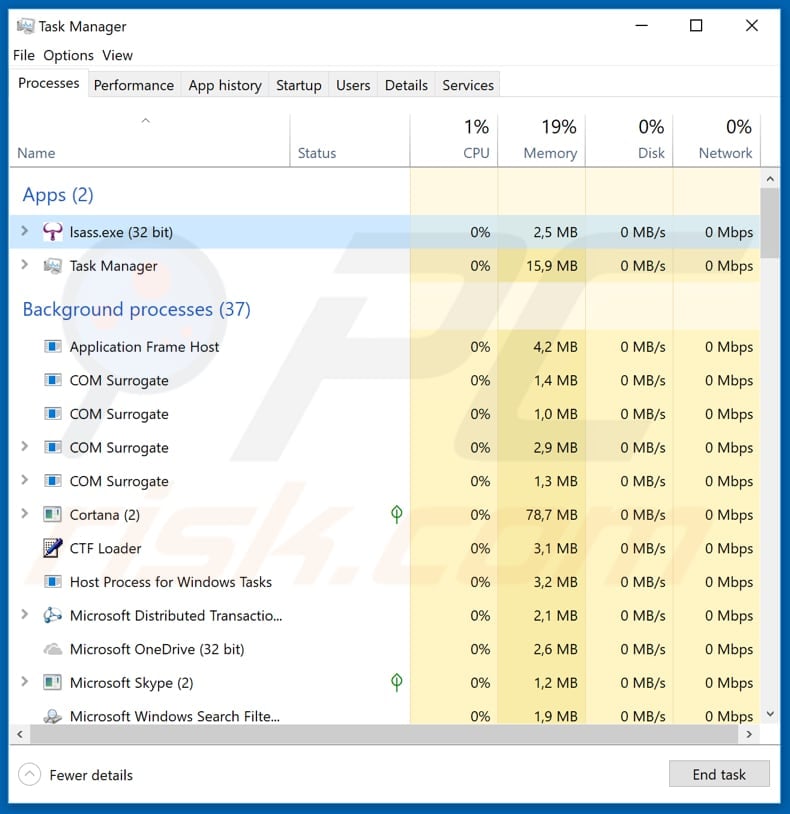
While lsass.exe is a legitimate and vital Windows process, its critical role in system security also makes it a prime target for malicious actors. Understanding how to identify normal versus anomalous behavior of lsass.exe in Task Manager is a crucial skill for anyone managing computing systems that support advanced Tech & Innovation, from R&D workstations to production ground control systems.
In Task Manager, lsass.exe should typically show relatively stable CPU and memory usage when the system is idle or performing routine tasks. Spikes in CPU usage for prolonged periods, unexpectedly high memory consumption, or unusual network activity associated with lsass.exe can be indicators of compromise. Malicious software, often known as “rootkits” or “credential stealers,” frequently attempts to inject code into lsass.exe or mimic its process to steal user credentials (e.g., “pass-the-hash” attacks) or escalate privileges. Since lsass.exe handles sensitive authentication data, a successful attack against it can provide an attacker with system-wide administrative access, enabling them to control the machine, deploy further malware, or access critical resources.
For organizations developing or deploying drone technology, such a compromise could have devastating effects. An attacker gaining control of a ground control station via a compromised lsass.exe could potentially:
- Alter flight plans or mission parameters: Leading to incorrect data collection, operational failures, or even dangerous flight incidents.
- Exfiltrate proprietary software and data: Stealing valuable algorithms for autonomous flight, design specifications for drone hardware, or sensitive client data gathered through remote sensing.
- Inject malicious code into drone firmware or software updates: Creating backdoors or vulnerabilities that could be exploited in future operations.
Best Practices for Secure Innovation Environments
To mitigate these risks and ensure the continued security of innovative drone solutions, several best practices are essential:
- Regular Security Updates: Keeping the operating system and all software patched and up-to-date is fundamental. Vulnerabilities in
lsass.exeor related components are often patched by Microsoft, and applying these updates promptly reduces the attack surface. - Robust Endpoint Security: Implementing advanced antivirus, anti-malware, and Endpoint Detection and Response (EDR) solutions can help detect and prevent attempts to compromise critical processes like
lsass.exe. These tools can often identify unusual process behavior, memory injection attempts, and suspicious network connections. - Principle of Least Privilege: Ensure that users and applications operate with the minimum necessary permissions. This limits the potential damage if an account or process is compromised, as the attacker would only gain access to a restricted set of resources.
- Regular Auditing and Monitoring: Continuously monitor system logs for suspicious activity, failed login attempts, or unusual process behavior related to
lsass.exe. Specialized security information and event management (SIEM) systems can centralize and analyze these logs, providing early warnings of potential breaches. - Network Segmentation: Isolate critical systems, such as those controlling drone operations or processing sensitive data, on segmented networks. This limits an attacker’s lateral movement even if one system is compromised.
By adhering to these security tenets, organizations can establish a robust foundation that protects their investments in Tech & Innovation, ensuring that the incredible advancements in autonomous flight, mapping, and remote sensing are built on secure and trustworthy infrastructure. The seemingly mundane process of lsass.exe thus becomes a crucial sentinel, guarding the gates to operational integrity and data confidentiality in the cutting-edge world of drone technology.