
In an era defined by rapid technological advancement and ubiquitous connectivity, the foundational principles of cybersecurity have undergone a profound transformation. No longer is it sufficient to rely on hardened network perimeters; the digital landscape is now a sprawling, interconnected web of users, devices, applications, and services. Within this complex ecosystem, Identity and Access Management (IAM) has emerged not just as a critical component, but as the very cornerstone of security, particularly for the cutting-edge innovations driving our world.
IAM in cyber is a framework of policies, processes, and technologies that manage digital identities and control how users, applications, and devices authenticate and are authorized to access resources. It’s about ensuring that the right entities have the right access to the right resources, at the right time, for the right reasons. This is paramount across all sectors of technology and innovation, from autonomous systems and AI to cloud-native development and advanced remote sensing.

The Imperative of Identity in the Digital Frontier
As technology pushes boundaries, the traditional concept of a secure “perimeter” has all but dissolved. Innovations like cloud computing, mobile workforces, Internet of Things (IoT) devices, and distributed AI models have blurred the lines of what constitutes a secure network. In this new paradigm, identity becomes the new perimeter. Every interaction, every data request, and every command within an innovative system must be validated against a known and authorized identity.
Defining Identity and Access Management (IAM)
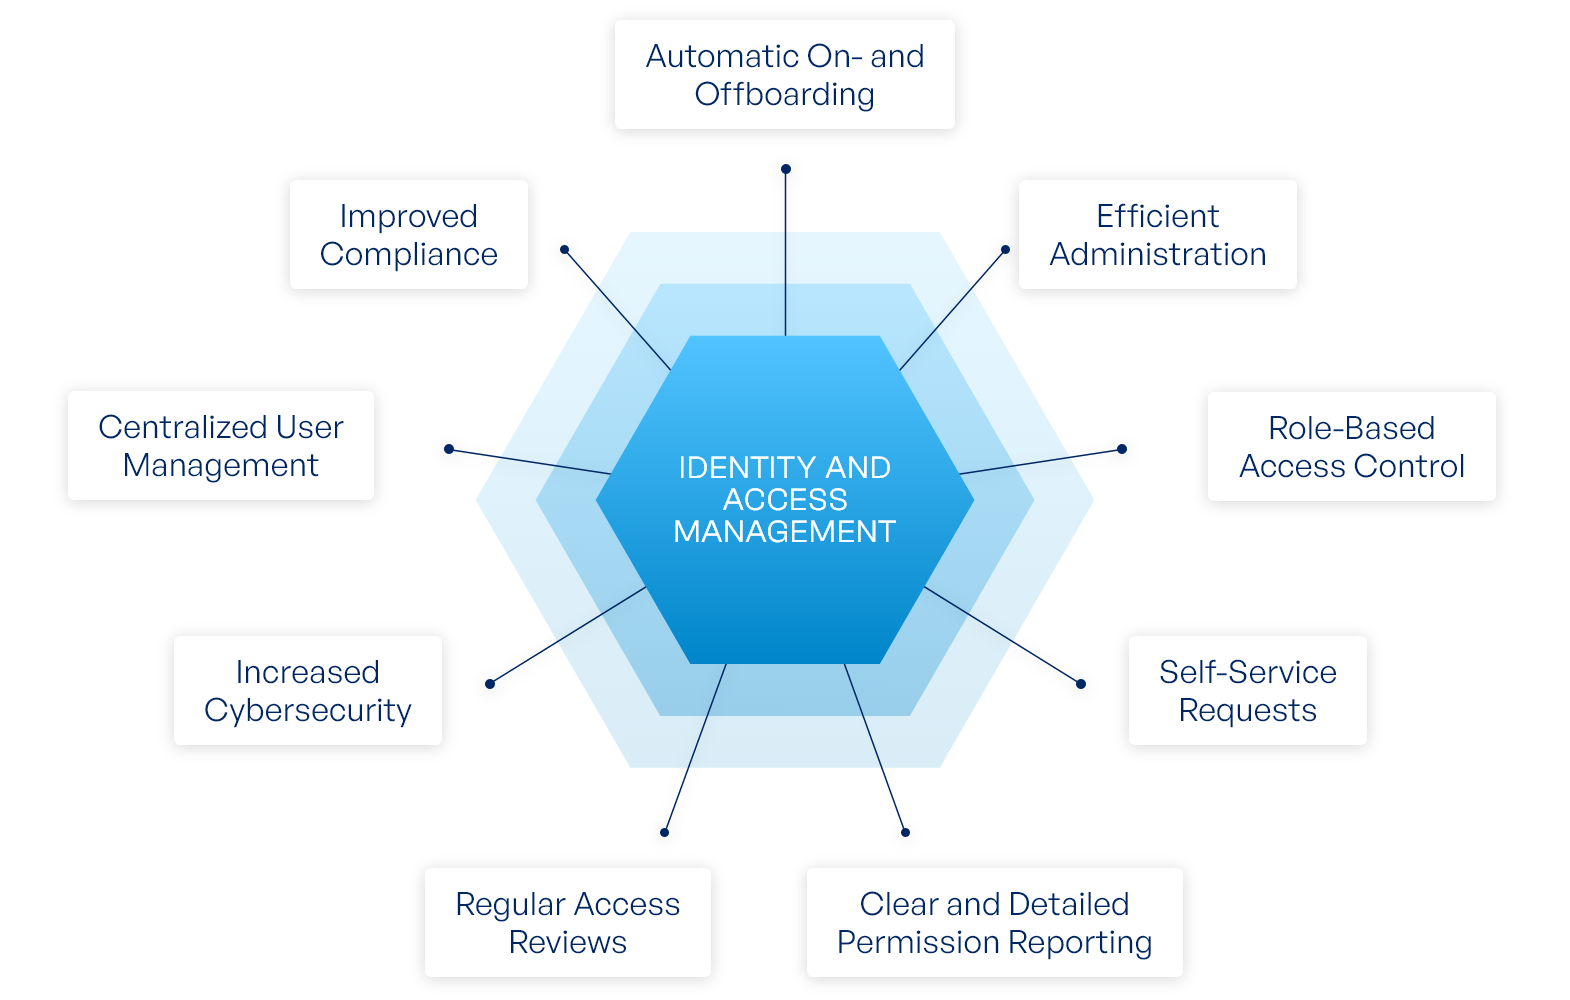
At its core, IAM encompasses a comprehensive set of capabilities designed to manage the entire lifecycle of digital identities and their corresponding access privileges. It goes far beyond mere password management, extending into sophisticated systems that provision identities, authenticate users and devices, authorize access based on roles and policies, and audit all interactions for compliance and security. For any organization pushing the envelope in tech, robust IAM ensures that intellectual property, sensitive data, and operational controls are protected from unauthorized access, both internal and external.
The Shift to Identity-Centric Security
The evolution of technology has necessitated a strategic shift in cybersecurity. Where once firewalls and intrusion detection systems were the primary defenses, the focus has moved to a zero-trust model where no user, device, or application is inherently trusted, regardless of its location or previous authentication. Every access request must be verified. This philosophy places identity at the center of the security strategy, making IAM not just an IT function, but a strategic business imperative for fostering secure innovation. Without granular control over who or what can access innovative systems and data, the very advancements that drive progress become vulnerable.
Core Pillars and Principles of Modern IAM
A comprehensive IAM strategy is built upon several key components, each playing a vital role in securing the digital identities and access pathways within complex technology environments. These pillars work in concert to establish a resilient security posture.
Identity Governance and Administration (IGA)
IGA focuses on the lifecycle management of digital identities and their entitlements. It encompasses processes like user provisioning (creating accounts), de-provisioning (disabling accounts upon departure), and ongoing management of roles and permissions. For large organizations developing and deploying advanced technologies, IGA ensures that access is consistently aligned with an individual’s or system’s current responsibilities.
- User Provisioning and De-provisioning: Automating the creation and removal of user accounts across various systems, crucial for agile development teams and rapidly evolving project landscapes.
- Role-Based Access Control (RBAC) & Attribute-Based Access Control (ABAC): Defining access based on job roles (e.g., “AI Developer,” “Drone Operator”) or specific attributes (e.g., department, project status). ABAC provides even finer granularity, adapting access dynamically based on real-time attributes.
- Access Certifications and Audits: Regularly reviewing and certifying user access privileges to ensure they remain appropriate and compliant with internal policies and external regulations, vital for sensitive R&D projects.
Access Management
Once an identity is established, access management dictates how that identity proves who it is (authentication) and what it is allowed to do (authorization). This is the gatekeeper function for all digital resources.
- Authentication Mechanisms: Beyond simple passwords, modern IAM leverages Multi-Factor Authentication (MFA) – requiring two or more verification methods – along with biometrics, FIDO keys, and certificate-based authentication. For machine identities in IoT or autonomous systems, strong device authentication is paramount.
- Authorization Controls: After authentication, authorization determines the specific actions an identity can perform. This is where policies are enforced to grant read-only access to one dataset but full administrative control over another, based on predefined rules.
- Single Sign-On (SSO): Enhances user experience and security by allowing users to authenticate once and gain access to multiple independent software systems with a single set of credentials. This is invaluable for developers working across numerous platforms and tools.
Privileged Access Management (PAM)
PAM is a specialized subset of IAM focused on securing and managing privileged accounts—those with elevated permissions that can make significant changes to critical systems or access sensitive data. These accounts, often used by system administrators, developers, and automated processes, represent the highest risk if compromised.
- Just-in-Time Access: Granting privileged access only when needed and for a limited duration, minimizing exposure.
- Session Monitoring and Recording: Continuously monitoring privileged sessions and recording activities for auditing and forensic analysis, critical for safeguarding highly sensitive innovation platforms.
- Credential Vaulting: Storing and managing privileged credentials in a secure, centralized vault, preventing direct exposure to users.
IAM in the Realm of Advanced Tech & Innovation
The principles of IAM are universally applicable, but their implementation takes on specific significance and complexity when applied to the forefront of technological innovation.
Securing Autonomous Systems and IoT
The proliferation of autonomous systems, from drones and self-driving vehicles to smart sensors and industrial robots, introduces a unique set of IAM challenges. Each device needs its own secure identity.
- Device Identity Management: Assigning unique, verifiable identities to every IoT device or autonomous unit. This includes secure onboarding and lifecycle management of device certificates or keys.
- Machine-to-Machine (M2M) Authentication: Ensuring that when an autonomous drone communicates with a ground control station or a sensor sends data to an analytics platform, both entities are securely authenticated and authorized.
- Controlling Operational Commands: Only authorized human operators or pre-approved automated systems should be able to issue commands to autonomous units, preventing malicious interference or unauthorized data access.
Protecting AI/ML Models and Data Pipelines
Artificial Intelligence and Machine Learning are increasingly central to innovation, but the models themselves and the vast datasets they consume are highly valuable and sensitive. IAM is critical for their protection.
- Access to Training Data: Granular control over who can access, modify, or delete the often-proprietary and sensitive data used to train AI models.
- Securing Model Development Environments: Managing access to development platforms, code repositories, and computational resources used by data scientists and ML engineers.
- IAM for Automated Pipelines: Ensuring that automated CI/CD pipelines used to deploy and update AI models operate with precisely the necessary permissions and no more.
Cloud-Native Development and Remote Sensing
Modern innovation heavily relies on cloud infrastructure, offering scalability and flexibility. Remote sensing, often facilitated by drones and satellite technology, generates massive amounts of sensitive geospatial data. IAM is the backbone for securing these environments.
- Cloud IAM (e.g., AWS IAM, Azure AD, GCP IAM): Managing identities and access to cloud resources, services, and data. This includes securing API access, service accounts, and virtual machines.
- Data Governance for Geospatial Data: Controlling who can access, process, and share high-resolution imagery and derived insights from drone surveys or satellite platforms, often critical for national security or commercial advantage.
- Automated Security for Cloud Microservices: Implementing IAM for serverless functions and microservices, ensuring secure communication and minimal privilege for each component of a complex cloud-native application.
Challenges and the Evolving Landscape of IAM
Despite its criticality, implementing and maintaining robust IAM in a rapidly evolving tech environment is not without its challenges. The landscape is dynamic, requiring continuous adaptation and innovation within IAM itself.
Complexity and Integration Hurdles
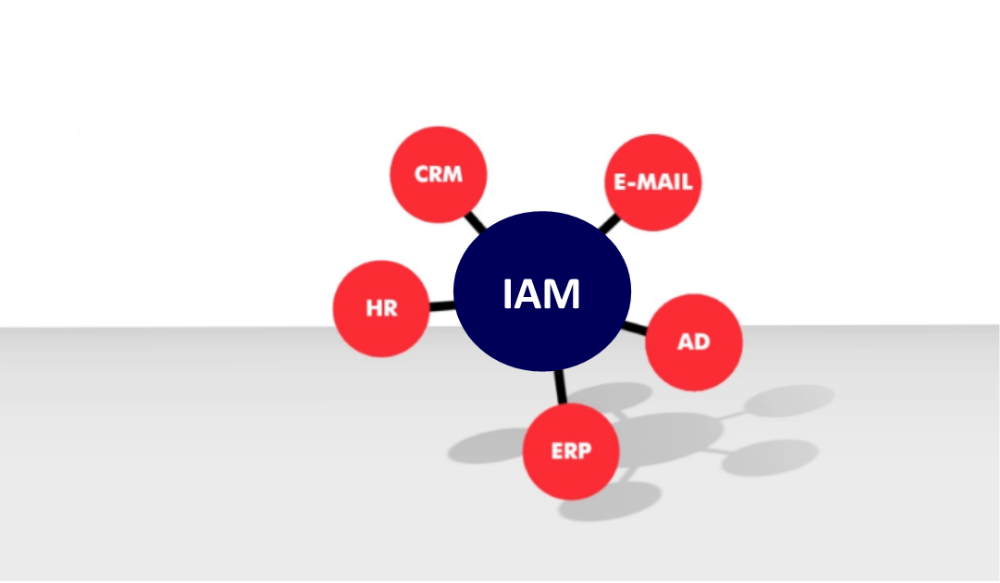
Integrating diverse, often disparate systems—legacy applications alongside cutting-edge cloud services, custom-built AI platforms, and IoT device networks—into a unified IAM framework is a monumental task. The absence of common standards and the sheer volume of identities and access points can lead to complex architectures and potential security gaps.
The Zero-Trust Imperative
The adoption of a zero-trust security model has profound implications for IAM. It mandates continuous verification of identity and device posture for every access request, moving beyond static permissions. This requires highly adaptive authentication policies and micro-segmentation capabilities, where IAM becomes an active, real-time decision engine rather than a passive enforcer.
AI and Behavioral Analytics in IAM
The future of IAM will increasingly leverage AI and machine learning to enhance its capabilities. Behavioral analytics can detect anomalous access patterns or user behavior indicative of a compromised account or insider threat. AI-driven identity governance can automate access reviews and recommend appropriate permissions, reducing manual overhead and improving accuracy. Adaptive authentication, which adjusts security requirements based on context (e.g., location, time, device health), further strengthens defense.
Compliance and Regulatory Demands
For organizations operating in regulated industries or handling sensitive data (e.g., personal data collected by drones, critical infrastructure data from remote sensing), robust IAM is essential for demonstrating compliance with various mandates like GDPR, HIPAA, or industry-specific standards. Comprehensive auditing, reporting, and lifecycle management capabilities are crucial for meeting these strict requirements and avoiding severe penalties.
In conclusion, as the pace of technological innovation accelerates, so too must our approach to securing these advancements. IAM is no longer a peripheral IT function but a strategic imperative that underpins the security, integrity, and trustworthiness of every new technology, from the smallest drone to the most complex AI system. It empowers organizations to innovate with confidence, knowing that their digital identities, assets, and intellectual property are comprehensively protected.