
The digital age has revolutionized how we conduct transactions, making purchasing more convenient than ever. Yet, with this convenience comes an inherent need for robust security measures. Among the myriad of safeguards designed to protect consumers and merchants, the Card Verification Value (CVV) code stands as a cornerstone of online and card-not-present transaction security. Often a small, seemingly innocuous set of numbers on the back of your credit or debit card, the CVV code plays an outsized role in authenticating purchases and mitigating fraud. Understanding its purpose, function, and importance is crucial for anyone engaging in modern financial exchanges, representing a significant piece of technological innovation in safeguarding digital commerce.

The Foundation of Card Security: What CVV Means
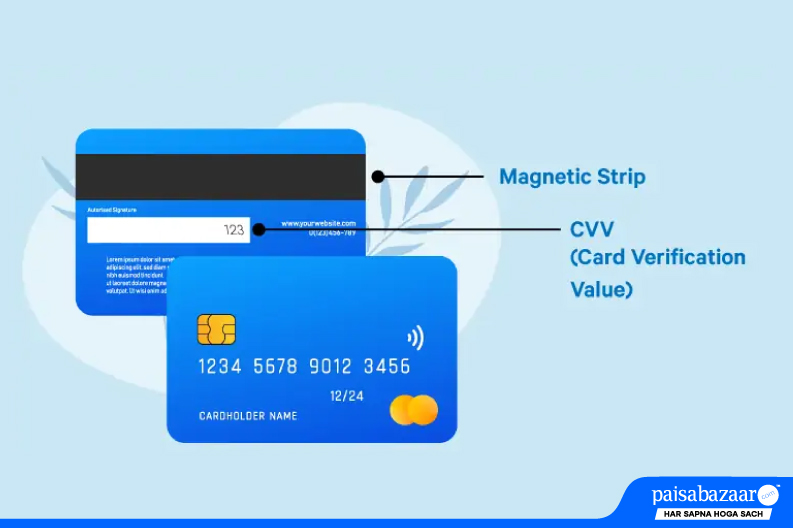
At its core, CVV is an acronym for Card Verification Value, a security feature implemented by major credit card companies. While the term “CVV” is widely recognized, different card networks use slightly varied nomenclature. Visa refers to it as CVV2, MasterCard as CVC2 (Card Validation Code 2), American Express as CID (Card Identification Number), and Discover as CID as well. Despite the different names, their fundamental purpose remains identical: to verify that the person making a purchase has legitimate physical possession of the card. This numerical sequence is not encoded on the magnetic stripe of the card, nor is it typically stored in point-of-sale (POS) systems or online merchant databases after a transaction, which is a critical design feature for security.
The inception of the CVV code was a direct response to the escalating problem of credit card fraud, particularly in card-not-present (CNP) scenarios such as online purchases, mail orders, and telephone orders. Before its widespread adoption, fraudsters could easily make purchases with stolen card numbers alone. The CVV code introduced an additional layer of authentication, requiring a piece of information that is only visible on the physical card itself. This innovation significantly raised the bar for fraudsters, making it much harder to misuse stolen card numbers without also possessing the physical card. It shifted the paradigm, forcing a verification step that could not be easily circumvented by simply obtaining card data through skimming or data breaches that typically only capture the primary account number (PAN) and expiration date.
How CVV Works: An Invisible Shield
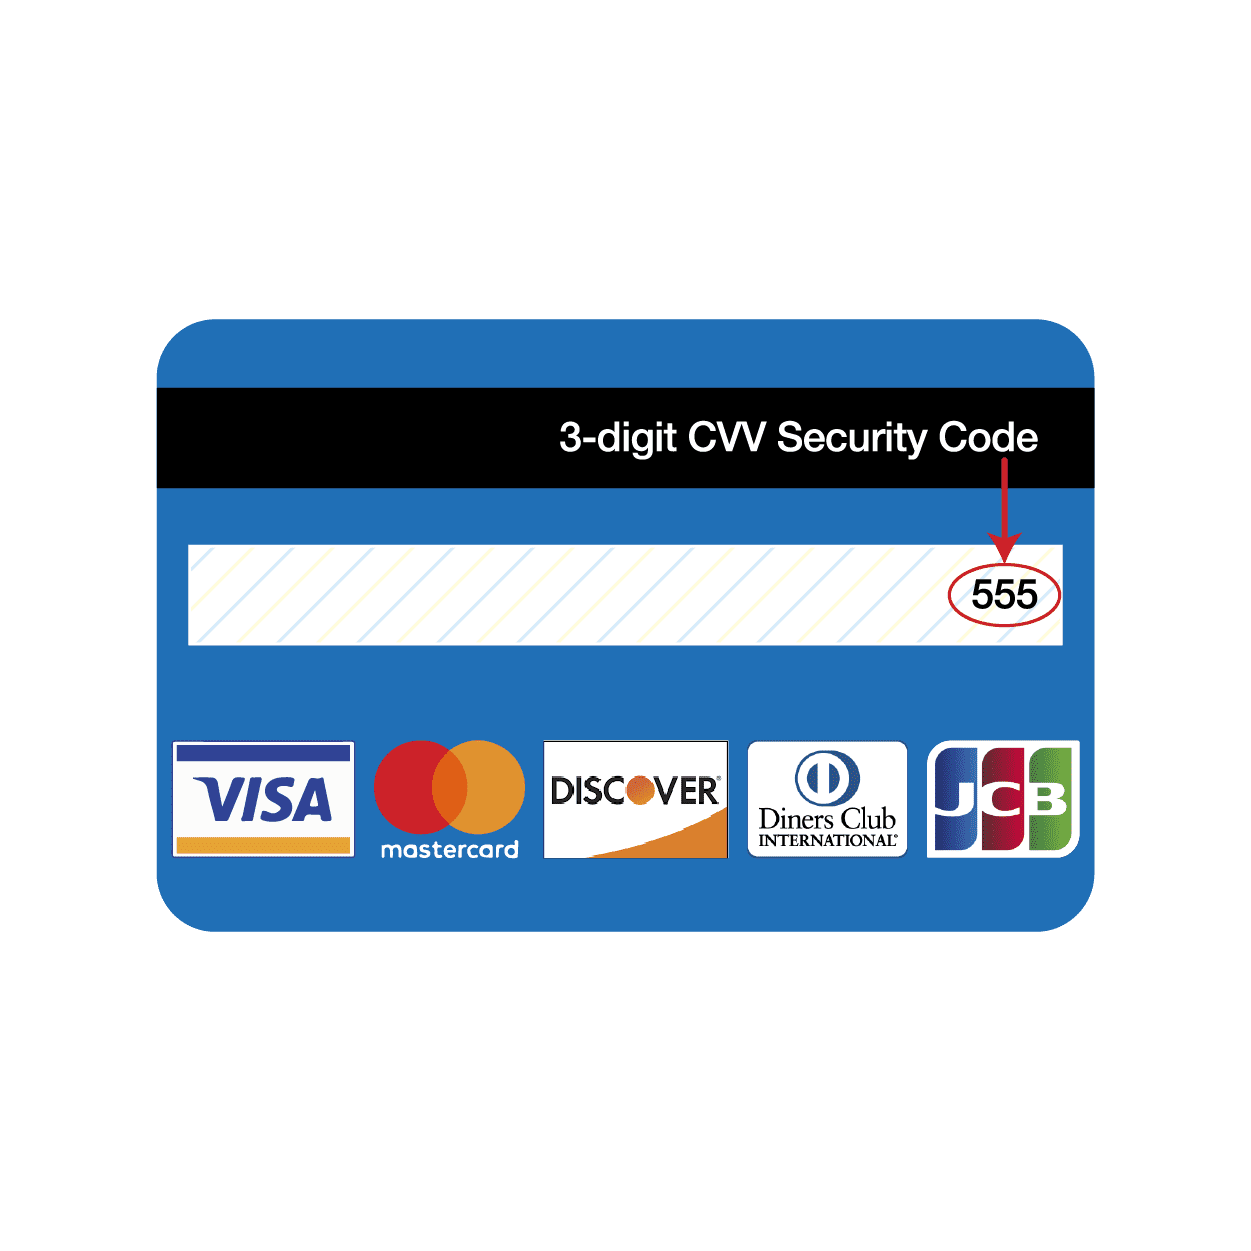
The mechanism behind the CVV code is elegantly simple yet remarkably effective. When you make an online purchase, you are typically prompted to enter the card number, expiration date, cardholder name, and the CVV code. This code is generated algorithmically and is unique to each card. For Visa, MasterCard, and Discover cards, it is a three-digit number usually found on the back of the card, often in or near the signature strip. For American Express cards, it is a four-digit number located on the front of the card, above the account number.
Upon submission, this information, including the CVV, is transmitted securely to the card issuer (your bank or credit union). The issuer’s system then performs a real-time verification check. It compares the entered CVV code against the original code generated for that specific card. If the codes match, the transaction proceeds; if they do not, the transaction is declined. This real-time authentication is paramount because it immediately confirms that the person initiating the transaction likely has the physical card.
A crucial aspect of CVV functionality lies in its non-storage policy. Payment Card Industry Data Security Standard (PCI DSS), a global standard for protecting cardholder data, strictly prohibits merchants from storing the CVV code after authorization. This is a deliberate design choice that enhances security significantly. Even if a merchant’s database is compromised in a data breach, the CVV codes of their customers are not stored there, meaning fraudsters cannot obtain them along with the card numbers and expiration dates. This greatly reduces the utility of stolen data for CNP fraud, as the essential verification code is missing. This distinction is vital: while a credit card number and expiration date can be used to make purchases if a CVV isn’t required (e.g., at certain older terminals or for recurring payments where the first transaction verified the CVV), the CVV acts as a dynamic, single-use key for each new card-not-present transaction.
It is also important to differentiate the CVV from other security features. It is not a PIN (Personal Identification Number), which is used for card-present transactions like ATM withdrawals or in-store purchases requiring chip-and-PIN authentication. Nor is it directly part of the EMV chip technology, which encrypts transaction data for card-present interactions. The CVV specifically addresses the unique vulnerabilities of transactions where the card is not physically swiped or inserted.
Why CVV is Crucial for Modern Transactions
The role of the CVV code in today’s digital economy cannot be overstated. With the massive shift towards e-commerce and mobile payments, CNP transactions now constitute a significant portion of all financial activity. Without the CVV, these transactions would be far more susceptible to fraud, leading to massive financial losses for both consumers and financial institutions. Its presence provides a simple yet effective barrier against unauthorized use, giving consumers greater confidence when shopping online.
For merchants, integrating CVV verification into their payment gateways is not just a best practice; it’s a critical component of their fraud prevention strategy and often a requirement for compliance with PCI DSS. By requiring the CVV, merchants not only protect themselves from chargebacks due to fraud but also contribute to a safer overall payment ecosystem. Transactions that include CVV verification are generally less risky and thus may incur lower processing fees from payment processors. This technological innovation, therefore, has both direct security benefits and economic implications, reducing the operational costs associated with managing fraud.
In the unfortunate event of a data breach where card numbers and expiration dates are stolen from a merchant’s system, the absence of the CVV code prevents fraudsters from immediately using that data for CNP transactions. This significantly limits the damage from such breaches and provides valuable time for card issuers to detect suspicious activity and take preventative measures, such as issuing new cards. This architectural choice underscores the foresight in its design – anticipating a future where data breaches would become increasingly common and building resilience into the payment system itself. This makes the CVV code a prime example of a simple, effective technological innovation designed to enhance trust and security in complex financial networks.
Best Practices and the Future of Card Security
Protecting your CVV code is as important as protecting your card number. Never share your CVV code via email or insecure messaging platforms. Be wary of phishing attempts that try to solicit this information. Legitimate financial institutions will never ask you for your full card number, expiration date, and CVV code in an unsolicited email or phone call. Always ensure you are on a secure website (look for “https://” and a padlock icon) before entering any payment information.
The landscape of payment security is continually evolving, with innovations building upon foundational concepts like the CVV. While the traditional CVV remains a vital tool, newer technologies are emerging to enhance security further. Dynamic CVV, for instance, is an innovative solution where the CVV code changes periodically, often displayed on a small e-ink screen on the card itself or generated within a banking app for digital cards. This makes even a compromised CVV useless after a short time. Tokenization, another significant advancement, replaces sensitive card data with a unique, encrypted token for each transaction, rendering the original card details unusable if intercepted.
Furthermore, advancements in biometric authentication (fingerprint, facial recognition) and improved versions of 3D Secure (like 3D Secure 2.0) are integrating more deeply into the payment process. These systems leverage a wider array of data points to assess transaction risk in real-time, often without requiring the user to manually enter additional information for low-risk transactions. However, even with these sophisticated layers, the CVV code continues to serve as a fundamental security check, especially for transactions initiated through less advanced systems or when initial authentication layers are circumvented. It stands as a testament to effective, robust technological innovation in the enduring battle against financial fraud.