
Understanding Common Vulnerabilities and Exposures (CVE)
In the intricate and rapidly evolving landscape of modern technology, security stands as a paramount concern. From the foundational operating systems that power our devices to the sophisticated algorithms driving artificial intelligence and autonomous systems, every piece of software and hardware carries the potential for exploitable flaws. To bring order and a common language to the discovery and reporting of these flaws, the cybersecurity community relies on the Common Vulnerabilities and Exposures (CVE) system. More than just a list, CVE is a dictionary that provides a standardized identifier for publicly disclosed cybersecurity vulnerabilities, making it an indispensable tool for security professionals, developers, and organizations striving to maintain robust defense postures.
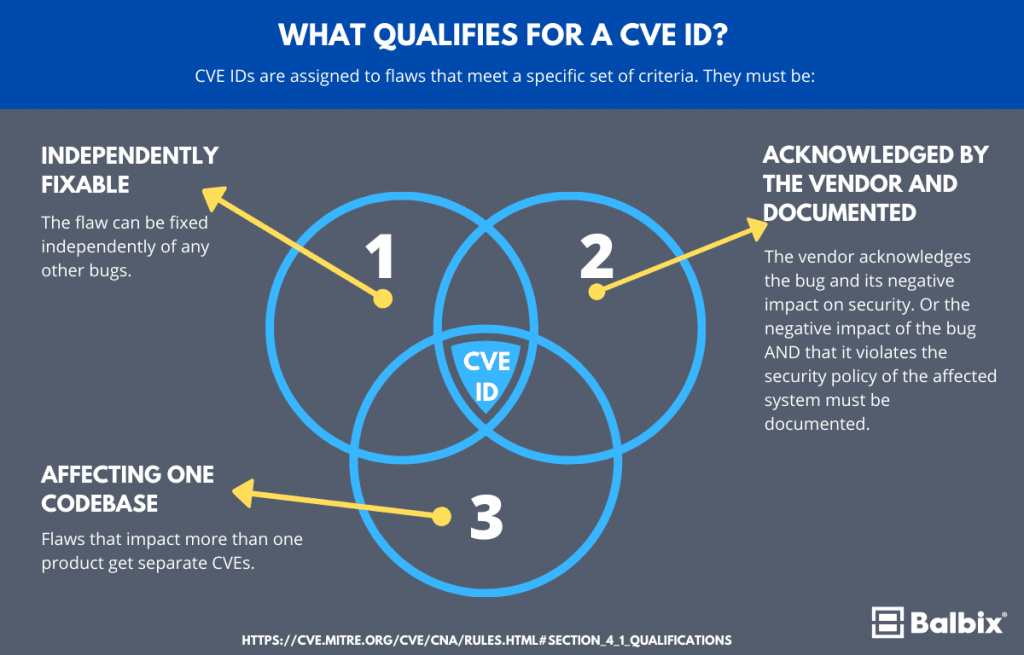
The genesis of CVE can be traced back to the late 1990s, an era when the internet was rapidly expanding, and with it, the number and complexity of software vulnerabilities. Before CVE, security advisories often used disparate naming conventions, making it exceedingly difficult to correlate information about the same vulnerability across different vendor reports, security bulletins, and vulnerability databases. This lack of a universal identifier created significant friction in information sharing, hindering effective risk assessment and mitigation efforts. MITRE Corporation, a not-for-profit organization dedicated to solving problems for a safer world, stepped forward to address this challenge by launching the CVE Project in 1999. Their vision was to establish a common, public registry of unique identifiers for all known cybersecurity vulnerabilities, thereby fostering a more cohesive and efficient approach to vulnerability management.
A CVE identifier is not merely a random string; it follows a precise structure designed for clarity and ease of reference. Typically, a CVE ID appears in the format CVE-YYYY-NNNNN, where YYYY represents the year the CVE ID was assigned or the vulnerability was publicly disclosed, and NNNNN is a sequential number. This numbering scheme allows for quick identification of when a vulnerability entered the public discourse and provides a unique handle to track its details. For instance, CVE-2023-12345 would refer to the 12,345th vulnerability assigned a CVE ID in 2023. It’s crucial to understand that a CVE ID itself does not contain technical details, risk scores, or remediation information; it serves solely as a unique pointer to a specific vulnerability description. This description, however, typically includes information about the affected product, the nature of the vulnerability, and references to advisories or patches from vendors.
At the heart of the CVE program’s operation is the collaborative ecosystem orchestrated by MITRE. While MITRE maintains the master list and provides overall guidance, the assignment of CVE IDs is a distributed process involving numerous organizations worldwide, known as CVE Numbering Authorities (CNAs). CNAs are vendors, open-source projects, bug bounty programs, and security research organizations authorized to assign CVE IDs to vulnerabilities discovered within their scope. This decentralized model ensures broad coverage and timely assignment of identifiers as new vulnerabilities emerge across the vast spectrum of software and hardware products. When a CNA discovers or is informed of a new vulnerability, they assign a provisional CVE ID, which then becomes official upon public disclosure and entry into the CVE List. This collaborative framework underscores CVE’s commitment to being a community-driven initiative, providing a shared foundation for cybersecurity information.
The Critical Importance of CVE in Tech & Innovation
The role of CVE transcends mere enumeration; it acts as a fundamental pillar supporting the security of cutting-edge technologies and driving innovation responsibly. In an era where AI, autonomous systems, and advanced remote sensing are rapidly becoming integral to our infrastructure and daily lives, understanding and addressing vulnerabilities with precision is paramount.
One of the most significant contributions of CVE is its function as a universal language for security flaws. Before CVE, different vendors might describe the same buffer overflow vulnerability in their respective products using entirely different terminology, making it difficult for organizations to track and correlate vulnerabilities across their diverse technology stacks. CVE provides a standardized, vendor-agnostic reference point. When a CVE ID is assigned, it creates a common denominator that all stakeholders—from software developers and security researchers to system administrators and end-users—can use to discuss, document, and manage specific vulnerabilities. This common language streamlines communication, reduces ambiguity, and ensures that everyone is on the same page when addressing a security threat, which is especially critical in complex, interconnected systems typical of modern tech innovations.
Furthermore, CVE plays a pivotal role in enhancing risk management and prioritization strategies within organizations. By having a unique identifier for each vulnerability, security teams can more effectively catalog the weaknesses present in their deployed technologies. This allows for systematic tracking of which components are affected, what patches are available, and the potential impact of an exploit. Many vulnerability management tools and services integrate CVE data, enabling automated scanning, assessment, and reporting. When new CVEs are disclosed, organizations can quickly determine if their systems are impacted and prioritize remediation efforts based on the severity of the vulnerability (often augmented by CVSS scores, which are distinct but frequently linked to CVEs) and the criticality of the affected assets. For innovative fields like autonomous navigation or sophisticated data processing in remote sensing, where a single vulnerability could have catastrophic consequences, robust risk management facilitated by CVE is non-negotiable.

CVE also acts as a powerful catalyst for facilitating collaboration and information sharing across the global cybersecurity community. The public nature of the CVE List means that once a vulnerability is assigned an ID and disclosed, it becomes accessible to security researchers, product vendors, and end-users worldwide. This transparency fosters a collective defense mechanism. Researchers can analyze disclosed CVEs to understand attack vectors and develop countermeasures, while vendors can use this information to develop patches and improve product security. Moreover, it enables threat intelligence platforms to aggregate data, provide context, and alert organizations about emerging threats that could impact their specific technology profiles. This open exchange of critical security intelligence is vital for keeping pace with sophisticated adversaries and for building more resilient, innovative technological ecosystems.
CVE’s Impact on Modern Technology Ecosystems
The ripple effect of the CVE program extends deeply into various advanced technology domains, particularly those that define the “Tech & Innovation” landscape, such as AI, autonomous systems, mapping, and remote sensing. The security of these systems is not merely a matter of data privacy; it often involves physical safety, critical infrastructure integrity, and national security implications.
Securing autonomous systems and AI is one of the most pressing challenges of our time. Whether we’re talking about self-driving vehicles, intelligent robotics in manufacturing, or drone-based logistics, these systems rely on complex software, sensor arrays, and decision-making algorithms. A vulnerability in any of these components could lead to erratic behavior, loss of control, or unauthorized access, with potentially disastrous real-world consequences. For instance, a CVE related to a buffer overflow in an autonomous drone’s flight control firmware could allow an attacker to gain control or crash the device. Similarly, a logic flaw or injection vulnerability in an AI model’s training data pipeline, if assigned a CVE, would highlight a critical weakness that could lead to biased outcomes or adversarial manipulation. The CVE framework provides the means to systematically identify, categorize, and address these vulnerabilities, enabling developers to build more secure and trustworthy autonomous and AI-driven platforms. It forces a rigorous security-first mindset from design to deployment, crucial for technologies interacting directly with the physical world.
Remote sensing and mapping infrastructure also stand to benefit immensely from a robust CVE-driven security approach. These technologies, often deployed via drones and satellites, gather vast amounts of sensitive geographical and environmental data. Vulnerabilities in the imaging software, data transmission protocols, or storage systems could compromise data integrity, lead to unauthorized access to sensitive information, or even allow for the manipulation of mapping data, which could have significant military, economic, or environmental consequences. A CVE detailing a weakness in the encryption used by a remote sensing payload, or a cross-site scripting flaw in a web application used to manage mapping data, directly enables organizations to understand the threat and implement necessary protections. By cataloging these exposures with CVEs, developers and operators can ensure the confidentiality, integrity, and availability of critical geospatial intelligence.
Beyond specific applications, CVE addresses broader supply chain vulnerabilities, a persistent and growing concern in the tech sector. Modern technologies, especially complex systems like drones, advanced robotics, or cloud-based AI platforms, are rarely built from scratch. They incorporate numerous third-party components, open-source libraries, and commercial off-the-shelf software. A vulnerability in one of these upstream components can propagate throughout the entire supply chain, affecting countless end products. When a CVE is published for a common library, for example, all vendors and developers using that library can quickly identify if their products are affected and take corrective action. This transparency is indispensable for managing the sprawling dependencies of contemporary tech ecosystems, helping to prevent widespread compromises that could halt innovation or cripple essential services.
Navigating the CVE Landscape for Developers and Users
Engaging with the CVE landscape is not just for security experts; it’s a responsibility shared by everyone involved in the lifecycle of technology, from developers writing code to end-users deploying and operating systems. Proactive engagement with CVE information is a cornerstone of effective cybersecurity posture.
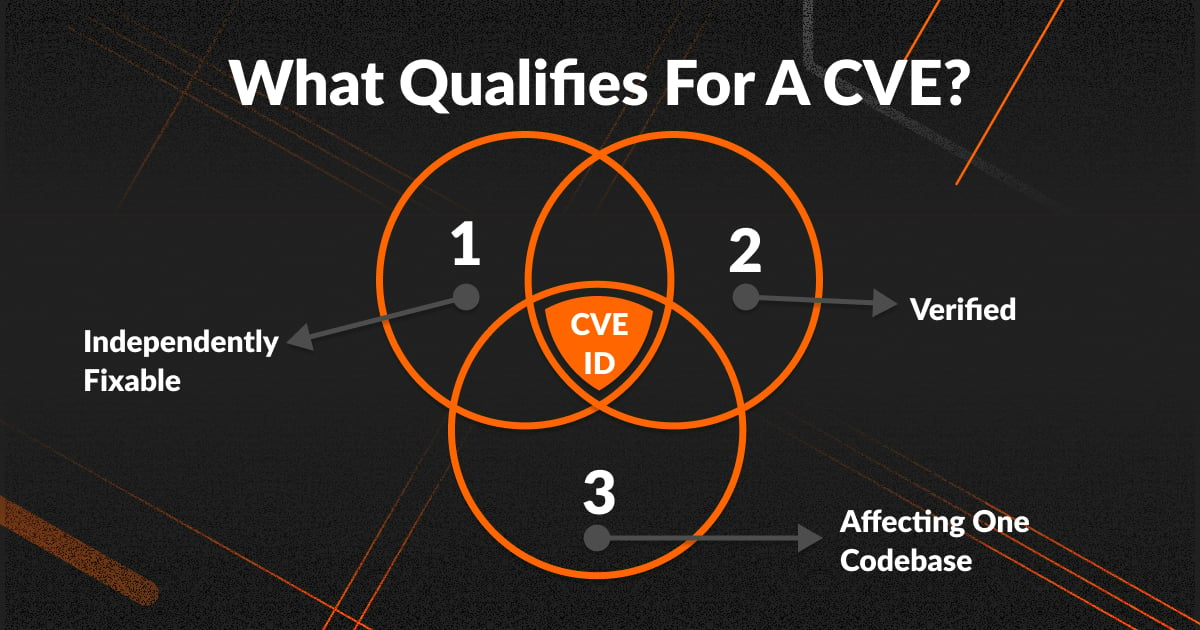
For developers and product teams, proactive vulnerability management is crucial. This involves integrating security best practices throughout the software development lifecycle (SDLC), from initial design and threat modeling to coding, testing, and deployment. When vulnerabilities are discovered—either internally or reported externally—developers must work closely with CNAs to ensure a CVE ID is assigned and that appropriate patches or workarounds are developed and disseminated promptly. This commitment to transparency and timely remediation builds trust and enhances the overall security of innovative products. It means embracing security as an integral part of product quality, not an afterthought, especially in high-stakes fields like autonomous navigation where reliability and safety are paramount.
Staying informed with CVE databases and advisories is equally vital for both developers and users. The official CVE List, maintained by MITRE, is the primary source, but numerous other security organizations, vendors, and community projects integrate and augment this data. Security advisories from vendors (e.g., operating system providers, hardware manufacturers) often refer to CVE IDs when announcing patches for specific products. Subscribing to mailing lists, utilizing vulnerability management platforms that ingest CVE data, and regularly reviewing security news feeds are all essential practices. For operators of systems leveraging AI, remote sensing, or autonomous capabilities, this means actively monitoring for CVEs that affect their specific hardware, software, and third-party dependencies. Being aware of disclosed vulnerabilities allows organizations to implement patches, reconfigure systems, or deploy mitigating controls before an exploit can occur.
Ultimately, contributing to a more secure future is a collective endeavor. While the CVE program provides the framework, its effectiveness relies on the active participation of the entire tech community. This includes security researchers responsibly disclosing vulnerabilities, vendors promptly addressing and patching flaws, and users diligently applying updates. As technologies continue to advance, with AI becoming more sophisticated and autonomous systems more pervasive, the challenge of securing them will only grow. The CVE program offers a standardized, internationally recognized mechanism to address this challenge, fostering a shared understanding and collaborative approach that is indispensable for building trustworthy and resilient innovations that benefit society.