
The Genesis of Card Security
The rapid proliferation of electronic payments revolutionized global commerce, offering unparalleled convenience and efficiency. However, with this technological advancement came an inherent challenge: ensuring the security of transactions, particularly those conducted remotely. Before sophisticated security protocols were commonplace, purchases made online or over the phone – known as “card-not-present” (CNP) transactions – posed significant risks. Fraudsters could easily exploit the system using stolen card numbers and expiration dates, which were often the only pieces of information required. The absence of a physical card for verification created a vulnerability that financial institutions and merchants desperately needed to address.
Early Challenges in Card-Not-Present Transactions
In the nascent stages of digital commerce, the verification methods for credit and debit cards were primarily designed for physical, point-of-sale transactions. Magnetic stripes, and later EMV chips, authenticated the card itself at a terminal. However, when a customer wasn’t physically present to swipe or insert their card, these mechanisms were rendered useless. A simple list of card numbers and expiry dates, whether obtained through data breaches, insecure websites, or even discarded receipts, was often sufficient to make unauthorized purchases. This era saw a surge in fraud, as criminals found it relatively easy to mimic legitimate cardholders from afar, leading to substantial financial losses for consumers, merchants, and card issuers alike. The lack of an additional, cardholder-specific, and non-storable piece of information for remote transactions was a glaring technological gap that necessitated urgent innovation.
The Need for an Additional Layer
Recognizing the escalating threat, card networks and financial technology innovators embarked on developing an supplementary layer of security for CNP transactions. The solution needed to be simple for consumers to use, yet complex for fraudsters to bypass. It had to provide a strong indicator that the person making the purchase was in legitimate possession of the physical card, without requiring a complete overhaul of the existing payment infrastructure. This necessity spurred the creation of a unique, dynamic, or semi-dynamic code that resided only on the physical card and was not embedded within the magnetic stripe or chip data that could be easily copied or skimmed. This innovative approach aimed to introduce a critical piece of information that fraudsters would find difficult, if not impossible, to obtain without direct access to the card itself, thereby significantly mitigating the risks associated with remote transactions and fortifying the trust in digital payments.
Decoding the Card Verification Value (CVV)
At the heart of enhanced CNP transaction security lies the Card Verification Value (CVV). This seemingly innocuous three or four-digit number serves as a powerful bulwark against fraud, acting as an essential authentication factor that verifies the physical presence of the card during remote purchases. Its design is a testament to sophisticated cryptographic principles and careful consideration of user experience, aiming for maximum security with minimal friction. Understanding its nuances, its various nomenclatures, and the underlying technology provides critical insight into its efficacy as a cornerstone of modern payment security.
What it Is and Where to Find It
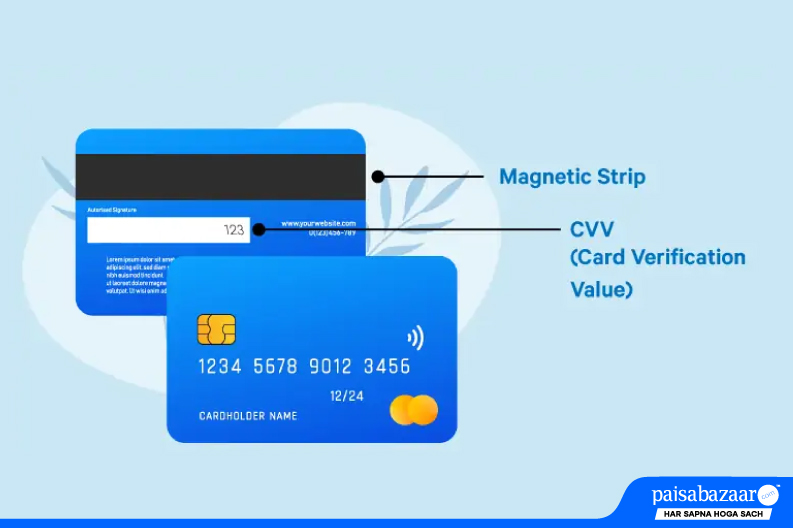
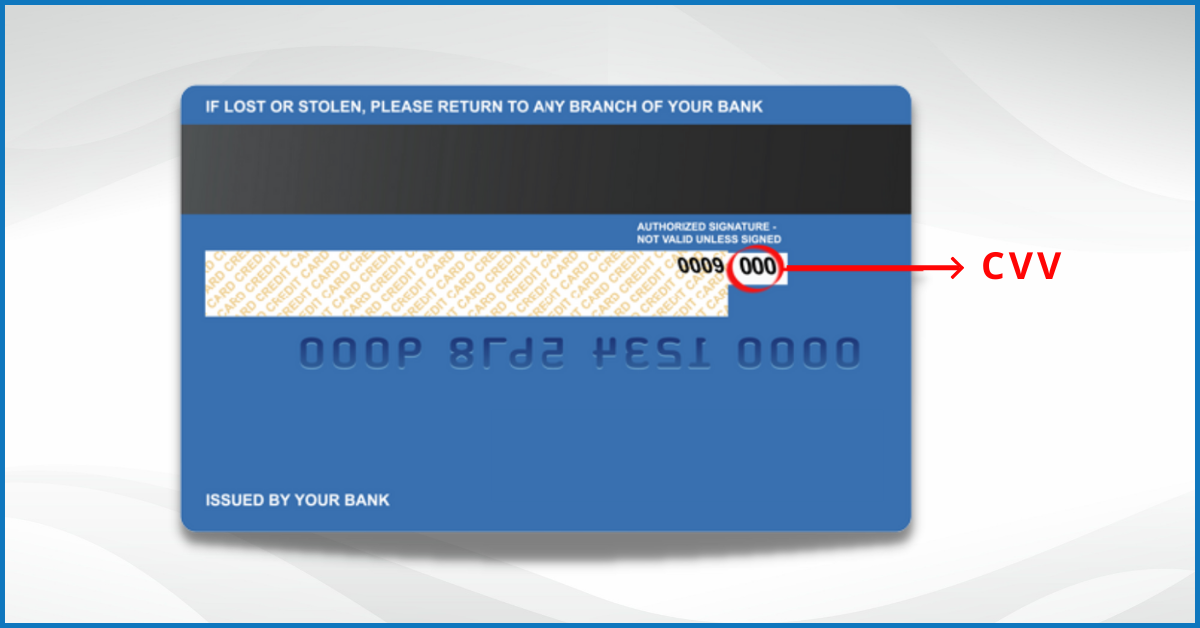
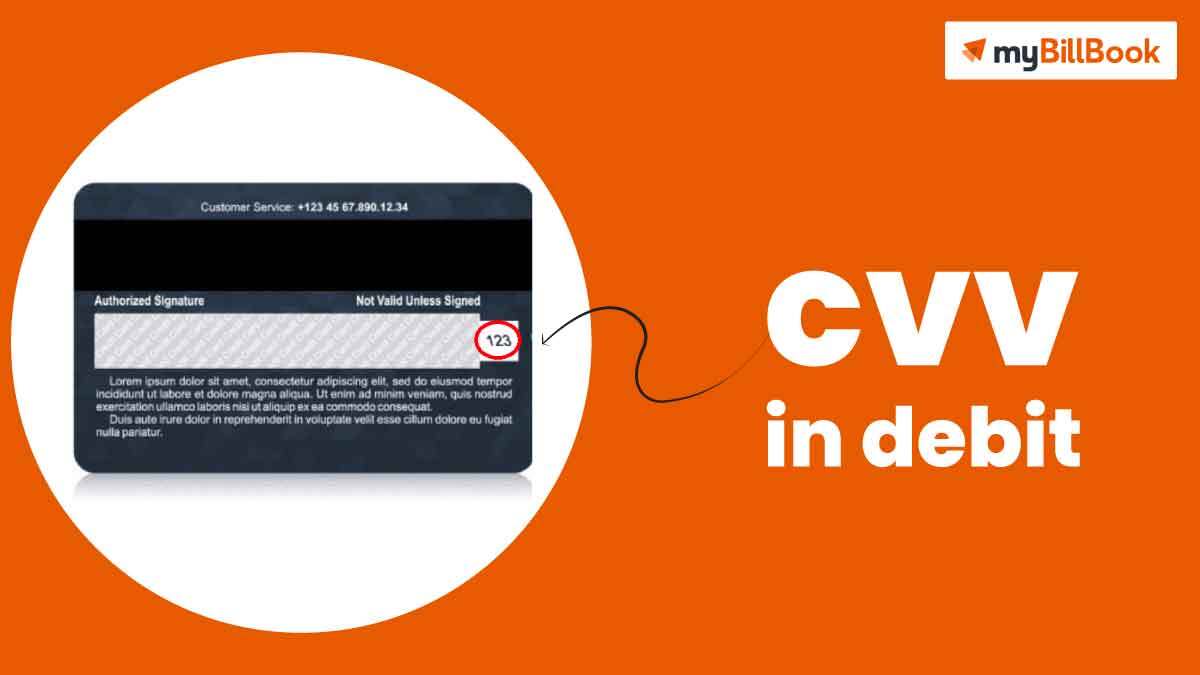
The CVV is a security feature physically printed on the credit or debit card, distinct from the embossed or printed card number. It is never stored electronically in merchant databases after a transaction is authorized, nor is it encoded in the magnetic stripe or chip, which makes it considerably harder for fraudsters to obtain through data breaches or skimming. For Visa, Mastercard, and Discover cards, the CVV is typically a three-digit number found on the back of the card, usually in the signature strip area. American Express cards, on the other hand, feature a four-digit code, often referred to as the Card Identification Number (CID), printed on the front of the card above the main card number. Its placement ensures it is readily accessible to the legitimate cardholder when making an online or phone purchase, yet remains protected from casual observation.
CVV vs. CVC, CID, and Other Acronyms
While “CVV” (Card Verification Value) is the most commonly recognized term, various card networks employ slightly different acronyms for the same security feature. Mastercard uses CVC2 (Card Validation Code 2), where the ‘2’ differentiates it from earlier internal codes. Visa refers to it as CVV2 (Card Verification Value 2). American Express designates it as CID (Card Identification Number). Discover often uses CID as well. Despite these different labels, they all refer to the same concept: a security code printed on the physical card, intended to verify the cardholder’s possession of the card during card-not-present transactions. These distinctions primarily serve branding purposes for the respective networks, but for the end-user and most merchants, the function remains identical – an essential numeric code required for enhanced security.
The Algorithm Behind the Numbers
The apparent randomness of the CVV code belies a sophisticated cryptographic algorithm that underpins its security. When a card is issued, the CVV is not arbitrarily assigned. Instead, it is cryptographically generated by the card issuer using a complex calculation that incorporates several key pieces of information: the card’s primary account number (PAN), the expiration date, the service code, and a unique encryption key known only to the card issuer. This process ensures that each CVV is uniquely linked to a specific card and is highly resistant to brute-force attacks or guessing. The resulting code is then printed on the card. Crucially, because the CVV is derived using this secret key and sensitive card data, it cannot be reverse-engineered or predicted by fraudsters even if they possess the other card details. This technological design makes the CVV an extremely effective tool for verifying the legitimacy of the physical card and, by extension, the cardholder’s authorization for a CNP transaction.
How CVV Enhances Transaction Security
The implementation of CVV as a standard security measure marked a significant leap forward in protecting digital transactions. By serving as a critical piece of information known only to the legitimate cardholder (via physical possession of the card), it erects a robust barrier against various forms of fraud that plague online and phone commerce. Its integration into payment processes has not only made transactions safer for consumers but has also instilled greater confidence among merchants, who are often on the front lines of fraud prevention. The CVV’s effectiveness is multifaceted, spanning protection against direct data theft to guiding industry best practices in data handling.
Protecting Against Fraud in Digital Commerce
The primary function of the CVV is to protect against fraud in card-not-present environments. When an individual makes an online purchase or provides card details over the phone, they are typically prompted to enter the CVV in addition to the card number, expiration date, and cardholder name. This requirement serves as a powerful verification mechanism. If a fraudster manages to steal just the card number and expiration date from a compromised database or through other illicit means, they will likely lack the CVV. Without this crucial three or four-digit code, most payment gateways will decline the transaction, effectively thwarting the unauthorized purchase. This system ensures that even if sensitive card details are compromised, the physical card’s unique identifier acts as a necessary gatekeeper, drastically reducing the success rate of such fraudulent attempts and safeguarding consumer funds.
Merchant Obligations and Data Handling
The CVV’s security benefits are inextricably linked to stringent data handling regulations imposed on merchants. The Payment Card Industry Data Security Standard (PCI DSS) mandates strict rules regarding the storage and transmission of sensitive cardholder data. A cornerstone of these regulations is the absolute prohibition against storing the CVV (CVV2, CVC2, CID, etc.) after the authorization of a transaction. Merchants are allowed to collect the CVV during the transaction process for verification, but once the payment is approved or declined, this sensitive data must be immediately purged from their systems. This technological constraint is critical: even if a merchant’s database is breached, fraudsters will only be able to access card numbers and expiry dates, not the CVV. This policy minimizes the potential damage from data breaches, ensuring that compromised merchant systems do not inadvertently become a source for collecting the essential security code needed to perpetrate further fraud. Adherence to these obligations is a vital component of the overall security ecosystem enabled by the CVV.
The CVV’s Role in Preventing Skimming and Phishing
Beyond safeguarding against database breaches, the CVV plays a crucial role in combating other prevalent fraud techniques like skimming and phishing. Skimming involves the illicit capture of card data from the magnetic stripe at compromised point-of-sale terminals or ATMs. While skimmers can often capture the card number and expiration date, they are generally unable to capture the CVV, as it is a visual code printed on the card and not encoded in the magnetic stripe data. Similarly, phishing attacks, which attempt to trick individuals into divulging sensitive information through deceptive emails or websites, often target card numbers and personal details. However, awareness campaigns educating consumers not to share their CVV via email or suspicious forms have reinforced its protective role. By requiring the CVV for online transactions, even if a fraudster obtains skimmed data or partially successful phishing yields, they are still missing the crucial piece of information needed to complete a card-not-present purchase. This layered defense significantly elevates the effort required for fraudsters to succeed, thereby enhancing overall payment system integrity.
Limitations and Evolving Security Measures
While the CVV has proven to be an indispensable innovation in securing card-not-present transactions, it is not an infallible solution. The landscape of cybersecurity is a constant arms race, with fraudsters continually devising new methods to bypass existing defenses. Consequently, the payment industry has continued to evolve its security protocols, introducing more dynamic and robust technologies that either augment or, in some cases, aim to supersede the traditional static CVV. These advancements reflect a proactive approach to staying ahead of emerging threats and maintaining the highest possible standards of financial security in an increasingly digital world.
When CVV Isn’t Enough
The static nature of the CVV, while beneficial for its simplicity, also presents its primary limitation. If both the card number and the CVV are compromised simultaneously, its protective value diminishes significantly. This can occur through various sophisticated fraud schemes, such as malware on a compromised point-of-sale terminal that captures all entered card details, including the CVV. Similarly, highly effective phishing or pharming attacks can trick cardholders into inadvertently revealing both their card number and CVV on a fake website. Furthermore, the CVV cannot protect against situations where a physical card is lost or stolen, as the fraudster then has direct access to the code. In these scenarios, the CVV’s ability to verify physical possession is negated, highlighting the need for additional layers of security beyond this single static identifier.
The Rise of Tokenization and Biometrics
To address the inherent limitations of static identifiers like CVV, the payment industry has heavily invested in more advanced security technologies such as tokenization and biometrics. Tokenization replaces sensitive card data (including the PAN and effectively the CVV) with a unique, randomly generated “token” during a transaction. This token is useless outside the specific transaction or merchant for which it was generated. If a merchant’s system is breached, only these valueless tokens are exposed, not actual card details. Biometrics, utilizing unique biological characteristics like fingerprints or facial recognition, offers an even more personal and dynamic form of authentication. Integrated into mobile payment systems and online banking, biometrics provides a powerful, user-centric layer of security that moves beyond memorized or printed codes, offering greater convenience and significantly enhanced protection against unauthorized access.
3D Secure and Dynamic CVV
Further bolstering CNP transaction security are protocols like 3D Secure and the emerging concept of Dynamic CVV. 3D Secure, encompassing programs such as Visa Secure (formerly Verified by Visa) and Mastercard Identity Check (formerly SecureCode), adds an extra authentication step during online purchases. After entering card details, including CVV, the cardholder may be redirected to their bank’s website to enter a password, a one-time passcode sent to their phone, or confirm their identity through a biometric scan. This ‘two-factor authentication’ ensures that even if a fraudster has both the card number and CVV, they cannot complete the transaction without this additional, real-time verification. The concept of Dynamic CVV takes this a step further. Instead of a static code, some specialized payment cards or digital wallets generate a CVV that changes periodically (e.g., every 30-60 seconds). Devices like ‘display cards’ feature a small screen to show the constantly changing code. This innovation renders stolen static CVVs useless within a very short timeframe, significantly enhancing protection against long-term data compromises and making it exponentially harder for fraudsters to execute delayed attacks.
Best Practices for Consumers and Businesses
The efficacy of CVV and other advanced security measures is ultimately amplified through informed best practices adopted by both consumers and businesses. While technological innovation provides the tools, diligent implementation and careful handling of sensitive information are paramount to creating a robust defense against fraud. Staying vigilant, adhering to established security protocols, and understanding the evolving threat landscape are collective responsibilities that strengthen the entire digital payment ecosystem.
Safeguarding Your CVV Information
For consumers, protecting your CVV is as crucial as safeguarding your card number. Never share your CVV via email, text message, or over suspicious phone calls, as legitimate institutions will rarely request this information in an unsolicited manner. Always ensure you are on a secure website (indicated by “https://” in the URL and a padlock icon) before entering your card details for online purchases. Be wary of websites or apps that prompt you to save your CVV; legitimate merchants are strictly prohibited from storing it. Physically protect your card by keeping it in a secure place and regularly checking your statements for unauthorized transactions. If you lose your card or suspect it has been compromised, report it to your bank immediately. Maintaining a high level of personal vigilance is your first line of defense in the complex world of digital security.
Implementing Robust Security Protocols
Businesses, particularly those engaged in e-commerce, bear a significant responsibility in protecting their customers’ payment data. Adherence to PCI DSS compliance is non-negotiable, specifically the rule prohibiting the storage of CVV data after authorization. Implementing robust payment gateway integrations that handle sensitive data securely, often through tokenization, is essential. Regular security audits, penetration testing, and vulnerability assessments help identify and rectify potential weaknesses in payment systems. Employing advanced fraud detection tools that analyze transaction patterns, IP addresses, and behavioral cues can help identify and flag suspicious transactions, even those where a CVV might have been compromised. Training staff on secure data handling practices and recognizing phishing attempts further strengthens the organization’s overall security posture. A multi-layered security approach, combining technological safeguards with human vigilance, is critical.
Staying Ahead of Emerging Threats
The battle against financial fraud is an ongoing one, with criminals constantly adapting their tactics. Both consumers and businesses must commit to continuous learning and adaptation to stay ahead of emerging threats. For consumers, this means staying informed about new scams, understanding the latest authentication methods like biometrics and dynamic CVVs, and promptly adopting them where available. For businesses, it involves investing in cutting-edge security technologies, staying abreast of evolving PCI DSS requirements, and actively participating in industry forums and intelligence-sharing networks to understand the latest attack vectors. Regular updates to software, payment systems, and fraud detection algorithms are not optional but essential. The collaborative effort between card networks, financial institutions, merchants, and individual users, underpinned by continuous innovation and education, is the only sustainable path to maintaining a secure and trustworthy digital payment environment.