
The Digital Transformation of Extortion
In its most traditional sense, a ransom is a sum of money or other consideration paid or demanded for the release of a captive or property. This concept, deeply rooted in human history, has undergone a profound transformation with the advent of the digital age. Today, the notion of “ransom” extends far beyond physical abduction or material seizure, evolving into complex digital forms that target information, system control, and operational capability. This shift places it firmly within the realm of Tech & Innovation, particularly in the context of cybersecurity and the protection of advanced technological systems.

Beyond Physical Captives: Data and System Hijacking
The modern interpretation of ransom often involves digital assets rather than human lives or tangible goods. In this evolving landscape, the “captive” can be an organization’s critical data, an individual’s personal files, or even the operational control of sophisticated machinery. The value proposition for the aggressor has moved from direct financial gain through physical seizure to the disruption of services, exploitation of sensitive information, or the immobilization of essential technological infrastructure. This form of digital extortion leverages the interconnectedness and reliance on technology prevalent in modern society, making virtually any digitally-enabled entity a potential target. The core principles of confidentiality, integrity, and availability (the CIA triad of information security) become the battleground, with attackers aiming to compromise one or more of these pillars to compel a payment.
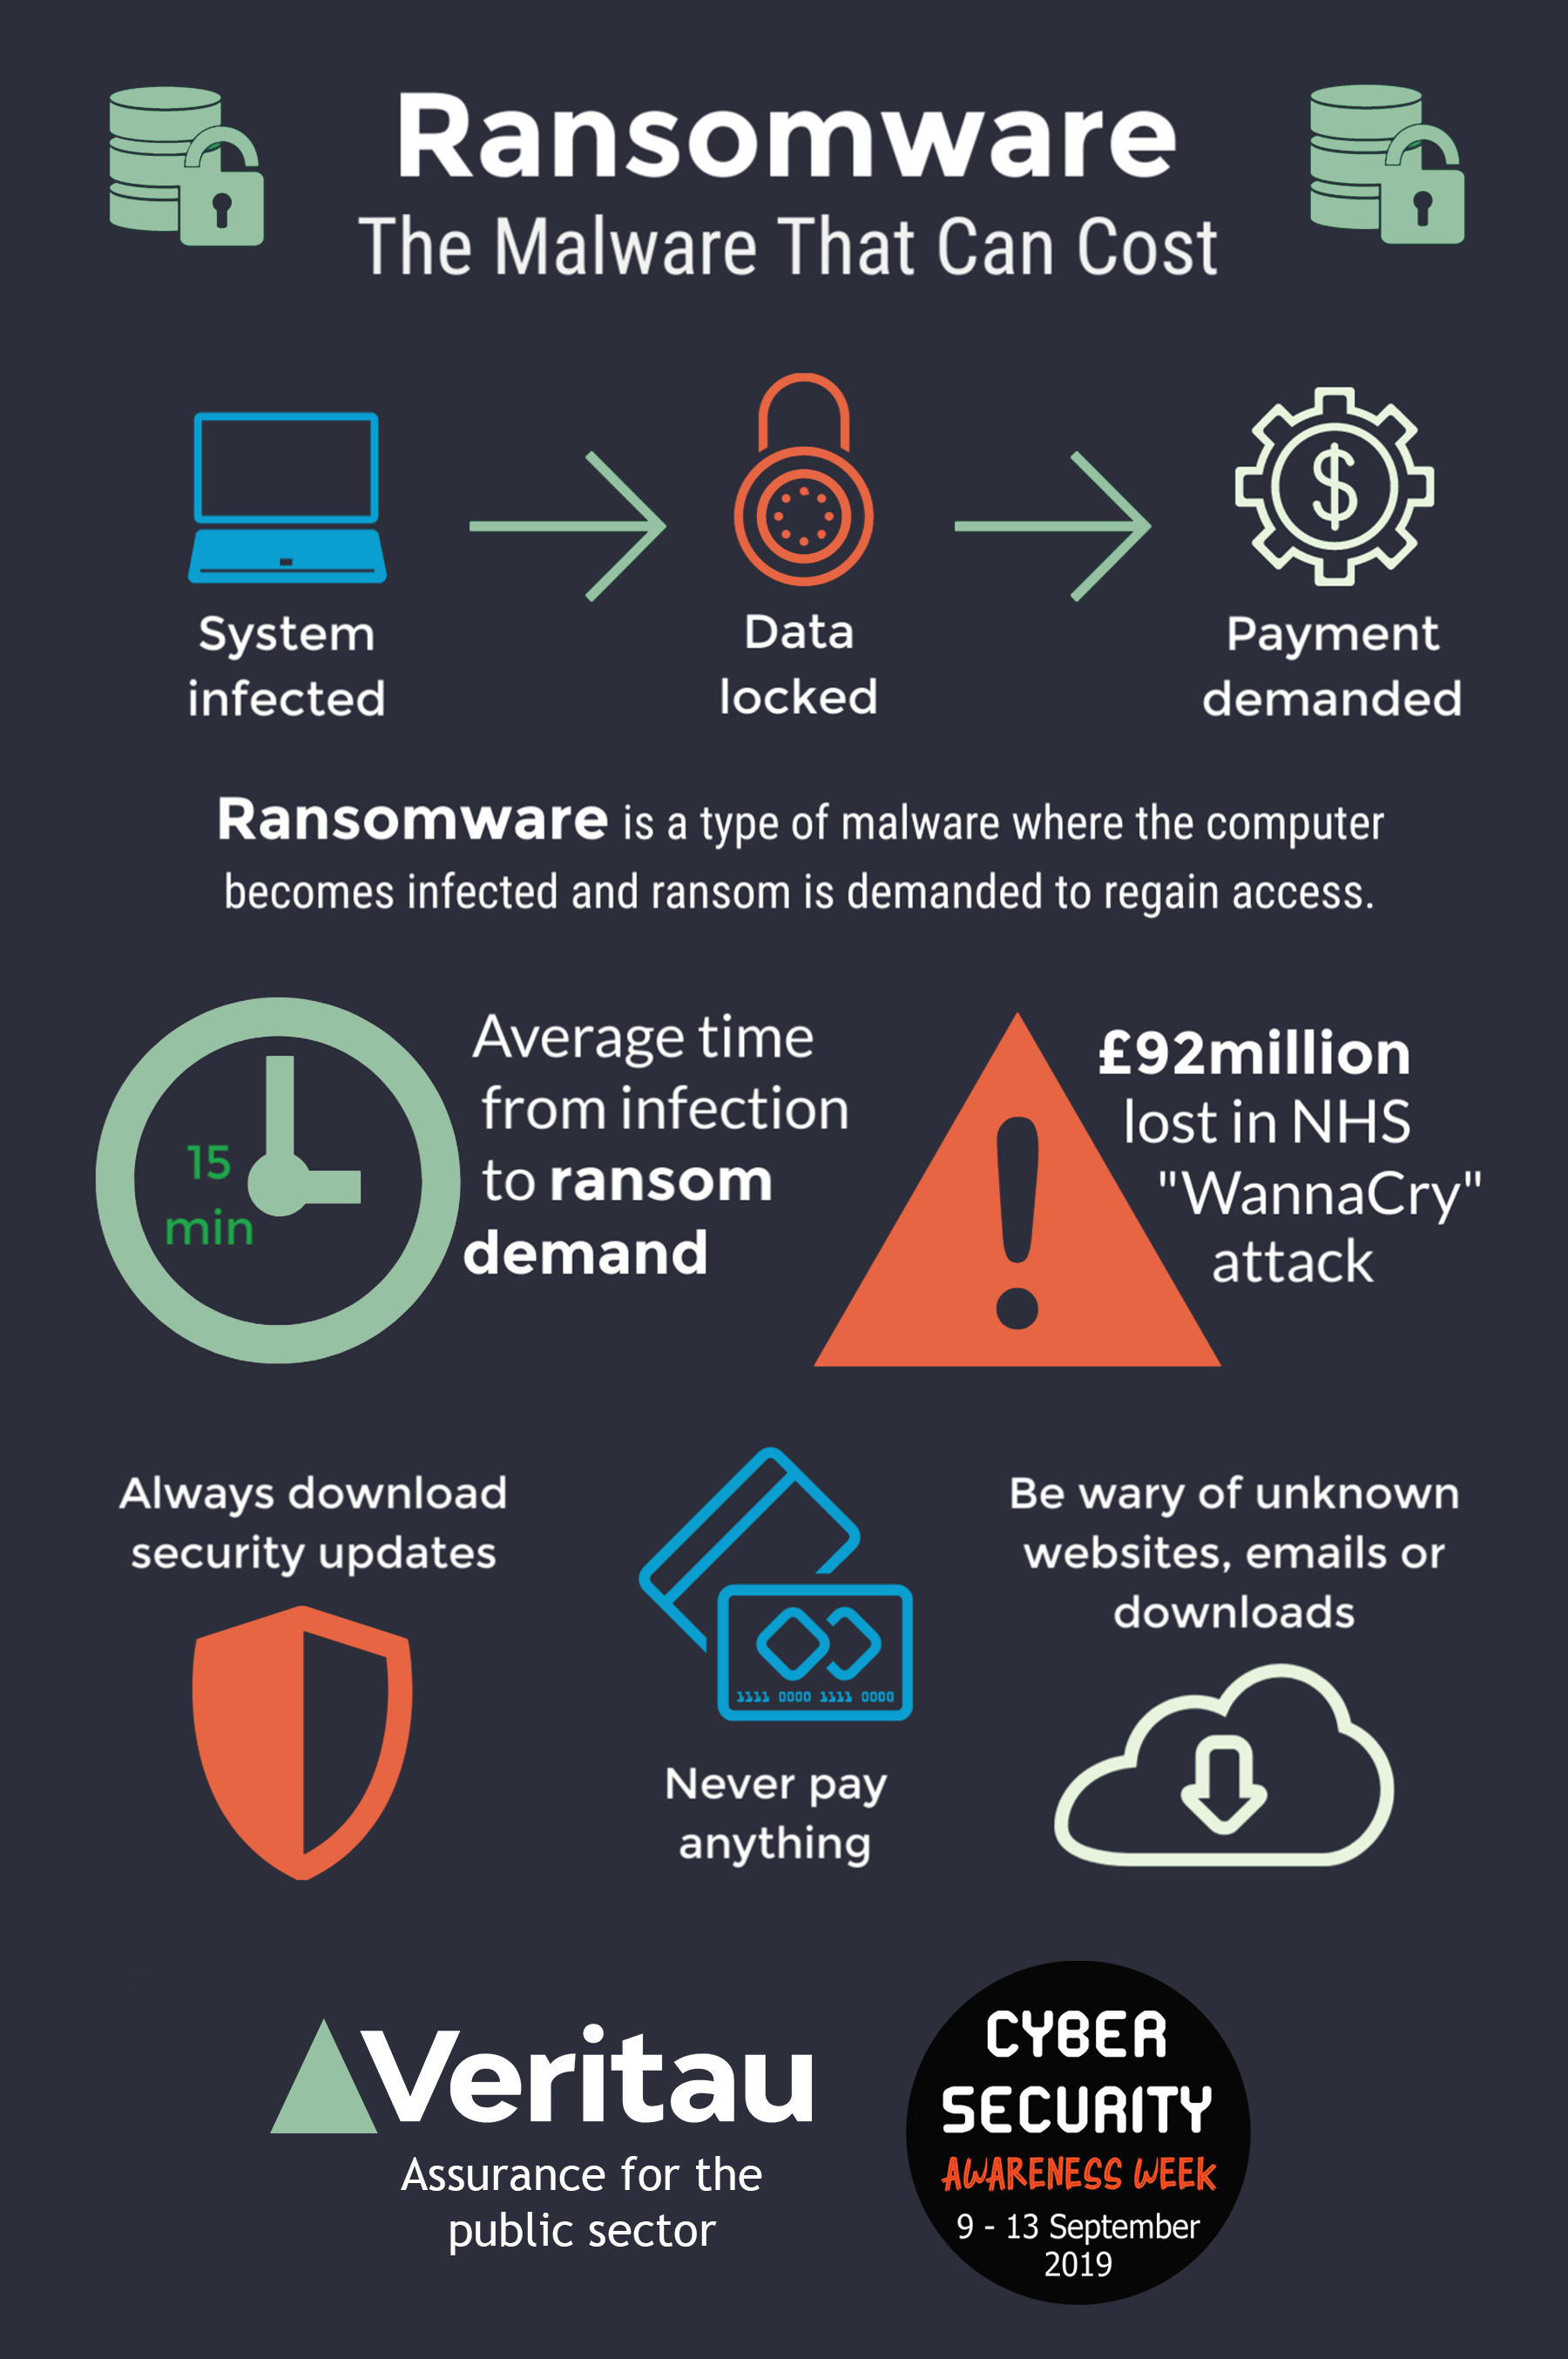
A primary manifestation of this digital ransom is ransomware – malicious software designed to block access to a computer system or data until a sum of money is paid. This is not merely a nuisance; it represents a fundamental threat to the functioning of businesses, governments, and critical services, often demanding payment in cryptocurrencies for anonymity. The payment is typically demanded in exchange for a decryption key or restoration of access, underscoring the shift from holding a person or object hostage to holding digital functionality hostage.
The Mechanics of Ransomware
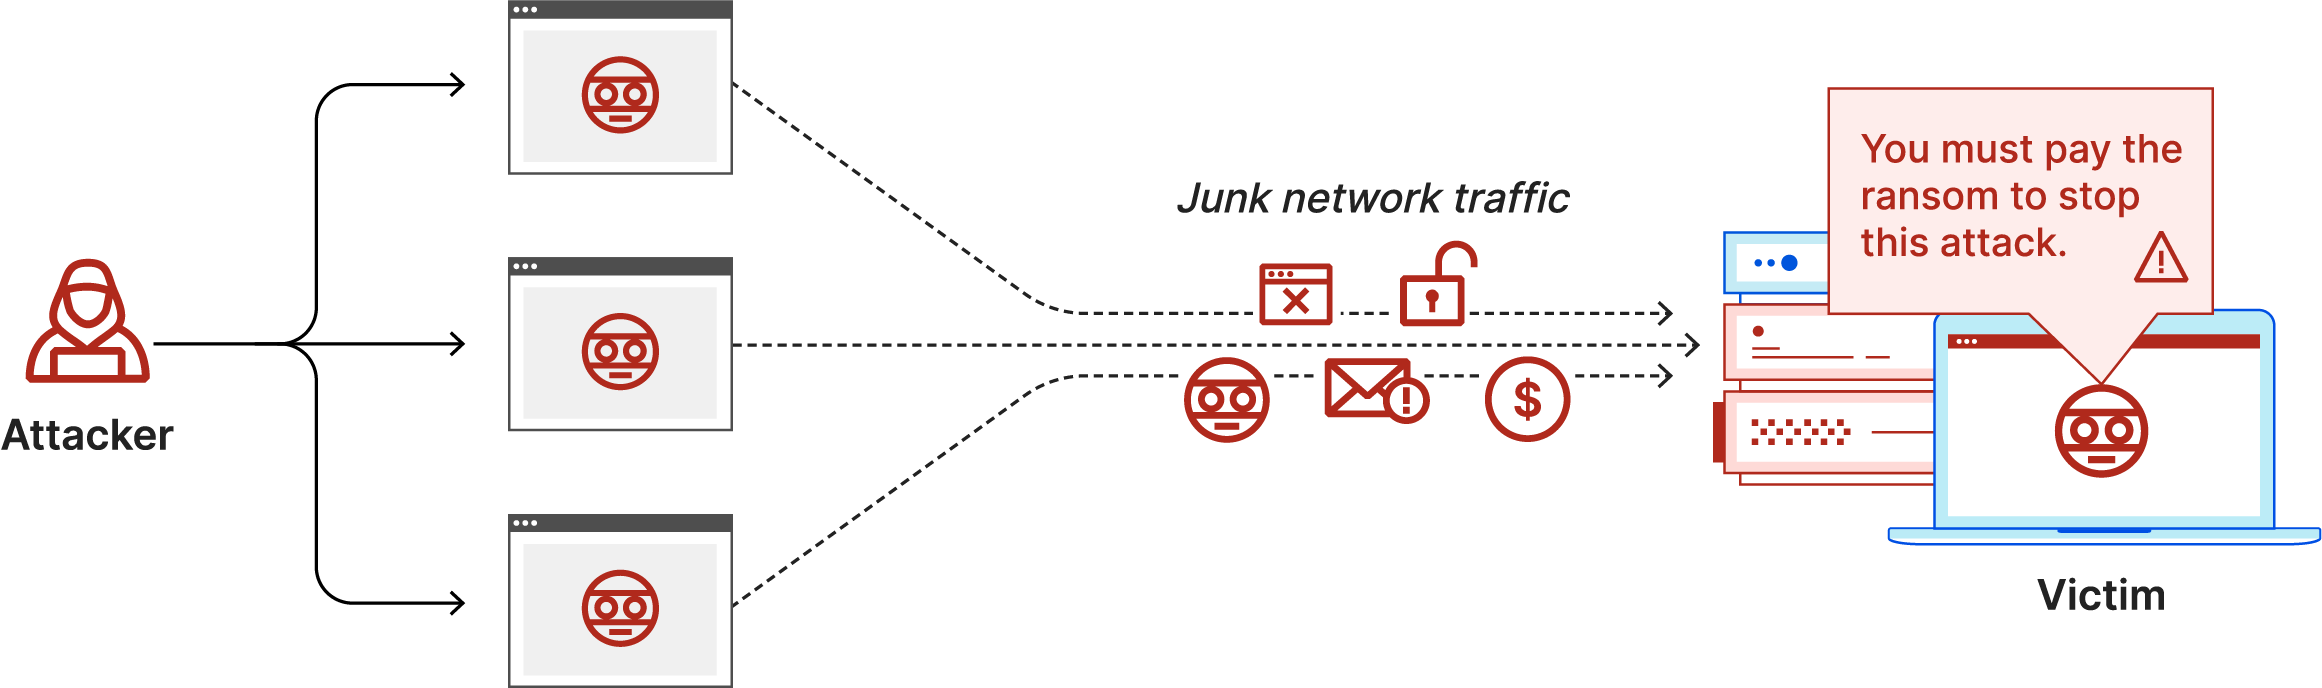
Ransomware attacks are sophisticated operations often involving multiple stages. Initially, attackers gain unauthorized access to a network, typically through phishing emails, exploiting software vulnerabilities (zero-days), or compromising remote access protocols. Once inside, the ransomware payload is deployed. This payload often involves encrypting files on compromised systems, rendering them inaccessible to legitimate users. The encryption is typically robust, making recovery without the attacker’s key virtually impossible. Concurrently, a ransom note appears, detailing the demand, the payment method (usually cryptocurrency like Bitcoin or Monero), and a deadline, often threatening permanent data loss or public release of exfiltrated data if the demand is not met.
Some variants of ransomware go beyond mere encryption, incorporating denial-of-service (DoS) components that flood network resources, or wipers that permanently delete data if the ransom is not paid. The anonymity afforded by cryptocurrencies and the complex network of dark web services used by cybercriminals make attribution and prosecution challenging, further fueling the proliferation of these attacks. The targets are diverse, ranging from individual users to large corporations, hospitals, and even governmental entities, all of whom are increasingly reliant on their digital infrastructure for continuity of operations.
Ransom Threats in the Drone and Autonomous Ecosystem
The rapid proliferation of drones and autonomous systems has introduced a new frontier for digital ransom. These technologies, vital for applications ranging from logistics and agriculture to surveillance and public safety, are inherently connected, relying on complex software, communication protocols, and cloud-based services. This interconnectedness, while enabling advanced capabilities, simultaneously expands the attack surface for cybercriminals seeking to exploit vulnerabilities for ransom.
Vulnerabilities in Connected Drone Systems
Drones, as Internet of Things (IoT) devices, present numerous points of entry for malicious actors. Their ecosystem includes not just the physical drone but also ground control stations (GCS), communication links (RF, cellular, satellite), cloud-based data storage and processing platforms, and the various sensors and payloads they carry. Each of these components can be a target:
- Firmware and Software Vulnerabilities: Exploitable flaws in the drone’s operating system, flight control software, or embedded applications can allow unauthorized access or the injection of malicious code.
- Communication Links: Interception or manipulation of command and control signals (e.g., GPS spoofing, signal jamming) can lead to loss of control, diversion, or even capture of the drone. Ransom could then be demanded for its safe return or release from compromised control.
- Ground Control Stations: GCS platforms, often running on standard operating systems, are susceptible to general PC malware, including ransomware, which could lock operators out of controlling their fleet.
- Cloud Services: Data collected by drones (high-resolution imagery, thermal scans, geospatial data) is often uploaded to cloud platforms for processing and storage. These platforms are attractive targets for data exfiltration and encryption, forming the basis for data ransom demands.
- Supply Chain Attacks: Vulnerabilities introduced at any stage of the drone’s manufacturing process, from hardware components to software libraries, can create backdoors or weaknesses that later facilitate ransomware deployment.
Operational Disruption and Data Exploitation
The impact of a successful ransom attack on a drone or autonomous system can be severe and multifaceted:
- Loss of Control: In a worst-case scenario, a drone could be “held captive” in mid-flight or on the ground, its control system locked out, until a ransom (e.g., a decryption key for its flight controller software, or access credentials) is paid. This could lead to mission failure, loss of expensive equipment, or even safety hazards if the drone falls out of the sky or deviates into restricted airspace.
- Data Ransom: Drones collect vast amounts of valuable data—everything from agricultural health metrics to critical infrastructure inspection data, and sensitive surveillance footage. If this data is encrypted by ransomware or exfiltrated and held hostage, the consequences can be dire. This could lead to significant financial losses due through operational downtime, intellectual property theft, competitive disadvantage, or regulatory fines for privacy breaches. For instance, a mapping company could lose access to years of proprietary geospatial data, crippling its business.
- Service Interruption: For organizations relying on drone fleets for services like package delivery, infrastructure monitoring, or emergency response, ransomware attacks targeting fleet management software, AI processing platforms, or critical data repositories could bring operations to a complete standstill. This “ransom” would be paid not for data, but for the restoration of essential operational capacity.
The Sophistication of Ransom Attacks and Their Vectors
Modern ransom attacks, particularly those targeting sophisticated technological ecosystems like drones, are characterized by their advanced nature, often leveraging a combination of technical exploits and human manipulation.
Advanced Persistent Threats and Social Engineering
Attackers frequently employ Advanced Persistent Threats (APTs), which involve stealthy and continuous computer hacking processes, often orchestrated by state-sponsored groups or highly organized cybercriminals. These groups may gain initial access through social engineering tactics, such as highly personalized phishing campaigns that trick drone operators, IT staff, or even executives into revealing credentials or installing malware. Once inside the network, they may dwell undetected for extended periods, mapping the system, escalating privileges, and identifying critical assets before deploying ransomware or initiating a more complex ransom scheme. The use of zero-day exploits (vulnerabilities unknown to software vendors) or sophisticated malware evasion techniques allows them to bypass traditional security measures. The complex supply chain of drone technology, involving multiple vendors for hardware, software, and services, provides numerous opportunities for attackers to find and exploit weaknesses, making it challenging to pinpoint the source of a compromise. The integration of AI and machine learning, while enhancing drone capabilities, also introduces new attack vectors and enables more intelligent, adaptive ransomware that can learn and overcome defenses.
Implications for Critical Infrastructure and Public Safety
The stakes for ransom attacks are significantly higher when they target drones and autonomous systems used in critical infrastructure or public safety. Drones are increasingly integrated into sectors like energy (power line inspection), transportation (logistics, traffic management), and emergency services (search and rescue, disaster assessment). A ransomware attack in these domains could:
- Disrupt Essential Services: Imagine a city’s drone-based infrastructure monitoring system being held for ransom, leading to undetected faults in power grids or water supply networks.
- Compromise National Security: Military or government drones could be hijacked, their data encrypted, or their missions incapacitated, posing serious national security risks.
- Endanger Public Safety: Drones used by law enforcement or fire departments could be rendered useless during critical operations, jeopardizing lives.
The decision of whether to pay a ransom in such scenarios becomes fraught with ethical dilemmas, balancing the immediate need to restore critical services against the long-term implications of funding criminal enterprises and potentially inviting future attacks.
Pioneering Resilience: Innovations in Ransom Mitigation
Addressing the evolving threat of digital ransom within the drone and autonomous ecosystem demands a proactive and multi-layered approach, driven by continuous innovation in cybersecurity. The mitigation strategies must encompass technological advancements, robust frameworks, and human preparedness.
Robust Cybersecurity Frameworks for UAVs
Effective defense against ransom attacks begins with designing and implementing strong cybersecurity frameworks specifically tailored for Unmanned Aerial Vehicles (UAVs) and their supporting infrastructure. This involves adopting principles like Zero Trust architecture, where no user, device, or application is implicitly trusted, regardless of its location relative to the network perimeter. All access requests are authenticated and authorized rigorously. End-to-end encryption is crucial for all data links—between the drone and ground control, within cloud storage, and for any sensitive data processed onboard—ensuring that even if data is intercepted, it remains unintelligible. Regular security audits, penetration testing, and vulnerability management processes are essential to proactively identify and remediate weaknesses in drone firmware, software, and communication protocols. Furthermore, implementing secure boot processes and tamper detection mechanisms can prevent unauthorized modification of a drone’s core operating system, ensuring its integrity from power-up.
AI-Powered Threat Detection and Autonomous Defense
The sheer volume and complexity of data generated by drone operations make manual threat detection impractical. This is where AI-powered solutions become indispensable. Machine learning algorithms can analyze flight patterns, communication signals, and data streams to detect anomalies that may indicate a compromise. For instance, deviations from standard flight paths, unusual data transmission volumes, or unexpected commands could trigger alerts. Predictive analytics can go a step further, identifying potential attack vectors and vulnerabilities before they are exploited, using historical data and threat intelligence. In cases of detected threats, automated response mechanisms can be designed to isolate compromised drone components, temporarily suspend operations, or even initiate secure data wipes of affected ground stations, minimizing the window of opportunity for attackers and limiting damage.
Blockchain and Decentralized Security Solutions
Emerging technologies like blockchain offer novel approaches to enhancing the security and integrity of drone operations, particularly against ransom threats. Blockchain’s distributed ledger technology can be used for immutable logging of flight data, command authentications, and firmware updates, creating an unalterable record that can prove the provenance and integrity of critical information. This can counteract data manipulation or falsification often associated with ransom attacks. Decentralized identity management for drones and operators can strengthen authentication and authorization processes, making it harder for unauthorized entities to assume control. Furthermore, smart contracts could enable secure, transparent payment systems for legitimate drone services, while hindering illicit ransom payments by making them traceable or tying them to verifiable conditions that cybercriminals cannot meet.
Human Element: Training and Awareness
Technological solutions alone are insufficient without addressing the human element, which often remains the weakest link in cybersecurity. Comprehensive training and awareness programs are crucial for all personnel involved in drone operations – from operators and developers to IT staff and management. These programs should educate individuals on identifying social engineering tactics (like phishing), adhering to cybersecurity best practices, and understanding the evolving nature of ransom threats. Developing detailed incident response plans specifically tailored to drone-related cyber incidents, including ransom scenarios, is equally vital. These plans outline clear steps for detection, containment, eradication, recovery, and post-incident analysis, ensuring a swift and effective response that minimizes downtime and data loss, ultimately building a resilient and secure autonomous ecosystem.