
The Foundational Mechanics of Digital Espionage
Keyloggers represent a potent and often insidious form of technology designed to record keystrokes made on a keyboard. At their core, these tools are about data interception, capturing every character typed by a user, from emails and documents to passwords and financial information. While the concept might seem straightforward, the underlying mechanics leverage various technological approaches, making keyloggers a significant area of focus within cybersecurity and a testament to the continuous innovation in data capture and surveillance technologies. Understanding their operational principles is crucial to appreciating both their threat and the defensive innovations developed to counter them.

Hardware Keyloggers: Physical Interception Innovations
Hardware keyloggers are physical devices inserted between a keyboard and a computer, or sometimes integrated directly into the keyboard’s circuitry. These innovative devices operate independently of the computer’s operating system, making them incredibly difficult to detect via conventional software means. Their ingenuity lies in their simplicity and stealth.
- Inline Devices: The most common form of hardware keylogger is a small, unobtrusive device that physically connects to the keyboard cable (USB or PS/2) and then to the computer’s port. These devices contain a microchip and memory, passively recording all data flowing from the keyboard to the computer. They draw power directly from the connection and require no software installation on the target machine. Innovation in this space has focused on miniaturization, increased storage capacity, and features like remote data retrieval via Bluetooth or Wi-Fi, turning a simple interceptor into a sophisticated wireless surveillance tool.
- Integrated Keyboards: Some keyloggers are built directly into the keyboard itself, appearing as a standard peripheral. This approach requires physical access to install a modified keyboard but offers complete invisibility once deployed. Advanced versions might even communicate logs wirelessly to a nearby receiver, bypassing the need for physical retrieval.
- Acoustic Keyloggers: While less common, acoustic keyloggers represent a fascinating intersection of signal processing and surveillance innovation. These systems analyze the unique sound signatures produced by different keys being pressed. By capturing keyboard sounds, often from a distance, and using sophisticated algorithms, they can reconstruct typed text. This method highlights an innovative, non-invasive approach to data capture that doesn’t rely on direct physical or software interaction.
Software Keyloggers: The Invisible Code
Software keyloggers are programs installed on a computer system, designed to run surreptitiously in the background. Unlike their hardware counterparts, these rely on exploiting the computer’s operating system and applications to capture data. Their innovation lies in their versatility, ability to propagate remotely, and sophisticated evasion techniques.
- API Hooking: Many software keyloggers function by “hooking” into the operating system’s application programming interfaces (APIs). When a user types, the keyboard driver sends data to various system APIs. A keylogger can intercept these calls before they reach their intended destination, logging the keystrokes. This method is highly effective because it captures data at a fundamental level of system interaction.
- Kernel-Level Keyloggers: These are among the most advanced and dangerous software keyloggers. They operate at the kernel level of the operating system, which is the core part of the OS. By running with the highest system privileges, they are extremely difficult to detect and remove. Innovation in this area often involves exploiting vulnerabilities in the OS kernel or employing rootkit techniques to hide their presence, making them a significant challenge for conventional security software.
- Hypervisor-Based Keyloggers: An even more sophisticated form involves creating a malicious hypervisor that runs beneath the operating system. This hypervisor can then monitor all activities, including keystrokes, of the “guest” OS. This type of keylogger represents a pinnacle of stealth technology, as it operates at a layer below the OS itself, making it virtually undetectable from within the compromised system.
- Form Grabbers: These keyloggers specifically target web forms. Instead of recording every keystroke, they capture the data entered into web forms before it is encrypted and sent over the internet. This is particularly effective for stealing login credentials, credit card numbers, and other sensitive information submitted through websites, even those using HTTPS.
The Evolving Landscape of Keylogger Technology
The evolution of keylogger technology mirrors the broader trajectory of digital innovation itself, marked by increasing sophistication, stealth, and integration with other malicious functionalities. What began as simple keystroke recorders has transformed into multi-faceted surveillance tools, continually adapting to new operating systems, security measures, and network architectures. This ongoing arms race between keylogger developers and cybersecurity innovators defines a critical frontier in digital defense.
From Simple Logging to Advanced Surveillance
Early keyloggers were relatively basic, often just writing captured keystrokes to a local file. Today, their capabilities extend far beyond mere text capture. Modern keyloggers are often components of larger malware suites, demonstrating significant innovation in their feature sets:
- Screenshot Capture: Many keyloggers now routinely capture screenshots at regular intervals or when specific events occur (e.g., a new window opens, a mouse click). This provides visual context to the keystrokes, helping attackers understand what the user was doing.
- Clipboard Monitoring: Data copied to the clipboard (Ctrl+C, Ctrl+V) is often sensitive. Advanced keyloggers monitor and log clipboard contents, capturing information not typed directly.
- Microphone and Webcam Recording: Some sophisticated keyloggers, especially those part of advanced persistent threats (APTs), can activate a device’s microphone and webcam, turning the compromised system into a remote listening and viewing post.
- File Activity Monitoring: Beyond keystrokes, these tools can track files opened, created, modified, or deleted, providing a comprehensive picture of a user’s digital activity.
- Network Activity Logging: Monitoring network connections, visited websites, and downloaded files adds another layer to the surveillance capabilities, painting a complete digital footprint.
Rootkit and Kernel-Level Keyloggers: Deep System Integration
The most formidable keyloggers are those that embed themselves deeply within a system, leveraging rootkit technologies or operating at the kernel level. Rootkits are collections of tools designed to obtain privileged access to a computer and conceal their presence. When combined with keylogging capabilities, they become exceptionally difficult to detect and remove.
- Kernel-Mode Rootkits: These operate within the kernel, the core of the operating system, making them virtually invisible to standard user-mode processes, including most antivirus software. They can intercept OS calls, manipulate system structures, and completely hide their files, processes, and network connections. The innovation here lies in the exploitation of low-level system vulnerabilities and the meticulous crafting of code that mimics legitimate system behavior.
- User-Mode Rootkits: While less potent than kernel-mode variants, user-mode rootkits still offer significant stealth. They typically hook into APIs used by legitimate applications, altering their behavior to hide malicious processes or files. These keyloggers are adept at masquerading as legitimate system processes or library files.
Cloud-Based and Remote Access Keyloggers
The advent of cloud computing and widespread internet connectivity has spurred innovation in how keylogger data is exfiltrated and managed.
- Remote Access and Exfiltration: Modern keyloggers rarely store all their data locally. Instead, they are designed to periodically transmit collected information to a remote server controlled by the attacker. This often occurs via encrypted connections, leveraging common protocols like HTTP, FTP, or even DNS queries to blend in with legitimate network traffic. This innovation allows attackers to maintain surveillance without needing direct physical access or even regular remote sessions.
- Cloud-Based Control Panels: Attackers can manage multiple compromised systems from a centralized, cloud-based control panel. This allows for efficient deployment, configuration updates, and data collection from a vast network of infected machines, highlighting the scalability and automation innovations in cybercrime tools.
Innovating Against the Invisible Threat: Detection and Prevention
The continuous evolution of keylogger technology necessitates equally innovative and robust detection and prevention strategies. Cybersecurity professionals and researchers are in a constant race to develop advanced countermeasures that can identify, block, and mitigate the threat posed by these sophisticated surveillance tools. This domain represents a significant area of technological innovation, focusing on multi-layered defenses that combine traditional security paradigms with cutting-edge analytical methods.
Technological Countermeasures: Antivirus and Endpoint Detection
Traditional antivirus (AV) software forms the first line of defense, but its effectiveness against advanced keyloggers relies on continuous innovation.
- Signature-Based Detection: AV programs maintain databases of known keylogger signatures (unique code patterns). This method is effective against established threats but struggles with new, polymorphic, or custom-built keyloggers that constantly alter their code to evade detection. Innovation here focuses on rapid signature updates and collective intelligence sharing.
- Heuristic Analysis: To combat unknown threats, AV software employs heuristic analysis, examining program behavior for suspicious activities commonly associated with keyloggers, such as attempts to inject code into other processes or monitor keyboard inputs at a low level. This proactive approach tries to identify malicious intent even without a known signature.
- Endpoint Detection and Response (EDR) Systems: EDR solutions represent a significant leap in endpoint security. They continuously monitor and collect data from endpoints (workstations, servers) to detect and investigate suspicious activities. EDR systems use machine learning and behavioral analytics to identify keylogger behavior that might bypass traditional AV, such as unusual API calls, process injection attempts, or unauthorized access to sensitive system resources. Their innovation lies in comprehensive visibility and automated response capabilities.
Behavioral Analysis and Anomaly Detection
Advanced keyloggers often mimic legitimate system processes, making them hard to spot. This challenge has driven innovation in behavioral analysis and anomaly detection.
- Machine Learning and AI: AI and machine learning algorithms are increasingly deployed to establish baselines of normal user and system behavior. Any deviation from this baseline—such as a new process attempting to monitor keyboard events or an application accessing network resources unusually—triggers an alert. This method is particularly effective against zero-day keyloggers (previously unknown threats) that lack signatures.
- Privilege Escalation Monitoring: Keyloggers, especially kernel-level ones, often require elevated privileges to operate stealthily. Monitoring for unauthorized attempts at privilege escalation or suspicious low-level system interactions can expose their presence.
- Network Traffic Analysis: Even the most sophisticated keyloggers need to exfiltrate data. Network monitoring tools can analyze outbound traffic for unusual patterns, encrypted data streams to unknown destinations, or traffic that deviates from expected application behavior, indicating a potential data breach.
User Awareness and Best Practices
While technological solutions are paramount, human awareness and adherence to best practices remain a critical, non-technical innovation in preventing keylogger infections.
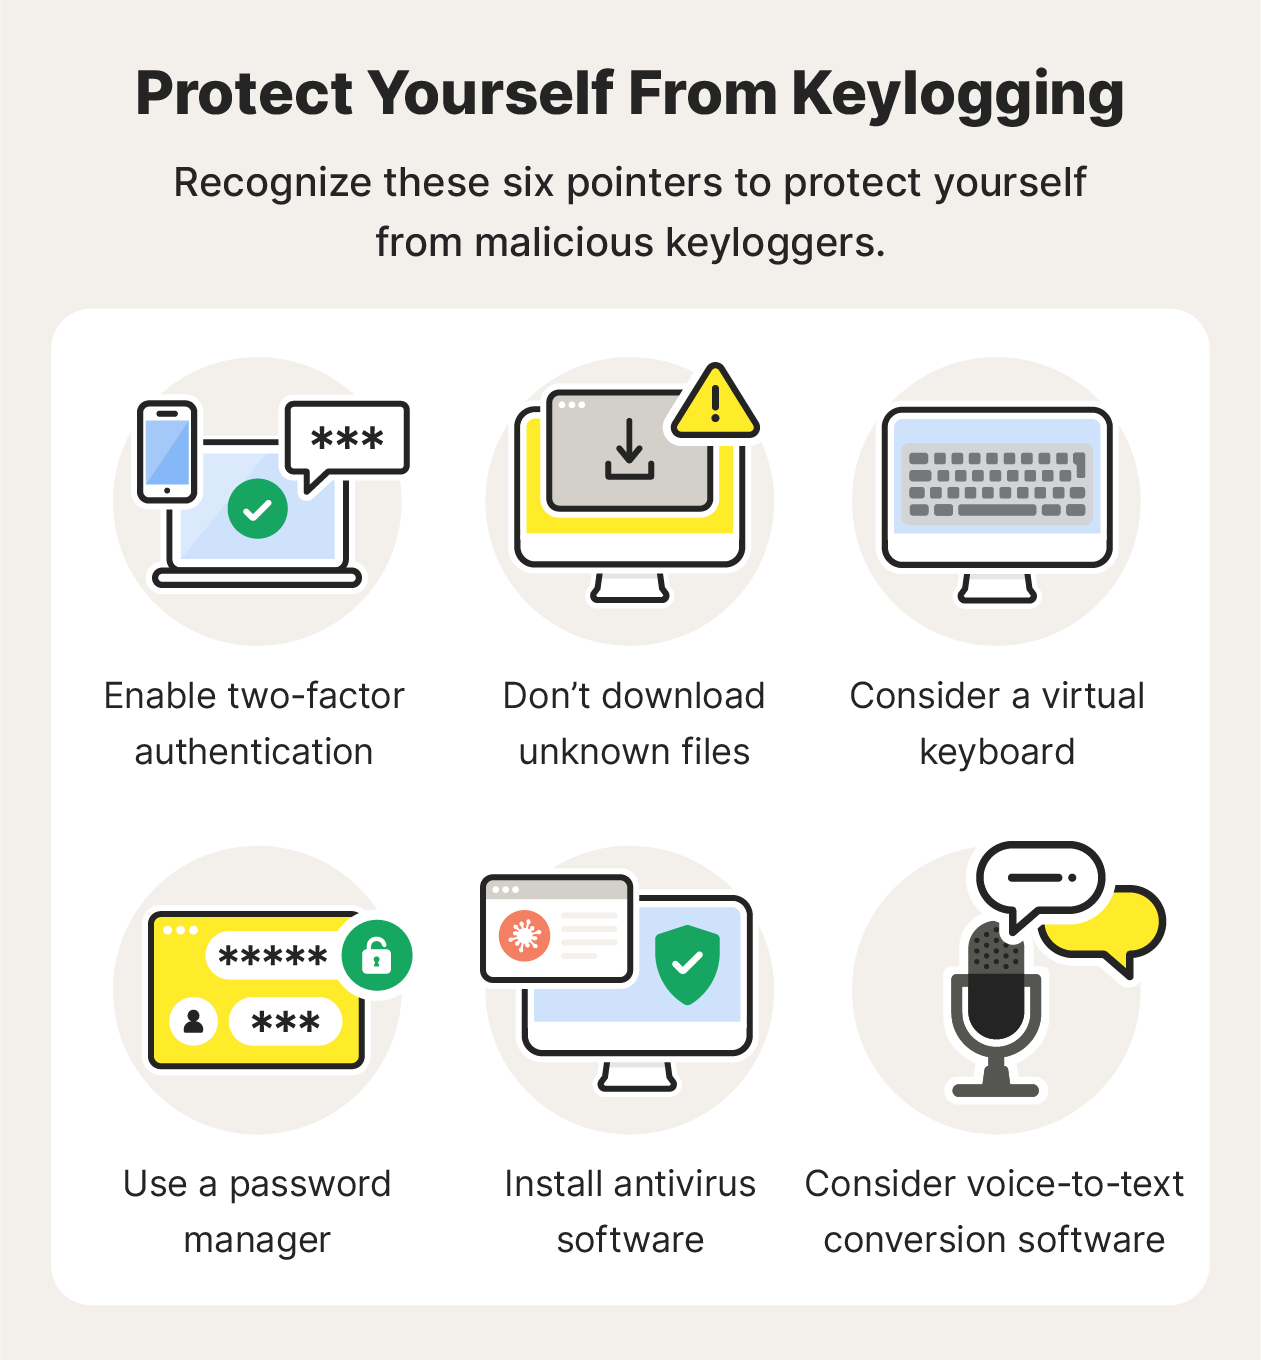
- Software Updates: Keeping operating systems, web browsers, and all software up-to-date is fundamental. Updates frequently patch security vulnerabilities that keyloggers might exploit for installation or privilege escalation.
- Strong Passwords and Multi-Factor Authentication (MFA): Even if a keylogger captures a password, MFA (e.g., using a one-time code from a phone) can prevent unauthorized access, adding an extra layer of security.
- Reputable Software and Downloads: Only downloading software from trusted sources and exercising caution with email attachments and suspicious links significantly reduces the risk of malware, including keyloggers.
- Disk Encryption: Encrypting the entire hard drive can protect stored data even if a hardware keylogger is physically installed and later retrieved, as the attacker would still need the decryption key.
- Virtual Keyboards: For highly sensitive inputs (like banking logins), using an on-screen virtual keyboard can sometimes bypass keyloggers that only record physical keystrokes, though sophisticated keyloggers can sometimes capture screen activity.
Keyloggers and the Future of Digital Trust
The existence and continuous evolution of keyloggers pose fundamental questions about digital trust and the future of online interactions. As technology becomes more intertwined with every aspect of life, the ability to discreetly record user inputs presents a significant threat to privacy, security, and the integrity of digital ecosystems. Addressing this challenge requires ongoing innovation in security technologies, policies, and user education.
Impact on Cybersecurity Innovation
The keylogger threat directly fuels innovation in cybersecurity. The constant cat-and-mouse game between attackers developing stealthier keyloggers and defenders creating more robust detection mechanisms drives advancements in:
- Threat Intelligence: Sharing information about new keylogger variants and attack vectors allows security vendors to update their defenses rapidly.
- Zero-Trust Architectures: These security models assume that no user, device, or application should be trusted by default, regardless of its location. This approach mitigates keylogger impact by requiring strict verification for every access attempt, even if credentials are compromised.
- Hardware-Assisted Security: Modern CPUs incorporate hardware-based security features (like Intel SGX or AMD SEV) that create secure enclaves for sensitive computations, protecting data from even kernel-level keyloggers. This represents a significant hardware innovation in preventing data interception.
- Post-Quantum Cryptography: As computational power grows, existing encryption methods could theoretically be broken, making keylogged data vulnerable. Research into post-quantum cryptography aims to develop new encryption algorithms resistant to quantum computer attacks, ensuring data privacy in the long term.
Regulatory and Ethical Considerations
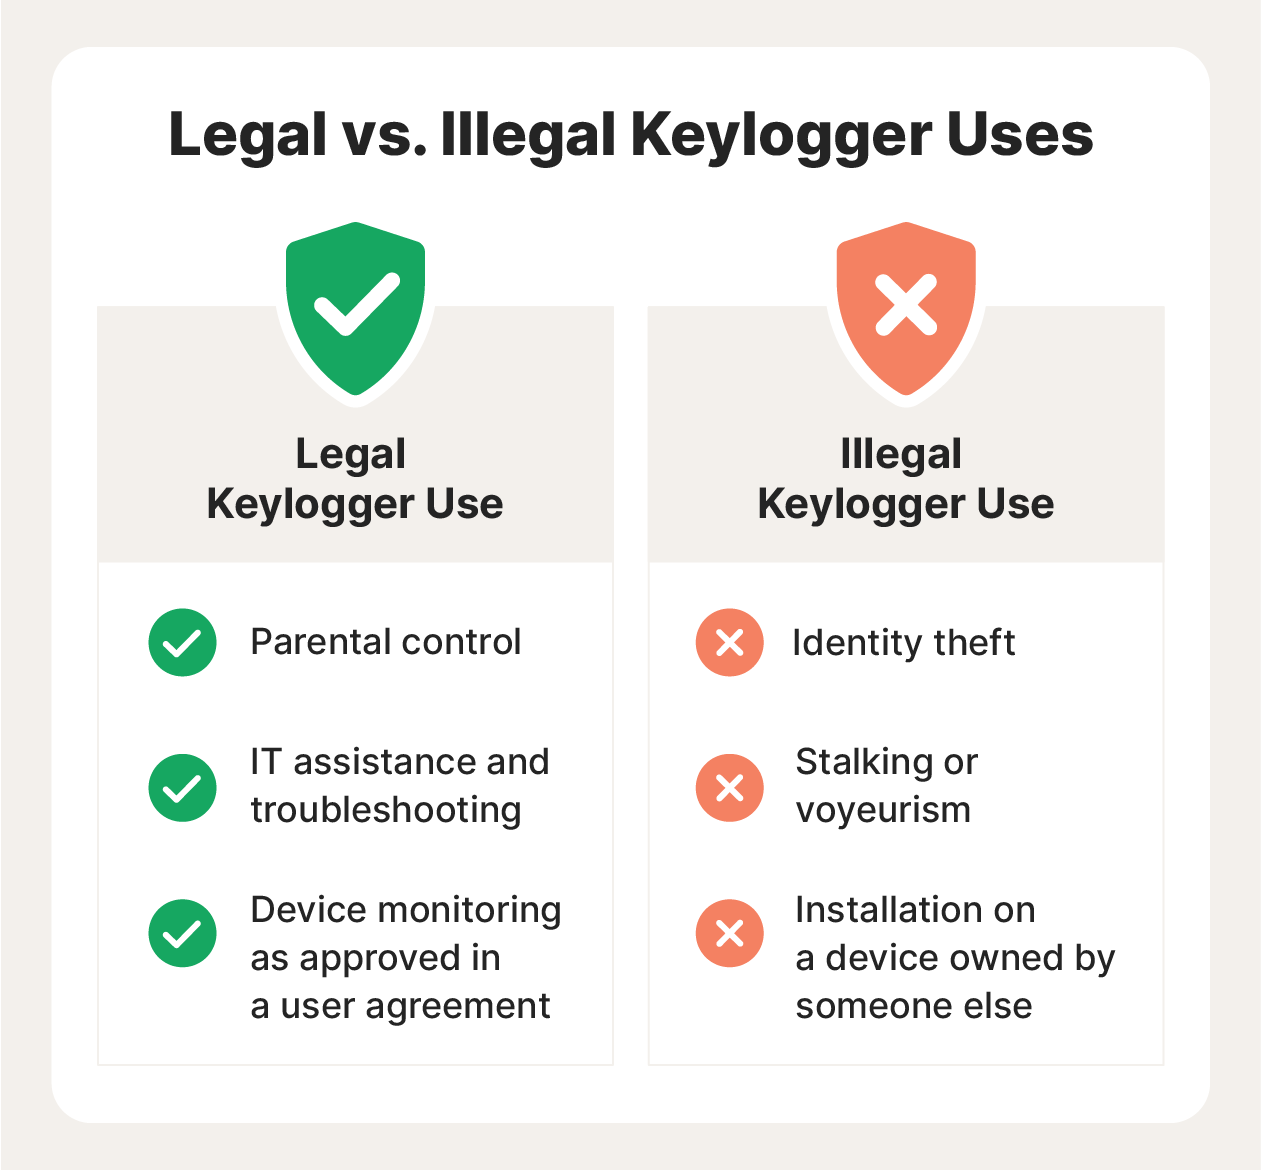
The deployment and use of keyloggers raise profound ethical and legal questions. While legitimate uses exist (e.g., parental monitoring, employee surveillance with explicit consent), their common misuse in cybercrime has led to increased regulatory scrutiny.
- Privacy Laws: Regulations like GDPR (General Data Protection Regulation) and CCPA (California Consumer Privacy Act) impose strict rules on data collection, storage, and processing, making unauthorized keylogging illegal and subject to severe penalties. These laws aim to restore user control over their digital footprint.
- Legitimate vs. Malicious Use: Distinguishing between legitimate (though ethically contentious) uses and purely malicious ones remains a challenge for law enforcement and technology providers. The development of “dual-use” technologies—tools that can be used for both benevolent and malevolent purposes—is a recurring theme in tech innovation.
- Ethical AI and Monitoring: As AI is increasingly used in surveillance and monitoring, there’s a growing need for ethical guidelines to ensure that advanced technologies are not weaponized against individual privacy.
In conclusion, keyloggers, in their various hardware and software manifestations, are sophisticated pieces of technology that continue to evolve. They represent a significant facet of the digital threat landscape, compelling constant innovation in detection, prevention, and the broader field of cybersecurity. Understanding “what are keyloggers” is not merely about recognizing a threat, but about appreciating the dynamic interplay of technological ingenuity, the ongoing battle for digital trust, and the societal implications of pervasive data surveillance.