
The Data Encryption Standard (DES) stands as a monumental landmark in the history of cybersecurity and information technology. Introduced in the mid-1970s, it represented a concerted effort to establish a standardized method for protecting digital information, fundamentally shaping how we approach data security in an increasingly interconnected world. While superseded by more robust algorithms today, understanding DES is crucial for appreciating the evolution of cryptographic techniques and the continuous race between code-makers and code-breakers in the realm of tech and innovation.
The Genesis and Purpose of DES
The need for a robust, publicly available encryption standard became acutely apparent in the early 1970s. As government agencies and businesses began to rely more heavily on computer systems for storing and transmitting sensitive data, the absence of a universal, strong encryption method posed a significant risk. Prior to DES, encryption practices were often proprietary, inconsistent, or not strong enough to withstand sophisticated attacks.
A Government-Led Initiative
In 1972, the U.S. National Bureau of Standards (NBS), now known as the National Institute of Standards and Technology (NIST), initiated a call for proposals for a national encryption standard. The goal was to develop an algorithm that was publicly known but cryptographically secure, allowing for widespread adoption while maintaining high levels of protection. After several rounds of submissions and evaluations, IBM’s Lucifer cipher, refined and strengthened in collaboration with the National Security Agency (NSA), was selected in 1976 and officially published as FIPS PUB 46, the Data Encryption Standard, in 1977.
The involvement of the NSA in modifying IBM’s original submission sparked considerable debate and controversy at the time. Concerns were raised regarding potential backdoors or deliberate weakening of the algorithm by the intelligence agency. However, subsequent independent analyses and the algorithm’s eventual public cracking did not confirm these fears, instead highlighting the complex interplay between security, transparency, and national interests in the development of critical technological standards. The standardization itself was a massive leap, allowing disparate systems to securely communicate for the first time using a common, well-vetted cryptographic method. This facilitated the growth of early digital commerce, secure government communications, and protected various forms of sensitive data.
Symmetric Key Cryptography Explained
At its core, DES is a symmetric-key block cipher. This means it uses the same secret key for both encrypting plaintext into ciphertext and decrypting ciphertext back into plaintext. This characteristic defines a broad class of cryptographic algorithms where the security relies entirely on keeping the single shared key confidential.
In a block cipher, the data is divided into fixed-size blocks, and the encryption algorithm processes one block at a time. For DES, the block size is 64 bits. This means every 64-bit segment of plaintext data is transformed into a 64-bit segment of ciphertext using the secret key. The key itself is 64 bits long, but only 56 of these bits are actively used in the encryption process; the remaining 8 bits are parity bits used for error checking. The principle of symmetric-key cryptography demands efficient key management and secure key distribution, as any compromise of the shared secret key renders all encrypted communications vulnerable. This fundamental design choice for DES underscored its practical application for scenarios where two parties could securely establish and maintain a shared secret.
How DES Works: The Feistel Cipher
DES employs a complex series of transformations based on a structure known as a Feistel network. This particular architecture is a critical feature, providing a robust and reversible method for scrambling data. The brilliance of the Feistel structure lies in its ability to build an invertible (reversible) cipher from non-invertible functions.
Key Components and Transformations
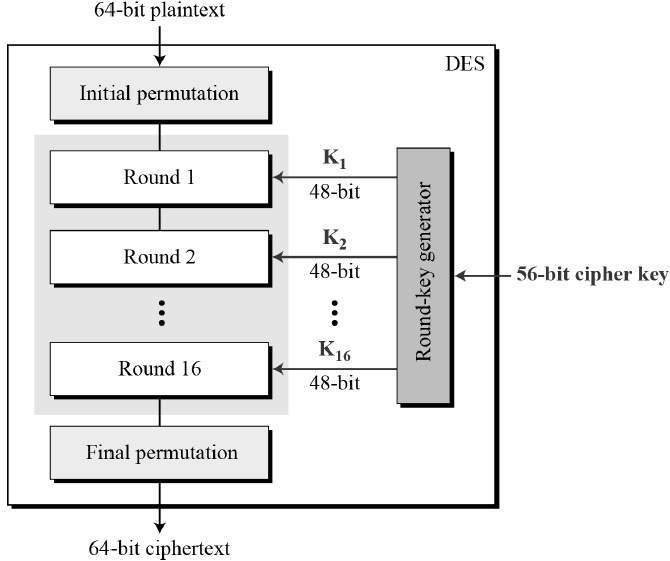
The encryption process in DES involves 16 identical rounds of operations. Each round mixes and permutes the data using a subkey derived from the main secret key. The 64-bit plaintext block undergoes an initial permutation (IP) to scramble the bits, after which it is divided into two 32-bit halves: a left half (L0) and a right half (R0).
In each of the 16 rounds, the following steps occur:
- Key Schedule: A 48-bit subkey (Ki) is generated from the 56-bit main secret key. The key schedule involves circular shifts and permutations of the main key to produce a unique subkey for each round.
- Feistel Function (f-function): The right half (Ri-1) is input into a complex function
f. Thisf-function expands the 32-bit right half to 48 bits, XORs it with the 48-bit subkey (Ki), passes the result through eight Substitution Boxes (S-boxes) which perform non-linear substitutions, and then permutes the 32-bit output of the S-boxes. Thisf-function is the core of the cipher’s complexity and its resistance to linear and differential cryptanalysis. - XOR and Swap: The output of the
f-function is then XORed with the left half (Li-1). This result becomes the new right half (Ri). The old right half (Ri-1) becomes the new left half (Li). Essentially, the output of thef-function, mixed with the current left half, replaces the left half, and the original right half is passed unchanged to become the next left half.
This process ensures that decryption can simply reverse the steps by applying the subkeys in reverse order. After 16 rounds, the left and right halves are swapped back (a final swap that undoes the initial split), and a final permutation (FP) is applied, which is the inverse of the initial permutation, to produce the 64-bit ciphertext.
The Iterative Nature of Encryption
The repetitive, iterative nature of the Feistel network, coupled with the complex S-box substitutions and the dynamic key schedule, creates a high degree of diffusion and confusion—two fundamental principles in cryptography. Diffusion spreads the influence of a single plaintext bit over many ciphertext bits, making statistical analysis difficult. Confusion obscures the relationship between the ciphertext and the encryption key, frustrating attempts to deduce the key from observed ciphertext. The design of DES, particularly the specific choices of S-boxes, was rigorously tested to ensure strong resistance against known cryptanalytic attacks at the time. This iterative processing of data blocks through a series of complex, key-dependent transformations cemented DES’s status as a formidable encryption standard for its era.
Strengths and Vulnerabilities of DES
Upon its release, DES was considered cutting-edge, offering a robust solution for securing digital communications. Its widespread adoption by financial institutions, governments, and corporations testified to its initial strength and reliability. However, like all cryptographic algorithms, DES was subject to continuous scrutiny and, eventually, the relentless march of technological progress.
Initial Robustness and Widespread Adoption
For over two decades, DES served as the de facto standard for secure data exchange. Its strength against known attacks in the 1970s and 80s was significant. The public specification allowed for peer review and implementation across diverse platforms, fostering interoperability and a baseline of trust in secure transactions. Financial transactions, especially ATM networks, relied heavily on DES. Its design, influenced by cryptographers at IBM and validated by the NSA, demonstrated a deep understanding of cryptographic principles that made it resilient to various forms of cryptanalysis available at the time, including differential cryptanalysis, which was independently discovered and kept secret by the NSA for years before being published.

The Key Length Conundrum
The primary vulnerability of DES was not in its algorithmic structure but in its key length. With a 56-bit effective key, there are 2^56 possible keys. While this number seemed astronomically large in 1977 (approximately 7.2 x 10^16), the rapid increase in computing power steadily eroded its security. A 56-bit key meant that, theoretically, an attacker could try every possible key until the correct one was found—a “brute-force” attack.
Brute-Force Attacks and Obsolescence
As early as the late 1980s and early 1990s, the feasibility of brute-force attacks against DES became a tangible concern. In 1997, RSA Security sponsored a contest that successfully broke a DES-encrypted message in 96 days using distributed computing. The following year, the Electronic Frontier Foundation (EFF) built a custom machine called “Deep Crack” for under $250,000, which cracked a DES key in just 56 hours. By 1999, Deep Crack, in collaboration with distributed.net, achieved the feat in under 24 hours.
These breakthroughs irrevocably demonstrated that DES’s 56-bit key was no longer sufficient to guarantee confidentiality against determined adversaries with access to significant computing resources. The algorithm itself remained mathematically sound in its design, but the limited key space rendered it vulnerable to exhaustive key search attacks, marking its transition from an unassailable standard to an increasingly obsolete technology for highly sensitive data.
The Transition to Triple DES (3DES) and Beyond
The evident vulnerability of single DES to brute-force attacks necessitated an evolution in encryption practices. Rather than immediately discarding the well-understood DES algorithm, an interim solution emerged: Triple DES (3DES), which effectively extended the lifespan of the underlying DES architecture.
Extending the Lifespan with 3DES
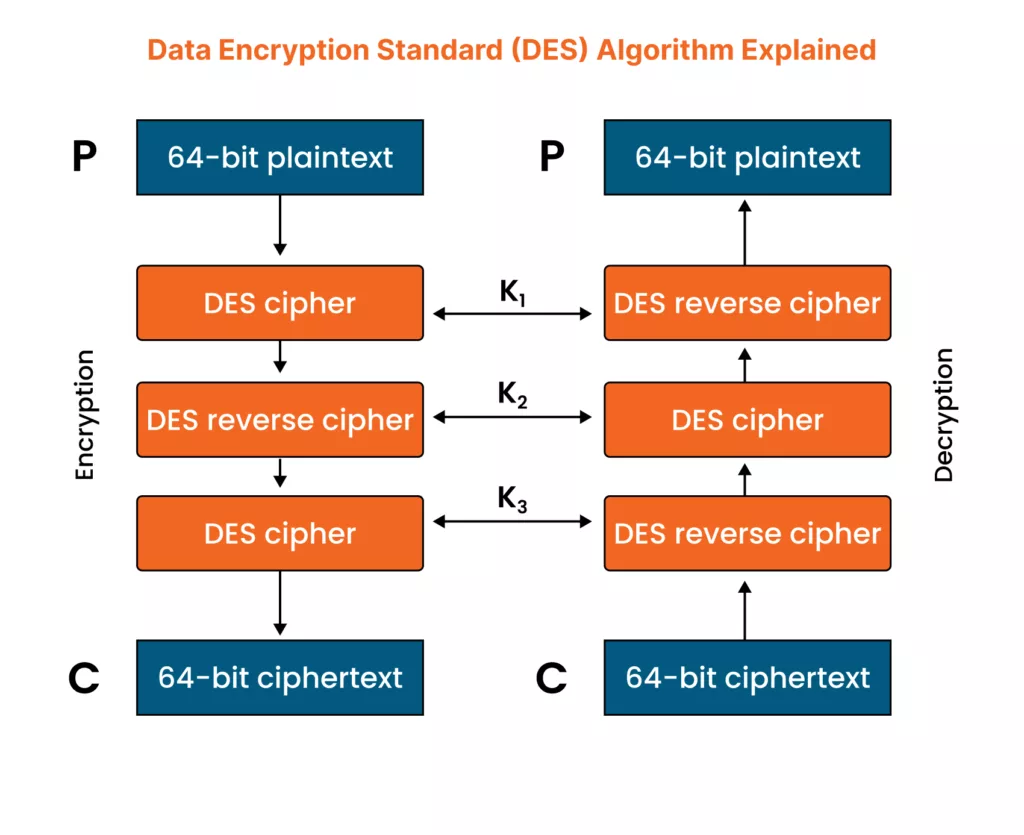
Triple DES, formally known as Triple Data Encryption Algorithm (TDEA), applies the DES algorithm three times to each data block. There are several modes of operation for 3DES, but the most common one, EDE (Encrypt-Decrypt-Encrypt), uses three different keys (K1, K2, K3) in sequence: Ciphertext = E_K3(D_K2(E_K1(Plaintext))).
The decryption process simply reverses these steps: Plaintext = D_K1(E_K2(D_K3(Ciphertext))).
The rationale behind using Encrypt-Decrypt-Encrypt rather than Encrypt-Encrypt-Encrypt was to allow backward compatibility with single DES if K1 = K2 = K3, where it would behave like single DES. More importantly, using three distinct keys (or two keys in some variants, where K1=K3 and K2 is different) effectively increases the key length to 112 bits (for two-key 3DES) or 168 bits (for three-key 3DES). This significantly enhances resistance to brute-force attacks and addresses certain meet-in-the-middle attacks that could potentially compromise simpler double-DES constructions.
3DES provided a much-needed increase in security during the transitional period of the late 1990s and early 2000s. It was widely adopted in financial services, particularly for EMV smart cards and payment systems, due to its proven track record and the considerable effort already invested in DES hardware implementations. However, 3DES is inherently slower than single DES due to its triple application of the algorithm, and its 64-bit block size started to become a limiting factor in efficiency and resistance to certain modern attacks, such as birthday attacks on block ciphers.
The Rise of Advanced Encryption Standard (AES)
Recognizing the limitations of 3DES, NIST initiated a new standardization process in 1997 to find a successor to DES. The goal was to select a new, stronger algorithm capable of securing data well into the 21st century. This led to a public competition, much like the one for DES, culminating in the selection of the Rijndael algorithm in 2001, which was then published as FIPS PUB 197, the Advanced Encryption Standard (AES).
AES offered several significant advantages over DES and 3DES:
- Larger Key Lengths: AES supports key lengths of 128, 192, or 256 bits, providing vastly greater security against brute-force attacks.
- Larger Block Size: AES uses a 128-bit block size, which improves efficiency and provides better security against certain types of attacks compared to DES’s 64-bit block.
- Speed and Efficiency: AES is considerably faster and more efficient in both hardware and software implementations compared to 3DES, making it suitable for a wider range of applications, from high-speed network communication to embedded systems.
- Different Structure: AES is not a Feistel cipher but a substitution-permutation network (SPN), offering a different set of cryptographic properties.
AES quickly became the global standard for symmetric-key encryption, adopted by governments worldwide and forming the backbone of modern secure communication protocols, file encryption, and secure storage solutions. While 3DES remains in use for legacy systems and specific applications where its performance overhead is acceptable or where existing hardware makes migration difficult, its use is steadily declining as AES offers superior security and efficiency.
The Enduring Legacy and Lessons Learned
Despite its eventual obsolescence, the Data Encryption Standard left an indelible mark on the landscape of information security. Its story is a testament to the dynamic nature of cybersecurity, where algorithms must continuously evolve to outpace the increasing capabilities of attackers.
Paving the Way for Modern Cryptography
DES was the first widely adopted public encryption standard. Its standardization created a common foundation for secure communication and provided a target for cryptanalysis, which, in turn, spurred significant academic and industry research into cryptographic design and attack methodologies. The public scrutiny and eventual cracking of DES were not failures of cryptography but rather crucial steps in its maturation. They demonstrated the critical importance of key length, the need for transparent evaluation of algorithms, and the necessity of anticipating future computational power.
The Feistel network structure, pioneered and popularized by DES, continues to influence the design of many modern block ciphers. The principles of diffusion and confusion, meticulously implemented in DES, remain central tenets of robust cipher design. Furthermore, the process by which DES was selected—a public competition leading to a government standard—set a precedent for future cryptographic standards like AES, ensuring broader community input and trust.
The Importance of Cryptographic Evolution
The journey from DES to 3DES to AES perfectly illustrates the fundamental principle of cryptographic evolution: security is not a static state but an ongoing process. What is considered secure today may not be secure tomorrow, given advancements in computing power, mathematical understanding, and cryptanalytic techniques. The lessons learned from DES emphasize the need for:
- Adequate Key Lengths: Always choose key lengths that can withstand foreseeable computing advancements.
- Robust Algorithmic Design: Algorithms must be designed to resist known and anticipated cryptanalytic attacks.
- Periodic Re-evaluation: Cryptographic standards must be regularly reviewed and updated or replaced when vulnerabilities emerge.
- Transparency and Peer Review: Openness in design and evaluation fosters trust and helps identify weaknesses.
The legacy of DES extends far beyond the algorithm itself. It laid the groundwork for the cryptographic infrastructure that underpins much of our digital world, from secure web browsing to protected financial transactions, and continues to inform the design and deployment of secure systems in all areas of tech and innovation, including the emerging challenges in drone technology, autonomous systems, and advanced imaging where data security is paramount. The debates and innovations surrounding DES highlight the continuous critical importance of cryptographic strength as a cornerstone of modern technological progress.