
In the rapidly evolving landscape of modern technology and innovation, the concept of cloud computing has become an indispensable backbone for businesses and developers alike. Within this expansive digital frontier, a particularly critical and foundational element for secure and scalable operations is the Virtual Private Cloud (VPC). Far more than just a buzzword, a VPC represents a powerful architectural design that merges the agility and cost-efficiency of public cloud infrastructure with the isolation and control typically associated with private networks.
At its core, a Virtual Private Cloud is an on-demand configurable pool of shared computing resources allocated within a public cloud environment, providing a logically isolated section where users can launch resources in a virtual network they define. Think of it as a dedicated, custom-built data center within a much larger, shared cloud facility. This isolation ensures that your resources, data, and network traffic remain completely separate and private from other customers’ traffic within the same public cloud provider. This fundamental principle of isolation, coupled with granular control over network configuration, makes VPCs a cornerstone for secure, scalable, and compliant cloud deployments across virtually every industry.
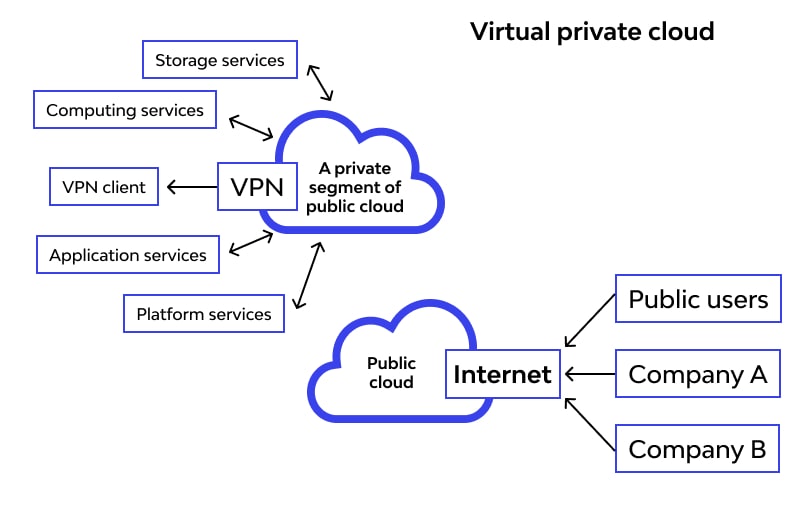
Key Characteristics and Components of a VPC
Understanding the core building blocks of a VPC is crucial to leveraging its full potential for technological innovation. These components work in concert to create a robust and customizable network environment tailored to specific application requirements.
Network Isolation and Segmentation
The defining characteristic of a VPC is its logical isolation. When you provision a VPC, you specify a private IP address range using Classless Inter-Domain Routing (CIDR) notation. This range is exclusive to your VPC and cannot be accessed or interfered with by other cloud users. Within this range, you can further segment your network into subnets. Subnets are logical partitions of your VPC’s IP address range, typically used to group resources based on security posture or function (e.g., web servers in a public subnet, database servers in a private subnet). Often, subnets are deployed across different availability zones within a region to enhance fault tolerance and high availability.
Routing and Connectivity
Route tables govern how network traffic flows within your VPC and how it connects to external networks. Each subnet must be associated with a route table that specifies rules for directing packets. For connecting to the internet, an Internet Gateway (IGW) is attached to the VPC, allowing resources in public subnets to communicate with the internet. For resources in private subnets that need outbound internet access (e.g., for software updates) but should not be directly accessible from the internet, a NAT Gateway or NAT instance is typically deployed. This provides Network Address Translation, allowing private resources to initiate outbound connections.
Security Mechanisms
VPCs offer multiple layers of security, providing fine-grained control over network traffic:
- Security Groups: These act as virtual firewalls for individual instances (e.g., virtual machines, containers). They are stateful, meaning if you allow outbound traffic, the corresponding inbound return traffic is automatically allowed. Security groups control both inbound and outbound traffic at the instance level.
- Network Access Control Lists (NACLs): NACLs are stateless firewalls at the subnet level. They control traffic in and out of subnets. Unlike security groups, NACLs are stateless, meaning you must explicitly allow both inbound and outbound rules for traffic to pass. This dual-layer approach provides robust security, ensuring only authorized traffic reaches your applications.
Private Network Connectivity
For hybrid cloud architectures or secure access to on-premises resources, VPCs offer dedicated connectivity solutions:
- VPN Gateway: A Virtual Private Network (VPN) Gateway allows you to establish a secure, encrypted connection between your VPC and your on-premises data center or corporate network over the public internet.
- Direct Connect (or similar dedicated connections like AWS Direct Connect, Azure ExpressRoute, Google Cloud Interconnect): For applications requiring high-bandwidth, low-latency, and consistent network performance, these services provide a dedicated private network connection from your premises directly to your cloud provider’s network, bypassing the public internet entirely.
The Transformative Power: Why VPCs are Essential for Modern Tech & Innovation
VPCs are not merely a networking construct; they are a strategic enabler for the most advanced technological innovations of our time. Their fundamental capabilities address critical needs for security, scalability, control, and efficiency, making them indispensable for modern IT architectures.
Enhanced Security and Compliance
One of the primary drivers for VPC adoption is security. By providing an isolated network segment, VPCs significantly reduce the attack surface. Organizations can implement multi-layered security controls, defining precise ingress and egress rules for every resource. This granular control is vital for meeting stringent regulatory compliance requirements (e.g., HIPAA, GDPR, PCI DSS) and protecting sensitive data from unauthorized access or breaches, which is paramount for tech companies handling personal, financial, or proprietary information.
Unprecedented Scalability and Flexibility
VPCs inherent elasticity mirrors the cloud’s on-demand nature. Resources within a VPC can be scaled up or down instantaneously to meet fluctuating demand, without the need for physical hardware procurement or complex network reconfigurations. This agility allows innovative startups and large enterprises to experiment, grow, and adapt rapidly, deploying new services and features with unparalleled speed. The ability to launch thousands of compute instances, containers, or serverless functions within a secure, predefined network environment empowers developers to focus on application logic rather than infrastructure constraints.
Full Control and Customization
Unlike shared network environments, a VPC gives you complete control over your virtual network topology. You dictate your IP address ranges, subnets, route tables, and security policies. This level of customization allows architects to design networks that perfectly align with application requirements, performance goals, and security postures. Whether deploying a complex microservices architecture, a high-performance computing cluster, or a secure data lake, the VPC provides the canvas for bespoke network solutions.
Facilitating Hybrid and Multi-Cloud Strategies
As organizations embrace hybrid and multi-cloud strategies, VPCs serve as the crucial bridge. They allow seamless integration between on-premises data centers and public cloud resources, enabling secure data exchange and workload migration. For multi-cloud approaches, distinct VPCs on different cloud providers can be interconnected, creating a unified and resilient global network infrastructure. This capability is vital for business continuity, disaster recovery, and avoiding vendor lock-in, all key considerations in forward-thinking technology strategies.

Cost-Effectiveness
While not immediately apparent, VPCs contribute to significant cost savings. By leveraging public cloud infrastructure, organizations eliminate the capital expenditure of building and maintaining physical data centers and networking hardware. The pay-as-you-go model for VPC components ensures that resources are allocated efficiently, optimizing operational expenses. The scalability reduces the need for over-provisioning, further driving down costs.
Enabling Advanced Technologies
Ultimately, the robust, secure, and flexible environment provided by VPCs forms the bedrock for deploying cutting-edge technologies. From machine learning model training and inference, big data analytics platforms handling petabytes of information, to complex IoT backend infrastructures and sophisticated microservices architectures, VPCs ensure that these demanding workloads have the secure, high-performance network they require to function effectively and innovate continuously.
Real-World Applications and Use Cases in Tech Innovation
The pervasive utility of Virtual Private Clouds underpins a vast array of modern technological advancements. Their ability to provide isolated, secure, and scalable network environments makes them the preferred choice for numerous innovative applications.
Hosting Secure SaaS Platforms
For Software-as-a-Service (SaaS) providers, a VPC is fundamental. Each customer’s environment, or even specific microservices within a multi-tenant application, can be isolated within dedicated subnets or separate VPCs. This ensures data segregation, prevents cross-tenant data leakage, and allows providers to meet stringent security and compliance requirements demanded by enterprise clients. This isolation is critical for maintaining trust and protecting sensitive user data.
Big Data Analytics and AI/ML Workloads
VPCs provide the ideal environment for processing and analyzing massive datasets and for deploying resource-intensive Artificial Intelligence and Machine Learning models. Data lakes, distributed processing frameworks (like Apache Spark), and ML training clusters can operate in private subnets, securely accessing sensitive data while leveraging the scalable compute power of the cloud. This isolation ensures that proprietary algorithms and confidential data remain protected throughout the entire data lifecycle.
IoT Backend Infrastructure
The Internet of Things (IoT) generates immense volumes of data from countless connected devices. A robust VPC architecture is essential for ingesting, processing, and storing this data securely and efficiently. VPCs can host IoT hubs, message queues, and data processing pipelines, ensuring that device telemetry is handled without bottlenecks and that the backend infrastructure remains resilient and secure against potential threats from the public internet.
E-commerce and Financial Services
Industries handling sensitive customer data and financial transactions, such as e-commerce and financial services, heavily rely on VPCs. The multi-layered security features, including security groups and NACLs, allow for strict control over network traffic to protect payment gateways, customer databases, and critical business applications. High availability and disaster recovery strategies, often spanning multiple VPCs in different regions, ensure continuous operation and data integrity, safeguarding against costly outages.
Disaster Recovery and Business Continuity
VPCs play a pivotal role in modern disaster recovery (DR) strategies. Organizations can configure secondary VPCs in different geographical regions to serve as recovery sites. Automated replication and failover mechanisms ensure that critical applications and data can be quickly restored or transitioned to the DR VPC in the event of a primary site failure, minimizing downtime and ensuring business continuity.
Remote Sensing and Geospatial Data Processing
In fields leveraging advanced remote sensing (e.g., satellite imagery, aerial surveys), VPCs offer a secure and scalable platform for managing and processing vast amounts of geospatial data. Researchers and analysts can deploy powerful compute instances and specialized databases within a VPC, applying complex algorithms, including AI/ML techniques for feature extraction, change detection, and environmental monitoring, all while ensuring the security and integrity of valuable earth observation data.
Navigating the VPC Landscape: Best Practices and Future Trends
Maximizing the benefits of a Virtual Private Cloud requires careful planning, adherence to best practices, and an eye towards future innovations. A well-architected VPC is a cornerstone of modern, resilient, and secure cloud operations.
VPC Design Considerations
Effective VPC design begins with meticulous IP address planning. Choosing non-overlapping CIDR blocks and planning for future growth is crucial to avoid complex network redesigns. Network segmentation using subnets to logically separate different tiers of an application (e.g., web, application, database) or different environments (dev, staging, prod) enhances security and simplifies traffic management. For high availability, designing your VPC to span multiple availability zones ensures that your applications remain operational even if one zone experiences an outage.
Security Best Practices
Security within a VPC is an ongoing process. Adhering to the principle of least privilege for security groups and NACLs is paramount – only allow necessary traffic. Regular security audits and vulnerability scanning of resources within the VPC are essential. Implementing comprehensive logging and monitoring solutions, such as VPC Flow Logs, provides invaluable insights into network traffic patterns, aiding in threat detection, troubleshooting, and compliance auditing. Integrating intrusion detection/prevention systems (IDS/IPS) adds another layer of defense.
Management and Automation
Modern VPC management heavily relies on Infrastructure as Code (IaC). Tools like Terraform or cloud-native solutions such as AWS CloudFormation or Azure Resource Manager allow you to define your VPC architecture and all its components in code. This enables consistent, repeatable, and version-controlled deployments, reducing human error and accelerating provisioning. Automating network configuration changes and security policy updates ensures agility and compliance across dynamic environments.

Future Trends
The evolution of VPCs continues to align with broader cloud computing trends. Enhanced integration with serverless architectures is becoming increasingly sophisticated, allowing serverless functions to securely access resources within a private VPC environment. The rise of edge computing means VPCs will increasingly extend their reach closer to data sources, providing low-latency processing capabilities for IoT and real-time applications. We can also anticipate further advancements in managed network services, including AI-driven anomaly detection within the VPC, and more robust multi-cloud and hybrid cloud mesh solutions that abstract network complexity across disparate environments, creating a truly unified global network for the next generation of technological innovation.