
In the vast landscape of modern technology and innovation, the ability to securely connect to and manage remote systems is not merely a convenience but an absolute necessity. From the intricate networks powering global enterprises to the distributed sensors gathering environmental data, and the burgeoning infrastructure for autonomous systems, secure communication protocols form the bedrock of operational integrity and data privacy. Among these, the Secure Shell (SSH) protocol stands out as an indispensable tool, a cryptographic network protocol that enables secure data communication between two networked devices. More than just a remote login utility, SSH is a cornerstone of tech and innovation, facilitating secure operations across countless domains.
The Foundational Protocol for Secure Remote Operations
At its core, SSH provides a secure channel over an unsecured network by utilizing strong encryption. Developed as a replacement for less secure protocols like Telnet, rsh, and rlogin, which transmit information, including passwords, in plaintext, SSH revolutionized the way system administrators, developers, and automated systems interact with remote machines. Its primary purpose is to allow command-line access to a remote computer, enabling users to execute commands, transfer files, and manage services as if they were physically present at the console.
The innovation of SSH lies in its ability to encapsulate any network service within an encrypted tunnel, protecting data from eavesdropping, connection hijacking, and other cyber threats. This capability extends beyond simple remote logins, allowing it to secure a myriad of applications and services. In an era where data breaches are rampant and cybersecurity threats are constantly evolving, SSH’s robust security mechanisms make it an essential component of any tech infrastructure, underpinning everything from cloud computing to the secure management of remote sensing platforms and autonomous robotics. It’s the silent guardian ensuring that the innovations we deploy are not vulnerable targets.
The Problem SSH Solved: A Paradigm Shift in Security
Before SSH, managing remote servers or accessing networked devices often involved protocols that lacked encryption. This meant that sensitive data, including login credentials, commands, and output, traversed the network in an easily readable format. A malicious actor could intercept this traffic using simple sniffing tools, gaining unauthorized access or critical information. This inherent vulnerability posed significant risks, especially as networks grew larger and more interconnected.
SSH emerged in the mid-1990s to directly address these glaring security deficiencies. By integrating robust cryptographic techniques, it transformed insecure network channels into secure ones, fundamentally changing the paradigm of remote access. This innovation was not just an incremental improvement; it was a fundamental shift that enabled the secure global connectivity we now take for granted, paving the way for distributed systems, remote development, and the secure operation of critical infrastructure. Without such a foundational shift, many modern technological advancements would be impractical or dangerously exposed.
How SSH Works: A Deep Dive into Cryptographic Security
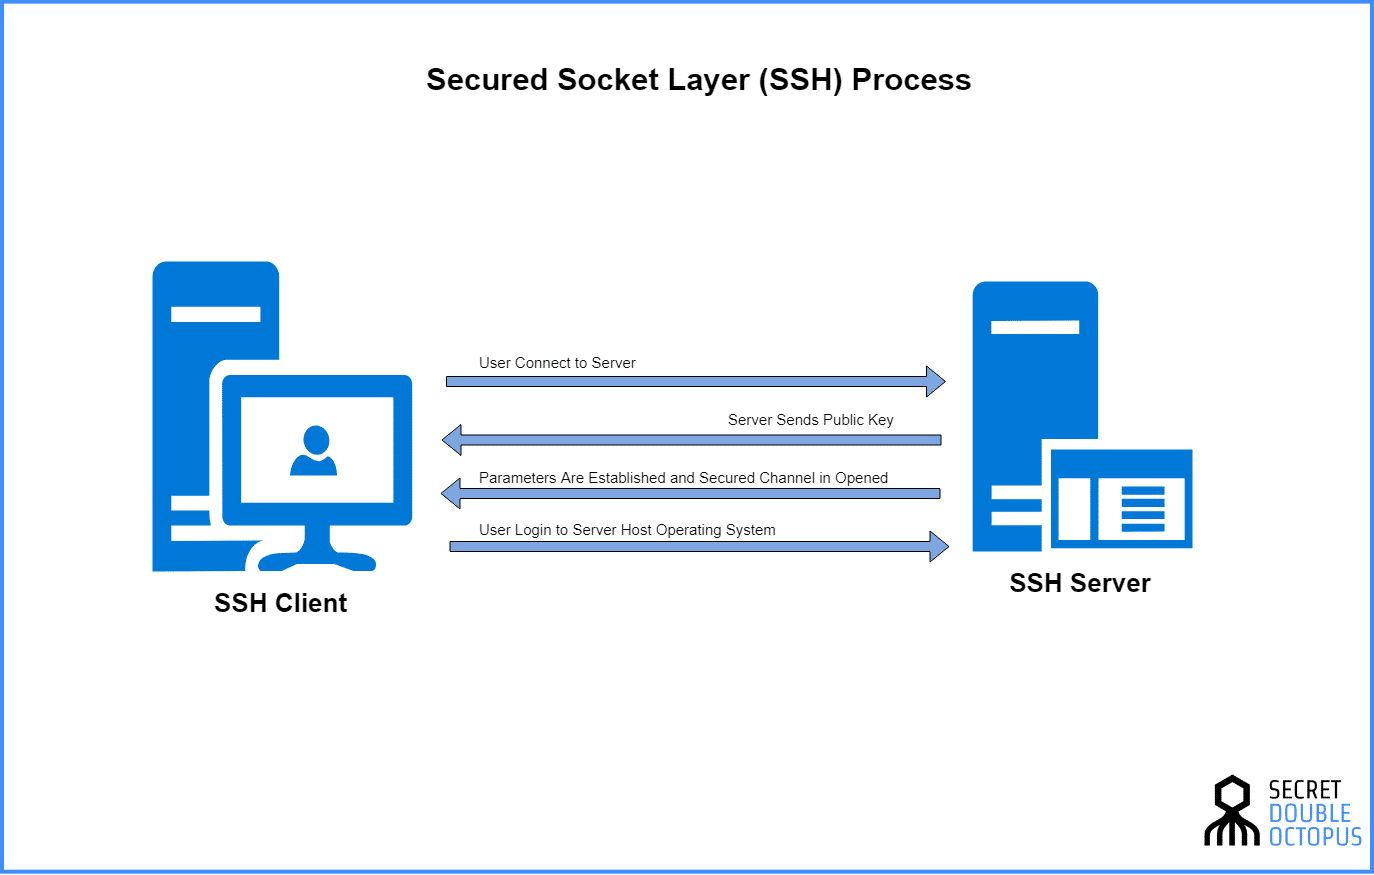
The effectiveness of SSH stems from its sophisticated architecture and the cryptographic principles it employs. It operates on a client-server model, where an SSH client connects to an SSH server running on the remote machine. This connection is established through a series of cryptographic handshakes that ensure both confidentiality and integrity of data.
Authentication Mechanisms: Proving Identity Securely
One of the most critical aspects of SSH is its powerful authentication capabilities, which prevent unauthorized access. SSH supports several authentication methods, each designed to provide a high level of security:
Password Authentication
This is the most common and often the simplest form of authentication, where the user provides a username and password to log in. While encrypted during transmission, password-based authentication is vulnerable to brute-force attacks if weak passwords are used. Thus, it is generally recommended for scenarios with strong password policies or as a fallback.
Public Key Authentication
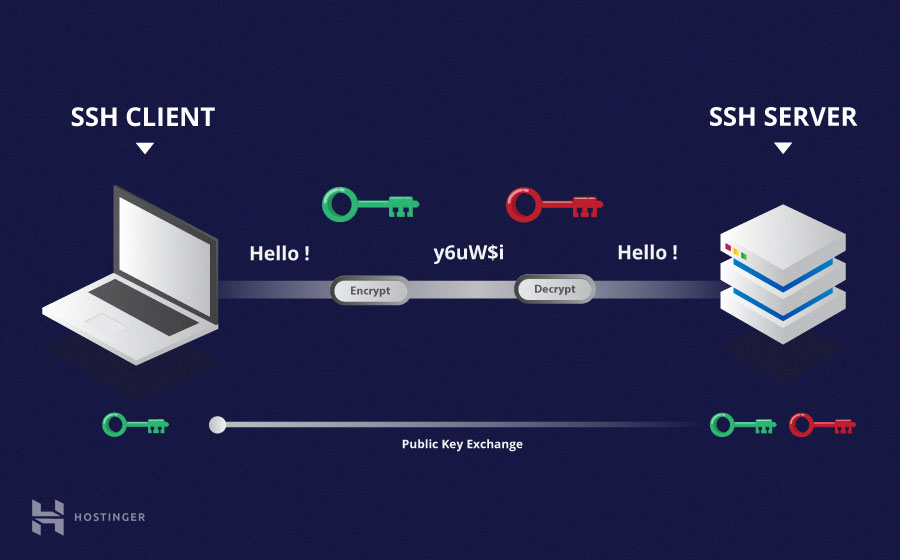
Considered the most secure and widely recommended method, public key authentication eliminates the need for passwords entirely. It relies on a pair of cryptographic keys: a public key and a private key. The public key is stored on the remote server, while the private key remains securely on the user’s local machine. When a client attempts to connect, the server uses the public key to challenge the client, and the client proves its identity by successfully responding to the challenge using its private key. This method not only enhances security by removing password vulnerabilities but also streamlines automated processes, making it ideal for scripting and secure machine-to-machine communication in innovative tech environments like cloud orchestrations or IoT device management.
Encryption and Data Integrity: Protecting the Payload
Once authentication is successful, SSH establishes an encrypted tunnel. This involves several cryptographic algorithms working in concert:
Symmetric Encryption
For the bulk of data transfer, SSH uses symmetric encryption algorithms (e.g., AES, ChaCha20). These algorithms use a single, shared key to encrypt and decrypt data. A new session key is generated for each SSH session using a key exchange algorithm, ensuring that even if one session’s key is compromised, it won’t affect past or future sessions. This provides high performance while maintaining strong confidentiality.
Asymmetric Encryption
Beyond public key authentication, asymmetric encryption (e.g., RSA, ECC) is also used during the initial key exchange process. The client and server use each other’s public keys to securely agree upon a shared symmetric session key without ever transmitting the key itself over the insecure network. This ensures that the symmetric key, which encrypts the actual data, remains secret from any eavesdropper.
Hashing and Message Authentication Codes (MACs)
To ensure data integrity, SSH employs hashing functions and Message Authentication Codes (MACs). These mechanisms verify that the data transmitted has not been altered or tampered with during transit. Each packet sent through the SSH tunnel includes a MAC, which is a cryptographic checksum. If even a single bit of the packet is changed, the MAC will no longer match, alerting the receiving end to potential tampering.
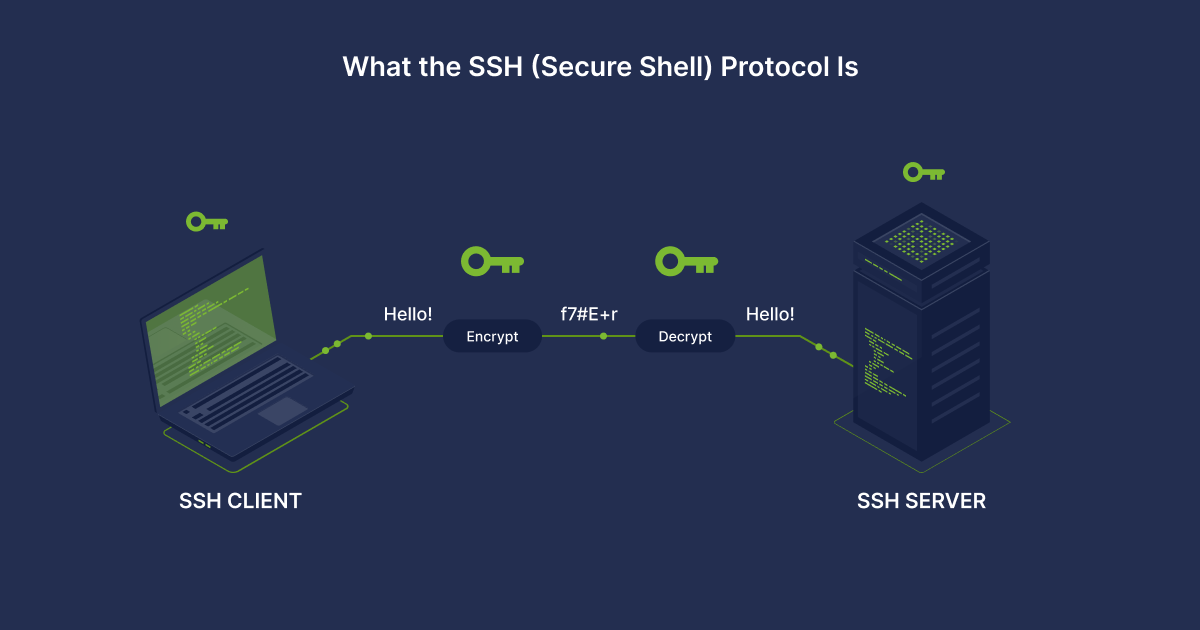
These layers of cryptographic protection create a robust and resilient communication channel, making SSH an unparalleled protocol for securing remote access and data transfer in any technologically advanced system.
Beyond Remote Login: Diverse Applications in Modern Tech
While remote command-line access is SSH’s most well-known function, its architecture allows for a much broader range of applications, many of which are fundamental to contemporary tech and innovation:
Secure File Transfer: SCP and SFTP
SSH forms the basis for two secure file transfer protocols:
- Secure Copy Protocol (SCP): A simpler protocol primarily used for transferring files between a local host and a remote host, or between two remote hosts, with the security of SSH. It’s ideal for quick, script-based file movements.
- SSH File Transfer Protocol (SFTP): A more feature-rich protocol that offers full file system management capabilities over an SSH channel. SFTP allows for listing directories, deleting files, resuming transfers, and more, making it a powerful tool for managing data on remote servers securely. This is crucial for environments like remote sensing platforms where large datasets need to be regularly uploaded or downloaded securely.
Port Forwarding (SSH Tunneling): Securing Insecure Services
One of SSH’s most powerful and versatile features is port forwarding, also known as SSH tunneling. This allows users to create encrypted tunnels between local and remote ports, effectively securing any TCP/IP traffic that flows through it. This capability has profound implications for securing otherwise insecure services:
Local Port Forwarding
This allows users to access a service on a remote server as if it were running on their local machine. For example, one could securely access a remote database or web interface that is only listening on localhost, by forwarding a local port to the remote service’s port through the SSH tunnel. This is invaluable for developers and system administrators working with internal-only services or securing access to web interfaces for IoT devices.
Remote Port Forwarding
This enables a remote server to access a service on the local client machine, or on another machine accessible from the client. This is particularly useful for establishing reverse connections, such as allowing a remote operations center to securely connect to a field-deployed sensor network that is behind a firewall and cannot initiate outbound connections directly.
Dynamic Port Forwarding (SOCKS Proxy)
Dynamic port forwarding creates a SOCKS proxy, allowing a client to create a secure tunnel for various applications through a single port. This means that a user can configure their web browser or other applications to route all their traffic through the SSH tunnel, effectively anonymizing and securing their internet browsing from a public Wi-Fi network or accessing services that are geo-restricted. This innovative use turns SSH into a powerful tool for network privacy and access.
SSH in Modern Tech Ecosystems: Cloud, IoT, and Autonomous Systems
The impact of SSH extends deeply into the fabric of modern technological innovation:
- Cloud Computing: SSH is the primary mechanism for managing virtual machines and containers in cloud environments (AWS EC2, Google Cloud, Azure). Developers and operations teams use SSH for deployment, troubleshooting, and maintenance, leveraging its security for critical infrastructure.
- Internet of Things (IoT): Securing edge devices and gateways in IoT deployments is paramount. SSH provides a secure way to remotely configure, update, and manage IoT devices, ensuring that sensitive data and control commands remain protected from compromise. This is vital for smart cities, industrial IoT, and home automation systems.
- Remote Sensing and Autonomous Systems: For drones, autonomous vehicles, and remote scientific instruments, SSH offers a reliable and secure channel for data offloading, command and control, and firmware updates. Imagine a remote scientific probe in an extreme environment needing a software patch; SSH enables this operation securely from a continent away. The ability to push updates or pull telemetry securely is a cornerstone of operational resilience for these advanced systems.
- DevOps and Automation: In the DevOps pipeline, SSH keys are extensively used for automated deployments, continuous integration/continuous delivery (CI/CD) processes, and secure communication between various build and deployment servers. This machine-to-machine authentication is critical for efficient and secure automation.
Implementing and Securing SSH: Best Practices
To maximize the benefits and security of SSH, several best practices are essential:
- Always Use Public Key Authentication: Prioritize public key authentication over password authentication. Generate strong, unique key pairs for each system and user.
- Secure Private Keys: Private keys must be protected with strong passphrases and never shared. Store them in secure locations, ideally hardware security modules (HSMs).
- Disable Password Authentication (if possible): On servers where public key authentication is fully implemented, disable password authentication in the SSH server configuration (
sshd_config) to eliminate a common attack vector. - Change Default SSH Port: While not a security measure against sophisticated attacks, changing the default SSH port (22) to a non-standard port can reduce the volume of automated scanning and brute-force attempts from bots.
- Regularly Update SSH Software: Keep SSH client and server software updated to patch known vulnerabilities and benefit from performance improvements and new features.
- Implement Firewall Rules: Restrict SSH access to only trusted IP addresses or networks using firewall rules.
- Use Strong Ciphers and MACs: Configure the SSH server to use modern, strong cryptographic algorithms for encryption and integrity checking.
- Monitor SSH Logs: Regularly review SSH server logs for unusual activity, failed login attempts, or unauthorized access attempts.
The Future of Secure Remote Access
SSH has proven its resilience and adaptability for decades, evolving with the demands of an ever-changing technological landscape. Its foundational principles of strong encryption and robust authentication remain critically relevant. As new paradigms emerge – from quantum computing to increasingly complex distributed ledger technologies – the core need for secure, verifiable communication channels will only intensify.
While new protocols and enhancements will undoubtedly emerge, SSH will likely continue to serve as a critical component, either directly or as an underlying inspiration for future secure access solutions. Its flexibility, open-source nature, and widespread adoption cement its place as a quintessential technology and innovation enabler, ensuring that as systems become more autonomous and interconnected, they remain securely managed and protected.