In the rapidly accelerating world of technology and innovation, where digital transformation is no longer an aspiration but a fundamental necessity, the concept of Identity and Access Management (IAM) stands as a critical, often invisible, cornerstone. IAM is far more than just a security measure; it is an intricate framework of policies, processes, and technologies designed to ensure that the right individuals and entities have the appropriate access to the right resources, at the right time, and for the right reasons. In an era defined by cloud computing, artificial intelligence, IoT, and an increasingly remote workforce, understanding and implementing robust IAM strategies is paramount for any organization striving for innovation, security, and operational excellence.
The Foundational Pillar of Modern Cybersecurity
At its core, IAM addresses two fundamental questions: “Who are you?” and “What are you allowed to do?” By providing verifiable answers to these questions, IAM systems create a secure digital perimeter, protecting sensitive data, systems, and applications from unauthorized access and potential breaches. It’s the gatekeeper, the bouncer, and the records manager all rolled into one, tirelessly working to authenticate identities and enforce access policies across an organization’s entire digital landscape.
Defining Identity: Who Are You, Really?
In the digital realm, an “identity” refers to a unique digital representation of a user, device, or application that requires access to an organization’s systems or resources. This could be an employee, a contractor, a customer, a partner, a server, a sensor, or even an AI model. Each identity carries attributes that define it—like a name, email, employee ID, department, or device serial number. The IAM system’s first task is to establish and verify this identity, often through a process known as authentication. Without a robust method for identity verification, the entire security infrastructure is compromised.
Defining Access: What Can You Do?
Once an identity is authenticated, the next crucial step is determining what resources that identity is permitted to access and what actions it can perform within those resources. This is known as authorization. Access can be granular, specifying permissions down to reading a specific file, executing a particular function within an application, or accessing a certain network segment. The principle here is least privilege—granting only the minimum access necessary for an identity to perform its designated functions, thereby minimizing the attack surface and potential damage from a compromised account.
The Core Principles of IAM
Effective IAM is built upon several core principles that guide its design and implementation:
- Authentication: Verifying the identity of a user or system. This involves mechanisms like passwords, multi-factor authentication (MFA), biometric scans, or digital certificates.
- Authorization: Granting or denying access to specific resources based on the authenticated identity’s privileges.
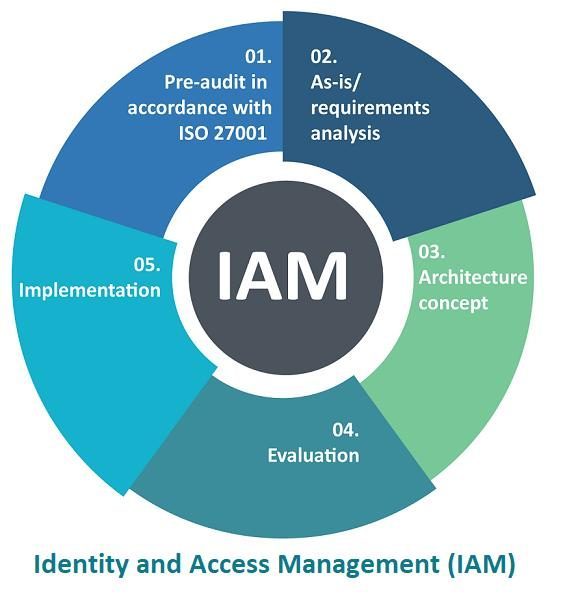
- Administration: Managing the entire lifecycle of identities and their access rights, from creation and provisioning to modification and de-provisioning.
- Auditing and Reporting: Maintaining detailed logs of access attempts and activities to ensure compliance, detect anomalies, and facilitate forensic analysis in case of a security incident.
These principles form a continuous cycle, ensuring that identities are consistently managed, access is appropriately controlled, and accountability is maintained throughout the digital ecosystem.
IAM in the Evolving Landscape of Tech & Innovation
The role of IAM has become increasingly critical as technological innovation drives organizations towards more complex, distributed, and interconnected environments. From securing cloud infrastructure to enabling cutting-edge AI deployments, IAM is the invisible force making these advancements possible and safe.
Securing Cloud Environments and Distributed Systems
The widespread adoption of cloud computing (IaaS, PaaS, SaaS) has fundamentally reshaped IT infrastructure. Resources are no longer confined to on-premise data centers but are distributed across various cloud providers. This distributed nature introduces significant challenges for traditional perimeter-based security. IAM becomes the new perimeter, extending its reach across hybrid and multi-cloud environments. It’s responsible for managing access to cloud consoles, APIs, storage buckets, virtual machines, and countless other cloud services, often requiring integration with various cloud-native IAM solutions (like AWS IAM, Azure AD, Google Cloud IAM). Effective cloud IAM ensures consistent policy enforcement, scalability, and agility without compromising security.
Enabling AI, Machine Learning, and Automation
Artificial intelligence and machine learning initiatives rely heavily on vast datasets and powerful computational resources. IAM plays a crucial role in securing access to these critical assets. It ensures that only authorized AI models can access specific training data, that ML engineers have the correct permissions to deploy and manage models, and that automated processes operate within predefined boundaries. As AI systems become more autonomous, their own “identities” and access rights must be carefully managed to prevent misuse or unintended actions. Furthermore, IAM enables the secure integration of AI-powered automation tools into existing workflows, ensuring they operate with appropriate privileges.
The Role of IAM in IoT and Edge Computing
The proliferation of Internet of Things (IoT) devices—from smart sensors in manufacturing plants to drones collecting aerial data—and the rise of edge computing present a new frontier for IAM. Each IoT device or edge node represents a potential identity that needs to be authenticated and authorized to communicate, collect data, or execute commands. Managing thousands or millions of diverse device identities, often with limited processing power and varying security capabilities, requires specialized IAM approaches. This includes device onboarding, secure credential management, continuous authentication, and granular access control for device-to-device and device-to-cloud communications, all critical for the secure operation of advanced monitoring, autonomous systems, and remote sensing technologies.
Key Components and Technologies of IAM
A comprehensive IAM solution is not a single product but an integrated suite of technologies designed to work synergistically. These components address different aspects of identity and access management.
Centralized Identity Repositories
At the heart of any IAM system is a centralized repository that stores all identity information. This can be a directory service like LDAP (Lightweight Directory Access Protocol), Microsoft Active Directory, or a cloud-native identity provider. These repositories serve as the authoritative source for identity attributes and are crucial for consistent identity management across an organization.
Authentication Methods: Beyond Passwords
While passwords remain common, modern IAM emphasizes stronger, more resilient authentication methods.
- Multi-Factor Authentication (MFA): Requires users to provide two or more verification factors (e.g., something you know like a password, something you have like a phone, something you are like a fingerprint).
- Biometrics: Using unique physical characteristics (fingerprints, facial recognition) for identity verification.
- Certificate-Based Authentication: Leveraging digital certificates to establish trust.
- Passwordless Authentication: Emerging methods that eliminate passwords entirely, relying on biometrics, FIDO2 security keys, or magic links.
Authorization and Role-Based Access Control (RBAC)
Authorization systems determine what an authenticated identity can do. Role-Based Access Control (RBAC) is a widely adopted method where permissions are assigned to specific roles (e.g., “Engineer,” “Accountant,” “Administrator”), and users are assigned to these roles. This simplifies management, as changing permissions for a role automatically updates all users assigned to it. Attribute-Based Access Control (ABAC) offers even finer granularity, allowing access decisions based on a combination of user attributes, resource attributes, and environmental conditions.
Single Sign-On (SSO) and Federation
Single Sign-On (SSO) allows users to authenticate once and gain access to multiple independent software systems without re-authenticating. This significantly improves user experience and reduces password fatigue. Federation takes this a step further, enabling identities and access rights to be shared and managed across different organizations or identity providers, crucial for collaboration with partners and customers. Protocols like SAML (Security Assertion Markup Language) and OAuth/OpenID Connect facilitate SSO and federation.
Privileged Access Management (PAM)
PAM focuses specifically on managing and securing “privileged accounts”—those with elevated permissions, such as system administrators, database administrators, and root users. These accounts are prime targets for attackers, and their compromise can lead to catastrophic breaches. PAM solutions enforce strict controls, monitor, and record all activity associated with privileged accounts, often requiring just-in-time access and session monitoring.
Identity Governance and Administration (IGA)
IGA combines identity management and access governance functions. It provides a comprehensive view of who has access to what, automates provisioning and de-provisioning, certifies access rights regularly, and ensures compliance with regulatory requirements (e.g., GDPR, HIPAA, SOX). IGA tools help organizations maintain control over the entire identity lifecycle and prove compliance through detailed audit trails.
The Strategic Imperative: Benefits and Challenges
Implementing a robust IAM strategy is not without its complexities, but the strategic benefits it offers in the current technological climate are undeniable.
Enhancing Security Posture
The most immediate benefit of IAM is a significantly strengthened security posture. By precisely controlling who can access what, organizations minimize the risk of unauthorized data access, insider threats, and sophisticated external attacks. IAM acts as the first line of defense, preventing unauthorized entry and limiting the damage potential if a breach occurs by segmenting access.
Improving Operational Efficiency and Compliance
IAM streamlines IT operations by automating user provisioning, de-provisioning, and access request processes. This reduces manual effort, improves efficiency, and minimizes human error. From a compliance perspective, IAM provides the audit trails and reporting capabilities necessary to demonstrate adherence to various industry regulations and internal policies, simplifying audits and reducing regulatory risk.
Overcoming Implementation Complexities
The main challenges in implementing IAM often revolve around complexity. Integrating disparate systems, managing a multitude of identities across hybrid environments, and ensuring user adoption can be daunting. Legacy systems may lack modern IAM capabilities, requiring significant investment in upgrades or custom integrations. User experience must also be considered; overly restrictive or cumbersome IAM processes can hinder productivity. Organizations must approach IAM implementation with a clear strategy, phased rollout, and a focus on user enablement.
The Future of IAM: Towards a Zero-Trust World
The future of IAM is deeply intertwined with the evolution of cybersecurity and tech innovation, moving towards more dynamic, intelligent, and user-centric models.
Adaptive and Context-Aware Access
The static “once authenticated, always trusted” model is giving way to a “never trust, always verify” or Zero Trust approach. Future IAM systems will leverage artificial intelligence and machine learning to continuously assess risk based on context—user location, device posture, time of day, unusual activity patterns, and even behavioral biometrics. Access will be granted dynamically, adjusted, or revoked in real-time based on these risk assessments, providing a far more resilient security layer.
Decentralized Identity and Blockchain
Emerging concepts like decentralized identity, often powered by blockchain technology, promise to give individuals more control over their digital identities. Instead of relying on central authorities, users would possess self-sovereign identities, selectively sharing verifiable credentials as needed. This paradigm shift could fundamentally alter how identities are managed and trusted across the internet, offering enhanced privacy and security.
AI and Machine Learning in IAM
AI and ML are not just beneficiaries of IAM but also powerful enablers within the IAM framework itself. These technologies are increasingly used to detect anomalous access patterns, predict potential threats, automate access reviews, and even proactively suggest optimal access policies. From enhancing fraud detection in authentication to intelligently automating compliance reporting, AI and ML will continue to drive greater intelligence and efficiency into IAM systems, making them more adaptive, predictive, and robust in the face of ever-evolving cyber threats.
In conclusion, Identity and Access Management is not merely a technical discipline but a strategic imperative that underpins the security, efficiency, and innovative capacity of modern enterprises. As technology continues its relentless march forward, IAM will remain at the forefront, evolving to secure the increasingly complex digital identities that power our interconnected world.