
The Evolving Landscape of Digital Security in Autonomous Systems
In an era increasingly defined by advanced technology and interconnected systems, cybersecurity has transitioned from a niche concern to a foundational pillar of operational integrity and innovation. This is particularly true in rapidly advancing fields like drone technology, autonomous flight, mapping, and remote sensing. As these technologies become more sophisticated, their attack surfaces expand, necessitating equally sophisticated security measures. Multi-Factor Authentication (MFA) stands out as a critical defense mechanism in this evolving landscape, offering a significantly enhanced layer of protection beyond simple passwords.
Why Traditional Passwords Fail
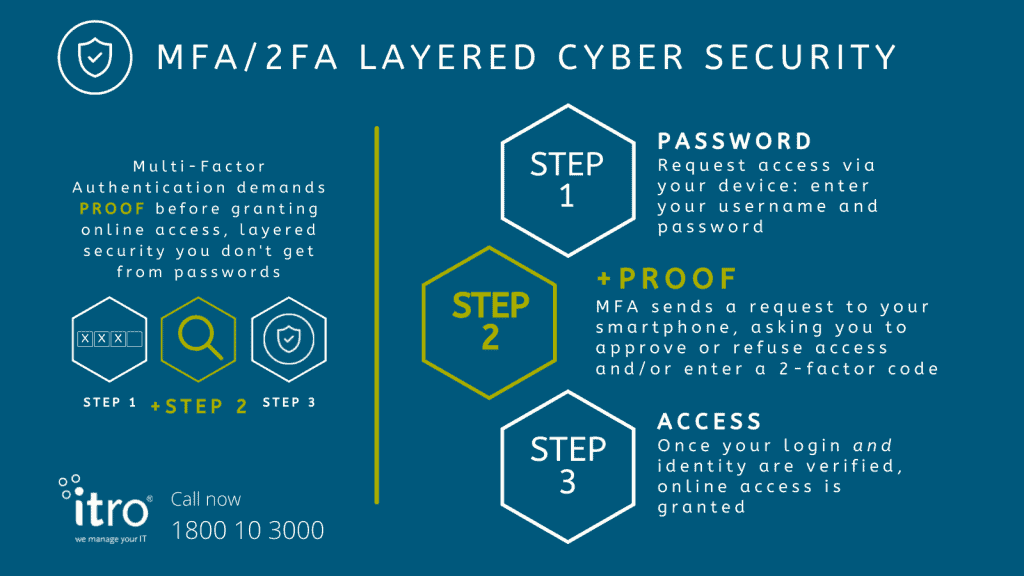
For decades, passwords have been the primary gatekeepers of digital access. However, their inherent weaknesses have become glaringly apparent. Users often choose weak, easily guessable passwords or reuse them across multiple services, creating a domino effect if one account is compromised. Phishing attacks, brute-force attempts, dictionary attacks, and credential stuffing are common tactics employed by malicious actors to bypass single-factor authentication. In the context of drone operations, where sensitive data, valuable equipment, and potentially critical infrastructure are at stake, relying solely on passwords presents an unacceptable level of risk. A compromised password could grant unauthorized access to flight plans, real-time telemetry, stored sensor data, or even direct control over a drone, leading to data breaches, operational disruptions, or even physical harm.
The Critical Need for Robust Authentication in Drone Operations
The burgeoning field of drone technology, encompassing everything from micro-drones for hobbyists to sophisticated UAVs for industrial inspection, mapping, and logistics, operates within a complex digital ecosystem. This ecosystem includes drone control software, ground station applications, cloud-based data storage for aerial imagery and sensor readings, communication links, and enterprise resource planning (ERP) systems that manage drone fleets. Each of these components represents a potential entry point for attackers. Robust authentication, therefore, isn’t just about protecting personal accounts; it’s about safeguarding entire operational frameworks. For example, in precision agriculture, where drones collect data on crop health, unauthorized access could lead to data manipulation, causing incorrect pesticide application or yield forecasts. In infrastructure inspection, compromised data could expose critical vulnerabilities. The very nature of autonomous flight, remote sensing, and mapping, which often involves collecting and processing highly sensitive geographical or proprietary data, demands an authentication paradigm that can withstand modern cyber threats. MFA provides this essential fortification, ensuring that only authorized personnel and systems can access and manipulate these critical assets and data streams.
Deconstructing Multi-Factor Authentication (MFA)
At its core, Multi-Factor Authentication (MFA) is a security system that requires a user to provide two or more verification factors to gain access to a resource such as an application, online account, or VPN. Instead of merely knowing something (like a password), MFA demands a combination of different categories of authentication, making it significantly harder for unauthorized users to gain access even if one factor is compromised.
The Three Pillars of Authentication
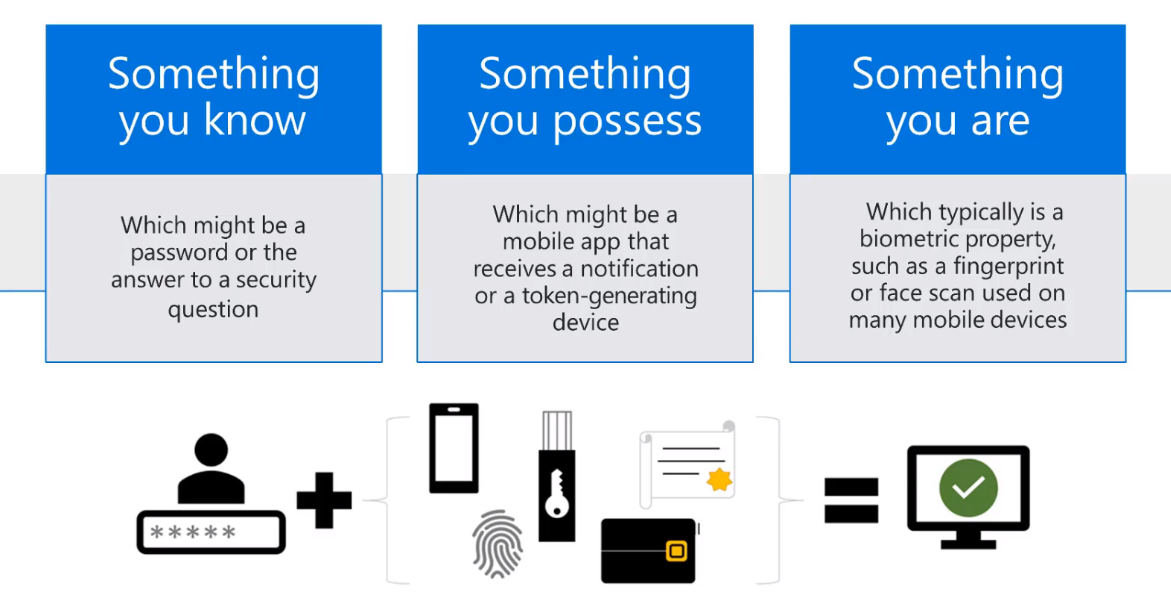
MFA operates on the principle of requiring verification from at least two of the three fundamental categories of authentication factors:
-
Something You Know (Knowledge Factor): This is the most traditional factor and includes passwords, PINs, security questions, or passphrases. It relies on information that only the legitimate user is supposed to possess. While susceptible to compromise on its own, it forms a crucial part of an MFA strategy when combined with other factors. In the context of drone tech, this could be the password for a ground station application or a login to a cloud-based drone management platform.
-
Something You Have (Possession Factor): This factor involves a physical item that belongs to the user. Common examples include a smartphone receiving a one-time passcode (OTP) via SMS or an authenticator app (e.g., Google Authenticator, Authy), a hardware security key (e.g., YubiKey), a smart card, or an access token. The assumption is that an attacker would need to physically steal this item in addition to knowing the password. For drone operators, this could mean an OTP sent to their registered device before they can access flight controls or sensitive mapping data archives.
-
Something You Are (Inherence Factor): This factor utilizes unique biological characteristics of the user, making it inherently personal and difficult to replicate. Biometric authentication falls into this category and includes fingerprint scans, facial recognition, iris scans, and voice recognition. As biometric technology advances, it’s becoming more prevalent in high-security applications. Imagine a drone pilot needing a fingerprint scan to initiate a flight or access mission-critical data on a ruggedized tablet in the field. This adds an extremely robust layer of verification, especially for critical infrastructure inspections or sensitive remote sensing missions.
By requiring a combination of factors from different categories, MFA significantly elevates the bar for attackers. Even if a cybercriminal manages to steal a password, they would still need to obtain the user’s physical token or biometric data to gain access, making the breach exponentially more difficult.
Common MFA Implementations in Tech Ecosystems
MFA takes various forms, each suited to different use cases and security needs within the broader tech landscape, including drone-related innovations:
- SMS-based OTPs: A one-time passcode is sent via text message to the user’s registered mobile phone. While convenient, it’s considered less secure due to potential SIM-swapping attacks.
- Authenticator Apps: Applications like Google Authenticator or Microsoft Authenticator generate time-based one-time passcodes (TOTP) directly on the user’s device. These are generally more secure than SMS-based OTPs as they don’t rely on network carrier security.
- Hardware Security Keys: Physical USB devices (e.g., YubiKey, Titan Security Key) that plug into a computer or connect via NFC/Bluetooth. They provide cryptographic proof of identity and are highly resistant to phishing. These are ideal for securing access to critical drone fleet management systems or sensitive data repositories.
- Biometric Authentication: Integrates fingerprint readers, facial recognition (e.g., Face ID), or iris scanners into devices. This offers a seamless yet robust authentication experience, particularly for field operations using mobile devices.
- Push Notifications: A notification is sent to a registered mobile device, asking the user to approve or deny a login attempt with a simple tap. This combines convenience with a strong possession factor.
The choice of MFA implementation often depends on the sensitivity of the data or system being protected, the user experience requirements, and the operational environment. For drone technology, where data integrity and system control are paramount, a multi-layered approach, perhaps combining hardware keys for administrative access and push notifications for routine operational logins, might be optimal.
MFA’s Role in Securing Drone Technology and Data
In the realm of Tech & Innovation, particularly concerning advanced aerial platforms, MFA is not merely an optional security enhancement; it’s a fundamental necessity. Its application spans the entire lifecycle of drone operations, from initial system access to post-flight data analysis.
Protecting Drone Control Systems and Ground Stations
The command and control systems of drones are arguably the most critical points of vulnerability. Unauthorized access could lead to catastrophic outcomes, ranging from data interception to loss of control, diversion, or even weaponization of the drone. MFA safeguards access to these systems at multiple levels:
- Pilot and Operator Authentication: Before a pilot can access flight planning software, initiate a mission, or take manual control, MFA ensures their identity. This could involve a password coupled with a biometric scan on a control tablet, a hardware security key plugged into a ground station laptop, or a one-time code from an authenticator app. This prevents rogue operators or unauthorized individuals from launching drones.
- Fleet Management Platforms: Enterprise drone operations often rely on centralized fleet management software to schedule missions, track maintenance, manage pilot certifications, and monitor drone telemetry. Implementing MFA for these platforms protects against unauthorized scheduling of missions, manipulation of operational logs, or theft of sensitive fleet data.
- Firmware and Software Updates: Secure over-the-air (OTA) updates are crucial for drones, but the update process itself is a target. MFA can protect access to the repositories from which updates are pushed, ensuring that only verified, signed firmware is deployed, preventing malicious code injection that could compromise drone functionality or security.
By fortifying these access points, MFA drastically reduces the risk of malicious actors gaining control of expensive hardware, disrupting critical operations, or using drones for illicit purposes.
Safeguarding Sensitive Aerial Data (Mapping, Sensing, Imagery)
Drones are powerful data collection machines. Whether performing precise LiDAR scans for construction, thermal imaging for energy inspections, multispectral analysis for agriculture, or high-resolution photography for mapping, the data collected is often proprietary, commercially valuable, or even classified.
- Cloud Storage and Processing Platforms: Most advanced drone operations involve uploading collected data to cloud platforms for processing, analysis, and storage. These platforms are prime targets for cyberattacks. MFA is essential for securing user accounts accessing these cloud services, protecting against unauthorized data downloads, tampering, or deletion. This ensures the integrity and confidentiality of mapping data, inspection reports, and other critical insights derived from drone operations.
- Data Access and Sharing: Collaboration often requires sharing data with various stakeholders, clients, or regulatory bodies. MFA can be integrated into secure data sharing portals, ensuring that only authorized recipients can decrypt and view sensitive aerial imagery or analytical reports. This prevents industrial espionage or exposure of sensitive infrastructure details.
- Edge Device Security: As AI and machine learning capabilities move closer to the drone itself (edge computing), securing access to data stored on the drone or its processing units becomes vital. While complex, MFA principles can inform the design of secure access protocols for retrieving data directly from the drone in the field, perhaps using proximity-based authentication or encrypted hardware tokens.
The integrity and confidentiality of this data are paramount, and MFA provides a robust defense against compromise, preserving the value and trustworthiness of drone-derived insights.
Ensuring Supply Chain and Software Integrity
The innovation cycle in drone technology is rapid, with new components, software, and integrations constantly emerging. This complex supply chain presents numerous security challenges that MFA can help mitigate.
- Developer and Administrator Access: Access to source code repositories, development environments, and critical infrastructure management tools for drone software and hardware manufacturers must be rigorously protected. MFA for developers and system administrators ensures that only trusted personnel can commit code, manage servers, or release updates, preventing insider threats or sophisticated supply chain attacks that could inject vulnerabilities into the core technology.
- Third-Party Integrations: Drone ecosystems often rely on integrations with third-party software for everything from weather forecasting to airspace management. MFA can secure the APIs (Application Programming Interfaces) and accounts used for these integrations, ensuring that data exchange is authenticated and authorized, preventing a vulnerability in one system from compromising the entire drone operation.
- Manufacturing and Assembly: While less direct, MFA can play a role in securing access to industrial control systems (ICS) and IT networks within manufacturing facilities where drone components are produced and assembled. This helps prevent tampering during the manufacturing process, ensuring the physical and software integrity of the drone from its inception.
By implementing MFA across these critical points, the drone industry can build a more resilient and trustworthy foundation for its ongoing technological advancements.
Implementing MFA: Challenges and Best Practices for Innovation
While the benefits of MFA are clear, its effective implementation, especially in diverse and rapidly evolving tech environments like drone technology, comes with its own set of challenges and demands careful consideration of best practices.
User Experience vs. Security Strength
One of the primary hurdles in widespread MFA adoption is balancing robust security with a seamless user experience. Overly complex or cumbersome authentication processes can lead to user frustration, workarounds, or resistance, ultimately undermining security efforts.
- Tailored Solutions: For drone operators working in the field, quick and efficient access to controls and data is essential. Implementing biometrics (fingerprint on a rugged tablet) or push notifications might be more user-friendly than requiring a hardware key for every action. For backend administrators accessing critical servers, the higher security of a hardware key might be warranted, even if slightly less convenient.
- Contextual Authentication: Advanced MFA systems can adapt based on context. If a drone operator logs in from a known, secure location and device, a simpler MFA might suffice. If they log in from an unusual location or device, stronger authentication could be triggered. This smart approach improves both security and user experience.
- Education and Training: Users must understand why MFA is necessary and how to use it effectively. Proper training can mitigate resistance and ensure correct adoption, highlighting the protection it offers to their work and the valuable assets they manage.
The goal is to integrate MFA in a way that feels like a natural part of the workflow, rather than an impediment.
Adapting MFA for IoT and Edge Devices (Drones)
Drones, as sophisticated IoT devices, present unique challenges for traditional MFA. They often have limited computational resources, operate autonomously or semi-autonomously, and communicate over various networks.
- Device Identity and Mutual Authentication: Beyond authenticating human users, MFA principles extend to authenticating devices themselves. Drones need to securely authenticate with ground stations, cloud services, and other drones. This involves mutual authentication using digital certificates or secure provisioning, ensuring that both ends of a communication are verified before data exchange.
- Hardware-Based Security Modules: Implementing MFA-like capabilities directly on drone hardware through Trusted Platform Modules (TPMs) or Hardware Security Modules (HSMs) can secure boot processes, cryptographic keys, and device identity, making the drone itself more resilient to tampering.
- Lightweight Protocols: Traditional MFA protocols might be too resource-intensive for some drone components. Innovation is required to develop lightweight, secure authentication protocols suitable for constrained IoT environments, ensuring the drone’s operational efficiency isn’t compromised by security overhead.
- Remote Management and Recovery: In scenarios where a drone is physically inaccessible, secure remote management requires robust authentication to prevent unauthorized remote control or data access.
The future of drone security lies in embedding MFA principles not just for human interaction, but throughout the entire device and data lifecycle, leveraging advanced cryptographic techniques suitable for edge computing.

The Future of Authentication: Biometrics and Beyond
The evolution of MFA continues, driven by the need for stronger security and improved usability.
- Advanced Biometrics: Beyond fingerprints and facial recognition, technologies like behavioral biometrics (analyzing typing patterns, gait, or interaction styles) and continuous authentication (constantly verifying identity throughout a session) promise even more seamless and robust security. Imagine a drone system that continuously verifies the operator’s identity based on their interaction patterns.
- Passwordless Authentication: The ultimate goal for many is to move beyond passwords entirely. FIDO (Fast IDentity Online) standards, leveraging public-key cryptography and biometrics, are paving the way for a passwordless future where users authenticate with a biometric scan or a security key directly, without ever typing a password. This would significantly reduce the attack surface for phishing and credential stuffing.
- Zero Trust Architecture: In a Zero Trust model, no user or device is inherently trusted, regardless of whether they are inside or outside the network perimeter. Every access request is authenticated, authorized, and continuously validated. MFA is a cornerstone of this architecture, ensuring rigorous identity verification at every step, which is highly relevant for complex, distributed drone operations across various networks and cloud environments.
As drone technology pushes the boundaries of autonomous flight, remote sensing, and interconnected systems, the role of MFA will only grow in importance. By embracing these innovative authentication strategies, the industry can build a foundation of trust and resilience essential for unlocking the full potential of aerial innovation.