
Multi-Factor Authentication (MFA) represents a cornerstone of modern cybersecurity, a critical safeguard in an increasingly interconnected digital landscape. In the realm of drone technology and innovation, where autonomous flight, sophisticated mapping, remote sensing, and AI-driven capabilities are pushing boundaries, the integrity and security of access systems are paramount. MFA moves beyond the traditional single-password barrier, demanding two or more verification methods from separate categories, thereby drastically reducing the risk of unauthorized access to critical drone systems, sensitive operational data, and proprietary intellectual property. For innovators working on AI follow modes, complex navigation algorithms, or managing fleets of remote sensing platforms, understanding and implementing MFA is not merely best practice; it is an essential defense against malicious actors who seek to compromise or exploit these advanced technologies.
The Imperative of Robust Security in Drone Tech & Innovation
The technological advancements in drones have opened doors to unprecedented capabilities, but concurrently, they have introduced new vectors for cyber threats. A drone operating with AI follow mode might be collecting sensitive data in a critical infrastructure inspection; an autonomous mapping drone could be gathering high-resolution geographical data for national defense or urban planning; a remote sensing platform might be monitoring environmental changes or agricultural health. In each scenario, the systems that control these drones, the data they collect, and the intellectual property embedded within their operational algorithms are high-value targets. A single compromised password can lead to catastrophic consequences: data breaches, manipulation of flight paths, disruption of services, or even the weaponization of a drone.
The “Tech & Innovation” category, encompassing AI, autonomous flight, mapping, and remote sensing, thrives on trust and reliability. This trust is fundamentally undermined if the underlying access controls are weak. MFA directly addresses this vulnerability by requiring multiple proofs of identity before granting access. Consider a scenario where a drone operator uses a cloud-based ground control station (GCS) to manage an autonomous fleet. If this GCS is protected only by a password, a compromised credential—perhaps through a phishing attack or data breach—could give an unauthorized individual control over multiple aircraft, access to flight plans, or the ability to exfiltrate mission-critical data. With MFA, even if the password is stolen, the attacker would still need a second factor, such as a code from a physical token or biometric verification, making the breach significantly more difficult, if not impossible.
Protecting Data Integrity in Remote Sensing and Mapping
Remote sensing and mapping operations frequently involve the acquisition and processing of vast quantities of sensitive data. This can include high-resolution imagery of private property, critical infrastructure schematics, geological survey data, or agricultural insights that hold significant commercial value. The integrity of this data is crucial for its utility and reliability. Unauthorized access could lead to data exfiltration, alteration, or deletion, compromising projects, violating privacy regulations, and eroding client trust.
MFA implementation extends to every access point where this data resides: the drone’s onboard storage (if remotely accessible), the ground control station, cloud storage services, and analytical platforms. By securing these points with MFA, drone operators and data analysts ensure that only verified personnel can access, process, and interpret the collected intelligence. This is particularly vital for organizations handling classified or proprietary information, where regulatory compliance often mandates stringent security measures beyond simple password protection.
Securing Autonomous Flight Pathways and AI Models
Autonomous flight, a pinnacle of drone innovation, relies heavily on sophisticated software, real-time data processing, and often, AI models for navigation, object recognition, and decision-making. The security of these systems is paramount, as a compromised autonomous drone could be redirected, its AI model manipulated, or its operational parameters altered. This could lead to mission failure, physical damage, or even malicious deployment.
MFA plays a critical role in securing the access points to the frameworks that develop, deploy, and manage these autonomous capabilities. This includes developer environments, code repositories, firmware update portals, and fleet management dashboards. Ensuring that only authorized developers and operators can push code, configure flight parameters, or initiate autonomous missions is a fundamental requirement. Without robust authentication, the promise of autonomous flight, which includes beyond visual line of sight (BVLOS) operations over vast distances, remains vulnerable to severe security risks. MFA acts as a vital gatekeeper, protecting the intellectual property of AI algorithms and the operational integrity of autonomous drone fleets.
Deconstructing Multi-Factor Authentication
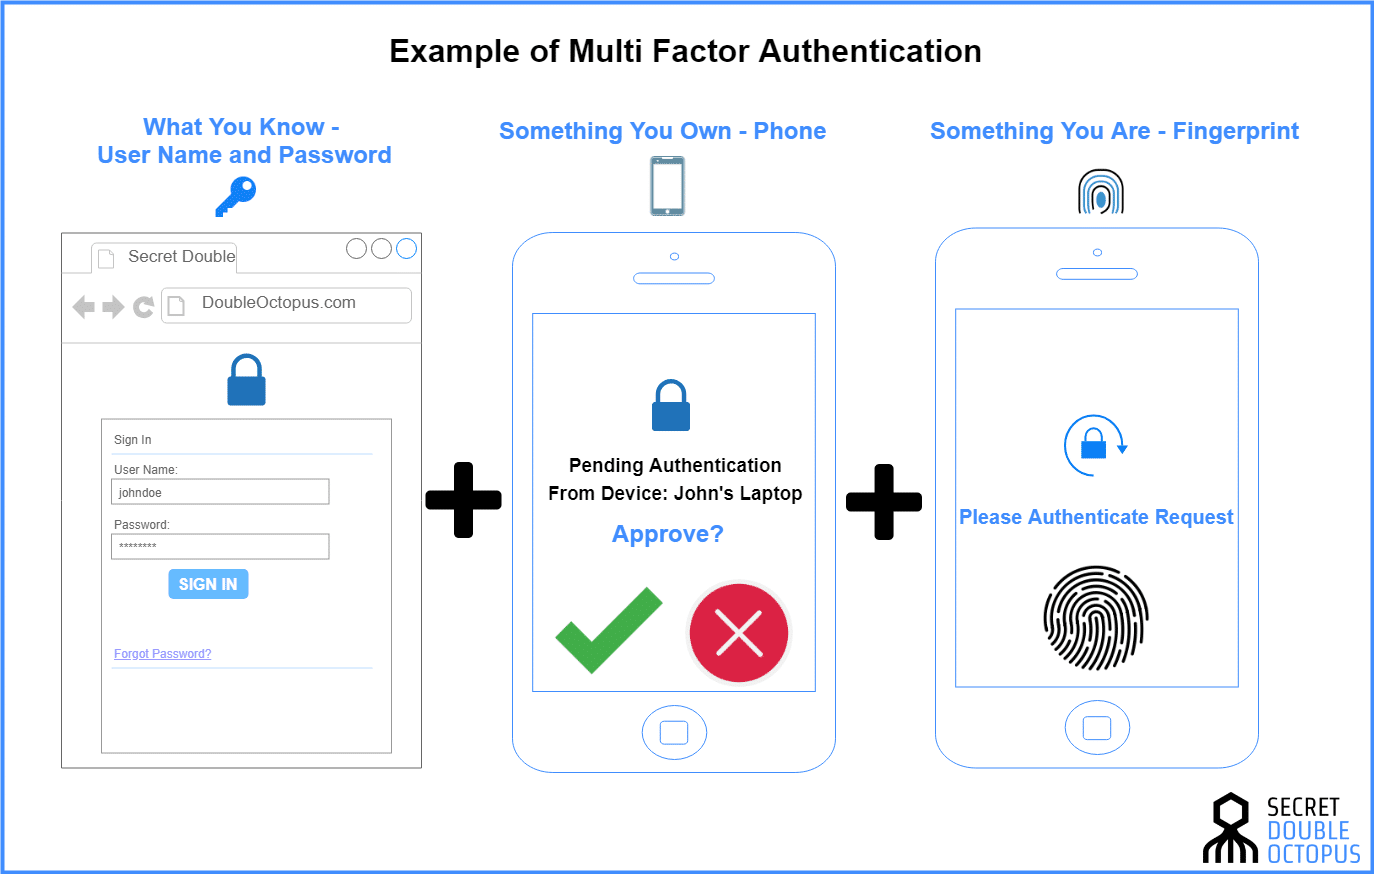
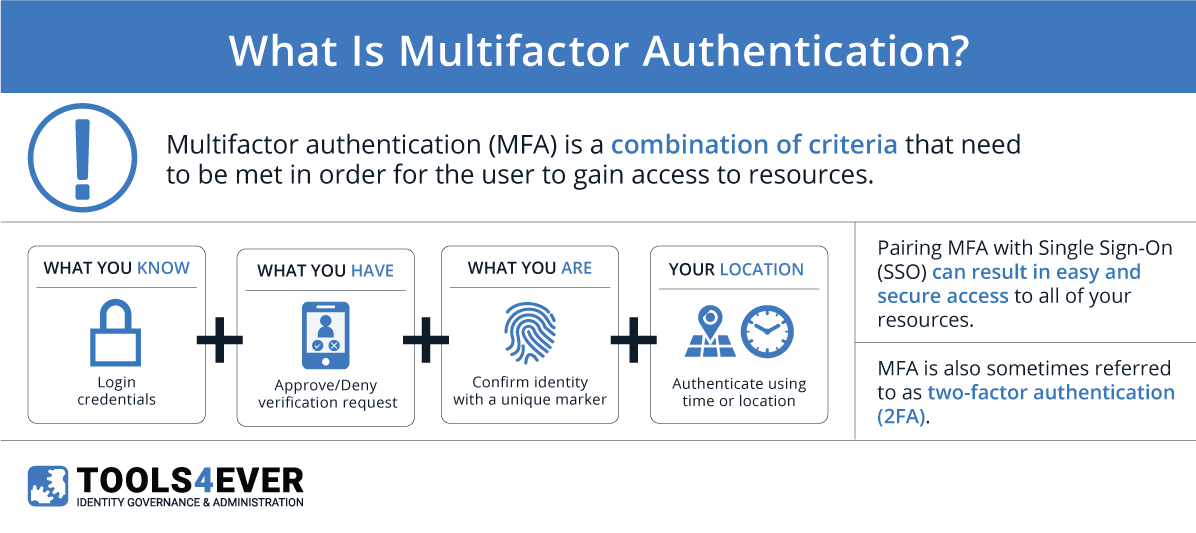
MFA fundamentally enhances security by requiring users to prove their identity through at least two different categories of verification factors. These categories are broadly defined as: something you know, something you have, and something you are. The combination of these distinct factors creates a much stronger authentication barrier than relying on a single factor alone.
Knowledge Factors (Something You Know)
This category includes information that only the legitimate user should know. The most common example is a password or a PIN. Other examples might include security questions (e.g., “What was your mother’s maiden name?”) or passphrases. While essential, these factors are the most susceptible to attack methods like phishing, brute-force attacks, or credential stuffing, where attackers use stolen username/password combinations from other breaches. Therefore, knowledge factors alone are insufficient for securing high-value assets in the drone innovation space.
Possession Factors (Something You Have)
Possession factors rely on an item that only the authorized user physically possesses. This category significantly elevates security because even if an attacker knows the password, they would still need to obtain the physical item. Examples include:
- Hardware Tokens: Small devices that generate time-sensitive, one-time passcodes (OTPs) or respond to cryptographic challenges.
- Software Tokens/Authenticator Apps: Applications on a smartphone that generate OTPs (e.g., Google Authenticator, Microsoft Authenticator) or approve login requests through push notifications.
- Smart Cards/USB Keys: Physical devices that store cryptographic keys and require insertion into a computer or reader.
- SMS/Email Codes: OTPs sent via text message or email. While convenient, these can be vulnerable to SIM-swapping attacks or compromised email accounts, making them generally less secure than dedicated authenticator apps or hardware tokens for critical systems.
For drone operators, particularly those managing sensitive missions or proprietary data, robust possession factors like hardware tokens or dedicated authenticator apps are highly recommended for accessing GCS, cloud platforms, and data repositories.

Inherence Factors (Something You Are)
Inherence factors are based on unique biological attributes of the user, making them inherently difficult to fake or steal. This category includes biometrics. Examples are:
- Fingerprint Scans: Using unique ridge patterns on a finger.
- Facial Recognition: Analyzing unique features of a user’s face.
- Retinal/Iris Scans: Analyzing the unique patterns in the human eye.
- Voice Recognition: Identifying unique vocal characteristics.
Biometric authentication offers a high level of convenience and security, as these factors are extremely difficult for an attacker to replicate. Modern smartphones and laptops often integrate fingerprint or facial recognition, making it easier to implement inherence factors for accessing applications or web platforms related to drone operations, provided the underlying system supports such integrations securely. The combination of, for example, a password (something you know) and a fingerprint scan (something you are) creates a powerful and user-friendly security paradigm.
Implementing MFA in Advanced Drone Ecosystems
The strategic implementation of MFA within advanced drone ecosystems is crucial for safeguarding the integrity, confidentiality, and availability of innovative technologies. It moves beyond securing individual accounts to fortifying entire operational frameworks.
Safeguarding Ground Control Stations and Cloud Platforms
Ground Control Stations (GCS) serve as the nerve center for drone operations, whether they are physical workstations or cloud-based dashboards. They are used for mission planning, real-time telemetry monitoring, payload control, and data download. Securing access to these platforms is non-negotiable. Implementing MFA ensures that only authorized pilots and mission commanders can log into the GCS. This might involve requiring a password (something you know) combined with an OTP from an authenticator app (something you have) or a biometric scan (something you are) to initiate a flight plan or take control of an autonomous mission.
Similarly, cloud platforms that host drone fleet management software, data storage, AI model training environments, or remote sensing data analytics tools are critical points of entry for attackers. MFA on these platforms protects against unauthorized access to valuable intellectual property, customer data, and operational continuity. Many cloud service providers offer native MFA capabilities that should be universally enforced across all user accounts.
Securing AI Follow Mode and Remote Operations
AI follow mode, autonomous navigation, and other intelligent drone functionalities represent significant advancements in operational efficiency and capability. However, they also introduce new attack surfaces. An attacker gaining unauthorized access to the parameters governing an AI follow mode could potentially manipulate its behavior, leading to erratic flight, privacy violations, or even physical damage.
MFA helps secure the configuration portals, API endpoints, and development environments used to manage and update these intelligent features. By enforcing MFA, organizations ensure that only vetted developers and engineers can deploy new AI models, modify critical flight algorithms, or push firmware updates to a drone fleet. For drone operators executing remote, beyond-visual-line-of-sight (BVLOS) operations, where direct human intervention might be delayed, the integrity of the remote access protocols, secured by strong MFA, becomes absolutely vital for safety and mission success. This prevents unauthorized individuals from taking over remote drone operations or altering their pre-programmed autonomous tasks.
Enhancing Regulatory Compliance and Public Trust
Many industries leveraging advanced drone technology, such as critical infrastructure inspection, defense, or sensitive data collection, are subject to stringent regulatory compliance frameworks (e.g., GDPR, HIPAA, CMMC). These regulations often mandate robust cybersecurity practices, including multi-factor authentication, to protect sensitive data and operations. Implementing MFA helps drone technology companies meet these compliance requirements, avoiding hefty fines and legal repercussions.
Beyond compliance, the consistent application of strong security measures, particularly MFA, builds public trust. As drones become more ubiquitous and their capabilities more advanced, public concern around privacy, safety, and potential misuse will naturally increase. Demonstrating a commitment to best-in-class security, with MFA as a foundational component, reassures stakeholders, clients, and the public that drone operations are conducted responsibly and securely. This trust is invaluable for the continued growth and acceptance of innovative drone applications.
The Future of Drone Security: Beyond Basic MFA
While MFA is a powerful defense, the evolving threat landscape demands continuous innovation in security. The future of drone security, particularly in the “Tech & Innovation” category, will likely see the integration of MFA with even more sophisticated techniques. This includes adaptive or risk-based authentication, where the system assesses contextual information (e.g., user location, device characteristics, time of day, historical behavior) to determine the level of authentication required. For instance, accessing a GCS from an unusual IP address might trigger an additional authentication challenge, even if standard MFA has already been satisfied.
Furthermore, advancements in hardware-based security, such as Trusted Platform Modules (TPMs) integrated into drone flight controllers or GCS hardware, will provide a secure root of trust for authentication processes. Zero-Trust Architecture, which operates on the principle of “never trust, always verify,” will also become increasingly relevant. In a Zero-Trust model, every user and device, regardless of their location within or outside the network, must be authenticated and authorized before accessing resources, with MFA being a critical component of this continuous verification.
The complexity of autonomous systems and the value of the data they process necessitate a multi-layered security approach where MFA is a fundamental, non-negotiable layer. As drone technology continues to innovate, so too must the security measures designed to protect it, ensuring that the incredible potential of these flying machines can be realized safely and securely.