
In the rapidly evolving landscape of cloud computing, where innovation thrives and data security is paramount, the Amazon Web Services (AWS) Virtual Private Cloud (VPC) stands as a foundational pillar. AWS VPC is a service that allows users to provision a logically isolated section of the AWS Cloud where they can launch AWS resources in a virtual network that they define. This dedicated, private space in the public cloud grants organizations granular control over their network environment, including IP address ranges, subnets, route tables, and network gateways. It’s akin to having your own private data center within the AWS infrastructure, but with all the inherent benefits of cloud scalability, flexibility, and reliability. For any enterprise engaged in cutting-edge tech development, from sophisticated AI models to large-scale data analytics for remote sensing, understanding and leveraging AWS VPC is crucial for building robust, secure, and high-performance solutions.
The Foundational Pillar of Cloud Security and Isolation
At its core, an AWS VPC offers a highly secure and isolated environment, crucial for enterprises dealing with sensitive data, intellectual property, or complex regulatory compliance. This isolation is not merely a feature; it’s a fundamental design principle that enables innovation without compromising security. By defining your own virtual network, you dictate how your resources interact with each other and with the internet, creating a fortified perimeter around your digital assets. This level of control is indispensable for organizations pushing the boundaries of technology, ensuring that their innovative solutions are built on a bedrock of security.
Logical Isolation: Your Dedicated Corner of the Cloud
The concept of logical isolation is central to AWS VPC. When you create a VPC, AWS allocates a unique, private network space for you, completely separate from other AWS customers. This separation ensures that your traffic, data, and resources are not exposed to or interfered with by others. You specify the IP address range (using CIDR blocks) for your VPC, providing a private address space that is not routable over the public internet. Within this private space, you can launch various AWS resources such as EC2 instances, RDS databases, and Lambda functions, all operating within your defined network boundaries. This dedicated environment empowers developers and architects to experiment and deploy innovative solutions with confidence, knowing their underlying infrastructure is secure and isolated.
Core Components of a VPC
Understanding the building blocks of an AWS VPC is essential for effective deployment and management. Each VPC is composed of several key elements:
- IP Address Range (CIDR Block): The first step in creating a VPC is to define its IP address range. This block of IP addresses (e.g.,
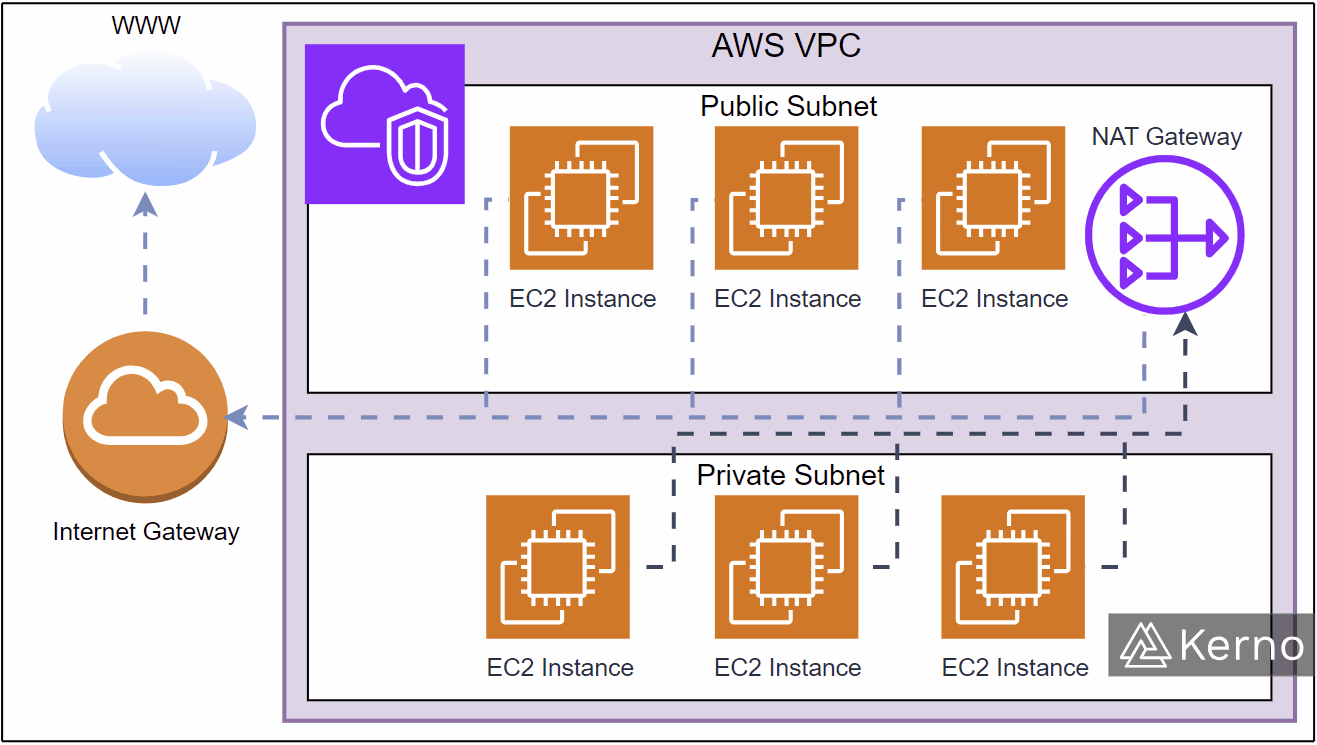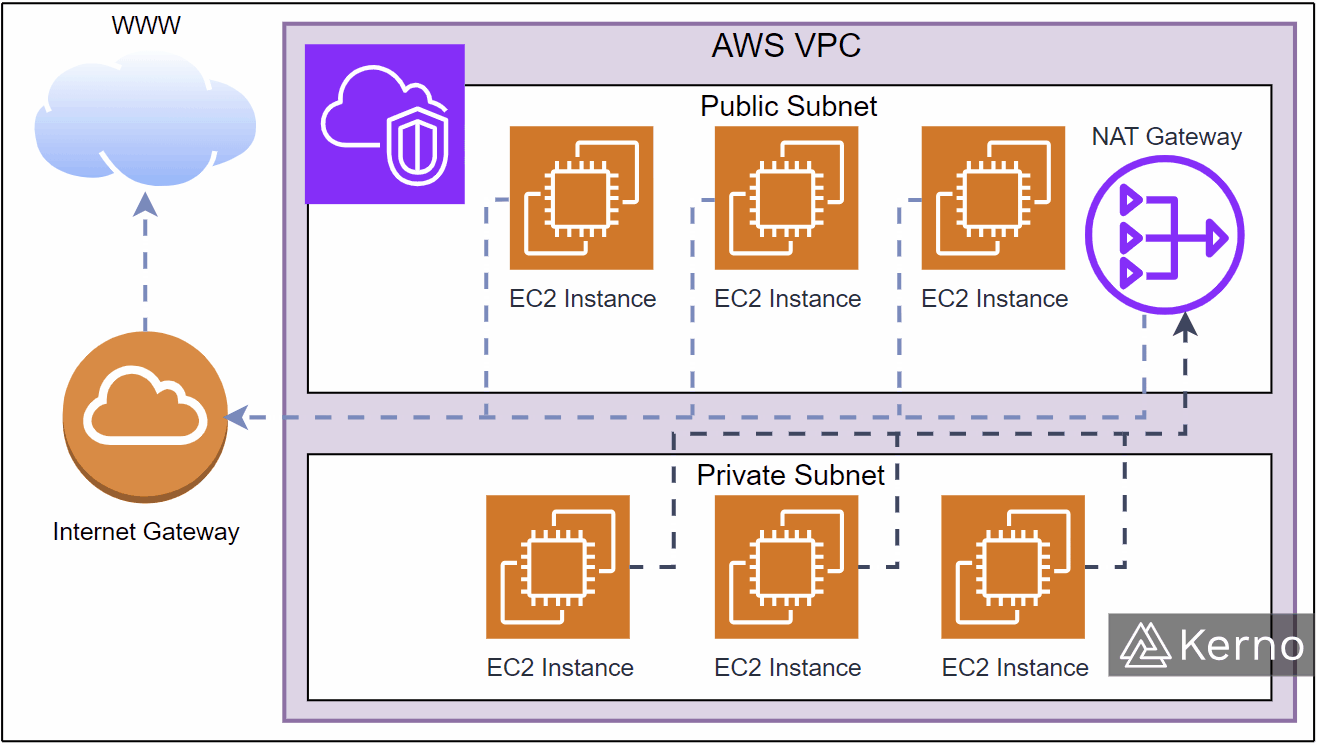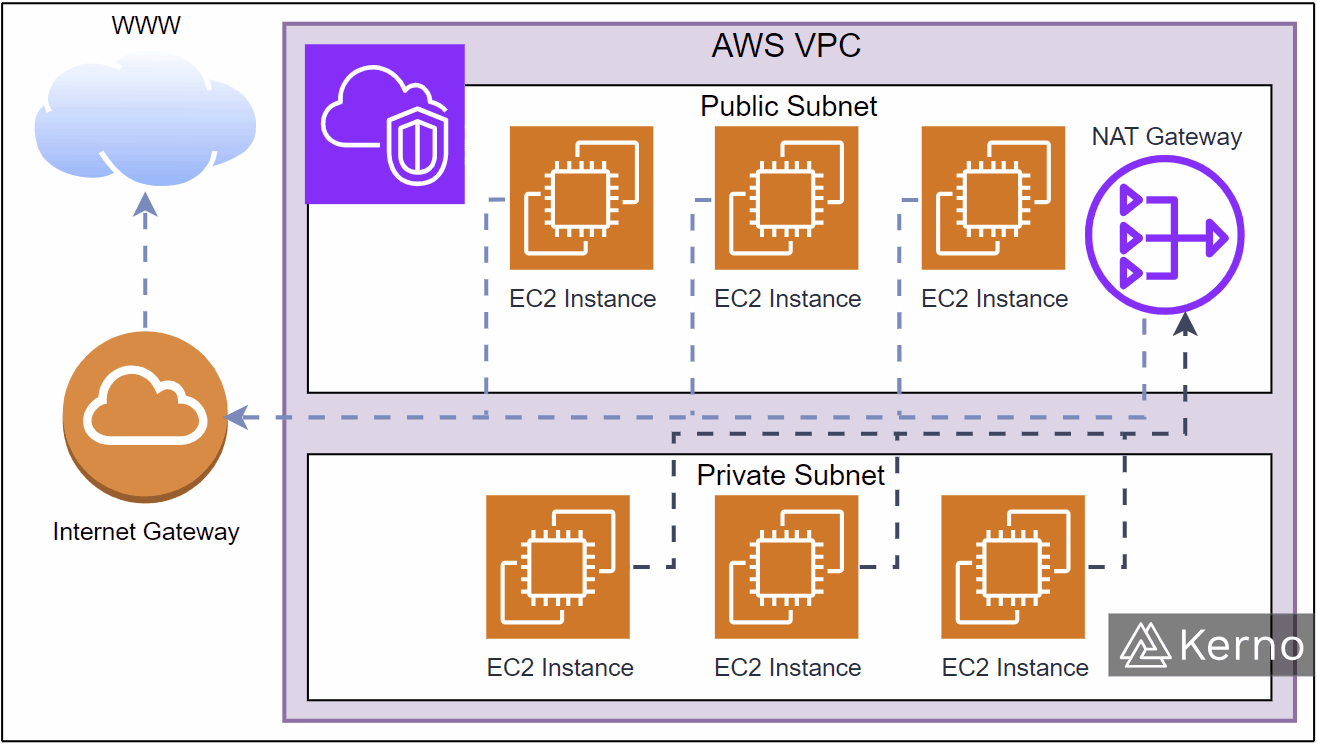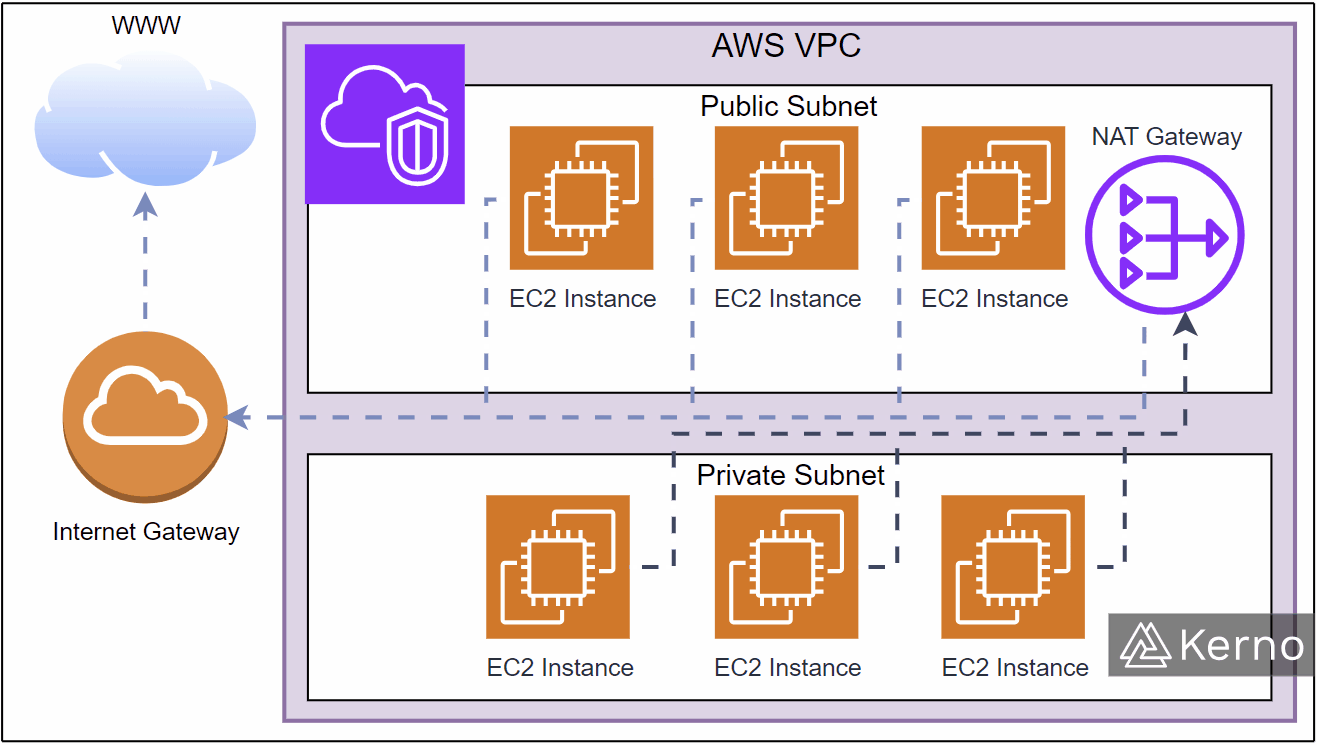
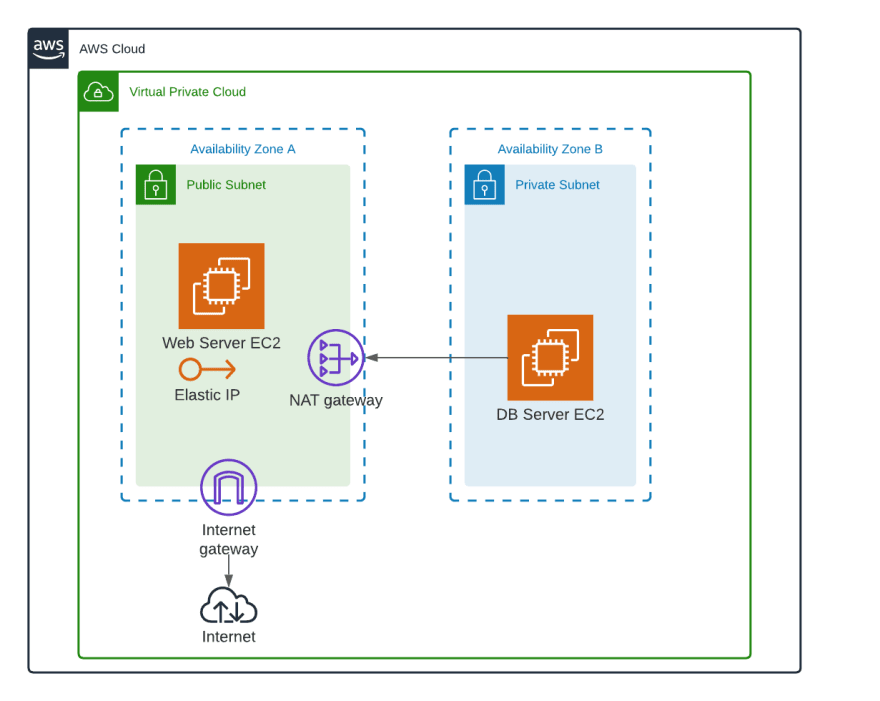
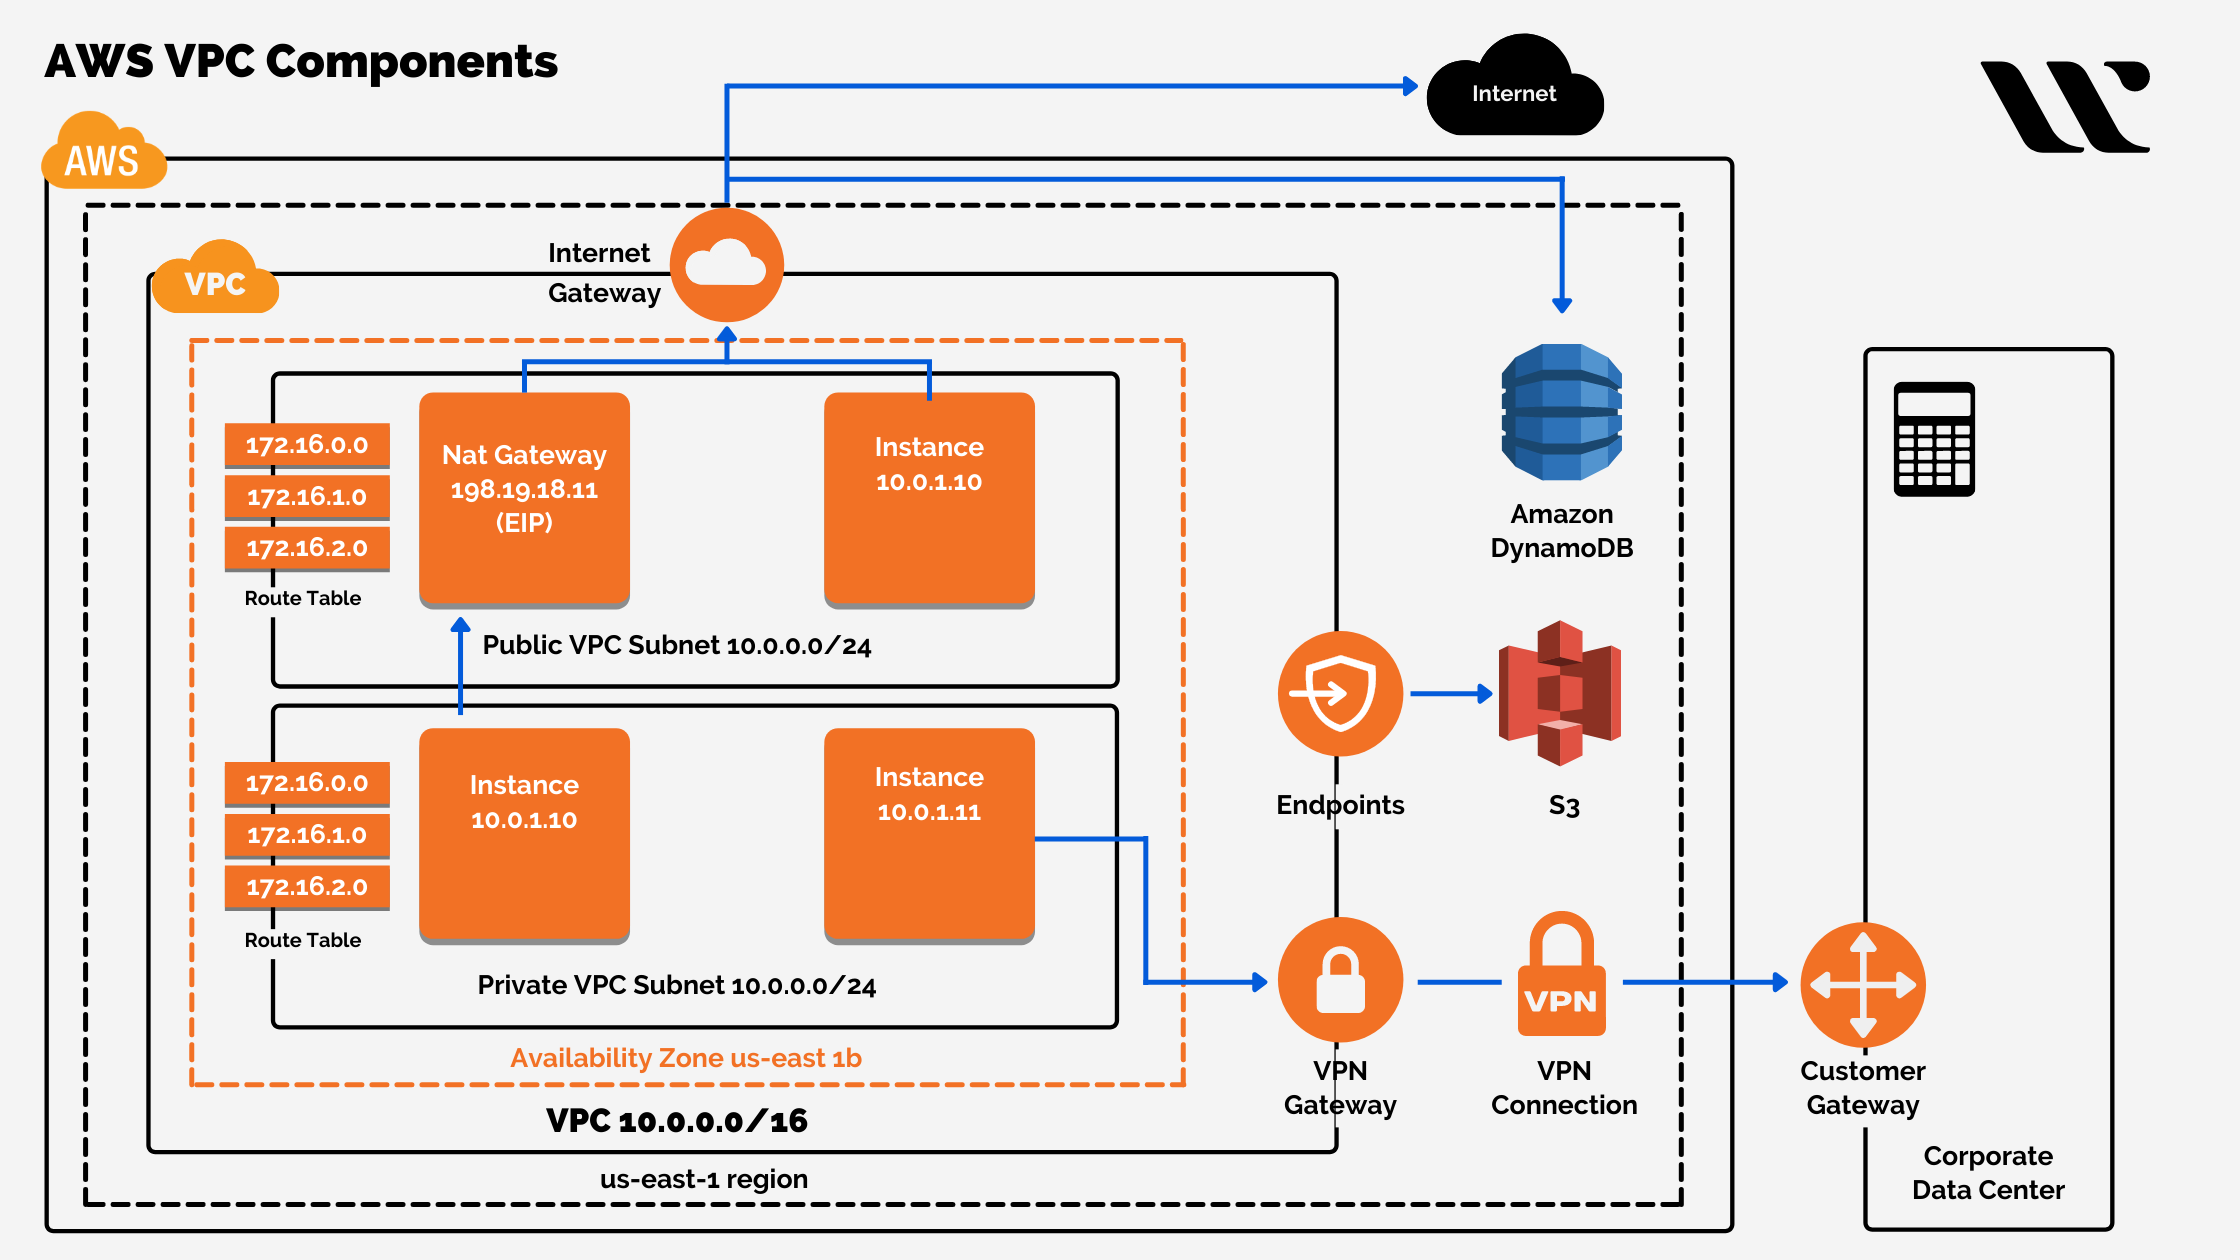
10.0.0.0/16) determines the total number of private IP addresses available within your VPC. - Subnets: Within your VPC, you can divide the IP address range into smaller segments called subnets. Subnets are tied to specific Availability Zones (AZs), providing high availability and fault tolerance. You can designate subnets as public (with direct internet access) or private (without direct internet access), depending on the resources they host.
- Route Tables: Each subnet in your VPC must be associated with a route table, which contains a set of rules, called routes, that determine where network traffic from the subnet is directed. This allows you to control the flow of data within your VPC and to external networks.
- Internet Gateway (IGW): For resources in a public subnet to communicate with the internet, an Internet Gateway must be attached to the VPC and a route added to the subnet’s route table. The IGW provides a target in your VPC’s route tables for internet-routable traffic.
- NAT Gateway/NAT Instance: Resources in private subnets that need to initiate outbound connections to the internet (e.g., for software updates or API calls) but should not be directly accessible from the internet can use a NAT (Network Address Translation) Gateway or NAT Instance.
- DHCP Option Sets and DNS Resolution: AWS VPCs automatically configure Dynamic Host Configuration Protocol (DHCP) option sets, which define how instances get their DNS servers and domain names. VPCs also support DNS resolution, allowing instances to resolve public and private hostnames.
Architecting for Innovation and Scalability
The flexibility of AWS VPC allows organizations to design complex, multi-tiered architectures that are highly scalable, resilient, and perfectly tailored to the demands of modern technological innovation. Whether you’re building a platform for real-time sensor data processing, deploying machine learning models for predictive analytics, or developing a new generation of autonomous systems, the VPC provides the adaptable network foundation required for these advancements.
Subnets and Routing: Segmenting Your Network
The strategic use of subnets is critical for effective network segmentation. By creating public and private subnets across multiple Availability Zones, you can distribute your applications for high availability and segment them based on their security requirements. For instance, web servers accessible from the internet can reside in public subnets, while databases containing sensitive information or backend processing servers (like those handling large datasets from remote sensing) can be placed in private subnets, completely shielded from direct internet exposure. Customizing route tables for each subnet ensures that traffic flows precisely where it needs to go, optimizing performance and security. This segmentation is paramount for complex applications that often comprise multiple layers and services, each with unique network access needs.
Internet Gateways and NAT Gateways: Connecting to the World
The Internet Gateway is the bridge between your VPC and the public internet, enabling direct internet access for resources in public subnets. This is vital for applications like web servers, public-facing APIs, or any service that needs to be globally accessible. Conversely, the NAT Gateway or NAT Instance is designed for resources in private subnets that require outbound internet connectivity without being directly addressable from the outside. This configuration is ideal for secure backend services that need to download updates, connect to external APIs, or push data to external storage, all while maintaining their private network status. For example, a data processing cluster in a private subnet might need to pull external libraries or push processed results to an S3 bucket, utilizing a NAT Gateway for secure outbound access.
VPN Connections and Direct Connect: Hybrid Cloud Integration
Many organizations operate in a hybrid cloud model, integrating their on-premises data centers with AWS. AWS VPC facilitates this through two primary services:
- AWS Site-to-Site VPN: This establishes a secure, encrypted connection between your on-premises network and your VPC over the public internet. It’s an excellent choice for quickly extending your data center to the cloud or for disaster recovery scenarios.
- AWS Direct Connect: For mission-critical applications requiring consistent, high-bandwidth, and lower-latency network performance, Direct Connect offers a dedicated network connection from your premises to AWS. This bypasses the public internet entirely, providing a more reliable and secure link, ideal for migrating large datasets, running hybrid applications, or connecting to latency-sensitive systems like those found in advanced manufacturing or research.
Enhancing Security and Control in Your VPC
Security within your VPC is not just about isolation; it’s about employing robust controls at multiple layers. AWS provides powerful tools to manage network access and monitor traffic, ensuring that your innovative projects remain protected from unauthorized access and potential threats.
Security Groups and Network Access Control Lists (NACLs)
AWS VPC offers two distinct layers of firewall protection:
- Security Groups: These act as stateful firewalls at the instance level. They control inbound and outbound traffic for individual instances, allowing you to specify rules based on protocols, port numbers, and source/destination IP addresses. Security groups remember previous connections, allowing return traffic automatically.
- Network Access Control Lists (NACLs): These are stateless firewalls that operate at the subnet level. NACLs allow you to permit or deny specific inbound and outbound traffic at the subnet boundary. Being stateless, they require separate rules for inbound and outbound traffic. NACLs provide an additional, broader layer of security, useful for segregating traffic between different security zones within your VPC.
Flow Logs, VPC Endpoints, and Endpoint Services
- VPC Flow Logs: For deep network visibility and troubleshooting, Flow Logs capture information about the IP traffic going to and from network interfaces in your VPC. They can be published to Amazon CloudWatch Logs or Amazon S3, providing valuable insights for security analysis, auditing, and optimizing network performance, especially crucial for monitoring high-throughput data streams from remote sensing or IoT devices.
- VPC Endpoints: These allow you to privately connect your VPC to supported AWS services (e.g., S3, DynamoDB) and VPC endpoint services powered by AWS PrivateLink, without requiring an Internet Gateway, NAT device, VPN connection, or AWS Direct Connect. This keeps traffic within the AWS network, enhancing security and reducing data transfer costs. This is critical for applications processing sensitive data that must never traverse the public internet.
- VPC Endpoint Services (AWS PrivateLink): For service providers, PrivateLink allows you to create your own endpoint services, making your applications available to other AWS customers in their VPCs without exposing them to the internet. This is a game-changer for building secure, shared services architectures for various tech partners.
Use Cases and The Future of Cloud Innovation
The adaptability and robust features of AWS VPC make it an indispensable tool for a wide array of technological innovations. From enabling the backend infrastructure for advanced AI algorithms to securely processing vast quantities of data from autonomous systems, the VPC provides the reliable and secure network environment needed to bring these concepts to fruition.
Supporting Advanced Analytics and AI/ML Workloads
AWS VPC provides the perfect environment for hosting compute-intensive AI and Machine Learning (ML) workloads. Data scientists can provision powerful EC2 instances with GPUs in private subnets, ensuring that training data and models remain secure. VPC Endpoints can then be used to securely access data lakes in Amazon S3 or analytics services like Amazon Athena, keeping all traffic within the AWS private network. This secure, high-performance environment is vital for processing the massive datasets generated by remote sensing, mapping initiatives, or sensor arrays from autonomous vehicles, allowing for rapid iteration and deployment of AI-powered insights.
Enabling Microservices and Serverless Architectures
Modern application development heavily relies on microservices and serverless functions (like AWS Lambda). AWS VPC allows these distributed components to communicate securely and efficiently. Microservices running on Amazon ECS or EKS (container services) within a VPC can access private databases and other internal services without exposing them to the internet. Lambda functions can be configured to run within a VPC, gaining access to private resources and benefiting from the defined network security policies, thereby extending the reach and security of serverless applications.
Disaster Recovery and Business Continuity
A well-architected VPC strategy is fundamental to robust disaster recovery (DR) and business continuity planning. By deploying resources across multiple Availability Zones within your VPC, and even replicating VPC configurations across different AWS regions, organizations can build highly resilient applications that can withstand regional outages. Hybrid cloud setups utilizing VPN or Direct Connect further enhance DR capabilities by allowing seamless failover between on-premises and cloud environments. This ensures that even the most innovative and critical applications remain operational and accessible under adverse conditions.
In conclusion, AWS VPC is far more than just a virtual network; it’s a strategic enabler for modern technology and innovation. By providing a secure, customizable, and scalable network environment, it empowers organizations to develop, deploy, and manage cutting-edge applications, ranging from secure data processing for mapping and remote sensing to robust backends for AI-driven autonomous systems. Its comprehensive suite of networking and security features provides the necessary control and isolation to build the future of technology with confidence.