The Evolution of Digital Authentication
Digital life is intrinsically linked to authentication. From logging into email to accessing banking services, proving one’s identity online has been a foundational, yet often fraught, aspect of the internet experience. For decades, the ubiquitous password has served as the primary gatekeeper, a simple string of characters intended to be a secret known only to the user and the service. However, the escalating complexity of the digital landscape has exposed the inherent vulnerabilities and user frustrations associated with passwords, pushing the tech industry towards more robust and user-friendly alternatives.
The Problem with Passwords
Passwords, despite their widespread use, are a relic of a bygone internet era. Their weaknesses are manifold and well-documented. Users are constantly pressured to create “strong” passwords—long, complex strings incorporating uppercase, lowercase, numbers, and symbols—which are difficult to remember and often lead to poor password hygiene. Many resort to reusing passwords across multiple services, a critical security flaw that allows a single data breach to compromise numerous accounts. Phishing attacks, where malicious actors trick users into revealing their credentials, remain a pervasive threat, exploiting human susceptibility rather than technical vulnerabilities. Furthermore, database breaches frequently expose millions of passwords, even if encrypted, to sophisticated attackers capable of decrypting them over time. The cumulative effect is a constant struggle between user convenience and robust security, often with security being sacrificed for the former. This precarious balance has driven the imperative for a paradigm shift in authentication.
Two-Factor Authentication’s Role and Limitations
Recognizing the fragility of passwords, two-factor authentication (2FA) emerged as a significant improvement. By requiring a second verification method—typically a code sent to a mobile device, a biometric scan, or a hardware security key—2FA adds an extra layer of defense, making it significantly harder for unauthorized individuals to access an account even if they possess the password. This method has dramatically reduced the success rate of many common cyberattacks. However, 2FA is not without its limitations. SMS-based 2FA, while convenient, can be susceptible to SIM-swapping attacks. Authenticator apps, while more secure, still rely on a password as the first factor. Hardware security keys offer the highest level of protection but are not universally adopted due to cost and convenience factors. Critically, 2FA still relies on the user knowing and inputting a password, meaning it doesn’t solve the fundamental issues of password memorability, creation, or the susceptibility to phishing if the first factor (the password) is compromised. The goal became to move beyond simply augmenting passwords and towards a truly passwordless future.
Understanding Passkeys: A FIDO Standard
Enter passkeys, a revolutionary approach to authentication that aims to eliminate the need for passwords altogether, offering a more secure, convenient, and phishing-resistant login experience. Google, as a leading technology innovator, has been at the forefront of implementing and championing passkeys, aligning with the Fast Identity Online (FIDO) Alliance’s standards. Passkeys represent a fundamental shift from “something you know” (passwords) to “something you have” (your device) and “something you are” (biometrics), or a combination thereof. They leverage modern cryptographic techniques to establish a secure identity assertion that is tied to your devices, effectively making your phone, laptop, or tablet a personal security key for your online accounts.
How Passkeys Work
At its core, a passkey is a digital credential that allows users to sign in to websites and apps without typing a password. When you create a passkey for an account, your device (e.g., smartphone, laptop) generates a unique cryptographic key pair: a public key and a private key. The public key is registered with the online service you’re trying to access, while the private key remains securely stored on your device, often protected by your device’s existing security measures like a PIN, pattern, fingerprint, or facial recognition.
When you attempt to log in, the service sends a challenge to your device. Your device then uses its private key to sign this challenge, and the signed message is sent back to the service. The service verifies this signature using the public key it already has. If the signature matches, authentication is successful. Crucially, the private key never leaves your device, and nothing is ever transmitted over the network that could be intercepted and reused by an attacker. This local verification process, coupled with strong device-level security, makes passkeys incredibly resistant to remote attacks like phishing.
Cryptography at Its Core
The robustness of passkeys is rooted in public-key cryptography, specifically asymmetric encryption. This sophisticated mathematical framework ensures that while the public key can verify a signature, it cannot be used to recreate the private key or sign new challenges. Each passkey is unique to the service it’s registered with, and the underlying cryptography prevents replay attacks, where an attacker might try to resend a captured authentication response. Furthermore, because the private key is generated and stored directly on the user’s device, it’s inherently tied to that specific hardware. Cloud synchronization mechanisms (like Google Password Manager for Google Passkeys) are designed to securely replicate these private keys across trusted devices associated with a user’s account, encrypted end-to-end to maintain their integrity and privacy. This cryptographic foundation creates a chain of trust that is far more resilient than traditional password-based systems.
Platform Authenticators vs. Roaming Authenticators
Passkeys can be categorized into two main types based on where and how they are stored and used:
Platform Authenticators: These are built directly into the operating system of a device (e.g., Windows Hello, Apple Face ID/Touch ID, Android biometrics). The passkey is stored securely within the device’s hardware enclave or trusted execution environment, and it is intrinsically linked to that specific device. When authenticating, the user interacts with the device’s biometric sensor or PIN prompt. These are highly secure as the private key never leaves the device and is often protected by hardware-level security.
Roaming Authenticators: These allow passkeys to be synced across multiple devices, offering greater convenience and a seamless experience. Google’s implementation of passkeys primarily falls into this category, leveraging Google Password Manager to securely synchronize passkeys across all devices signed into the same Google Account. While offering convenience, the security model relies on the integrity of the synchronization mechanism and the underlying device security for each synced device. The FIDO Alliance also supports physical security keys (like YubiKey) as roaming authenticators, where the passkey is stored on the physical key and requires its presence for authentication. The innovation lies in providing flexibility without compromising the core security benefits of the FIDO standard.
The Google Passkey Experience
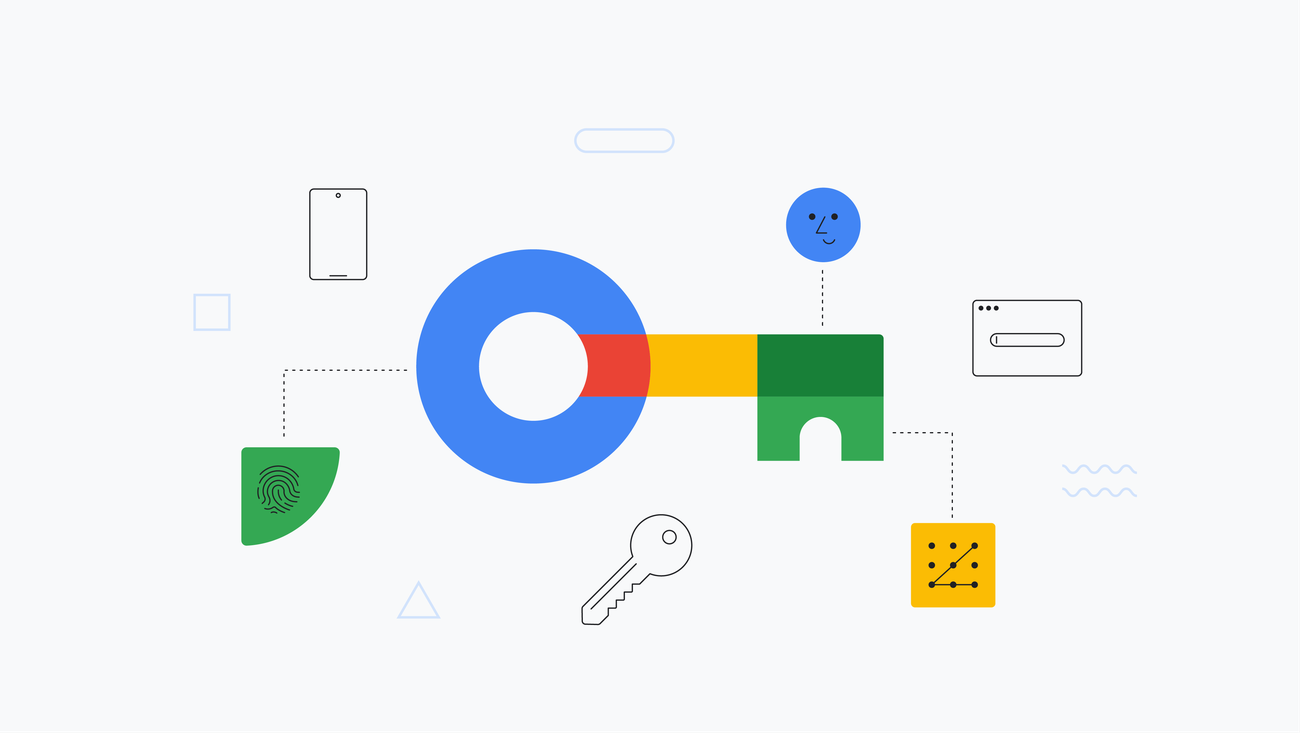
Google’s embrace of passkeys represents a significant stride towards making a passwordless future a reality for millions of users. By integrating passkey functionality directly into its ecosystem, Google aims to streamline the authentication process, enhance security, and reduce the friction traditionally associated with online logins. The focus is on creating a user experience that is intuitive, fast, and remarkably more secure than its password-reliant predecessors.
Seamless Login Across Devices
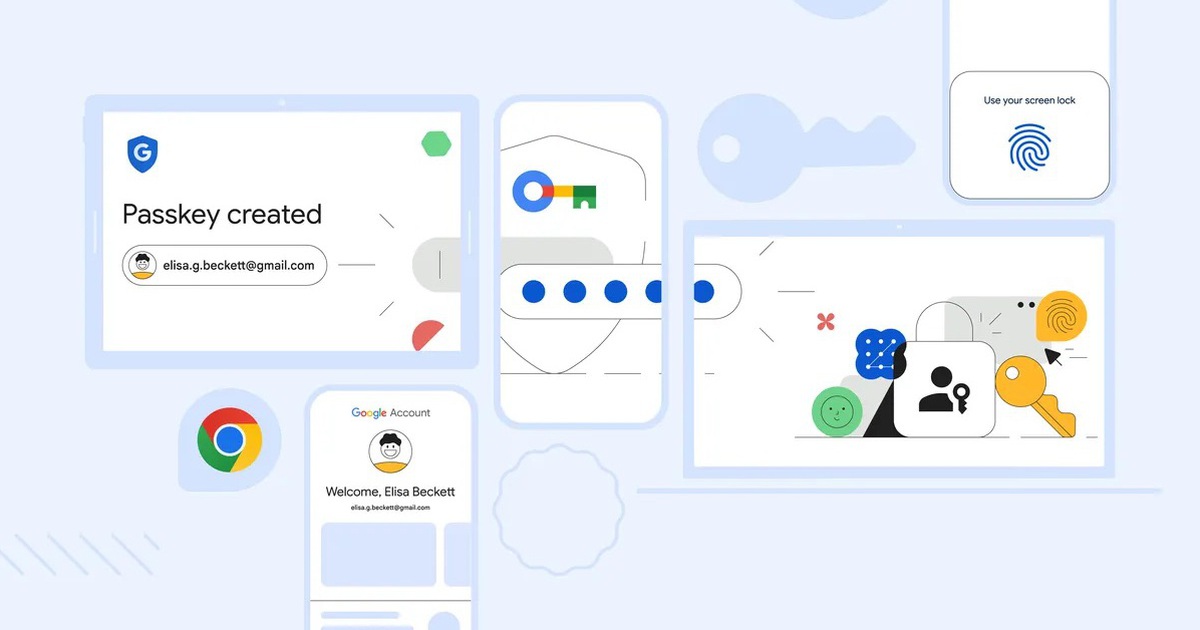
One of the most compelling advantages of Google Passkey is its ability to provide a truly seamless login experience across various devices. Once a passkey is created for an account and stored in Google Password Manager, it becomes available across all devices where the user is signed into their Google Account. This means you can create a passkey on your Android phone and then use it to log in on your Windows laptop, Mac, or even another mobile device, typically by simply confirming your identity with a fingerprint, face scan, or PIN.
For instance, if you’re on a desktop computer trying to log into a Google service or a third-party website that supports passkeys, you might be prompted to use a passkey. You can then use your nearby phone (linked to your Google Account) to approve the login request via its biometrics, eliminating the need to type anything on the desktop. This cross-device functionality eradicates the common frustration of needing to recall or manually input passwords on every new device or browser session.
Enhanced Security Against Phishing and Credential Stuffing
The primary driver behind passkeys is a dramatic improvement in security, particularly against the most prevalent forms of cyberattacks.
Phishing Resistance: Because passkeys don’t involve transmitting a password, and the private key never leaves your device, they are inherently resistant to phishing. Even if an attacker manages to trick you into visiting a fake website, your device will only attempt to use its passkey with the legitimate domain for which it was created. The underlying FIDO standards ensure that the passkey can only be used with the specific web origin it was registered to, making it impossible for a malicious site to trick your device into revealing credentials. This protects users from inadvertently exposing their login information to imposters.
Credential Stuffing Protection: Since there are no passwords to “stuff” (try against multiple accounts), passkeys entirely eliminate the threat of credential stuffing attacks, where attackers use leaked usernames and passwords from one breach to gain unauthorized access to accounts on other services. Each passkey is unique to a service, and its cryptographic nature means it cannot be “reused” in the same way a password can.
User Adoption and Accessibility
Google’s broad reach and integration capabilities are critical for driving passkey adoption. By making passkeys easily accessible and manageable through its widely used ecosystem (Android, Chrome, Google Accounts), Google is lowering the barrier to entry for millions. Users can manage their passkeys through Google Password Manager, making it straightforward to view, delete, or create new passkeys. The gradual rollout, alongside continued support for traditional passwords and 2FA, allows users to transition at their own pace. Furthermore, the intuitive biometric or PIN-based authentication aligns with familiar device unlocking patterns, reducing the learning curve for new users and making the experience feel more natural than remembering complex passwords. This focus on accessibility is crucial for widespread acceptance and the ultimate realization of a passwordless internet.
The Broader Implications for Tech & Innovation
Google’s commitment to passkeys, alongside initiatives from other tech giants like Apple and Microsoft, signals a pivotal moment for the future of digital authentication. This collaborative push towards a passwordless paradigm holds profound implications for security, user experience, and the very architecture of online services, driving significant innovation across the technology landscape.
Industry-Wide Adoption and the Passwordless Future
The collective endorsement of passkeys by major tech players like Google, Apple, and Microsoft is critical. This interoperability, built on the open FIDO standards, ensures that a passkey created on one platform can be used to log in on another, fostering a unified and seamless experience across the web. This cross-platform compatibility is essential for breaking down silos and accelerating widespread adoption by both end-users and developers. As more websites and applications integrate passkey support, the reliance on passwords will steadily diminish, leading to a truly passwordless future. This shift will free developers from the complexities and security burdens of managing password databases and verification systems, allowing them to focus on core product innovation. For users, it promises a simpler, more secure, and less frustrating online existence.
Impact on User Data Security and Privacy
Passkeys significantly bolster user data security and privacy. By eliminating passwords, they remove a major attack vector for data breaches. Stolen passkeys are non-existent in the traditional sense, as the private keys reside securely on individual devices and are never transmitted. Even if a service’s database were compromised, there would be no reusable passwords for attackers to steal. This means less sensitive user data for companies to protect, reducing their attack surface and compliance burden related to password handling. From a privacy perspective, passkeys don’t track user activity across sites in the way that some traditional authentication methods might, and they rely on local, on-device verification, giving users more direct control over their authentication process. The move away from centralized password databases towards distributed, device-centric authentication fundamentally enhances the privacy posture of online interactions.
Challenges and Future Developments
Despite their transformative potential, the path to universal passkey adoption still faces challenges. One key area is ensuring robust recovery mechanisms for users who lose all their authenticated devices or forget their device PINs/biometrics. While cloud synchronization helps mitigate this, comprehensive, user-friendly recovery flows are essential to prevent account lockout. Educating the vast user base about the benefits and mechanics of passkeys will also be an ongoing effort. Furthermore, backward compatibility for legacy systems and ensuring a smooth transition for existing users accustomed to passwords will require careful planning and execution by service providers.
Future developments in passkey technology will likely focus on enhancing device diversity (e.g., more secure hardware-based authenticators), improving management tools, and exploring advanced cryptographic techniques for even greater resilience against emerging threats. The continued collaboration within the FIDO Alliance and the proactive efforts of tech leaders like Google will be instrumental in overcoming these challenges and solidifying passkeys as the de facto standard for digital authentication in the next era of online innovation. The journey towards a truly passwordless and inherently more secure internet is well underway, with passkeys paving the way.