
The Innovative Tactics of Digital Deception
Phishing, a term derived from the analogy of “fishing” for sensitive information using deceptive lures, represents one of the most pervasive and technologically evolving cyber threats of our digital age. It is a sophisticated form of social engineering where attackers masquerade as trustworthy entities to trick individuals into divulging confidential data such as usernames, passwords, credit card details, or other personal identifiers. Far from being a static threat, phishing continually innovates, adapting to new technologies, communication platforms, and human behavioral patterns, making its understanding and defense a critical aspect of modern tech and innovation.
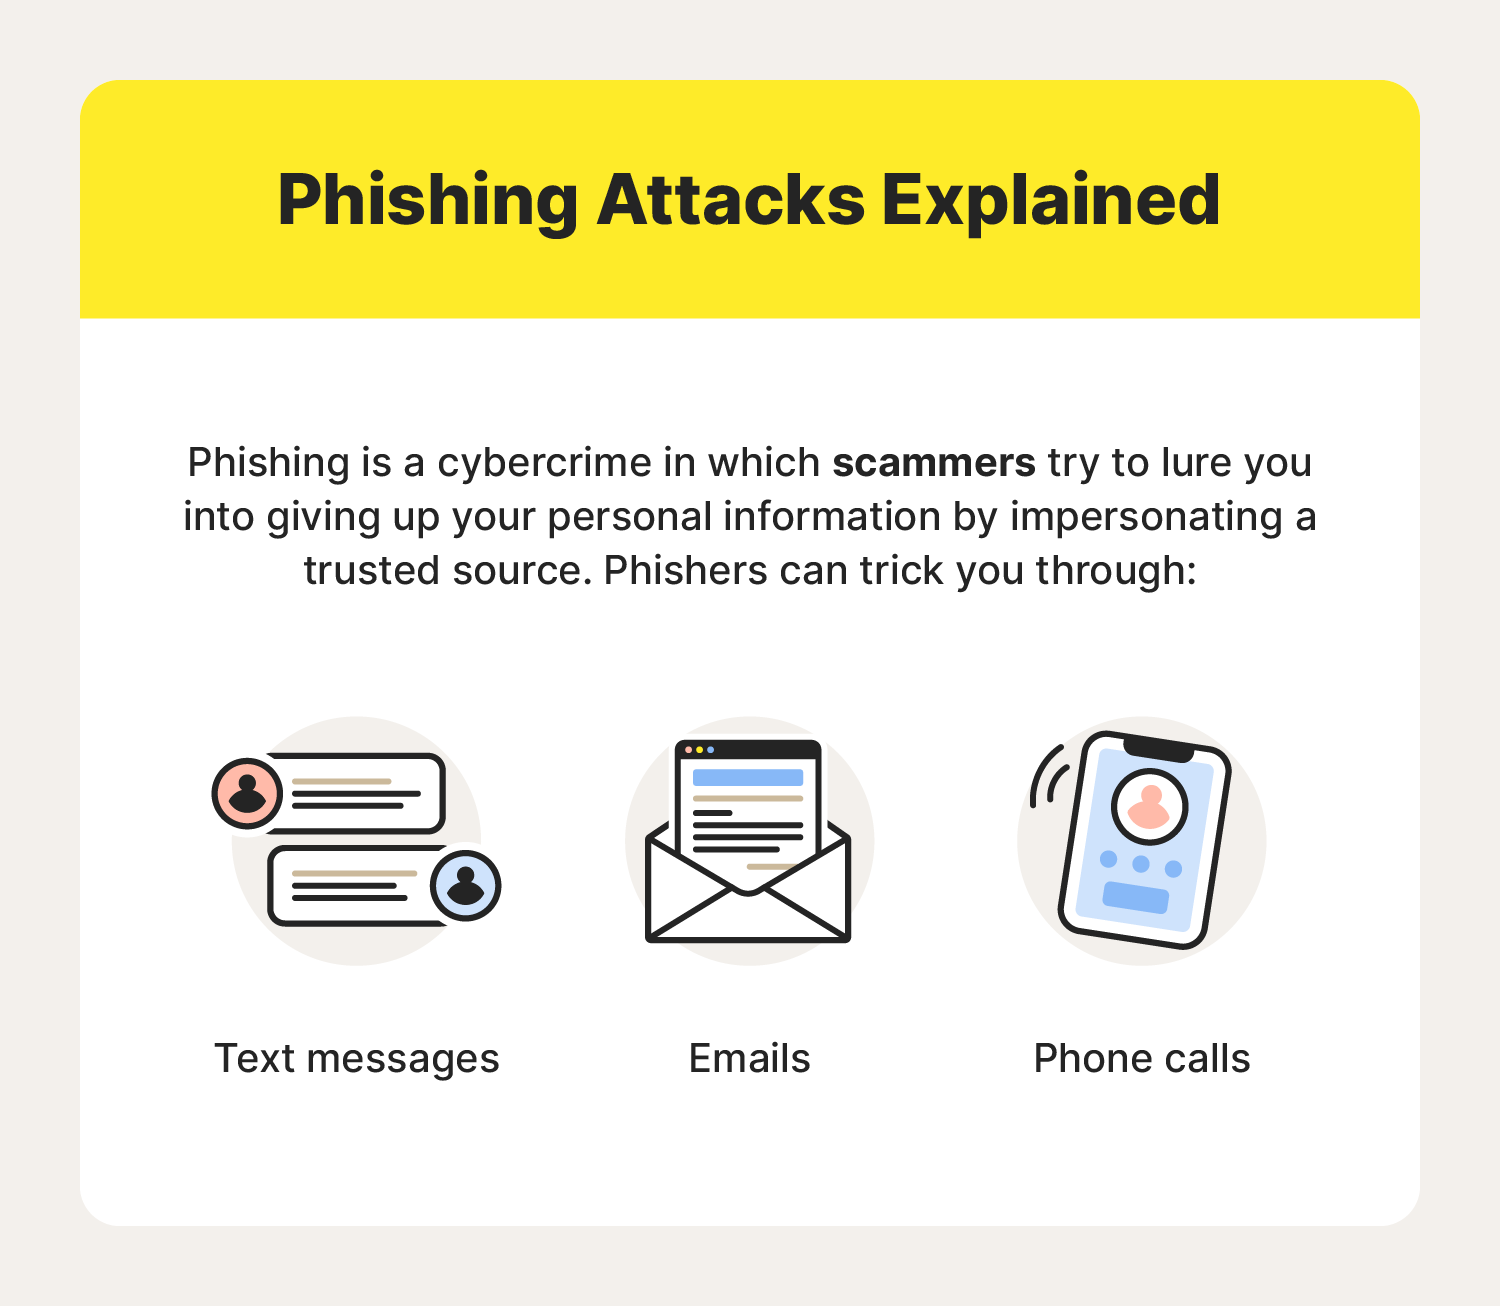
Crafting Convincing Lures: Email and Messaging Phishing
The most common vector for phishing attacks remains email. Attackers leverage sophisticated techniques to mimic legitimate organizations, often employing high-fidelity replicas of company logos, brand messaging, and even sender email addresses that appear authentic at first glance. These emails often contain urgent calls to action, threats of account suspension, or tempting offers designed to bypass critical thinking and prompt immediate clicks on malicious links or attachments. The innovation here lies in the ever-improving realism of these lures, driven by access to graphic design tools and an understanding of human psychology, often exploiting current events, popular trends, or anxieties. Beyond email, phishing has aggressively migrated to messaging platforms, giving rise to “smishing” (SMS phishing) and “vishing” (voice phishing). Smishing attacks distribute malicious links or requests for information via text messages, often pretending to be banks, package delivery services, or government agencies. Vishing involves fraudulent phone calls, where attackers impersonate technical support, law enforcement, or financial institutions to verbally extract sensitive data. The multi-channel approach significantly broadens the attack surface and requires robust, integrated security strategies.
Advanced Spear Phishing and Whaling Techniques
While traditional phishing casts a wide net, advanced variants like spear phishing and whaling are highly targeted, demonstrating an even greater degree of innovative social engineering. Spear phishing targets specific individuals or organizations, with attackers conducting extensive reconnaissance to gather personal information about their victims. This data, often gleaned from social media, corporate websites, or public records, allows them to craft highly personalized and credible messages that appear to come from known contacts or trusted internal sources. The precision and personalization make these attacks incredibly difficult to detect, as they often bypass generic spam filters and leverage existing trust relationships. Whaling is an even more specialized form of spear phishing, exclusively targeting high-value individuals within an organization, such as CEOs, CFOs, or other senior executives. These “whale” attacks aim to trick executives into authorizing large wire transfers or divulging highly sensitive corporate data, often by impersonating legal counsel, board members, or high-ranking government officials. The success of whaling attacks hinges on impeccable impersonation and a deep understanding of corporate hierarchies and communication flows, representing the apex of phishing innovation in terms of social engineering complexity.
Vishing and Smishing: Expanding the Attack Surface
The evolution of communication technologies has naturally led phishers to explore new attack vectors beyond email. Vishing (voice phishing) leverages VoIP and traditional telephone networks, where attackers use spoofed caller IDs to impersonate legitimate entities. These calls often employ sophisticated scripts designed to create a sense of urgency or fear, pushing victims to reveal banking details, social security numbers, or login credentials. The innovative aspect here often involves using automated calling systems, voice changers, and even pre-recorded messages that mimic official tones. Smishing (SMS phishing), similarly, utilizes text messages to deliver malicious links or solicit personal information. These messages are often designed to appear as critical alerts from banks, government agencies, or delivery services, playing on common anxieties or expectations. The ubiquity of mobile phones makes smishing an incredibly potent tool, as people are often less wary of links received via text message compared to email. The seamless integration of these methods across different communication channels demonstrates the attackers’ continuous innovation in exploiting human trust and technological convenience.
Cutting-Edge Technological Countermeasures
The relentless innovation in phishing tactics demands equally cutting-edge technological countermeasures. Cybersecurity firms and researchers are constantly developing advanced tools and strategies to detect, prevent, and respond to these sophisticated attacks, often leveraging artificial intelligence, machine learning, and behavioral analytics.
AI-Driven Phishing Detection and Threat Intelligence
Artificial Intelligence and Machine Learning are revolutionizing the fight against phishing. AI algorithms can analyze vast quantities of email data, including sender reputation, content, linguistic patterns, URL structures, and header information, to identify subtle indicators of phishing that might evade traditional rule-based filters. ML models can be trained on millions of benign and malicious emails, learning to distinguish between genuine and fraudulent communications with high accuracy. This includes identifying zero-day phishing attacks—new, previously unseen variants—by recognizing anomalous characteristics. Threat intelligence platforms, often powered by AI, continuously aggregate data from global sources, sharing information about new phishing campaigns, malicious domains, and attack methodologies. This enables organizations to proactively block known threats and update their defense systems in real-time, staying a step ahead of attackers. The innovation lies in the ability of these systems to learn, adapt, and predict, transforming reactive security into a more proactive and intelligent defense posture.
Behavioral Analytics and Adaptive Authentication
Beyond mere detection, innovative security solutions are employing behavioral analytics and adaptive authentication to strengthen defenses. Behavioral analytics systems monitor user and network activity patterns to establish a baseline of “normal” behavior. Any deviation from this baseline—such as unusual login locations, access times, or data transfer patterns—can trigger alerts or additional verification steps. This is particularly effective against highly targeted spear phishing attacks where credentials may be compromised but the subsequent access attempts appear suspicious. Adaptive authentication, a direct response to the vulnerability of static passwords, dynamically adjusts the authentication requirements based on the context of the login attempt. For instance, if a user attempts to log in from an unfamiliar device or geographic location, the system might demand multi-factor authentication (MFA) or an additional biometric verification, even if the password is correct. This layered, context-aware approach represents significant innovation in securing access points, making it exponentially harder for phishers to exploit stolen credentials.
Secure Email Gateways and Anti-Spoofing Innovations
Secure Email Gateways (SEGs) serve as the first line of defense for organizations, filtering incoming emails before they reach employee inboxes. Modern SEGs incorporate a suite of advanced technologies, including sandboxing for suspicious attachments, URL rewriting and reputation checks for malicious links, and content analysis for phishing indicators. Innovation in SEGs includes predictive threat intelligence that anticipates new attack vectors and advanced anti-spoofing mechanisms. Protocols like SPF (Sender Policy Framework), DKIM (DomainKeys Identified Mail), and DMARC (Domain-based Message Authentication, Reporting, and Conformance) are critical anti-spoofing technologies. DMARC, in particular, empowers domain owners to specify how recipient email servers should handle unauthenticated emails purporting to be from their domain, effectively blocking spoofed emails from reaching their intended targets. The continuous enhancement of these protocols and their integration into sophisticated gateway solutions represents a vital innovation in preventing impersonation and brand abuse, directly countering one of phishing’s core strategies.
The Intersection of Phishing and Emerging Tech Risks
As technology evolves, so do the opportunities for phishing. Emerging technologies introduce new vulnerabilities and expand the attack surface, creating a dynamic challenge for cybersecurity innovators.
Cloud-Based Attacks and Supply Chain Vulnerabilities
The widespread adoption of cloud computing has inadvertently created new avenues for phishing attacks. Phishers now frequently target cloud service credentials, knowing that access to a single cloud account can unlock a trove of sensitive data, applications, and infrastructure. Cloud-based phishing often mimics login pages for popular cloud platforms (e.g., Microsoft 365, Google Workspace, AWS), exploiting trust in these widely used services. Furthermore, the increasing interconnectedness of digital supply chains presents a significant vulnerability. A successful phishing attack against a third-party vendor or supplier can provide attackers with a foothold into larger, more secure organizations, leading to supply chain compromises. Innovating security in the cloud and across supply chains requires a shift towards zero-trust architectures, continuous monitoring, and robust identity and access management solutions that can withstand sophisticated, multi-stage phishing campaigns.
The Challenge of Deepfakes and AI-Generated Phishing
One of the most concerning emerging threats is the potential for deepfake technology and other AI-generated content to enhance phishing attacks. Deepfakes, which use AI to create highly realistic synthetic media—images, audio, and video—could be weaponized to create incredibly convincing vishing or video-based phishing attempts. Imagine an attacker creating an AI-generated voice or video of a CEO giving a fraudulent instruction, or a deepfake video appearing to be a legitimate news report to distribute misinformation and malicious links. Similarly, advanced AI models like large language models (LLMs) can generate highly persuasive, grammatically perfect, and contextually relevant phishing emails at scale, overcoming the linguistic tells that often betray malicious intent. Counteracting these AI-enhanced threats requires a new generation of AI-driven defenses capable of detecting synthetic media and identifying subtle inconsistencies that human eyes or traditional filters might miss, pushing the boundaries of detection technology.
Cultivating a Culture of Cyber Resilience and Innovation
Ultimately, the fight against phishing is not solely a technological battle; it requires a holistic approach that integrates technology with human awareness and robust organizational policies.
Employee Training and Security Awareness Initiatives
Even the most advanced technological defenses can be undermined by human error. Continuous, engaging, and up-to-date employee training is paramount. These programs must move beyond simply identifying obvious phishing attempts, instead focusing on the evolving tactics of spear phishing, whaling, and new attack vectors. Training should simulate real-world phishing scenarios, provide regular refreshers, and clearly communicate the latest threats. Fostering a culture of security awareness means empowering employees to be the first line of defense, encouraging them to question suspicious communications, report potential phishing attempts, and understand the crucial role they play in protecting organizational assets. Innovation in this area includes gamified training modules, interactive simulations, and micro-learning approaches that deliver timely security tips, enhancing engagement and retention.

Collaborative Security Models and Regulatory Frameworks
The global nature of phishing necessitates collaborative security models. Information sharing among organizations, industries, and national cybersecurity agencies is vital for rapidly identifying and mitigating new threats. Threat intelligence feeds, joint task forces, and public-private partnerships play a crucial role in staying ahead of attackers. Regulatory frameworks, such as GDPR, CCPA, and various industry-specific compliance standards, impose strict requirements for data protection and incident response, incentivizing organizations to invest in robust anti-phishing measures. These regulations also mandate reporting of breaches, which, while challenging, contributes to a collective understanding of attack patterns. Future innovation will increasingly focus on international cooperation, standardized threat intelligence sharing protocols, and adaptive regulatory frameworks that can keep pace with the rapid evolution of cyber threats, ensuring a resilient global digital ecosystem against the pervasive and innovative challenge of phishing.