
The intricate web of the internet, with its myriad devices, services, and data flows, relies on a foundational system that often operates invisibly yet is absolutely critical: the Domain Name System (DNS). Far from being a mere technical detail, understanding DNS settings is paramount for anyone navigating the landscape of modern tech and innovation, especially as devices from autonomous drones to smart sensors become increasingly interconnected. It underpins virtually every digital interaction, from accessing cloud-based AI processing for aerial imagery to ensuring reliable telemetry data transmission for remote operations.
The Internet’s Address Book: Understanding DNS Fundamentals
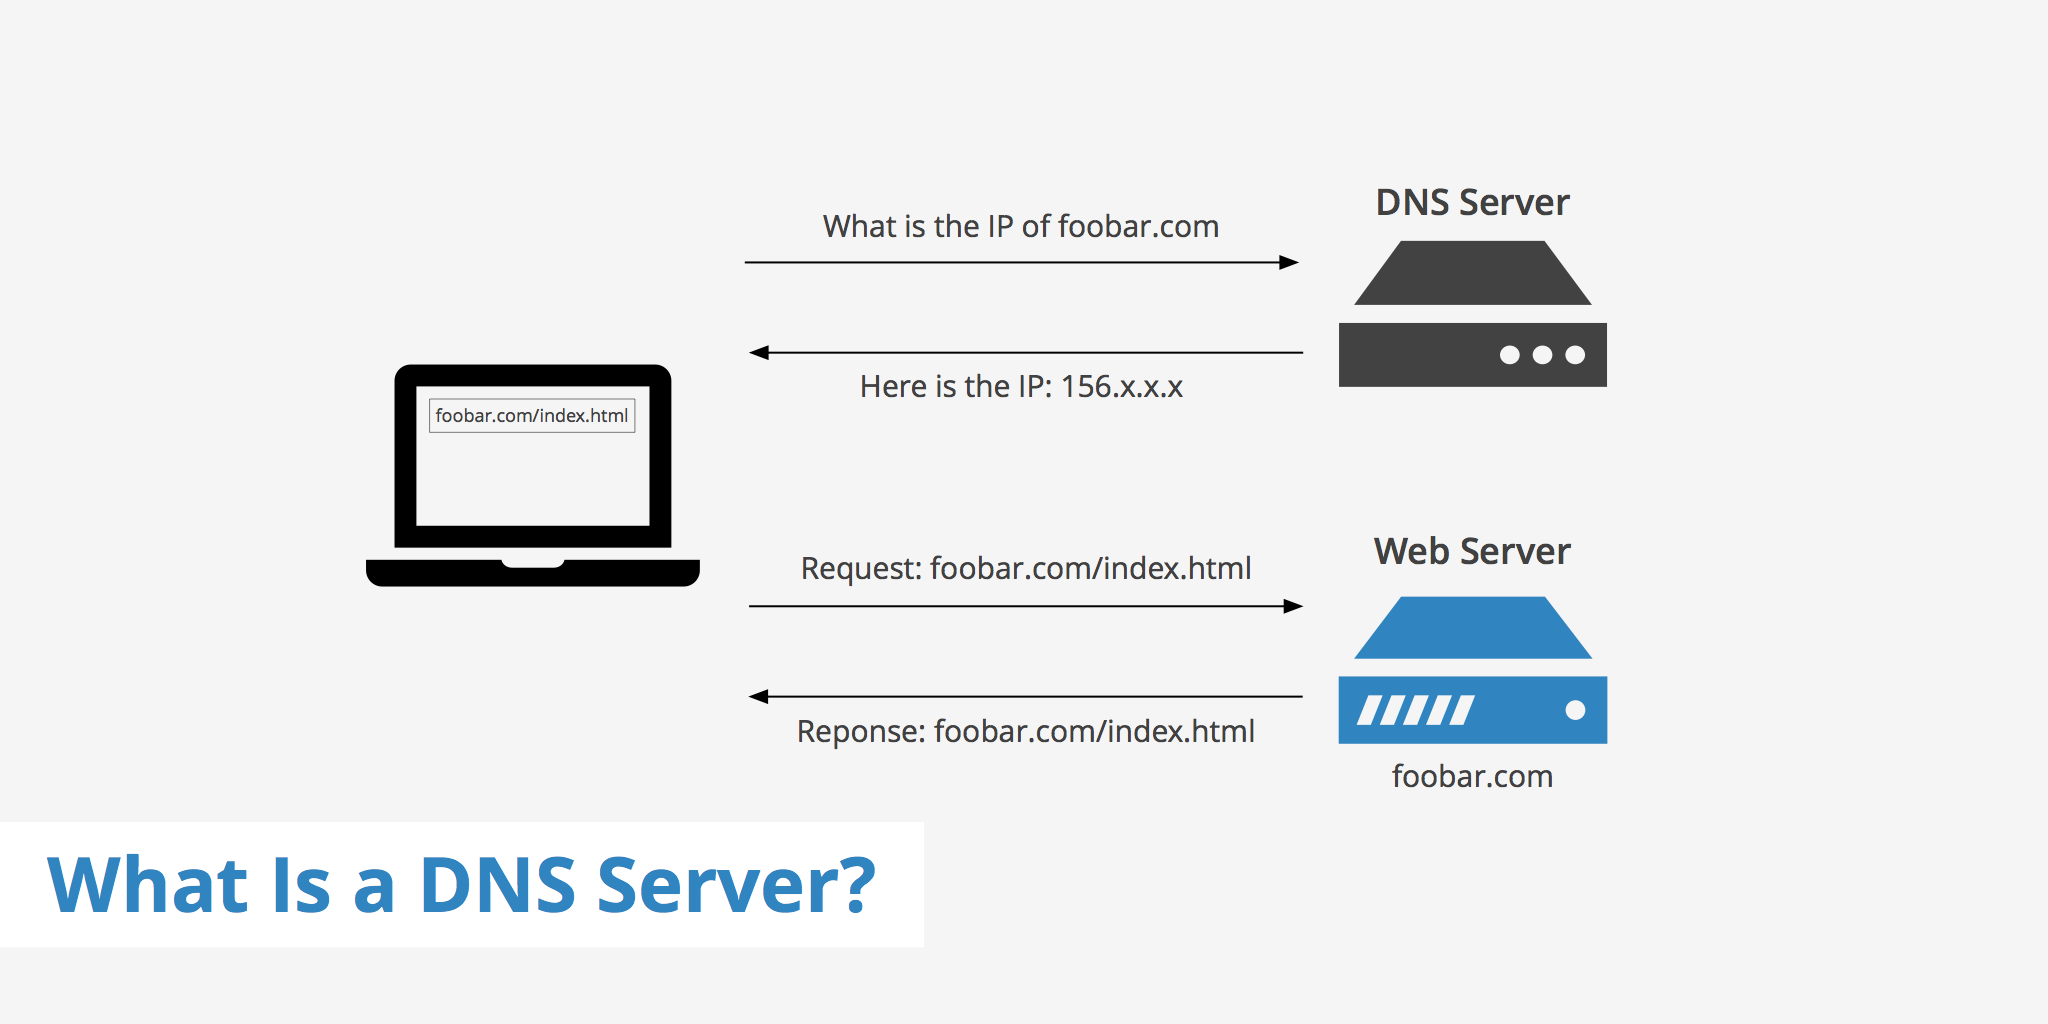
At its core, DNS functions as the internet’s decentralized phonebook. Humans interact with the internet using human-readable domain names, such as “example.com,” while computers and network devices communicate using numerical Internet Protocol (IP) addresses, like “192.0.2.1.” The primary role of DNS is to translate these memorable domain names into their corresponding IP addresses, allowing devices to locate and connect to each other across the global network. Without DNS, remembering a string of numbers for every website or service would be an impossible task, effectively crippling the modern internet and, by extension, countless technological innovations.

Domain Names vs. IP Addresses
A domain name is a unique, human-friendly label that identifies a specific website or service on the internet. It provides an intuitive way for users to recall and access online resources. Domain names are hierarchical, comprising several levels, with the Top-Level Domain (TLD) (e.g., .com, .org, .net) at the highest level, followed by second-level domains (e.g., “example” in example.com), and potentially subdomains (e.g., “blog” in blog.example.com).
IP addresses, conversely, are numerical labels assigned to every device connected to a computer network that uses the Internet Protocol for communication. There are two primary versions: IPv4 (e.g., 192.0.2.1), a 32-bit address system that is rapidly running out of unique addresses, and IPv6 (e.g., 2001:0db8:85a3:0000:0000:8a2e:0370:7334), a 128-bit system designed to accommodate the exponential growth of internet-connected devices, including the burgeoning Internet of Things (IoT) and autonomous systems. While domain names offer convenience, IP addresses are the actual network coordinates that facilitate data routing and delivery.
The DNS Resolution Process
When a user or a connected device attempts to access a resource using a domain name, a complex yet rapid DNS resolution process unfolds:
- Request Initiation: The device (e.g., a drone’s ground control station or a remote sensing platform) sends a query to a resolver (typically provided by an Internet Service Provider – ISP) for the IP address corresponding to the desired domain name.
- Recursive Resolver Query: The resolver, if it doesn’t have the answer cached, forwards the query to a root name server. There are 13 logical root servers globally, forming the top of the DNS hierarchy.
- TLD Name Server Redirection: The root server doesn’t know the full IP address but directs the resolver to the authoritative name server for the Top-Level Domain (TLD) – for example, the .com name server.
- Authoritative Name Server Query: The resolver then queries the TLD name server, which in turn directs it to the authoritative name server for the specific domain (e.g., example.com). This authoritative server holds the definitive record linking the domain name to its IP address.
- IP Address Retrieval: The authoritative name server returns the IP address to the recursive resolver.
- Response to Client: The recursive resolver then sends the IP address back to the original device, which can now initiate a direct connection to the target server using its IP address.
This entire process, involving multiple queries and responses across different servers, typically occurs in milliseconds, illustrating the efficiency required for modern interactive applications and real-time data flows essential for innovations like AI-powered autonomous flight or remote sensing data aggregation.
Types of DNS Servers
The DNS ecosystem is comprised of several types of servers, each with a distinct role:
- DNS Recursive Resolver: This is the server that clients (devices) first query. It’s responsible for making the series of queries to find the correct IP address and then returning the answer to the client. Most ISPs provide these resolvers, but public options like Google DNS (8.8.8.8) or Cloudflare DNS (1.1.1.1) are also popular.
- Root Name Server: These servers are at the top of the DNS hierarchy. They do not store domain name information but rather direct resolvers to the appropriate TLD name servers.
- TLD Name Server: These servers manage information for all domain names under a specific Top-Level Domain (e.g., .com, .org, .gov). They direct resolvers to the authoritative name server for the specific domain requested.
- Authoritative Name Server: These servers store the actual DNS records for a particular domain. When a resolver reaches an authoritative name server, it receives the definitive IP address for the requested domain name.
Why DNS Matters in Tech & Innovation
In the context of rapidly advancing tech and innovation, DNS is not merely a background service; it is a critical enabler. From facilitating communication for intelligent systems to ensuring the integrity of data streams, its proper functioning is indispensable for the operational reliability and security of cutting-edge applications.
Enabling Cloud Connectivity for Drones and IoT
Modern technological ecosystems, particularly those involving drones, IoT devices, and remote sensing platforms, are heavily reliant on cloud computing. Drones transmit vast amounts of data—from high-resolution imagery and video to sensor readings and telemetry—to cloud servers for processing, analysis, and storage. IoT devices, deployed across diverse environments, communicate with cloud platforms for data aggregation, command and control, and firmware updates.
DNS is the lynchpin for establishing these cloud connections. When a drone or IoT gateway needs to upload data to a specific cloud endpoint (e.g., “data-ingest.mycloudprovider.com”), DNS resolves this human-readable address into the correct IP address of the cloud server. Any misconfiguration or performance issue with DNS directly impacts the ability of these devices to connect to their respective cloud services, leading to data loss, delayed processing, or outright operational failure. For applications requiring real-time data streaming, such as autonomous flight control or critical infrastructure monitoring, robust DNS resolution is non-negotiable.
Facilitating Remote Operations and Telemetry
Innovation in areas like remote piloting, autonomous navigation, and predictive maintenance hinges on reliable communication. For instance, an operator controlling a drone from a remote location requires constant, low-latency telemetry data (GPS coordinates, altitude, battery status, speed) to make informed decisions or for an AI system to execute autonomous flight paths. Similarly, remote sensing applications demand precise data transmission to ground stations or processing centers.
DNS plays a crucial role in ensuring that these communication channels are established correctly and efficiently. It enables the drone or ground control station to locate and connect to the correct command-and-control servers or data relay points. Poor DNS performance can introduce latency, leading to delays in command execution or gaps in telemetry data, which can be critical for safety and operational efficiency in drone delivery, search and rescue, or precision agriculture. Optimized DNS settings can help reduce these latencies by directing traffic to the closest or fastest available server.
Secure Communication and Digital Identity
Security is paramount in advanced tech applications, especially when dealing with sensitive data or mission-critical operations. DNS is integral to establishing secure communication channels through technologies like SSL/TLS (used for HTTPS). When a drone app connects to its backend server via HTTPS, DNS first resolves the server’s domain name to an IP address. During the subsequent secure connection handshake, the server presents a digital certificate that is cryptographically tied to its domain name. DNSSEC (DNS Security Extensions) adds another layer of security to DNS itself, preventing attackers from redirecting traffic to malicious servers by tampering with DNS records.
By ensuring the authenticity of domain name resolution, DNS helps guarantee that devices are communicating with legitimate servers and not imposters. This is vital for protecting data integrity, preventing unauthorized access, and maintaining the digital identity of connected systems, which is increasingly relevant in a world where autonomous systems and sensitive data are routinely exchanged over the internet.
Configuring and Optimizing DNS Settings
While often managed automatically, the ability to configure and optimize DNS settings offers significant advantages for enhanced performance, security, and access control in advanced technological deployments. Understanding these configurations is key for system administrators, developers, and tech enthusiasts.
Common DNS Settings and Their Impact
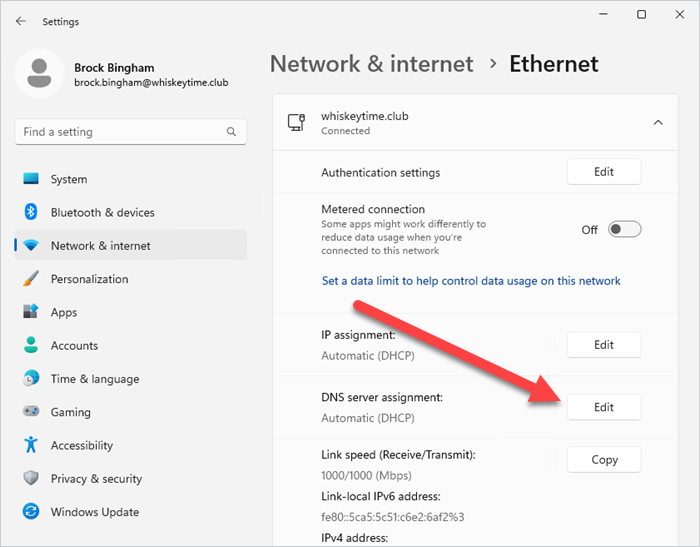
Most devices obtain DNS settings automatically from a router or network gateway, which in turn gets them from an ISP. These automatic settings typically point to the ISP’s recursive DNS resolvers. Basic settings include:
- Primary DNS Server: The first DNS server a device attempts to query.
- Secondary DNS Server: A backup DNS server used if the primary fails to respond.
The impact of these settings is profound:
- Resolution Speed: Faster DNS servers can reduce the time it takes to look up IP addresses, leading to quicker loading times for web applications and faster connection establishments for remote services.
- Reliability: Redundant DNS servers ensure that network services remain accessible even if one server experiences an outage.
- Security: Some DNS providers offer enhanced security features, such as blocking known malicious domains (malware, phishing sites) at the DNS level, providing an initial layer of defense for connected devices.
- Content Filtering: Certain DNS services can be configured to filter content, blocking access to specific categories of websites or applications, which can be useful in controlled environments or for parental controls.
Custom DNS Servers: Benefits and Considerations
Users and organizations can manually configure their devices or network routers to use custom DNS servers instead of the default ISP-provided ones. Popular public options include:
- Google Public DNS (8.8.8.8, 8.8.4.4): Known for its speed and reliability.
- Cloudflare DNS (1.1.1.1, 1.0.0.1): Emphasizes privacy and speed.
- OpenDNS (208.67.222.222, 208.67.220.220): Offers customizable filtering and security features.
Benefits of using custom DNS servers:
- Improved Performance: Often, public DNS servers are faster than ISP defaults, especially if they have edge locations closer to the user or better peering with popular content networks.
- Enhanced Security: Many custom DNS providers offer built-in malware and phishing protection, blocking access to harmful domains. DNSSEC validation can also be enabled to prevent DNS spoofing.
- Privacy: Some providers prioritize user privacy by not logging queries or selling user data.
- Content Filtering/Parental Controls: Services like OpenDNS allow granular control over what types of content can be accessed, critical for managing connected devices in educational or sensitive environments.
- Bypassing ISP Restrictions: In some cases, custom DNS can bypass ISP-level content blocking or censorship, though this depends on local regulations.
Considerations: While beneficial, ensure the chosen custom DNS provider is reputable and reliable, as all your internet traffic will pass through their resolvers. Misconfigured custom DNS can lead to connectivity issues.
Troubleshooting DNS-Related Issues in Connected Devices
DNS problems are a common culprit for connectivity issues, particularly with devices that rely heavily on consistent network access. For drones, IoT sensors, or remote AI processing units, a DNS hiccup can be devastating.
Common symptoms of DNS issues include:
- “Server not found” or “website cannot be reached” errors, even if the internet connection appears active.
- Slow loading times for web applications or data streams.
- Inability to connect to specific cloud services or remote servers.
- Firmware update failures.
- Inconsistent connectivity or dropped connections for remote-controlled systems.
Troubleshooting steps:
- Flush DNS Cache: Devices store a local cache of recently resolved DNS entries. Corrupted or outdated cache entries can cause problems. On Windows, use
ipconfig /flushdns; on macOS/Linux,sudo killall -HUP mDNSResponderorsudo systemd-resolve --flush-caches. - Verify DNS Settings: Check the device’s network settings or router configuration to ensure DNS servers are correctly specified. Ensure there are no typos.
- Test with Public DNS: Temporarily switch to a public DNS server (e.g., Google DNS 8.8.8.8) to see if the issue resolves. This helps determine if the problem lies with your ISP’s DNS servers.
- Ping IP Addresses: Try to
pinga known IP address (e.g., 8.8.8.8) to verify basic internet connectivity. If this works but domain names don’t resolve, the issue is likely DNS. - Use Diagnostic Tools: Tools like
nslookupordig(on Linux/macOS) can be used to query specific DNS servers for domain resolution and diagnose where the breakdown occurs. - Check Router/Firewall: Ensure no firewall rules or router settings are blocking DNS traffic (port 53 UDP/TCP).
For mission-critical applications or large-scale IoT deployments, continuous DNS monitoring tools can preemptively identify and mitigate potential resolution issues, ensuring uninterrupted operation.
The Future of DNS in an Evolving Tech Landscape
As technology continues its rapid evolution, particularly with the proliferation of AI, autonomous systems, and edge computing, DNS is also adapting and innovating. New protocols and architectural considerations are emerging to address growing demands for privacy, security, and efficiency.
DNS Over HTTPS (DoH) and DNS Over TLS (DoT)
Traditional DNS queries are sent unencrypted, making them susceptible to eavesdropping and manipulation (like DNS spoofing) by anyone on the network path. This poses a significant privacy and security risk, especially in the context of sensitive data from advanced tech.
DNS Over HTTPS (DoH) and DNS Over TLS (DoT) are emerging protocols designed to encrypt DNS queries, safeguarding them from interception and tampering.
- DoT encrypts DNS traffic using TLS (Transport Layer Security) over a dedicated port (853).
- DoH encrypts DNS traffic using HTTPS (HTTP Secure) over port 443, making it indistinguishable from regular web traffic.
The benefits for tech innovation are substantial:
- Enhanced Privacy: Prevents ISPs, governments, or malicious actors from monitoring DNS queries, which can reveal browsing history, application usage, and even specific drone communication patterns.
- Improved Security: Makes DNS spoofing and man-in-the-middle attacks much harder, ensuring that autonomous systems and cloud services connect to legitimate endpoints.
- Bypassing Censorship: DoH, in particular, can be harder to block due to its reliance on standard HTTPS port 443, offering a more resilient path for critical communication in restricted environments.
Adoption of DoH and DoT is growing in browsers, operating systems, and specialized network hardware, offering a more secure and private foundation for the next generation of connected devices.
Decentralized DNS and Blockchain Integration
The current DNS system, while robust, is centralized around a few key entities (root servers, TLD registries). This centralization presents potential vulnerabilities, including single points of failure, censorship, and data control issues. Decentralized DNS initiatives, often leveraging blockchain technology, aim to address these concerns.
Projects like Handshake, Ethereum Name Service (ENS), and Unstoppable Domains are exploring ways to create a more resilient, censorship-resistant, and user-controlled domain naming system. By storing domain records on a distributed ledger, these systems offer:
- Increased Resilience: No single point of failure; domains remain accessible even if traditional DNS infrastructure is compromised.
- Censorship Resistance: Difficult for any single entity to remove or block domain names.
- User Control: Users often have greater ownership and control over their domain names without reliance on traditional registrars.
While still nascent, decentralized DNS holds promise for future tech ecosystems, particularly for Web3 applications, immutable data storage, and sovereign digital identities for autonomous agents and sensitive IoT deployments where traditional centralized control is undesirable or risky.
Impact on Edge Computing and Autonomous Systems
Edge computing, where data processing occurs closer to the source (e.g., on a drone itself or a local gateway), is a cornerstone of future autonomous systems and real-time AI. While edge processing reduces reliance on constant cloud connectivity, DNS remains critical for initial setup, periodic synchronization, firmware updates, and hybrid cloud/edge architectures.
- Service Discovery at the Edge: As more microservices and localized processing units are deployed at the edge, efficient DNS-like service discovery mechanisms will be essential for these components to locate and communicate with each other, often within dynamic, self-healing networks.
- Reliable Software Updates: Autonomous systems require regular software and AI model updates. DNS ensures that these systems can reliably connect to update servers, fetching the latest patches and enhancements critical for performance and security.
- Seamless Cloud Offload: When edge systems need to offload data or complex computations to the cloud, robust DNS ensures seamless and efficient handovers, maintaining continuity of operations.
The evolution of DNS, with its focus on enhanced security, privacy, and decentralization, will continue to be a silent but powerful enabler for the next wave of technological innovation, providing the fundamental addressing and discovery services that connected devices and intelligent systems critically depend on.