Understanding IP Addresses and Network Communication
In the vast, interconnected world of modern technology, data flows constantly between devices, from smartphones and servers to complex autonomous systems. At the heart of this communication lies the Internet Protocol (IP), a fundamental set of rules governing how data packets are formatted and sent over a network. Every device connected to the internet, or even a local network, possesses a unique identifier known as an IP address. This address is akin to a postal address for data, ensuring that information sent from one point reliably reaches its intended destination.
The Role of IP Addresses
An IP address serves two primary functions: identification and location addressing. It identifies a network interface of a computer or device on a network, allowing other devices to distinguish it from countless others. More importantly, it provides the necessary addressing information for data packets to traverse the intricate web of routers and switches, ultimately arriving at the correct host. Without IP addresses, the internet as we know it would cease to function, as there would be no way to direct traffic efficiently and accurately. Modern IP addresses come in two main forms: IPv4 (e.g., 192.168.1.1) and IPv6 (e.g., 2001:0db8:85a3:0000:0000:8a2e:0370:7334), with IPv6 designed to accommodate the exponential growth of connected devices.
Packet Transmission Basics
When you send an email, stream a video, or simply browse a webpage, your data is broken down into small units called packets. Each packet contains not only a segment of the original data but also crucial header information. This header includes the source IP address (your device’s address) and the destination IP address (the server’s address), along with other details like the protocol being used, sequence numbers, and checksums for error detection. These packets then embark on a journey across various network devices, with each router inspecting the destination IP address to determine the optimal path for forwarding the packet closer to its goal. This seemingly simple process underpins all digital communication, relying heavily on the integrity of the source and destination IP addresses within each packet.
The Mechanics of IP Spoofing
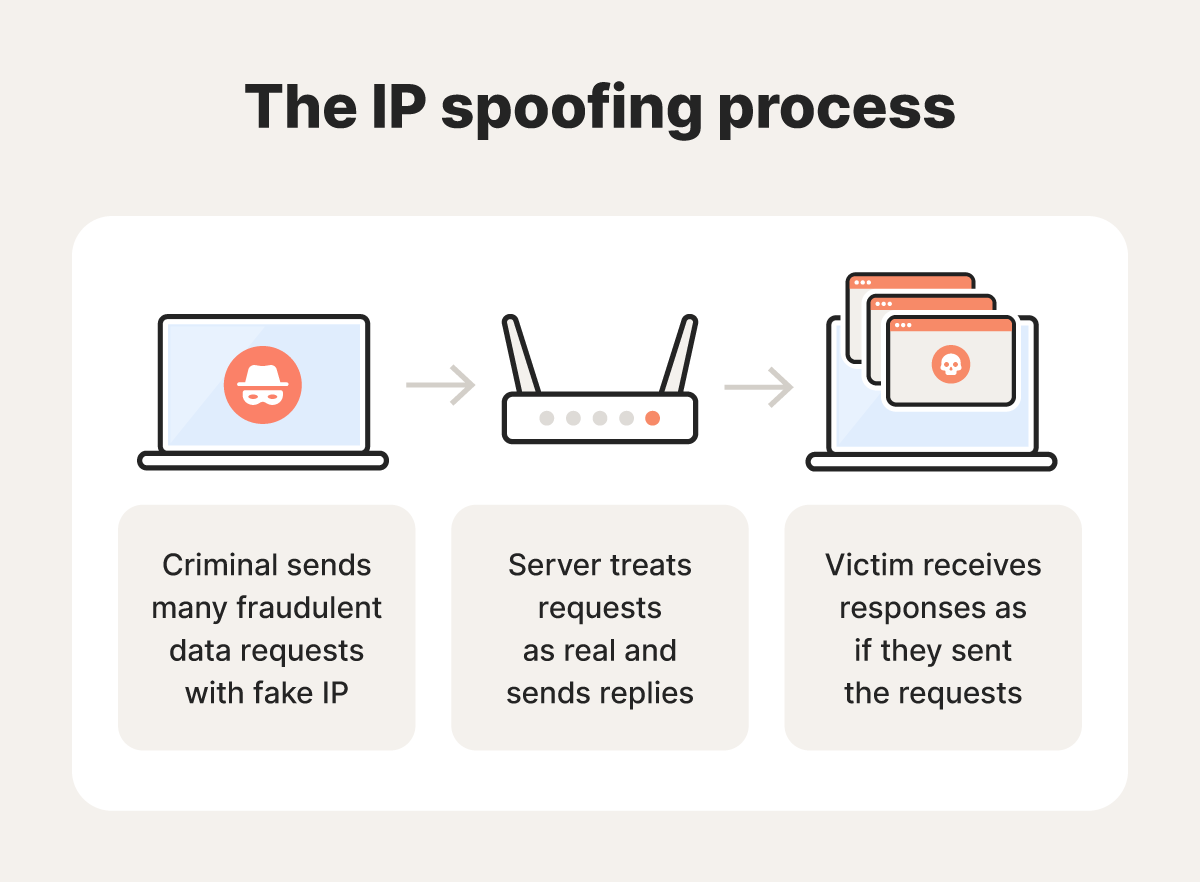
IP spoofing is a technique where an attacker crafts IP packets with a falsified source IP address, making the packet appear to originate from a legitimate, trusted host on the network. This deceptive practice is a cornerstone for various types of cyberattacks, leveraging the trust mechanisms inherent in many network protocols and applications. By manipulating the source IP address, an attacker can bypass security measures, gain unauthorized access, or obscure their true identity.
How Spoofing Works
At its core, IP spoofing exploits the stateless nature of IP itself. The Internet Protocol, by design, does not inherently verify the source IP address listed in a packet’s header. When a device sends a packet, it simply includes its own IP address as the source. A receiving device generally accepts this information at face value, assuming the stated source is genuine. An attacker, using specialized software or tools, can manually construct IP packets and insert any desired IP address into the source field before sending them into the network.
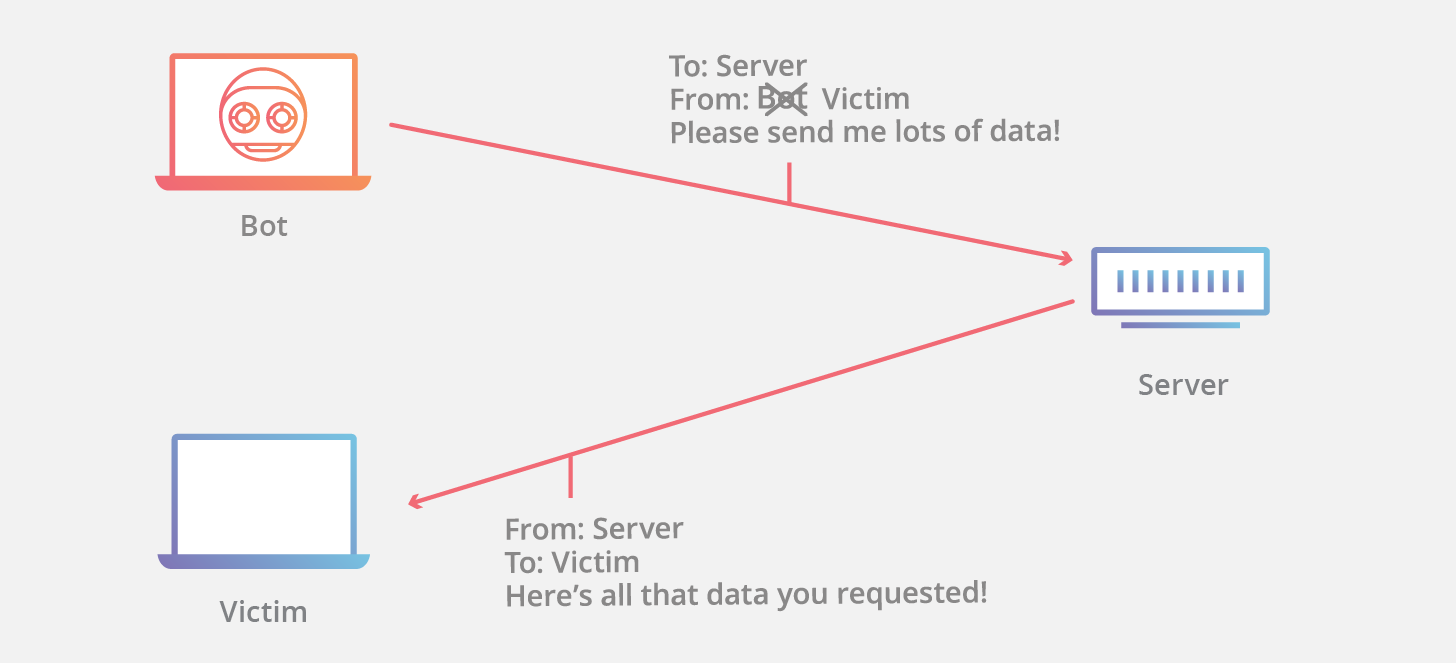
The most critical challenge for an attacker performing IP spoofing is managing the response. If a server receives a spoofed packet and sends a reply, that reply will be directed back to the spoofed source IP address, not the attacker’s actual IP. This is where different attack methodologies come into play. In some scenarios, the attacker doesn’t care about the response (e.g., a simple DoS attack). In others, they might employ techniques like blind spoofing, where they guess responses or rely on information gathered through other means, or more sophisticated methods like man-in-the-middle attacks where they can intercept and reroute traffic.
Types of IP Spoofing
While the basic principle remains the same, IP spoofing can manifest in several forms depending on the attacker’s objective and network topology:
- Non-Blind Spoofing: This occurs when the attacker is on the same local network segment as the victim and can observe the network traffic, including the responses to spoofed packets. This allows them to effectively participate in a communication session by intercepting replies meant for the spoofed address. This is often achieved through ARP spoofing, a related technique that manipulates the Address Resolution Protocol to redirect traffic.
- Blind Spoofing: In this more challenging scenario, the attacker is not on the same network segment and cannot see the replies to their spoofed packets. They must guess sequence numbers, acknowledgment numbers, and other session-related parameters to successfully inject commands or data into an ongoing communication. This is significantly more difficult but not impossible, especially against systems with predictable session parameters.
- IP-in-IP Encapsulation (Tunneling): While not strictly an attack vector in itself, IP-in-IP tunneling involves encapsulating an IP packet within another IP packet. This can be used legitimately for VPNs or network overlays, but it can also be exploited. An attacker might encapsulate a spoofed packet inside a legitimate one, making it harder for simple firewalls to detect the spoofed inner packet.
- Reflective Spoofing: This method is often used in Distributed Denial-of-Service (DDoS) attacks. Attackers send spoofed requests to a large number of legitimate, high-bandwidth servers (reflectors) with the victim’s IP address as the source. These reflectors then send large responses back to the victim, overwhelming their network resources.
Malicious Applications and Impact
IP spoofing is a foundational technique for many insidious cyberattacks, enabling attackers to mask their identity, bypass security controls, and disrupt services. Its impact can range from temporary service outages to complete data breaches and system compromise.
Denial-of-Service (DoS/DDoS) Attacks

One of the most common and impactful uses of IP spoofing is in Denial-of-Service (DoS) and Distributed Denial-of-Service (DDoS) attacks. In a DoS attack, an attacker floods a target system with an overwhelming volume of traffic, preventing legitimate users from accessing services. With IP spoofing, the attacker can send these malicious packets with falsified source IP addresses. This makes it incredibly difficult to trace the attack back to its true origin, complicating mitigation efforts.
DDoS attacks amplify this by coordinating multiple compromised machines (a botnet) to launch a synchronized attack. Each bot sends spoofed packets, making the source of the attack appear to come from hundreds or thousands of different, non-existent or innocent IP addresses. Common types include SYN flood attacks, where attackers send a barrage of SYN (synchronize) requests with spoofed IPs, exhausting the target server’s connection resources. Another variant is the aforementioned reflective DDoS, where spoofed requests are sent to third-party services (e.g., NTP, DNS servers), which then amplify and reflect the traffic towards the victim.
Man-in-the-Middle Attacks and Session Hijacking
While direct man-in-the-middle (MitM) attacks often involve ARP spoofing at the local network level, IP spoofing can be a component in more complex scenarios to hijack communication sessions. In a session hijacking attack, an attacker takes over an existing legitimate communication session between two parties. If an attacker can successfully predict or obtain sequence numbers and acknowledgment numbers, they can inject spoofed packets that appear to come from one of the legitimate communicators, allowing them to send commands or receive data without being detected by the original parties. This is particularly dangerous for unencrypted protocols where authentication is performed only at the beginning of a session.
Trust Exploitation
Many legacy network systems and services are configured to trust connections originating from specific IP addresses, particularly within an internal network or between trusted partners. Attackers can leverage IP spoofing to impersonate a trusted host and bypass these IP-based authentication mechanisms. For example, if a server grants administrative access to connections from a specific internal IP address without further authentication, an attacker spoofing that internal IP can gain unauthorized privileges. This highlights a fundamental flaw in relying solely on IP addresses for trust in modern security architectures.
Detection and Prevention Strategies
Given the pervasive threat of IP spoofing, robust detection and prevention mechanisms are crucial for securing network infrastructure and protecting against a wide array of cyberattacks. These strategies typically involve a combination of network configurations, monitoring tools, and cryptographic protocols.
Ingress and Egress Filtering
One of the most effective prevention techniques is implementing ingress and egress filtering at network perimeters.
- Ingress filtering: This involves routers at the network’s entry point checking incoming packets. If a packet claims to originate from an IP address that is not part of the network’s internal address space, or from an external IP that shouldn’t be entering from that specific interface, the router drops it. This prevents attackers from spoofing internal IP addresses from outside the network.
- Egress filtering: Conversely, egress filtering involves routers checking outgoing packets. If a packet originates from an IP address that is not legitimately assigned to a device within that network, it is dropped. This prevents compromised machines within the network from launching spoofed attacks against external targets and helps prevent an organization’s network from being used as a source for DDoS attacks.
The BCP 38 standard (RFC 2827) provides guidelines for Internet Service Providers (ISPs) to implement ingress filtering, urging them to prevent customers from sending traffic with spoofed source IP addresses.
Packet Inspection and Traffic Analysis
Deep Packet Inspection (DPI) firewalls and intrusion detection/prevention systems (IDS/IPS) can analyze packet headers beyond just the IP address. While a basic firewall might only check source/destination IP and port, DPI can examine packet content and context to identify anomalous behavior. For example, if a packet claims to be from an internal IP but its sequence numbers or other protocol-specific fields are unexpected or out of sync with an ongoing session, an IDS might flag it as suspicious.
Traffic analysis tools can also detect spoofing by identifying unusual traffic patterns, such as a sudden surge of connection requests from seemingly disparate or non-existent IP addresses, which is characteristic of a DDoS attack using spoofed sources. Baselining normal network behavior is key to identifying these anomalies.
Authentication and Encryption
The most robust defense against IP spoofing’s malicious applications lies in stronger authentication and encryption. Relying solely on IP addresses for trust is inherently insecure.
- Stronger Authentication: Mechanisms like multi-factor authentication (MFA), digital certificates, and secure protocols that verify the identity of communicating parties at a higher layer (e.g., TLS/SSL) render IP spoofing less effective for gaining unauthorized access. Even if an attacker spoofs an IP, they still need valid credentials or a cryptographic key.
- Encryption (e.g., TLS/SSL, VPNs): Encrypting communication channels makes it significantly harder for attackers to read or alter data, even if they manage to inject spoofed packets into a session. Virtual Private Networks (VPNs) create secure, authenticated tunnels, making IP spoofing within the tunnel practically impossible for an external attacker.
Network Monitoring
Continuous and vigilant network monitoring is essential. Security information and event management (SIEM) systems collect logs and alerts from various network devices, providing a centralized view of security events. By correlating data, SIEMs can detect patterns indicative of spoofing attempts, such as multiple failed connection attempts from rapidly changing source IPs, or unusual traffic volumes targeting specific services. Timely alerts allow network administrators to respond quickly to potential attacks.
In conclusion, IP spoofing remains a potent threat in the digital landscape, a testament to the stateless design of the Internet Protocol. However, through a combination of diligent network architecture, advanced security tools, and the adoption of robust authentication and encryption protocols, organizations can significantly mitigate its risks and safeguard their digital assets in an ever-evolving technological environment.