
In the rapidly evolving landscape of unmanned aerial vehicles (UAVs), where innovation in autonomous flight, AI integration, mapping capabilities, and remote sensing continually pushes boundaries, the concept of “gray hat hacking” takes on a unique and critical dimension. Gray hat hacking occupies an ambiguous middle ground between the altruistic intentions of white hat hackers, who uncover vulnerabilities to improve security, and the malicious objectives of black hat hackers, who exploit weaknesses for personal gain or damage. Within the realm of drone technology, a gray hat hacker might identify a significant flaw in a drone’s navigation system, a vulnerability in its data transmission protocols, or a backdoor in its autonomous flight algorithms. Their actions, while not strictly illegal or overtly destructive, often occur without explicit authorization from the drone manufacturer or operator, and their motives can be complex, ranging from a desire to expose lax security to seeking recognition, or even a precursor to potential financial gain through bug bounties. Understanding this nuanced form of cyber activity is paramount for anyone involved in the design, deployment, or regulation of modern drone systems, as it directly impacts the reliability, safety, and public trust in these advanced technological innovations.

The Spectrum of Cybersecurity in Drone Technology
The distinction between different “hats” in the cybersecurity world is crucial for comprehending the ethical and legal frameworks governing digital interactions. This spectrum is particularly relevant in drone technology, where systems increasingly rely on sophisticated software, network connectivity, and AI-driven decision-making.
White Hat Hackers and Proactive Security
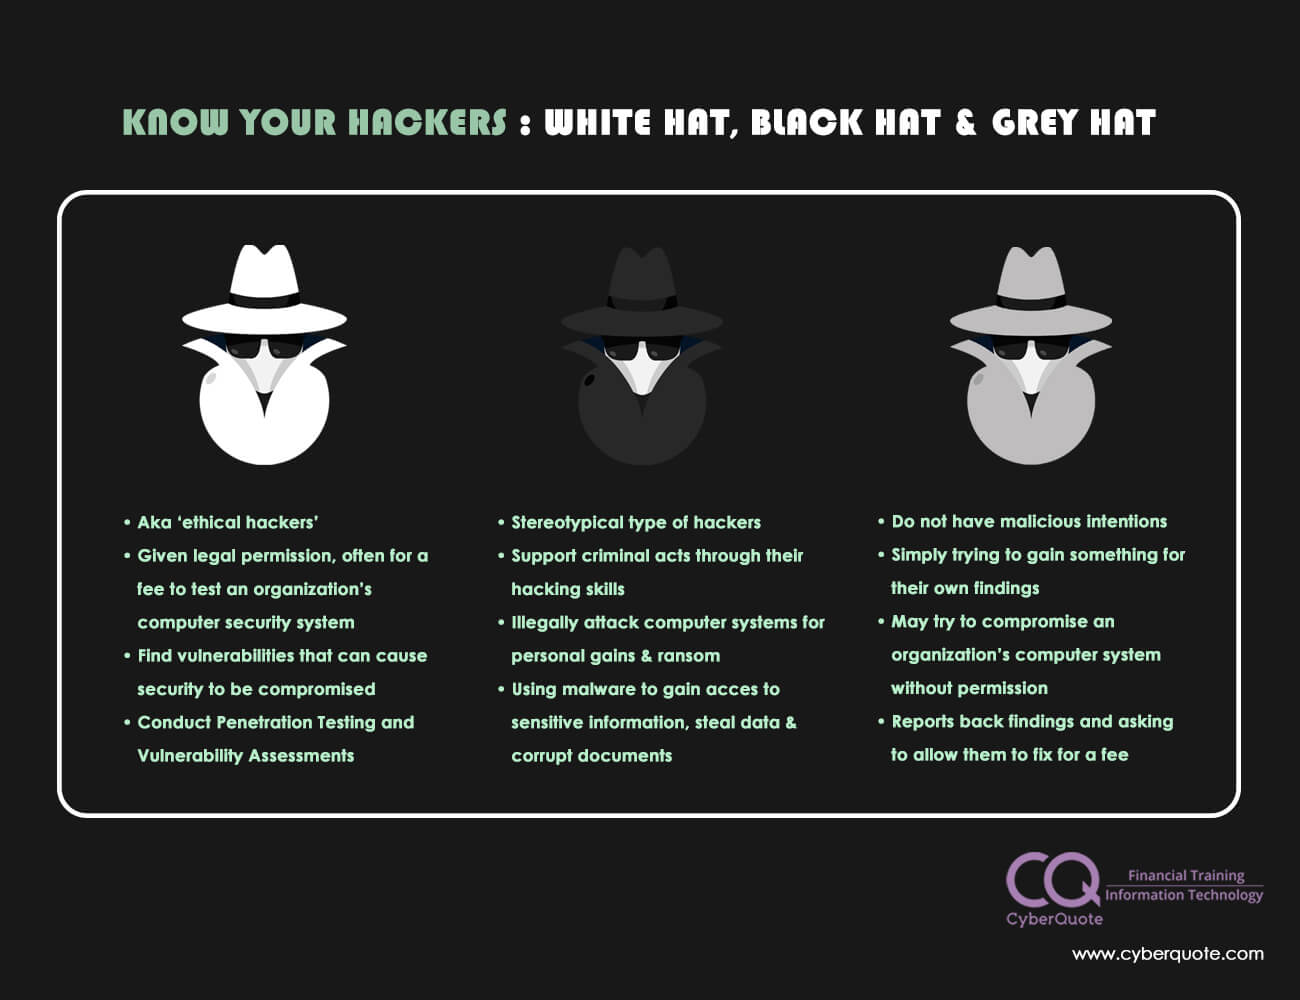
White hat hackers, often referred to as ethical hackers, are cybersecurity professionals who employ their skills to identify vulnerabilities in systems with the explicit permission of the owner. In the drone sector, white hats might be employed by manufacturers to rigorously test the resilience of new flight control software, GPS spoofing countermeasures, or data encryption for remote sensing payloads. Their work is sanctioned, collaborative, and aimed squarely at bolstering the security posture of drone platforms before they are deployed. This proactive approach is vital for ensuring the safety of autonomous flights, protecting sensitive mapping data, and preventing unauthorized control of UAVs. Their findings are typically disclosed privately to the vendor, allowing for patches and improvements to be implemented responsibly, contributing directly to the innovation of more secure and trustworthy drone systems.
Black Hat Hackers and Malicious Exploitation
At the opposite end of the spectrum are black hat hackers. These individuals or groups exploit system vulnerabilities for illicit purposes, ranging from gaining unauthorized control of a drone, disrupting its mission, stealing valuable intellectual property from its onboard systems, or even using it for surveillance or direct harm. For drone technology, a black hat attack could involve hijacking a drone mid-flight, injecting malicious code into its operating system to cause it to crash, or intercepting and manipulating its communication links to collect sensitive data from its cameras and sensors. The emergence of sophisticated autonomous flight modes and AI-powered capabilities makes drones particularly attractive targets for black hats, as compromising such systems could have significant economic, privacy, or national security implications. Their actions are illegal, unethical, and universally condemned, posing a constant threat to the integrity and safety of drone operations.
Gray Hat Hackers: Navigating the Ethical Middle Ground
Gray hat hackers occupy the often-ambiguous space between white and black hats. Their defining characteristic is that they uncover vulnerabilities without explicit authorization, much like black hats, but their ultimate intent is not malicious. Instead, they typically disclose their findings to the public or directly to the affected company, aiming to prompt a fix rather than exploit the flaw for personal gain or damage. In the drone context, a gray hat might discover a critical vulnerability in a popular drone’s firmware update mechanism or a flaw in the security of an associated ground control station application. Instead of reporting it through official channels or exploiting it, they might publish details on a security blog or demonstrate the vulnerability at a conference. While their intention might be to improve security, the unauthorized nature of their actions can sometimes put them in a legal gray area, and the public disclosure of a vulnerability before a patch is available can expose users to risk. This challenges drone manufacturers to balance rapid innovation with robust security infrastructure, as even well-intentioned unauthorized disclosures can lead to negative consequences.
Vulnerability Discovery in Advanced Drone Systems
Gray hat activities frequently intersect with the cutting-edge aspects of drone technology, particularly concerning autonomous functions and data management. Their explorations often reveal weaknesses in areas where security is still catching up with innovation.
Exposing Flaws in Autonomous Flight and AI
Modern drones are increasingly equipped with sophisticated autonomous flight capabilities, leveraging AI for tasks like obstacle avoidance, object tracking, and complex mission planning. These systems rely on intricate algorithms, sensor fusion, and real-time decision-making. A gray hat hacker might investigate the resilience of these systems to external interference or internal manipulation. This could involve attempting to “trick” an AI follow mode into tracking the wrong target, manipulating sensor inputs to cause misidentification in obstacle avoidance, or demonstrating how to bypass geofencing restrictions embedded in autonomous flight paths. For example, by analyzing the code or communication protocols, a gray hat might uncover a way to inject false telemetry data, leading a drone’s AI to misinterpret its position or surroundings, potentially causing it to deviate from its intended flight path or even crash. Such discoveries, though often performed without authorization, highlight critical areas for improvement in the robustness and security of AI-driven drone intelligence.
Securing Mapping, Remote Sensing, and Data Transmission
Drones are invaluable tools for mapping, remote sensing, and collecting vast amounts of data—from high-resolution imagery to thermal scans and LiDAR point clouds. The security of this collected data, both at rest and in transit, is a significant concern. Gray hat hackers may focus on uncovering vulnerabilities in how this data is stored on the drone, transmitted to the ground control station, or processed in cloud-based platforms. This could involve demonstrating weaknesses in encryption protocols used for real-time video feeds, identifying backdoors in data synchronization mechanisms, or exposing flaws in how sensitive mapping data is protected from unauthorized access. For instance, a gray hat might show how an unsecured API in a drone mapping application could be exploited to download proprietary topographical data or how a particular drone model’s telemetry stream could be intercepted to reconstruct its flight path and collected data. These revelations force manufacturers and operators to re-evaluate their data security practices, leading to more robust encryption, secure transmission channels, and improved data governance in an era where drone-collected data is an increasingly valuable asset.
The Impact on Drone Security and Innovation
The activities of gray hat hackers, while sometimes controversial, undeniably play a role in shaping the security landscape of drone technology. Their often-unconventional methods of discovery can force advancements that might otherwise be overlooked, driving a continuous cycle of innovation in security.
Driving Security by Design
When a gray hat publicly demonstrates a significant vulnerability in a drone system—especially one related to critical functions like flight control, GPS navigation, or data integrity—it creates immense pressure on manufacturers to address these flaws swiftly. This often leads to an increased focus on “security by design,” where security considerations are integrated into every stage of the drone’s development lifecycle, from hardware architecture to software algorithms. Instead of patching vulnerabilities reactively, companies are compelled to innovate proactively, developing more resilient communication protocols, tamper-proof firmware, and self-healing autonomous systems. The exposure of flaws, even if unauthorized, can be a catalyst for investing in more rigorous testing methodologies, incorporating advanced cryptographic techniques, and fostering a culture of security awareness among engineers and developers. This push for inherent security ultimately benefits the entire drone ecosystem, making future generations of UAVs more resistant to a broader range of cyber threats.

Fostering a Culture of Transparency and Resilience
Gray hat hacking, by its nature, often involves a degree of public disclosure. While sometimes problematic, this transparency can serve to educate both manufacturers and end-users about potential risks that exist within complex drone technologies. It encourages a more open dialogue around security challenges and the need for constant vigilance. For the broader “Tech & Innovation” category, this means recognizing that no system is entirely impenetrable and that continuous assessment and improvement are essential. When vulnerabilities are exposed, it drives innovation not just in patching individual flaws, but in developing more adaptable, resilient, and self-monitoring drone systems that can withstand evolving attack vectors. It can also prompt the establishment of bug bounty programs, transforming what might have been unauthorized gray hat activity into sanctioned white hat contributions, thereby harnessing external expertise for the collective good of drone security and technological advancement. Ultimately, the gray hat phenomenon, despite its complexities, underscores the critical need for a dynamic and responsive approach to security in the ever-advancing world of drone innovation.